php-cve-2026-10961x-lab-poc

PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…

PHP CVE-2026-109618/109619 — self-contained unauthenticated RCE on stock PHP 8.5.11 (in-band PS(id)→cookie memory disclosure + UAF chain), full…

PoC for CVE-2026-87902 — unauthenticated path traversal in WordPress page-template resolution (local PHP inclusion, conditional RCE) with a pinned…

POC for CVE-2026-78006 The Events Calendar <= 6.17.4 - Unauthenticated PHP Object Injection to Remote Code Execution

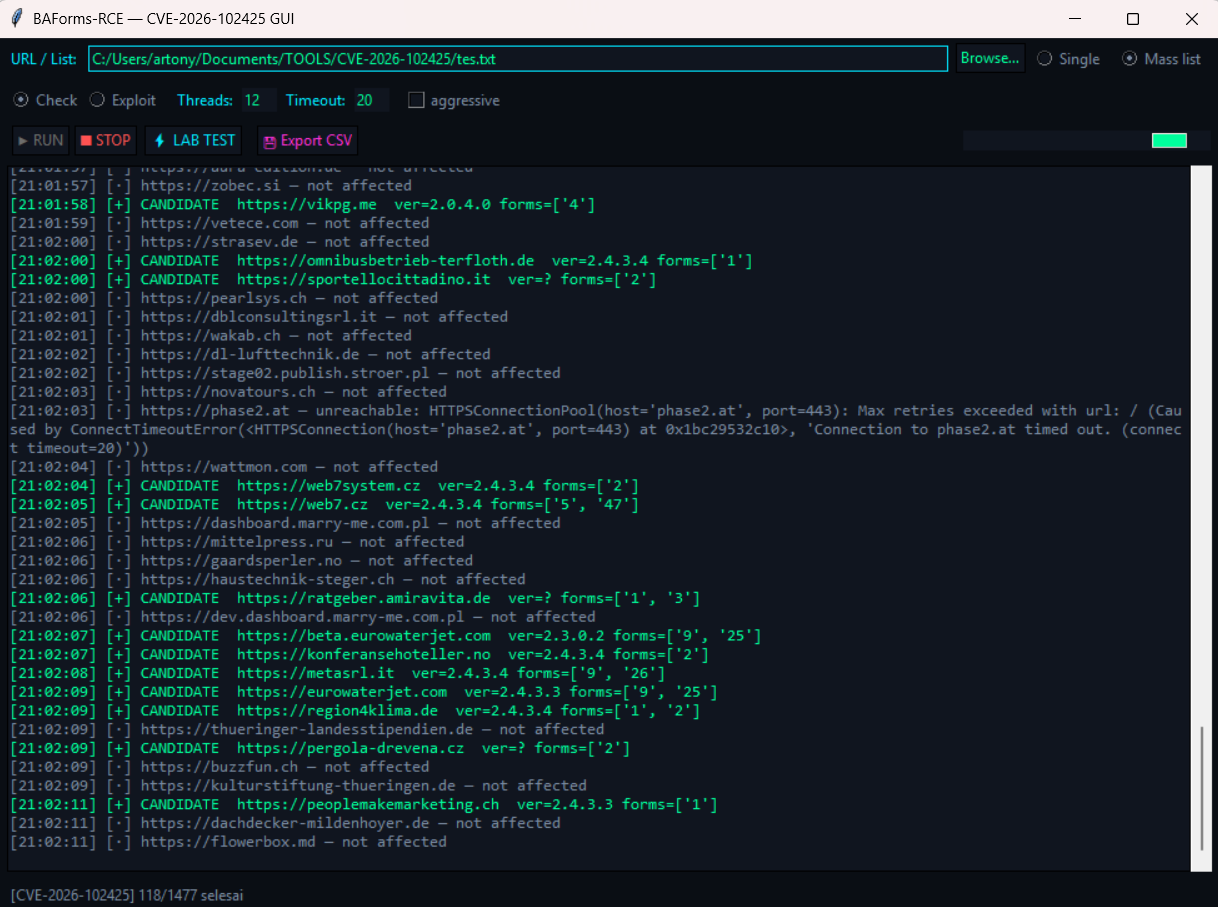
GUI scanner and exploit for CVE-2026-102425, an unauthenticated RCE in Balbooa Forms (com_baforms) via PHP shortcode injection, with mass scanning…

Proof-of-concept exploit for CVE-2021-29447, an XXE injection vulnerability in WordPress 5.6–5.7 via malicious WAV file upload, enabling arbitrary…

Laravel Reverb 为 Laravel 应用提供实时 WebSocket 通信后端。在 1.6.3 及更早版本中,Reverb 将来自 Redis 通道的数据直接传递给 PHP 的 unserialize() 函数,且未对可实例化的类进行限制,导致用户面临远程代码执行风险。

Educational CVE-2024-12877 exploit demo for PHP Object Injection in GiveWP WordPress plugin. Includes root cause analysis, regex bypass techniques,…

Demonstrates exploitation of CVE-2024-4577, a PHP CGI RCE on Windows, including attack steps, reverse shell deployment, and ransomware simulation…

CVE-2026-109618/109619 PHP session.upload_progress Exploit Research — POC & Analysis

Pure-HTTP exploit achieving RCE on PHP 8.4.26 + Apache mod_php via session upload_progress heap leak, dangling pointer reuse, and ASLR bypass to call…

Proof-of-Concept (PoC) exploit for php2shell (CVE-2026-109618 / CVE-2026-109619), demonstrating remote code execution in vulnerable PHP environments.…

Unified repository for different Metasploit Framework payloads


Shell PoC for CVE-2026-87902, an unauthenticated WordPress core LFI via page-template resolution that chains to RCE through pearcmd.php.

Proof-of-concept exploit for CVE-2022-30887, demonstrating remote code execution via file upload in Pharmacy Management System 1.0, with mitigation…


Based on the x.pl exploit/loader script for CVE-2009-1151

🤖 NO, There is an easy way to exploit this vulnerability! (vibecoded to prove a point)