MCP-Inspector-CVE-2025-49596

MCP-Inspector-vulncheck is a Python script that checks if an MCP Inspector server is vulnerable to CVE-2025-49596. It tests whether the /sse endpoint…

MCP-Inspector-vulncheck is a Python script that checks if an MCP Inspector server is vulnerable to CVE-2025-49596. It tests whether the /sse endpoint…

Proof-of-concept exploit for CVE-2023-27532 in Veeam Backup and Replication that abuses an unsecured API endpoint to extract credentials from the…

GLPI Privilege Escalation via authtype Manipulation PoC - CVE-2026-53625. Ethical PoC for the GLPI vulnerability allowing a Technician to take full…

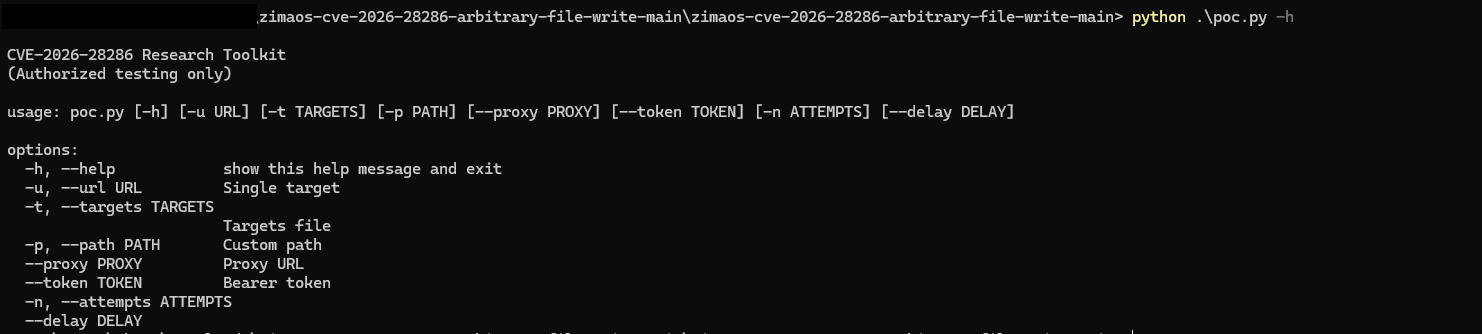
PoC and verification toolkit for CVE-2026-28286, an arbitrary file write vulnerability in ZimaOS, exploiting API misconfiguration to write files…

PoC exploit for CVE-2026-73678: unauthenticated RCE in MindsDB Cowork via attacker-supplied LLM key and unsandboxed scratchpad exec to run OS…

Reproducer for CVE-2026-46592: Apache Camel camel-cxf operationName header injection redirecting the invoked SOAP operation (confused deputy) from a…

PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB

Time-based blind SQL injection proof-of-concept for LiteLLM v1.65.4. Exploits the `/key/block` endpoint to extract database contents and read server…

Strapi CVE-2026-27886. Leaking sensitive data via relational filtering due to lack of query sanitization

CVE-2024-11972 in Hunk Companion <1.9.0 allows unauthenticated attackers to exploit insecure REST API endpoints and install vulnerable plugins,…

Hunk Companion <= 1.8.4 - Missing Authorization to Unauthenticated Arbitrary Plugin Installation/Activation

Proof-of-concept exploit for CVE-2026-24134, a Broken Object Level Authorization vulnerability in StudioCMS, demonstrating unauthorized access to…

Python proof-of-concept for CVE-2026-30944, exploiting a BOLA vulnerability in StudioCMS to escalate privileges via insecure API token generation.

g-FFL Cockpit <= 1.7.1 - Improper Authorization to Unauthenticated Product Deletion

Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…

Demonstrates an IDOR vulnerability in TelegAI's chat API allowing unauthorized conversation tampering, leading to phishing and XSS-based account…

Proof-of-concept exploit for CVE-2024-50633, a Broken Object Level Authorization (BOLA) vulnerability in Indico v3.2.9–v3.3.2, enabling unauthorized…

XSS Test Swagger 3.14.1 to 3.37.0