
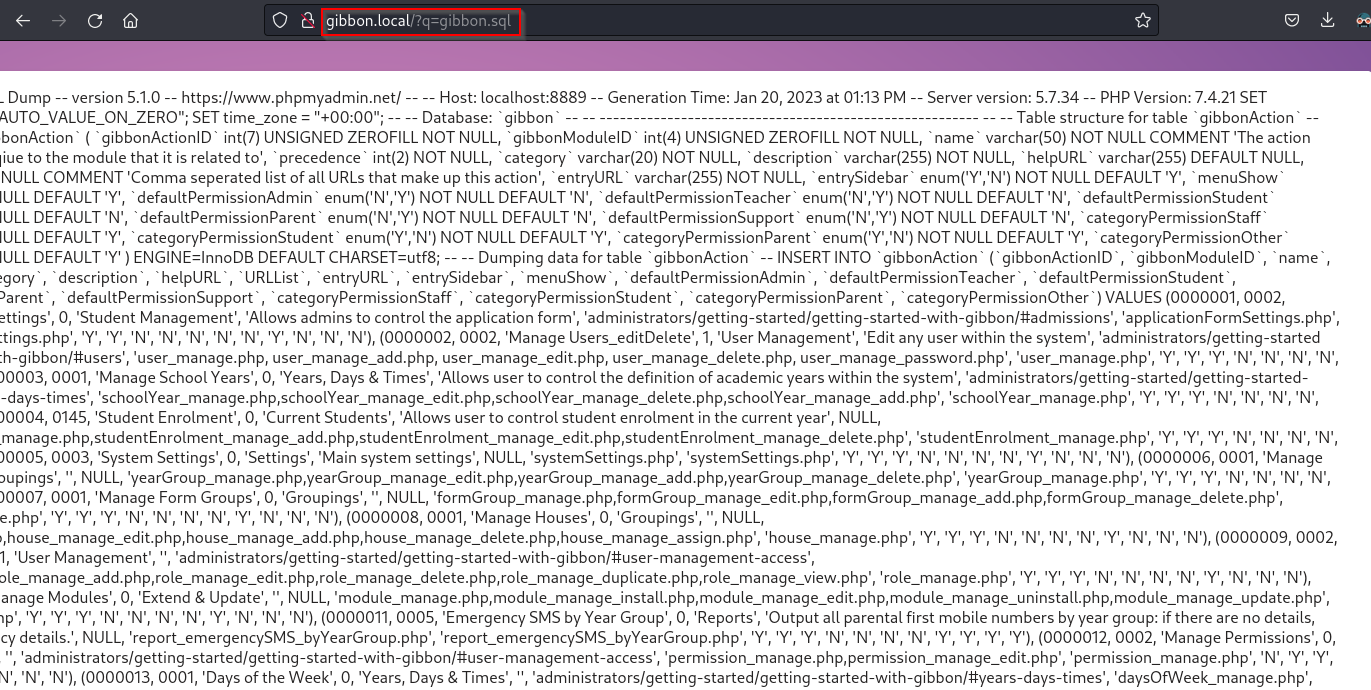
CVE-2023-34598
 maddsec/cve-2023-34598
Gibbon v25.0.0 is vulnerable to a Local File Inclusion (LFI) vulnerability where it's possible to include the content of several files present in the…
exploitationinformation-gatheringpenetration-testing+2
3
maddsec/cve-2023-34598Gibbon v25.0.0 is vulnerable to a Local File Inclusion (LFI) vulnerability where it's possible to include the content of several files present in the…
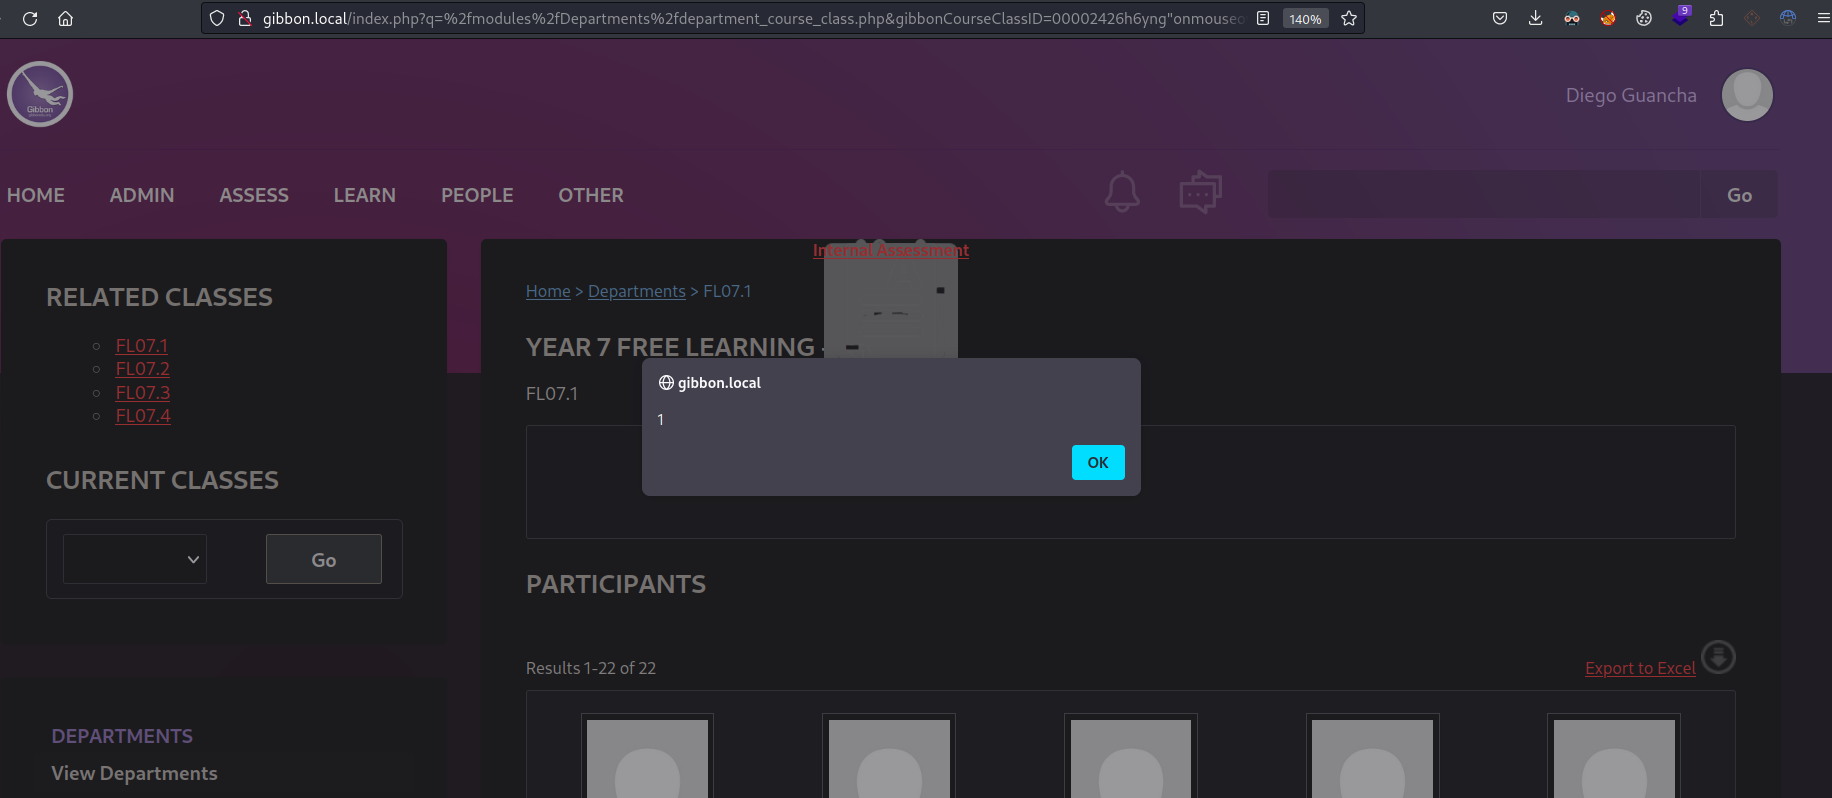 maddsec/cve-2023-34599
Multiple Cross-Site Scripting (XSS) vulnerabilities have been identified in Gibbon v25.0.0, which enable attackers to execute arbitrary Javascript…
 mbanyamer/cve-2026-25890-filebrowser-access-control-bypass
Exploit for CVE-2026-25890, a path-based authorization bypass in FileBrowser <= v2.57.0, allowing authenticated low-privileged users to read, upload,…
 codermohammed1/cve-2025-63848
CVE disclosure for stored cross-site scripting (XSS) in SWISH Prolog up to v2.2.0, enabling arbitrary code execution and account takeover via crafted…
 zer0f8th/cve-2023-34598
Gibbon v25.0.0 is vulnerable to a Local File Inclusion (LFI)
 dani33339/tough-cookie-v2.5.0-patched
Patched tough-cookie v2.5.0 fixing CVE-2023-26136 prototype pollution vulnerability with Object.create(null) in MemoryCookieStore, including exploit…
 lauleysen/cve-2024-46538
based on [EQSTLab](https://github.com/EQSTLab)
 biitts/cve-2026-56423-misp-deleteselection-brokenaccesscontrol
PoC for CVE-2026-56423: MISP deleteSelection broken access control (CWE-862, contributor hard-deletes other orgs' Event Reports/Sharing Groups, CVSS…