
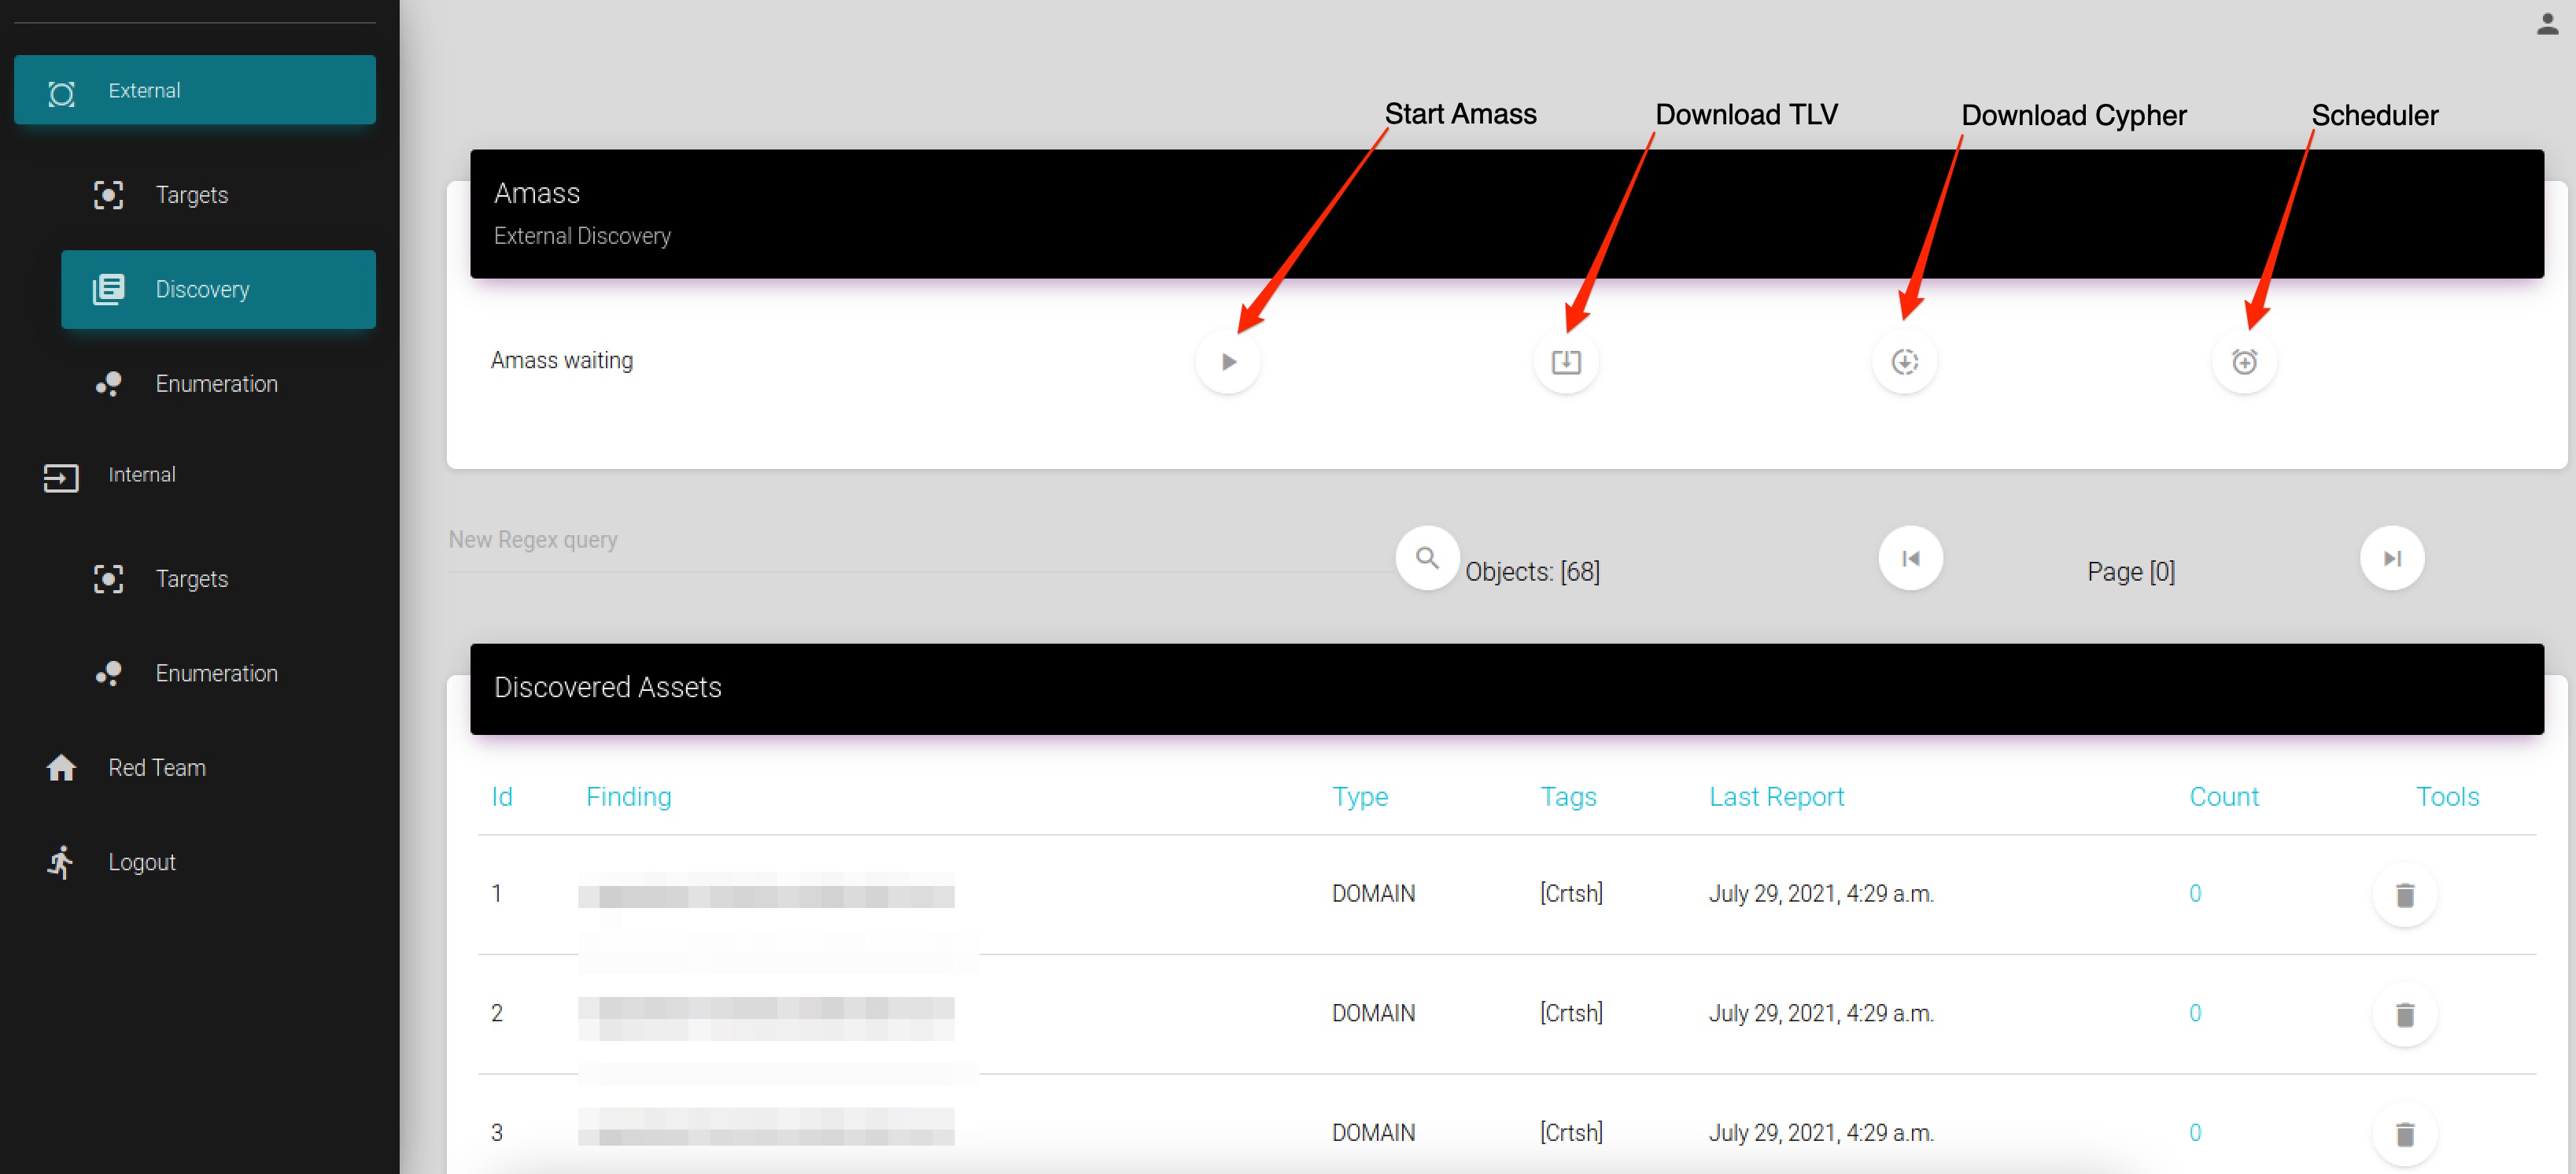
attack-surface-framework
 vmware-labs/attack-surface-framework
Tool to discover external and internal network attack surface
dns-subdomain-enumerationexploitationinformation-gathering+8
206
vmware-labs/attack-surface-frameworkTool to discover external and internal network attack surface
 manyaigdtuw/cve-2025-68613_scanner
GUI Shodan-powered scanner to identify n8n instances exposed to CVE-2025-68613 (version range 0.211.0–1.122.0)
 initstring/evil-ssdp
Spoof SSDP replies and create fake UPnP devices to phish for credentials and NetNTLM challenge/response.
 pedrocruz2202/mongobleed-scanner
🔍 Scan for MongoDB vulnerabilities with MongoBleed, a high-performance tool for detecting CVE-2025-14847 across large networks quickly and…
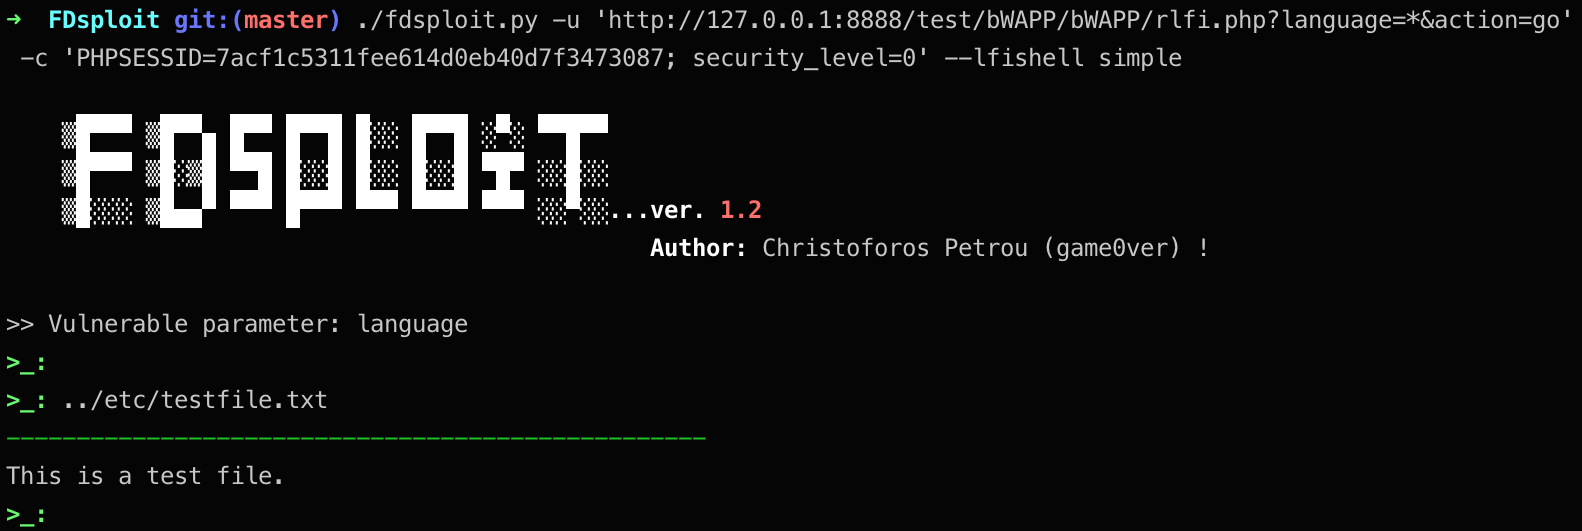 chrispetrou/fdsploit
File Inclusion & Directory Traversal fuzzing, enumeration & exploitation tool.
 orange-cyberdefense/keepwn
A python tool to automate KeePass discovery and secret extraction.
 0xbinder/cve-2026-0073
An automated exploit for CVE-2026-0073 (Android ADB TLS Auth Bypass). Features a built-in mDNS/Zeroconf scanner to instantly discover randomized…
 exfil0/cve-2024-55591-poc
A comprehensive all-in-one Python-based Proof of Concept script to discover and exploit a critical authentication bypass vulnerability…
 futureslab/binvariants
Register-level invariant-guided fuzzing framework for closed-source binaries, leveraging likely invariant violations to discover crashes and bugs in…
 cobbbex/cisco-asa-vulnerability-research
Systematic reverse engineering of Cisco ASA's lina binary to discover and analyze memory corruption vulnerabilities, including CVE-2025-20333 and…
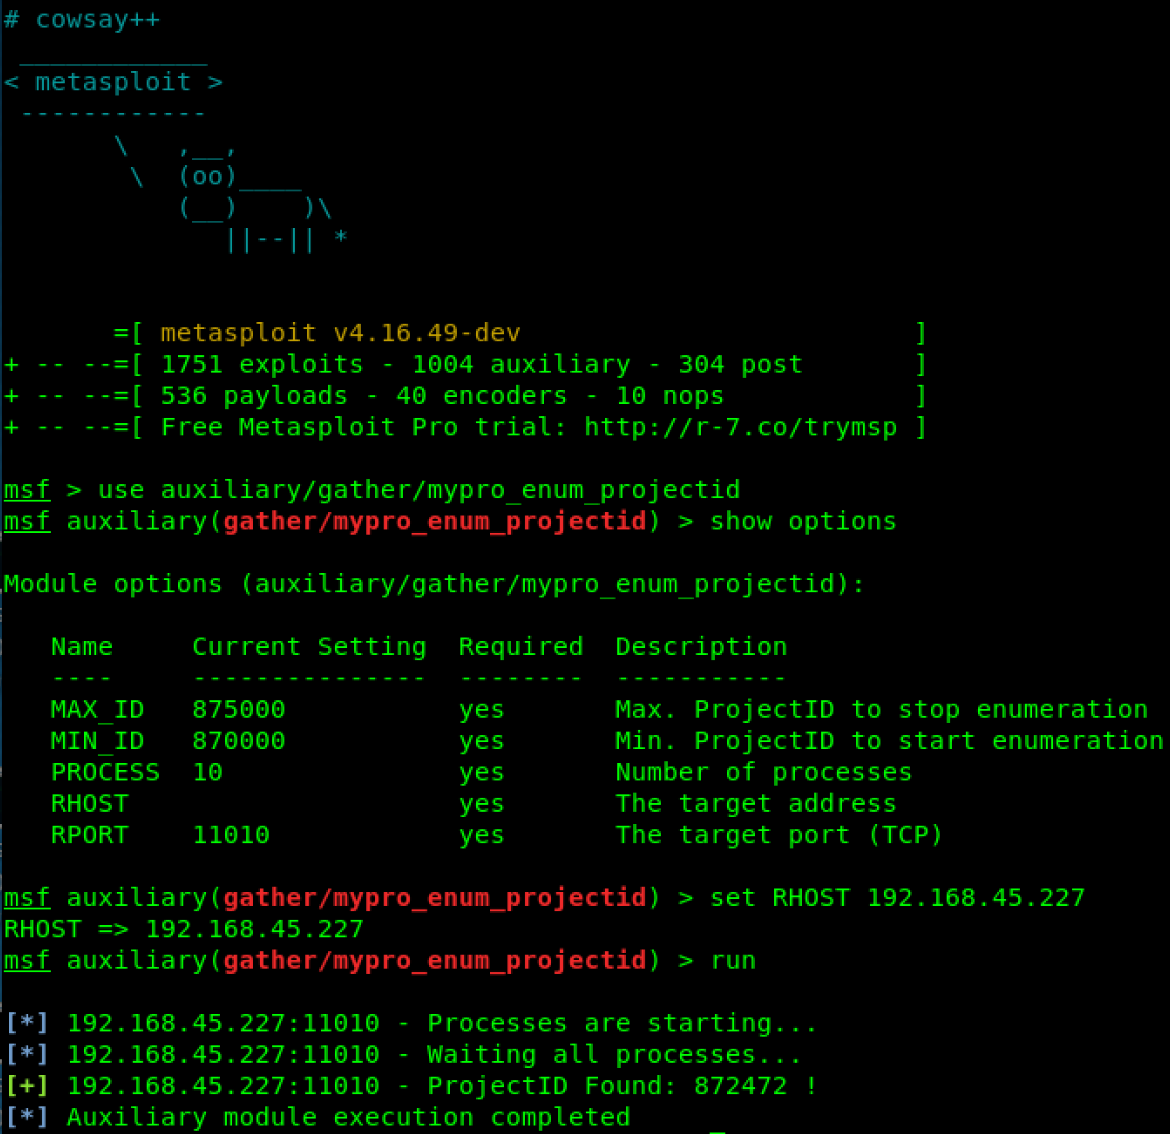 emreovunc/myscada-mypro-7-projectid-disclosure
CVE-2018-11517 | mySCADA myPRO v7.0.46 has another vulnerability to discover all projects in the system.
 vulncheck-oss/fetch-broker-conf
A go-exploit for fetching the RocketMQ broker configuration in order to discover indicators of compromise for CVE-2023-33246
 justin-p/geoexplorer
Mass vulnerability scanner targeting CVE-2024-36401 in GeoServer, using WFS requests to discover feature types and deliver payloads for automated…
 debugactiveprocess/cve-2026-18963
Nuclei template to discover exposed Keycloak reset-credentials endpoints across multiple paths, aiding validation of CVE-2026-18963 exposure.
 ryeyao/cve-2014-6271_test
Python-based scanner to detect CVE-2014-6271 (Shellshock) vulnerability in CGI-enabled servers, using Google search to discover potential targets.
 yggcwhat/cve-2021-45232
Batch vulnerability scanner that integrates FOFA to discover and test Apache APISIX Dashboard instances for CVE-2021-45232 unauthorized access.
 freefv/cve-2020-5902-fofa-scan
Automated scanner for CVE-2020-5902 (F5 BIG-IP RCE) using FOFA search engine to discover and exploit vulnerable targets.
 mohwahyudi/cve-2021-41773
Python script that uses Shodan to discover Apache HTTP Server 2.4.49 instances vulnerable to CVE-2021-41773 path traversal and file disclosure.