
aDLL
 ideaslocas/adll
Automated DLL hijacking vulnerability discovery tool that analyzes PE binaries at load-time and runtime via API hooking, enumerating missing DLLs and…
binary-analysisdynamic-analysis-sandboxingexploitation+1
73
ideaslocas/adllAutomated DLL hijacking vulnerability discovery tool that analyzes PE binaries at load-time and runtime via API hooking, enumerating missing DLLs and…
 gmh5225/keypatchx
KeyPatch Enhanced — IDA Pro plugin for symbol-aware x86/x64 assembly patching, powered by Keystone Engine. Fork of Keypatch with automatic IDA symbol…
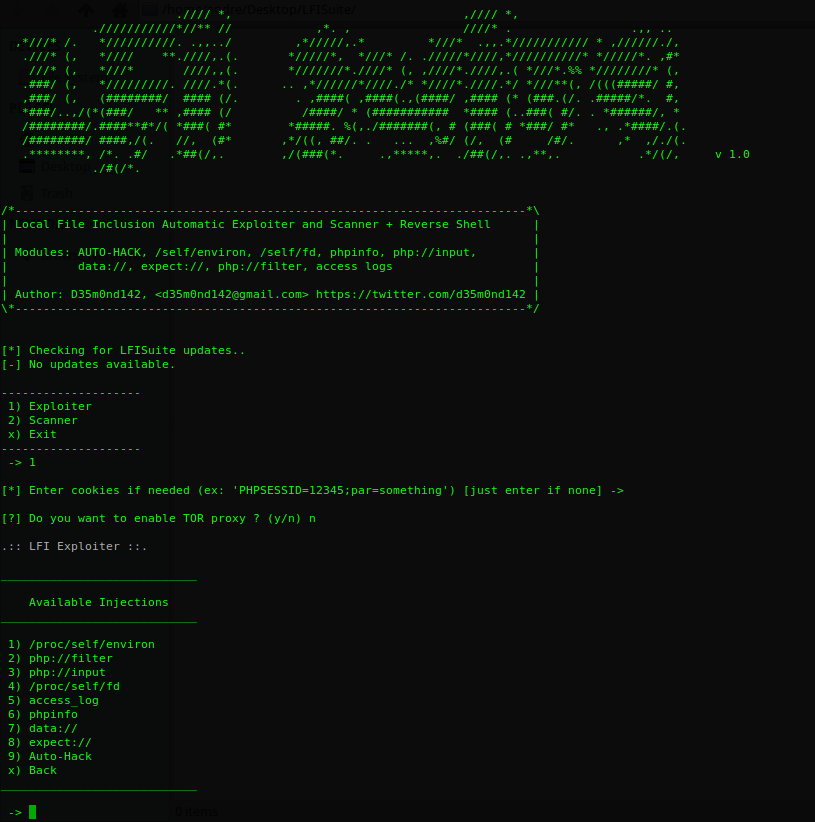 d35m0nd142/lfisuite
Totally Automatic LFI Exploiter (+ Reverse Shell) and Scanner