

cve-2025-66723
 audiopump/cve-2025-66723
CVE-2025-66723: inMusic Brands Engine DJ >=3.0.0 through <4.3.4 exposes local and network files to external parties
data-exfiltrationexploitationinformation-gathering+3
audiopump/cve-2025-66723CVE-2025-66723: inMusic Brands Engine DJ >=3.0.0 through <4.3.4 exposes local and network files to external parties
 dicanio/cve-2021-44228-docker-example
Docker-based demonstration of CVE-2021-44228 (Log4Shell) exploitation, featuring a vulnerable Java server, malicious LDAP server, and data…
 smarttfoxx/cve-2025-65321
Language Sloth Sloth Bot 1.0 is vulnerable to Directory Traversal in the gif() and png() functions. The functions build file paths using unsanitized…
 george0papasotiriou/cve-2026-21015-php-filter-chain-arbitrary-file-read
PoC exploit for CVE-2026-21015 that abuses PHP filter chains to read arbitrary files through a vulnerable include() call, disclosing source and…
 daemoncibsec/flar3ad
POC of CVE-2026-51031 for arbitrary local file read
 ioncodes/cve-2020-16938
Bypassing NTFS permissions to read any files as unprivileged user.
 p0dalirius/cve-2021-31800-impacket-smb-server-arbitrary-file-read-write
A path traversal in smbserver.py allows an attacker to read/write arbitrary files on the server.
 0xterror/cve-2023-22047-oracle-peoplesoft-lfi
CVE-2023-22047 is a critical unauthenticated Local File Inclusion (LFI) vulnerability in Oracle PeopleSoft Enterprise PeopleTools. This exploit…
 george0papasotiriou/cve-2026-11111-toctou-in-file-permission-check-before-open
Educational CVE PoC for a TOCTOU file-permission race in Flask; uses symlink replacement during the check-open window to disclose sensitive files.
 hannob/cve-2020-27603-bbb-libreoffice-poc
Proof of Concept of Libreoffice file exfiltration vulnerability in Big Blue Button
 mbadanoiu/mal-014
MAL-014: Authenticated Arbitrary File Read in VMware vCenter Server
 alpernae/cve-2024-40422
Python implementation/PoC for CVE-2024-40422. Exploits a critical directory traversal vulnerability in Devika v1's /api/get-browser-snapshot endpoint…
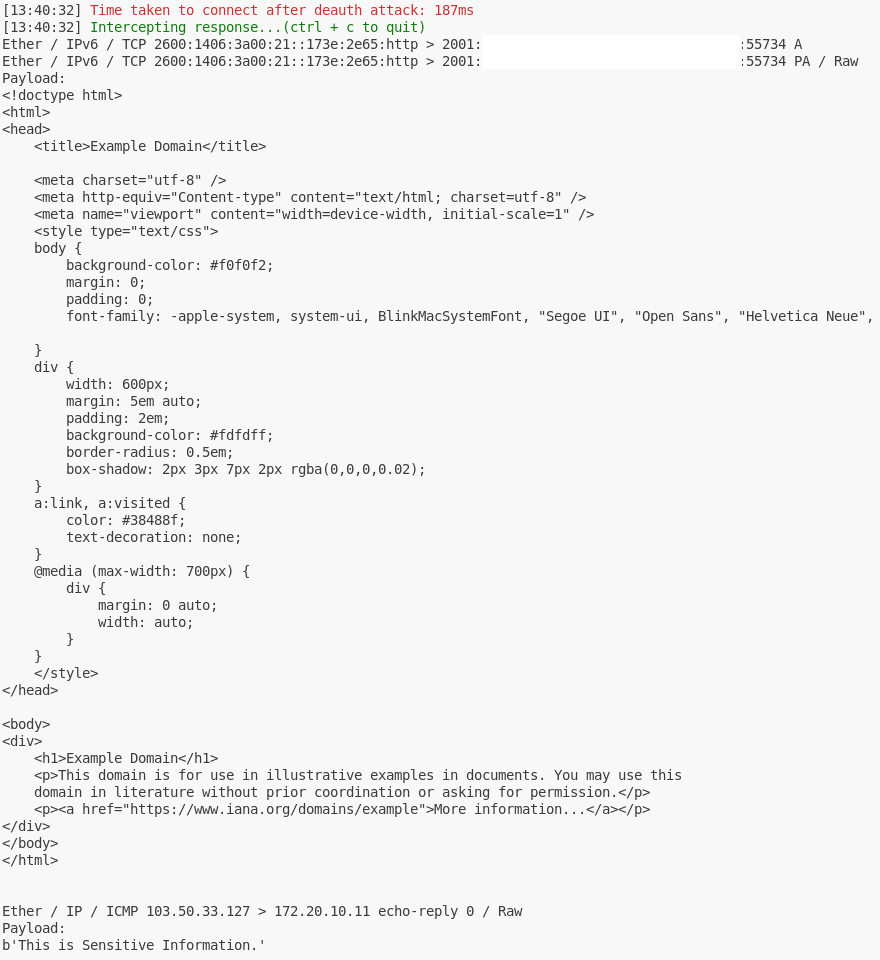 toffeenutt/cve-2022-47522-poc
Proof-of-concept exploit for CVE-2022-47522 demonstrating Wi-Fi frame interception via deauthentication attack and MAC address spoofing to capture…
 tastypepperoni/pplblade
Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…
 jfriedli/cve-2025-12137
Proof-of-concept exploit for CVE-2025-12137 demonstrating local file disclosure via a WordPress plugin's REST API importer endpoint. Includes…
 thestingr/cve-2024-36991-tool
This binary POC automates the exploitation of CVE-2024-36991 by sending crafted curl requests to a vulnerable Splunk instance. It retrieves sensitive…
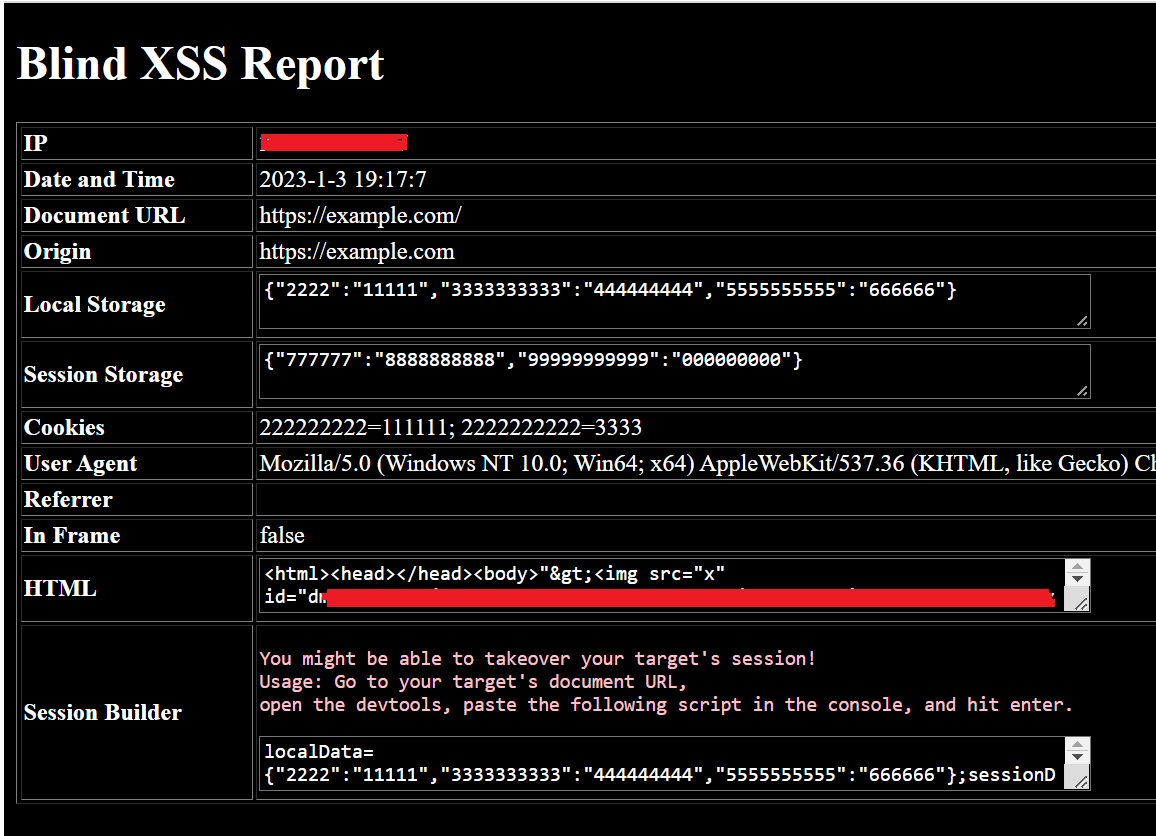 seifelsallamy/xssfire
A standalone Blind XSS Script.