
PXEThief
 mwr-cybersec/pxethief
PXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
exploitationinformation-gatheringpassword-attacks+5
438
mwr-cybersec/pxethiefPXEThief is a set of tooling that can extract passwords from the Operating System Deployment functionality in Microsoft Endpoint Configuration Manager
 sunweb3sec/defihacklabs
Reproduce DeFi hacked incidents using Foundry.
 edwardzpeng/presentations
Slides and conference talks from security research covering Windows, virtualization, web, and blockchain exploit techniques, presented at Black Hat,…
 tyeurada/edrevasionworkshop
Workshop materials for “Step-by-Step Malware Development: Evading EDR from Loaders to the Kernel” presented at DEF CON 34 and BSidesLV 2026. Covers…
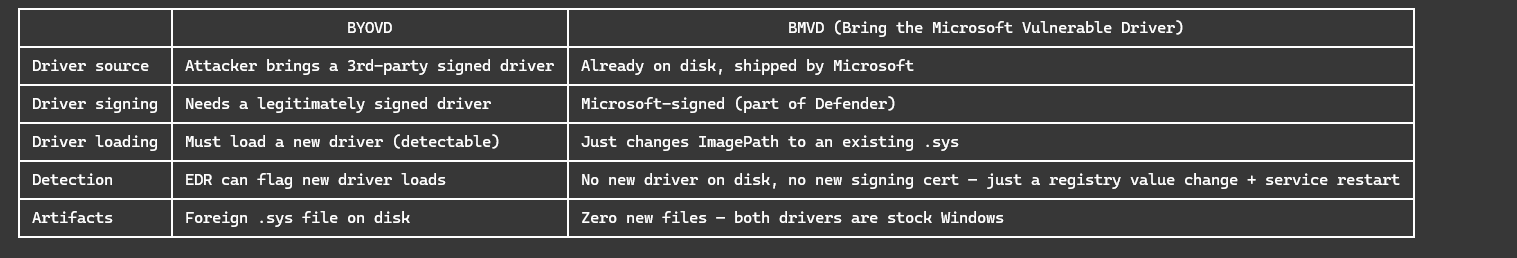 andreisss/ksldump
KslDump — Why bring your own knife when Defender already left one in the kitchen?
 urbanesec/zackattack
Unveiled at DEF CON 20, NTLM Relaying to ALL THE THINGS!
 bishopfox/deephack
PoC code from DEF CON 25 presentation
 forrest-orr/artifacts-kit
Pseudo-malicious usermode memory artifact generator kit designed to easily mimic the footprints left by real malware on an infected Windows OS.
 live-ctf/livectf-defcon30
Collection of DEF CON 30 CTF challenge binaries, build scripts, and solve scripts for practicing binary exploitation and reverse engineering.
 exploitblizzard/windowsmdm-lpe-0day
CVE-2021-24084 Windows Local Privilege Escalation Left officially unpatched since 2020. Hence, its still a zero day
 infobyte/ezviz_lan_rce
PoC exploits and Docker build environment for CVE-2023-34551 and CVE-2023-34552 targeting EZVIZ IP cameras, with DEF CON 31 Hardware Hacking Village…
 timtimxs/cve-2026-51947-advisory
Pivotal CRM's patch for an initial deserialization vulnerability was incomplete. The fix switched from BinaryFormatter to JSON.NET but left…
 roaris/cve-2024-27304-poc
PoC of "DEF CON 32 - SQL Injection Isn't Dead Smuggling Queries at the Protocol Level - Paul Gerste"
 thecyberviking/cve-2020-5902-vuln-checker
Simple Vulnerability Checker Wrote by me "@TheCyberViking" and A fellow Researcher who wanted to be left Nameless... you know who you are you…
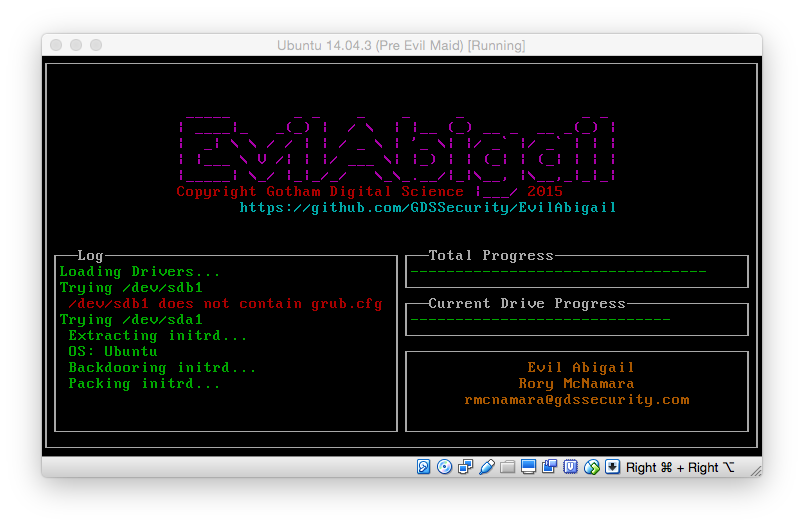 strozfriedberg/evilabigail
Automated Linux evil maid attack
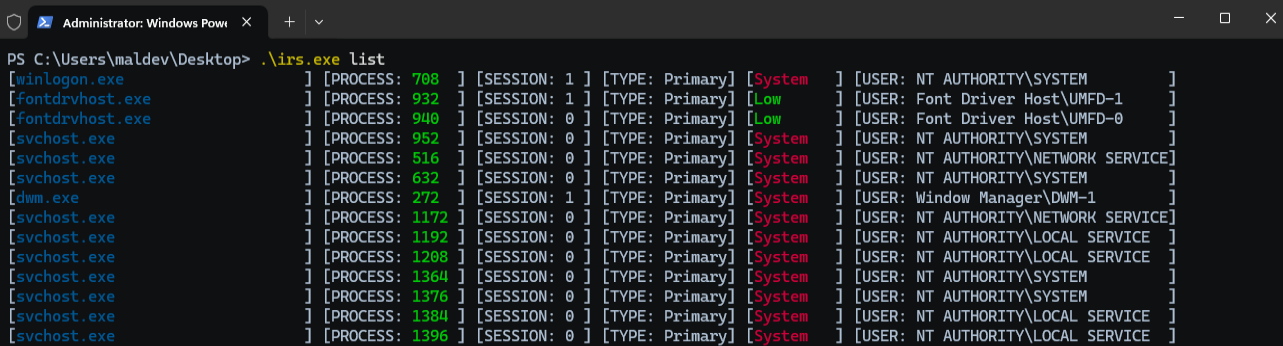 zblurx/impersonate-rs
Rusty Impersonate
 jbaines-r7/cisco_asa_research
Cisco ASA Software and ASDM Security Research
 misterxid/watchguard_cve-2022-26318
Proof-of-concept exploit for CVE-2022-26318, a remote code execution vulnerability in WatchGuard XTM and FireWare OS, delivering a reverse shell via…