
CVE-2026-43914-PoC
 boreas37/cve-2026-43914-poc
PoC for CVE-2026-43914: Vaultwarden <1.35.4 email-2FA brute-force bypass password oracle. Stdlib-only Python.
exploitationpassword-attackspenetration-testing+2
1
boreas37/cve-2026-43914-pocPoC for CVE-2026-43914: Vaultwarden <1.35.4 email-2FA brute-force bypass password oracle. Stdlib-only Python.
 io1337/icg-autoexploiterbot
Automated exploitation tool targeting CMS vulnerabilities in Joomla, WordPress, Drupal, PrestaShop, and OsCommerce with built-in brute-force and…
 trackflaw/cve-2023-23397
Simple PoC of the CVE-2023-23397 vulnerability with the payload sent by email.
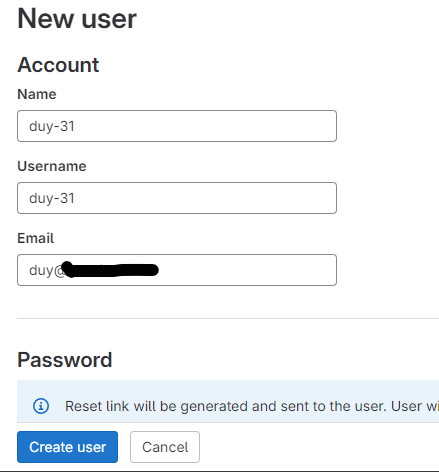 duy-31/cve-2023-7028
An issue has been discovered in GitLab CE/EE affecting all versions from 16.1 prior to 16.1.6, 16.2 prior to 16.2.9, 16.3 prior to 16.3.7, 16.4 prior…
 hackeremmen/gitlab-exploit
Exploit for GitLab CVE-2023-7028: password reset bypass via dual email verification, allowing unauthorized account takeover. Includes affected…
 randomrobbiebf/cve-2022-0439
CVE-2022-0439 - Email Subscribers & Newsletters < 5.3.2 - Subscriber+ Blind SQL injection
 anothersec/cve-2025-4796
eventin <= 4.0.34 - privilege escalation via user email change / account takeover for authenticated contributor+
 jfriedli/cve-2025-10658
Python exploit script for CVE-2025-10658: brute-forces 6-digit OTP in WordPress SupportCandy guest login to achieve full account takeover via…
 hatlesswizard/cve-2023-6875
CVE-2023-6875 exploit written for Xakep.Ru
 mr-un1k0d3r/redteamscripts
Collection of offensive red team scripts including process termination, SPF bypass for phishing, password spraying, and ColdFusion password…
 bronzebee/cve-2023-23397
Python script for sending e-mails with CVE-2023-23397 payload using SMTP
 theunknownsoul/cve-2023-23397-pow
Proof of Work of CVE-2023-23397 for vulnerable Microsoft Outlook client application.