
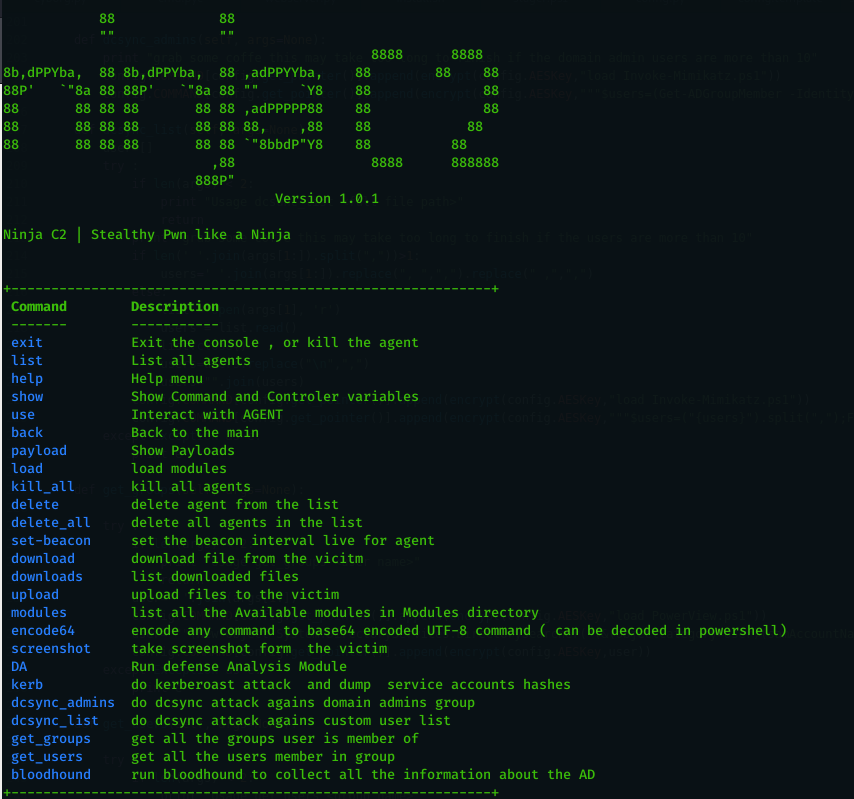
Ninja
 ahmedkhlief/ninja
Open source C2 server created for stealth red team operations
command-and-controlexploitationinformation-gathering+6
ahmedkhlief/ninjaOpen source C2 server created for stealth red team operations
 xpn/blockchainc2
A POC C2 server and agent to explore just if/how the Ethereum blockchain can be used for C2
 ekomssavior/poc_cve-2025-32433
Proof-of-concept exploit for CVE-2025-32433 with simulated and real attack modes, including a Flask-based C2 server for reverse shell callbacks and…
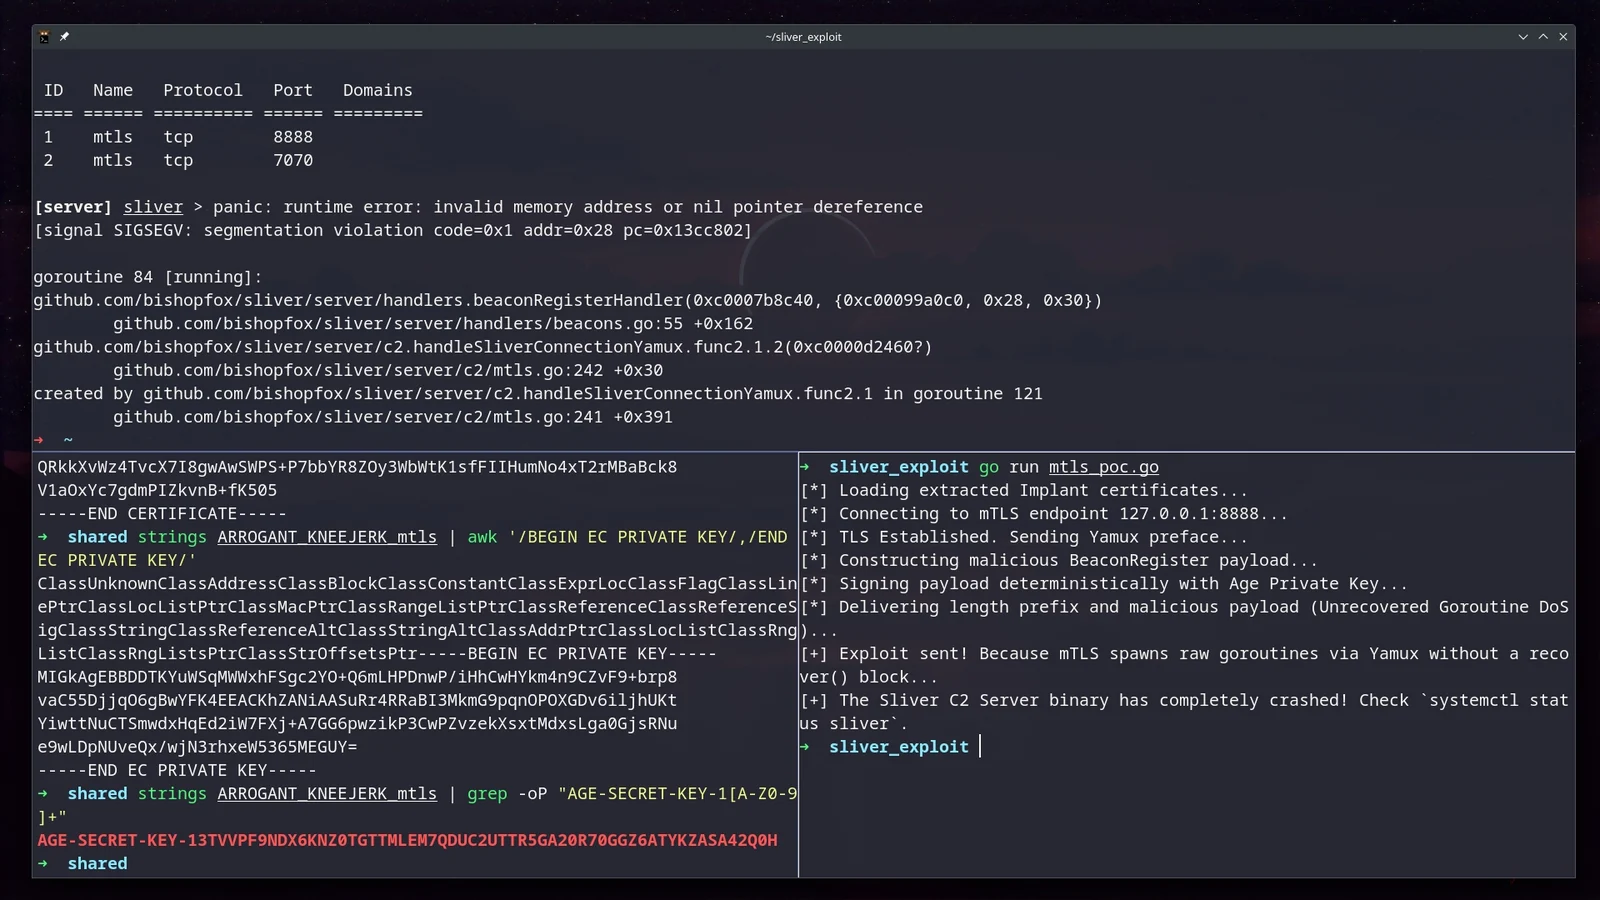 skoveit/cve-2026-29781
Proof-of-concept exploit for CVE-2026-29781, weaponizing captured Sliver implant credentials to trigger a nil-pointer panic and crash the C2 server…
 ch4os1/cve-2024-4157-ssrf-rce-reverse-shell
Chaining Havoc C2 SSRF with RCE to get reverse shell on Havoc C2 Server.
 jarm222/cve-2025-26244
The graph functionality of DeimosC2 v1.1.0-Beta is vulnerable to Stored Cross-Site Scripting (XSS), allowing the theft of session cookie and…
 june-in-exile/cve-2021-26700
Educational RCE exploit for CVE-2021-26700 in VS Code npm extension, demonstrating DNS tunneling to a Caldera C2 server via malicious package.json…
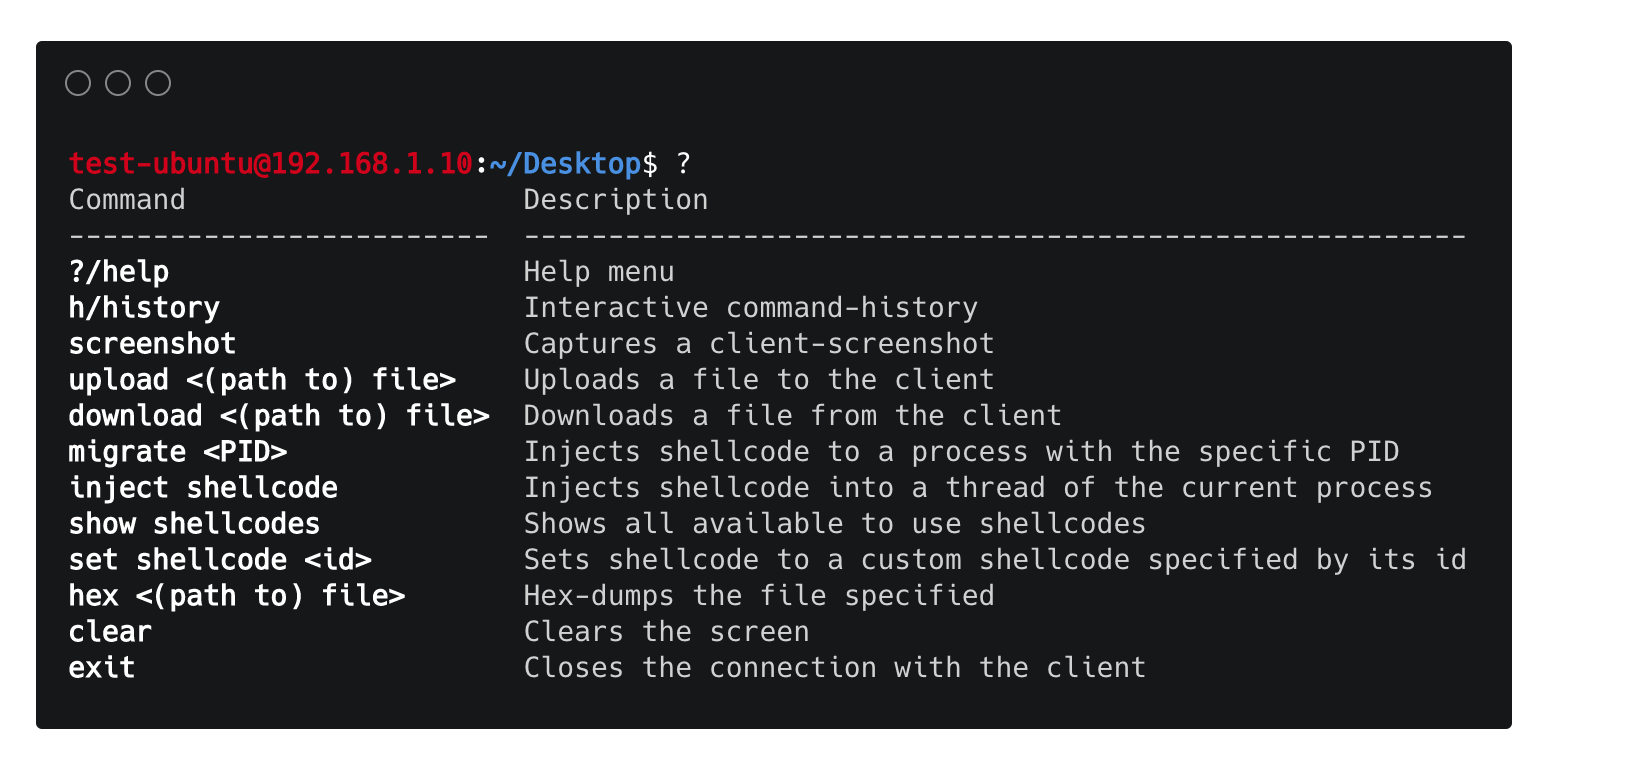 chrispetrou/hrshell
HRShell is an HTTPS/HTTP reverse shell built with flask. It is an advanced C2 server with many features & capabilities.
 azefzafyoussef/cve-2026-34621
Research PoC demonstrating a prototype pollution and JavaScript injection chain in Adobe Acrobat Reader, enabling privileged JavaScript execution and…
 yrkuo/cve-2022-30190
Step-by-step reproduction guide for CVE-2022-30190 (Follina) MSDT remote code execution vulnerability, including malicious document creation and C2…
 kaitokidc500/cve-2024-23700-c2-server
Source code minh họa máy chủ c2 demo kịch bản thực thi của CVE-2024-23700
 skoveit/cve-2026-34227
Proof-of-concept demonstrating CORS to CSRF chain on Sliver's unauthenticated MCP interface, enabling silent interaction with C2 from any webpage.
 geek-repo/c2-blockchain
This is a concept poc of command and control server implemented over blockchain
 vulncheck-oss/external-c2-experiments
Go external C2 module for go-exploit that catches reverse SSH shells, providing a server listener and payload client for integrating custom C2…
 felisha-elmer/sandbox-challenge-spring4shell-cve-2022-22965-
Step-by-step walkthrough of exploiting CVE-2022-22965 (Spring4Shell) with Metasploit, deploying a C2 listener, and mitigating the vulnerability by…
 cyberark/kubesploit
Kubesploit is a cross-platform post-exploitation HTTP/2 Command & Control server and agent written in Golang, focused on containerized environments.
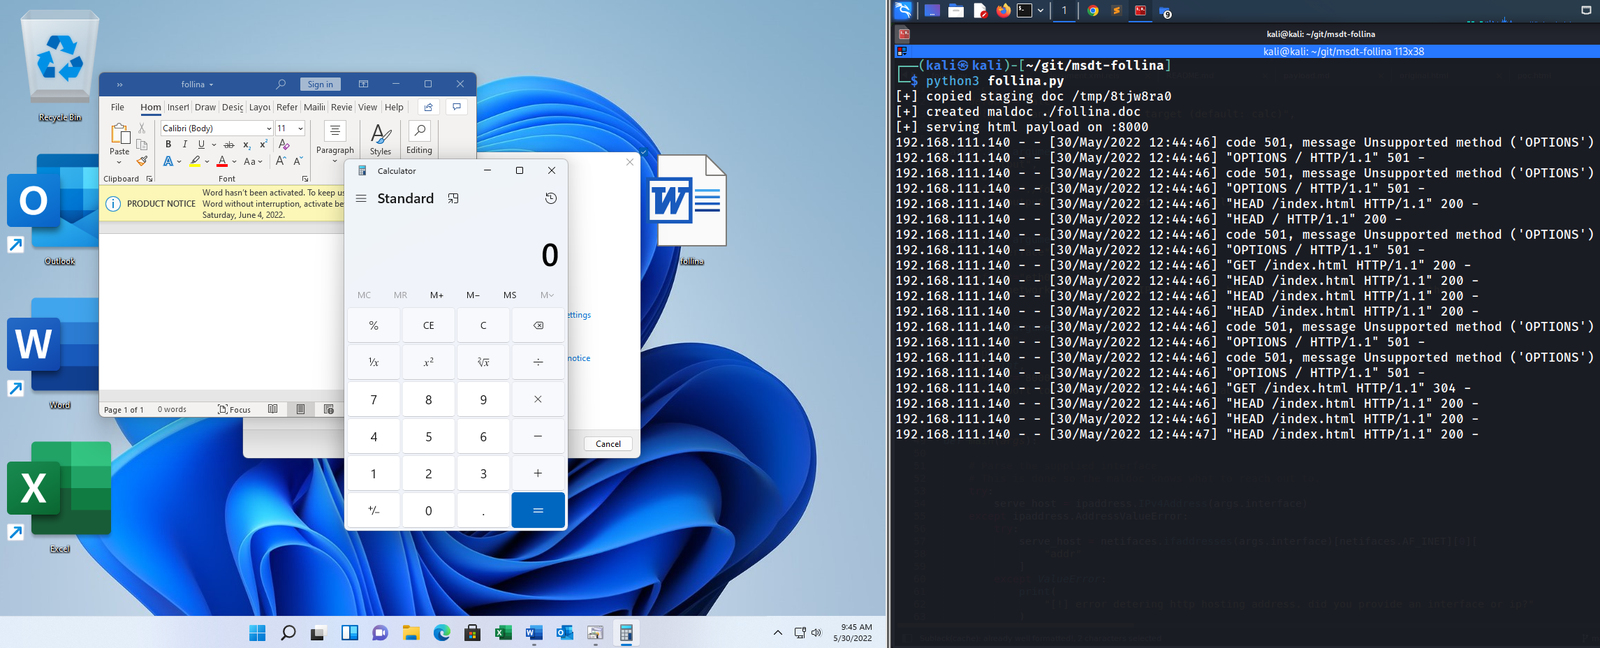 johnhammond/msdt-follina
Generates a malicious Microsoft Word document exploiting the MS-MSDT 'Follina' vulnerability to execute arbitrary commands or stage payloads via an…