
CVE-2023-33246
 0xkayala/cve-2023-33246
Exploits Apache RocketMQ brokers vulnerable to CVE-2023-33246 remote code execution and checks targets via IP, CIDR, or file input.
exploitationinformation-gatheringpenetration-testing+3
2
0xkayala/cve-2023-33246Exploits Apache RocketMQ brokers vulnerable to CVE-2023-33246 remote code execution and checks targets via IP, CIDR, or file input.
 cypholab/evilact
Fast scanner for detecting and confirming Next.js RCE vulnerabilities (CVE-2025-55182 & CVE-2025-66478).
 mbadanoiu/cve-2024-22275
CVE-2024-22275: Partial File Read in VMware vCenter Server
 randomrobbiebf/cve-2024-10245
Relais 2FA <= 1.0 - Authentication Bypass
 itpatjidr/cve-2022-41040
SSRF exploit payloads and reconnaissance dorks for CVE-2022-41040 targeting Microsoft Exchange Autodiscover endpoint with Burp Collaborator…
 g-rubert/cve-2020-9460
Proof-of-concept for a stored cross-site scripting (XSS) vulnerability in Octech Oempro 4.7–4.11 via the CampaignName parameter in Campaign.Create.
 87achrafg-stack/cve-2026-5513
CVE-2026-5513 — Bookly ≤ 27.2 Stored XSS via Cookie
 keraattin/cve-2026-35616
Detection toolkit for CVE-2026-35616, a pre-authentication API bypass in FortiClient EMS. Includes Python scanner and Nmap NSE script for identifying…
 tihmstar/freepw_tc7200eploit
Technicolor TC7200 - Credentials Disclosure CVE : CVE-2014-1677
 daryllundy/cve-2025-5054
Python-based vulnerability detector for CVE-2025-5054 (Apport race condition) on Ubuntu. Checks Apport version, core dump configuration, and SUID…
 identity-threat-labs/cve-2024-6387-vulnerability-checker
This Python script checks for the CVE-2024-6387 vulnerability in OpenSSH servers. It supports multiple IP addresses, URLs, CIDR ranges, and ports.…
 adanikamal/cve-2025-0282
Ivanti Connect Secure, Policy Secure & ZTA Gateways - CVE-2025-0282
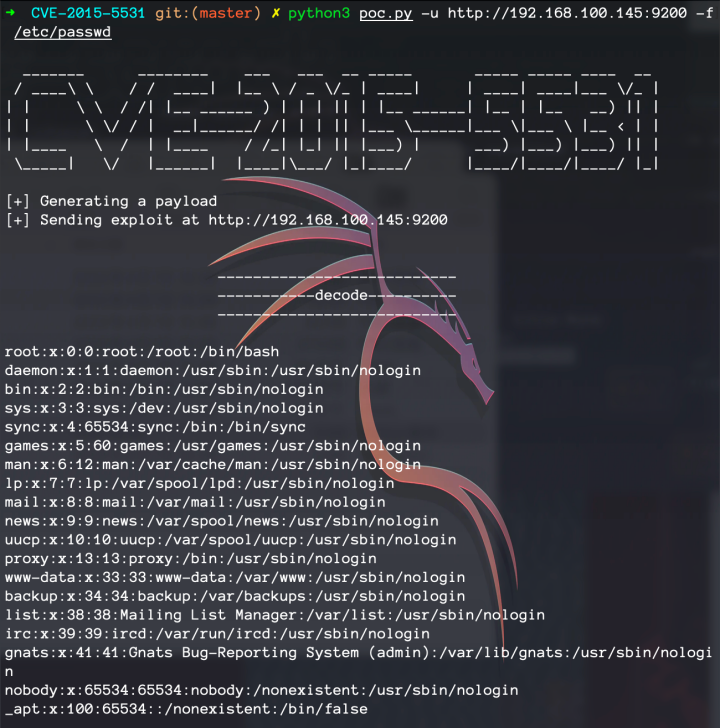 moch3n/cve-2015-5531-poc
Proof-of-concept exploit for CVE-2015-5531, a directory traversal vulnerability in Elasticsearch 1.6.1 and earlier, allowing remote file read via…
 ipk1/cve-2023-29489.py
a pyhton script to test all results from shodan for cPanel CVE-2023-29489, credits to @assetnote, I just automate
 itres-labs/cve-2025-1868
CVE-2025-1868: Advanced IP Scanner & Advanced Port Scanner NTLM Leakage HTTP Tester
 halencarjunior/f5scan
CVE-2020-5902 scanner for F5 BIG-IP with Shodan host discovery, LFI file reading, and remote command execution capabilities.
 gh0st0ne/rdpscan-bluekeep
A quick scanner for the CVE-2019-0708 "BlueKeep" vulnerability.
 avento/cve-2024-8522
LearnPress – WordPress LMS Plugin <= 4.2.7 - Unauthenticated SQL Injection via 'c_only_fields'