
CVE-2026-42089
 0xmrma/cve-2026-42089
A local package installation helper trusted caller-supplied package names too much. In yeoman-environment, missing generators could be installed…
code-analysiseducationexploitation+3
0xmrma/cve-2026-42089A local package installation helper trusted caller-supplied package names too much. In yeoman-environment, missing generators could be installed…
 shams-ul-mehmood/cve-2018-7600-drupalgeddon2-rce
Educational CVE-2018-7600 exploit project combining a Python RCE PoC, isolated Docker Drupal lab, payload research, and mitigation documentation for…
 shahdawadfallah-sys/cybersecurity-capstone-project
Cybersecurity Capstone Project completed during the NCSC Nashama CyberCamp 11, delivered in collaboration with IT Security C&T. The project…
 balochkainat160-cyber/cs50-cybersecurity
CS50's Introduction to Cybersecurity final project on React2Shell (CVE-2025-55182)
 smarttfoxx/cve-2025-45778
A stored cross-site scripting (XSS) vulnerability in The Language Sloth Web Application v1.0 allows attackers to execute arbitrary javascript or HTML…
 nithylesh/web-application-firewall-
This project demonstrates a Web Application Firewall (WAF) simulation using Flask and a vulnerability checker for CVE-2017-5638. The WAF middleware…
 stavrosgns/text4shellpayloads
This project includes a python script which generates malicious commands leveraging CVE-2022-42889 vulnerability
 winslowe/cve-2024-4309-analysis
BGT-Pentest-LAB Final Project: Xiaomi HyperOS System Updater OTA Signature Verification Bypass (CVE-2024-4309) Deep Analysis.
 jeffreybxu/five-nights-at-follina-s
A Fullstack Academy Cybersecurity project examining the full cycle of the Follina (CVE-2022-30190) vulnerability, from exploit to detection and…
 subhdotsol/cve-2025-55182
This project provides a fully functional demonstration of CVE-2025-55182 (React2Shell) - a critical Remote Code Execution vulnerability in React…
 majaktech/apache-struts-cve-2017-5638-project
Attack and Defense course project focused on CVE-2017-5638 analysis, exploitation, and mitigation.
 ypl6/heaplens
CMPT733 Cybersecurity Lab II Project: GDB plugin for heap exploits inspired by CVE-2021-3156
 kmeps4/cverev3
Proof-of-concept testing environment for CVE-2021-30858, based on Google Project Zero's root cause analysis of an in-the-wild iOS exploit.
 jfs-jfs/cve-2026-37067
Incorrect access control in /vfm-admin/admin-panel/view/save-cvs.php in Veno File Manager Project 4.4.9 allows an unauthenticated attacker to extract…
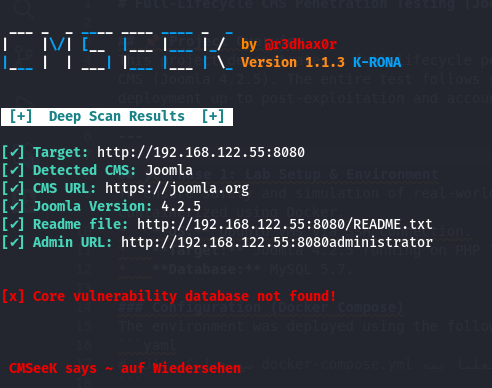 marwan651/joomla-cms-full-lifecycle-pentest
A comprehensive full-lifecycle penetration testing project on Joomla 4.2.5 exploiting CVE-2023-23752 inside a Dockerized lab environment
 nullbyte8080/cve-2026-36226
Benign proof-of-concept for CVE-2026-36226, a cross-site scripting vulnerability in Advantech WebAccess/SCADA 8.0-2015.08.16 Admin Dashboard Create…
 dampedcoast/exploiting-a-vulnerability-using-reverse-shell
This project simulates a real-world attack-and-defend scenario across two virtual machines. You will exploit a critical pre-authentication RCE…
 canomer/cve-2026-36980-kernel-bsod-dos-poc
Project Date : Feb 2026 / Discovered a buffer overflow vulnerability in the IOCTL handler of the kernel driver. The vulnerability allows an…