

WinPwn
 s3cur3th1ssh1t/winpwn
Automation for internal Windows Penetrationtest / AD-Security
exploitationpenetration-testingpenetration-testing-frameworks+4
3.7k
s3cur3th1ssh1t/winpwnAutomation for internal Windows Penetrationtest / AD-Security
 tr0uble-maker/poc-bomber
利用大量高威胁poc/exp快速获取目标权限,用于渗透和红队快速打点
 chudry/xerror
fully automated pentesting tool

 bb00/zer0dump
Abuse CVE-2020-1472 (Zerologon) to take over a domain and then repair the local stored machine account password.
 straightblast/my-poc-exploits
PoC exploits I wrote. They're as is and I will not offer support
 mogwaisec/mjet
Mogwai Java Management Extensions (JMX) Exploitation Toolkit
 zcgonvh/cve-2017-7269
fixed msf module for cve-2017-7269
 0x09al/cve-2017-11882-metasploit
This is a Metasploit module which exploits CVE-2017-11882 using the POC released here : https://embedi.com/blog/skeleton-closet-ms-office-vulnerabilit…
 mstxq17/cve-2021-1675_rdl_lpe
PrintNightMare LPE提权漏洞的CS 反射加载插件。开箱即用、通过内存加载、混淆加载的驱动名称来ByPass Defender/EDR。
 straight-tamago/nocamerasound
CVE-2022-46689
 taroballzchen/cve-2022-41040-metasploit-proxynotshell
the metasploit script(POC) about CVE-2022-41040. Microsoft Exchange are vulnerable to a server-side request forgery (SSRF) attack. An authenticated…
 chacka0101/exploits
Exploits project Hacking Command Center
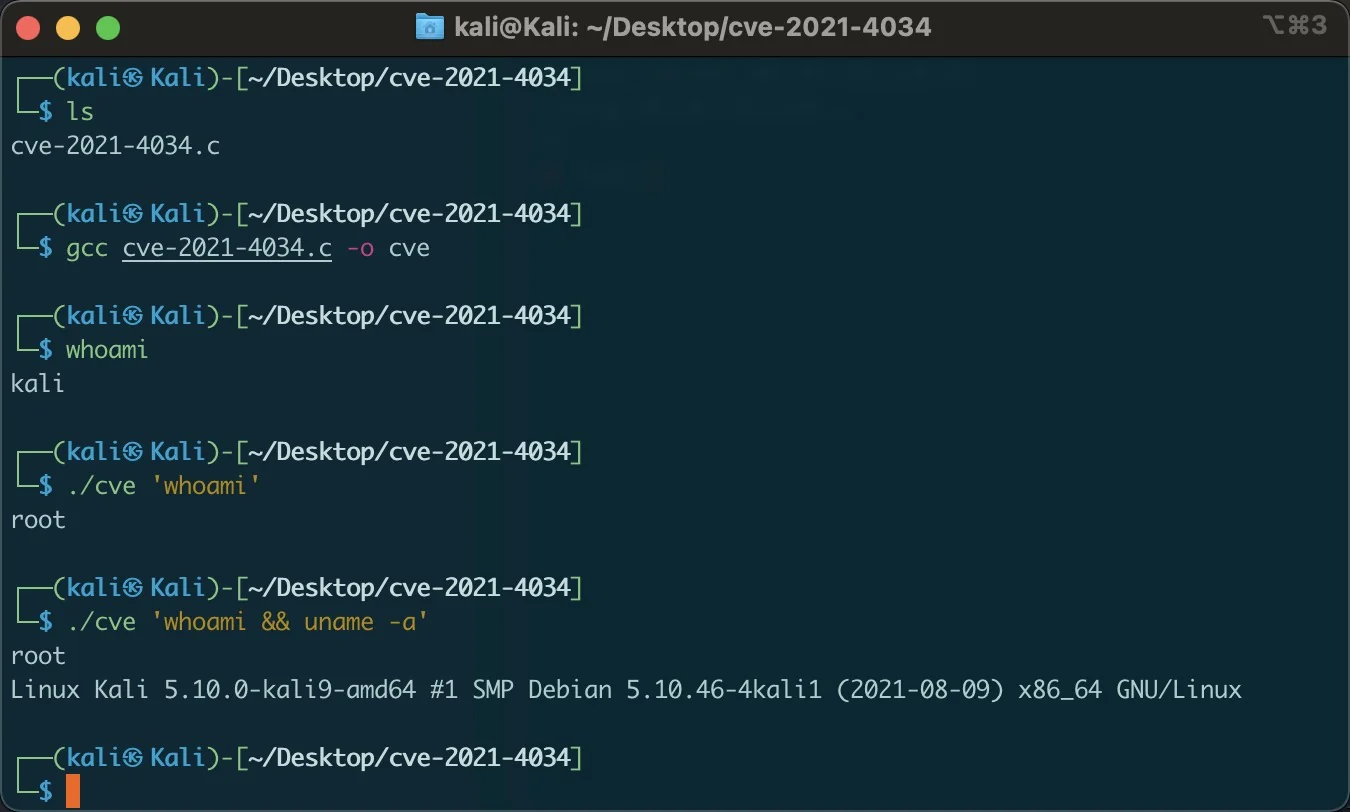 zhzyker/cve-2021-4034
polkit pkexec Local Privilege Vulnerability to Add custom commands

 jgoyd/glass-cage-ios18-cve-2025-24085-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, bypassing LockDown mode protection by exploiting ImageIO (CVE-2025-43300), then…
 taroballzchen/cve-2021-22005-metasploit
the metasploit script(POC/EXP) about CVE-2021-22005 VMware vCenter Server contains an arbitrary file upload vulnerability
 ssrsec/cve-2020-11651-cve-2020-11652-exp
CVE-2020-11651&&CVE-2020-11652 EXP