

CVE-2022-22963
 jrbh4ck/cve-2022-22963
Proof-of-concept exploit for CVE-2022-22963, a Spring Cloud Function SpEL injection leading to remote code execution. Includes a shell script for…
educationexploitationremote-access-tool+2
jrbh4ck/cve-2022-22963Proof-of-concept exploit for CVE-2022-22963, a Spring Cloud Function SpEL injection leading to remote code execution. Includes a shell script for…
 erranfenech/cve-2021-21300
Proof-of-concept exploit for CVE-2021-21300, a Git vulnerability enabling arbitrary code execution during clone operations. Includes shell script for…
 fnatalucci/cve-2021-41773-rce
Shell script to exploit CVE-2021-41773, an Apache HTTP Server path traversal and remote code execution vulnerability.
 prodrious/cve-2020-13942
Shell script to exploit CVE-2020-13942, a remote code execution vulnerability in Apache Unomi, with pre-scanning via httpx or httprob.
 otissymbos/cve-2021-44228-log4shell-
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) remote code execution vulnerability in Apache Log4j. Includes shell script for testing and…
 lhamouche/bash-exploit-for-cve-2022-0739
Shell script exploit for CVE-2022-0739, an unauthenticated SQL injection in BookingPress < 1.0.11. Automates exploitation against vulnerable…
 jahithoque/cve-2024-10914-exploit
Shell script exploiting CVE-2024-10914 for remote OS command injection in D-Link DNS-320, DNS-320LW, DNS-325, and DNS-340L devices via cgi_user_add.
 j4f9s5d2q7/cve-2023-43208-mirthconnect
Shell script to identify and exploit CVE-2023-43208, an unauthenticated remote code execution vulnerability in NextGen Mirth Connect before version…
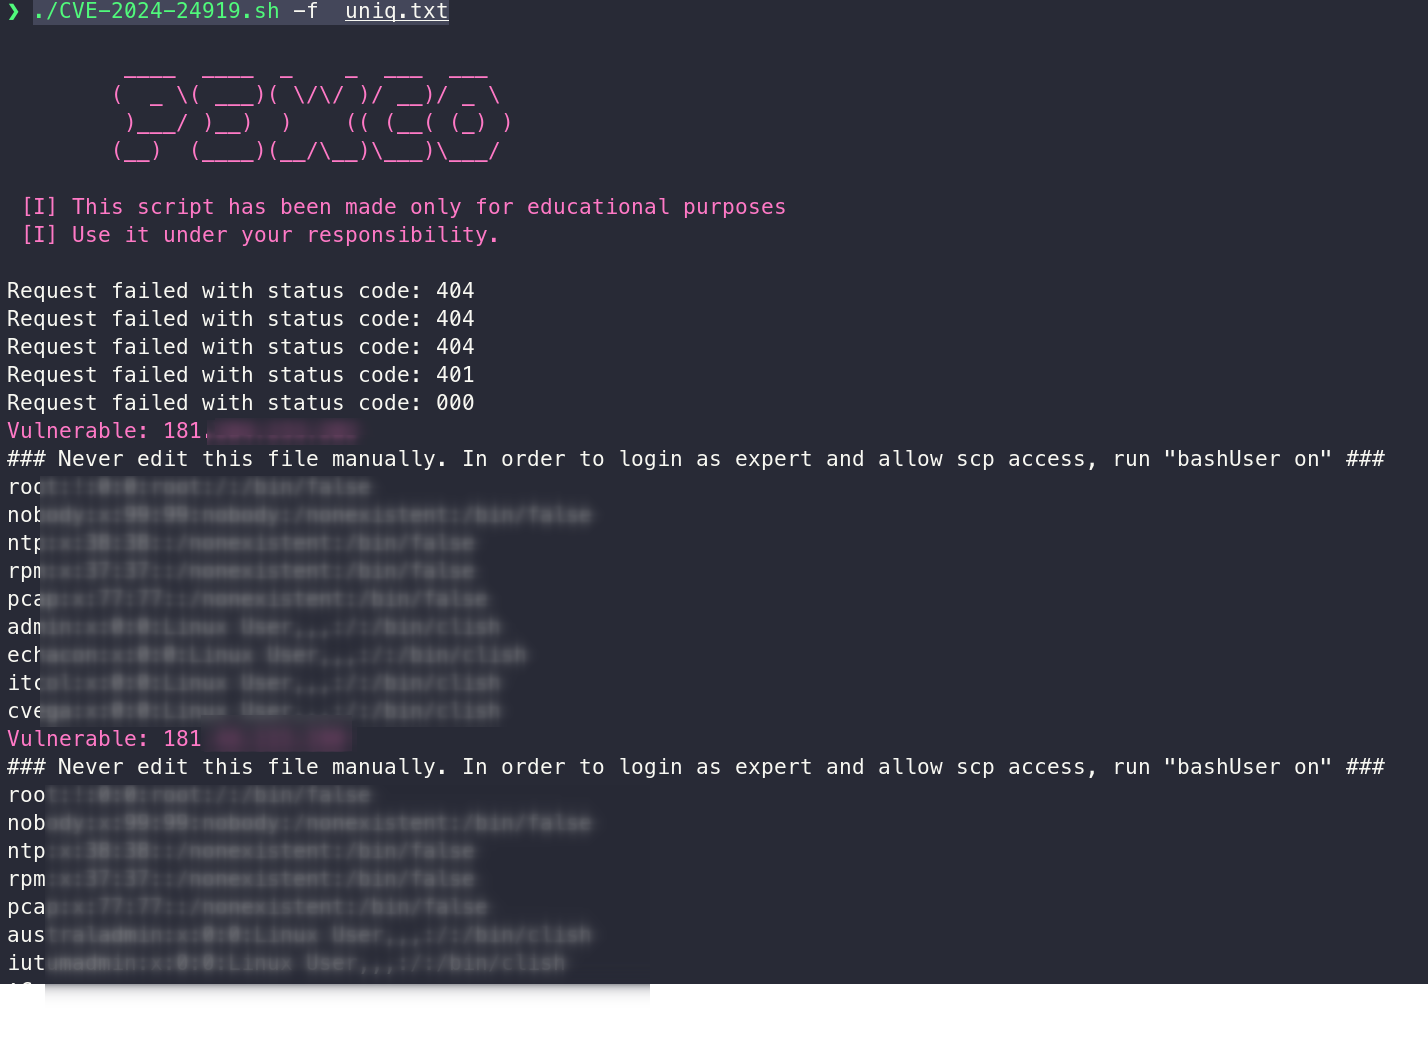 p3wc0/cve-2024-24919
Shell script to exploit CVE-2024-24919, enabling path traversal file retrieval from Check Point Security Gateways. Supports single IP and batch…
 lukechilds/reverse-shell
On-demand reverse shell service that auto-detects target environment and executes appropriate payload for remote access during penetration tests.
 devploit/put2win
Script to automate PUT HTTP method exploitation to get shell
 atlassion/log4j-exploit-builder
Script to create a log4j (CVE-2021-44228) exploit with support for different methods of getting a reverse shell
 bhdresh/cve-2021-33766
ProxyToken (CVE-2021-33766) : An Authentication Bypass in Microsoft Exchange Server POC exploit
 marcingadz/spring-rce-poc
Testing CVE-2022-22968
 mantanhacker/mass-cve-2025-29306
Mass Exploit for CVE-2025-29306
 glynzr/cve-2023-50564
Pluck v4.7.18 - Remote Code Execution (RCE)
 prodigiousmind/revshell
Pentestmonkeys' PHP reverse shell with dynamic host and port passing through GET request parameters
 regantemudo/cve-2024-25641-exploit-for-cacti-1.2.26
Automated exploit for CVE-2024-25641 targeting Cacti 1.2.26. Achieves remote code execution via authenticated arbitrary file write in the Package…