

CVE-2023-6444-POC
 wayne-ker/cve-2023-6444-poc
Proof of concept on Unauthenticated Administrator Email Disclosure CVE-2023-6444
exploitationinformation-gatheringpenetration-testing+2
wayne-ker/cve-2023-6444-pocProof of concept on Unauthenticated Administrator Email Disclosure CVE-2023-6444
 geraldoalcantara/cve-2023-49973
Customer Support System 1.0 - Cross-Site Scripting (XSS) Vulnerability in "email" field/parameter on "customer_list" Page
 ahmedmansour93/event-id-263-rule-name-soc287---arbitrary-file-read-on-checkpoint-security-gateway-cve-2024-24919-
🔍 Just wrapped up an incident report on a Phishing Alert (Event ID 257, SOC282). Enhancing my expertise in email threat detection and response! 🚨…
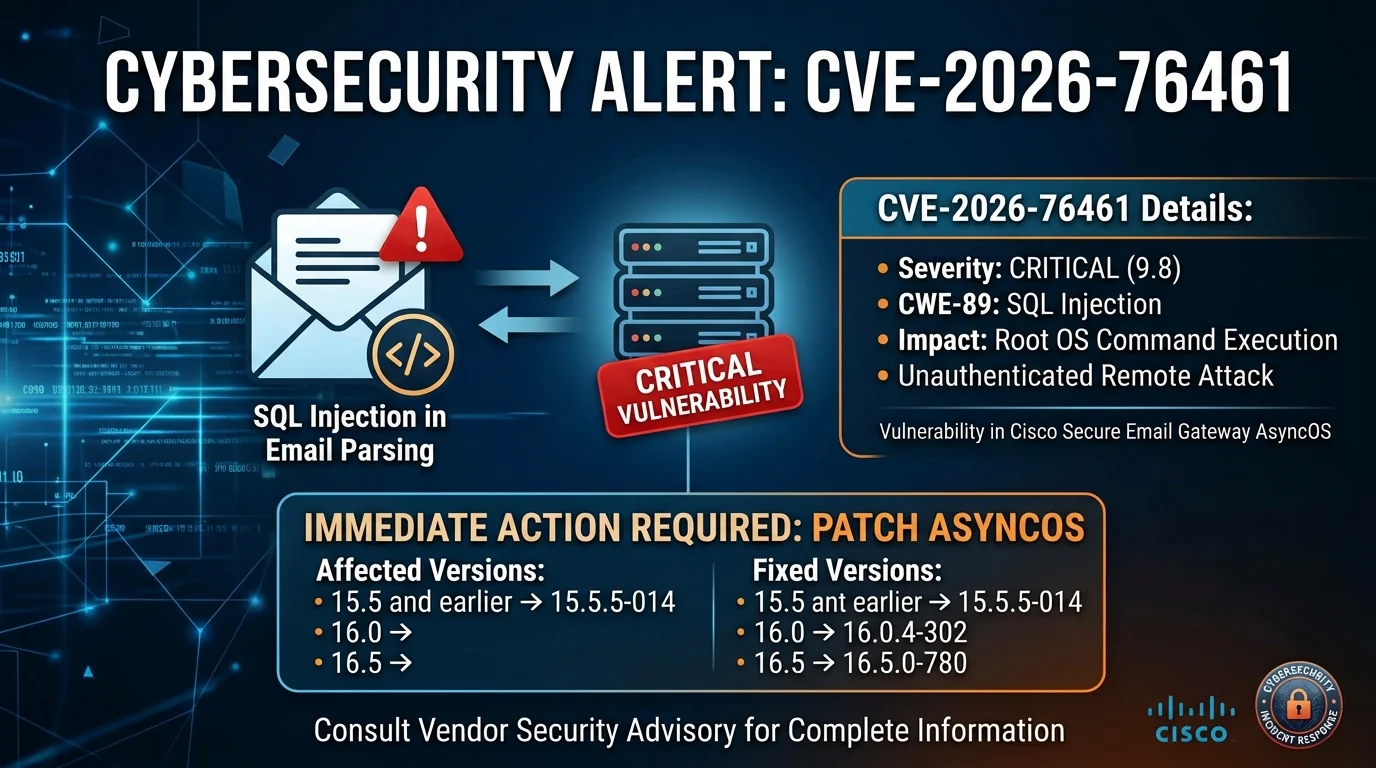 0xblackash/cve-2026-76461
Research repository for CVE-2026-76461, a critical SQL injection in Cisco Secure Email Gateway leading to root RCE, with detection rules, mitigation…
 djackreuter/cve-2023-23397-poc
C# PoC exploit for CVE-2023-23397 that sends malicious Outlook meeting invites with a UNC path trigger for NTLM credential theft.
 amirzargham/cve-2024-37383-exploit
Roundcube mail server exploit for CVE-2024-37383 (Stored XSS)
 random-robbie/cve-2020-0688
cve-2020-0688
 vlad902/hacking-team-windows-kernel-lpe
Previously-0day exploit from the Hacking Team leak, written by Eugene Ching/Qavar.
 duy-31/cve-2023-51764
Postfix SMTP Smuggling - Expect Script POC
 therealjunior/mtk-su-reverse-cve-2020-0069
reversing mtk-su
 prot0tw/keycloak_cve-2026-18963_poc
This repo is poc of cve-2026-18963. Please use it on legal products (lab, local,...).
 randomrobbiebf/cve-2023-32117
Integrate Google Drive <= 1.1.99 - Missing Authorization via REST API Endpoints
 leakix/sentryexploit
CVE-2023-38035 Recon oriented exploit, extract company name contact information
 error-inside/cve-2026-10520
Root-Level RCE via OS Command Injection in Ivanti Sentry
 ahrixia/cve-2023-30256
QloApp 1.5.2: Vulnerable to XSS on two Parameter (email_create and back)
 skraft9/cve-2025-29471
Stored XSS in Nagios Log Server 2024R1.3.1
 motikan2010/cve-2021-34646
CVE-2021-34646 PoC
 h1ssbl1tz/blind-trust-cve-2024-21413-research
A security research tool for simulating targeted phishing campaigns using CVE-2024-21413 (Moniker Link).