
gitlab-ssrf
 cs4239-u6/gitlab-ssrf
Demonstration of CVE-2018-19571: GitLab SSRF CVE
command-and-controleducationexploitation+3
cs4239-u6/gitlab-ssrfDemonstration of CVE-2018-19571: GitLab SSRF CVE
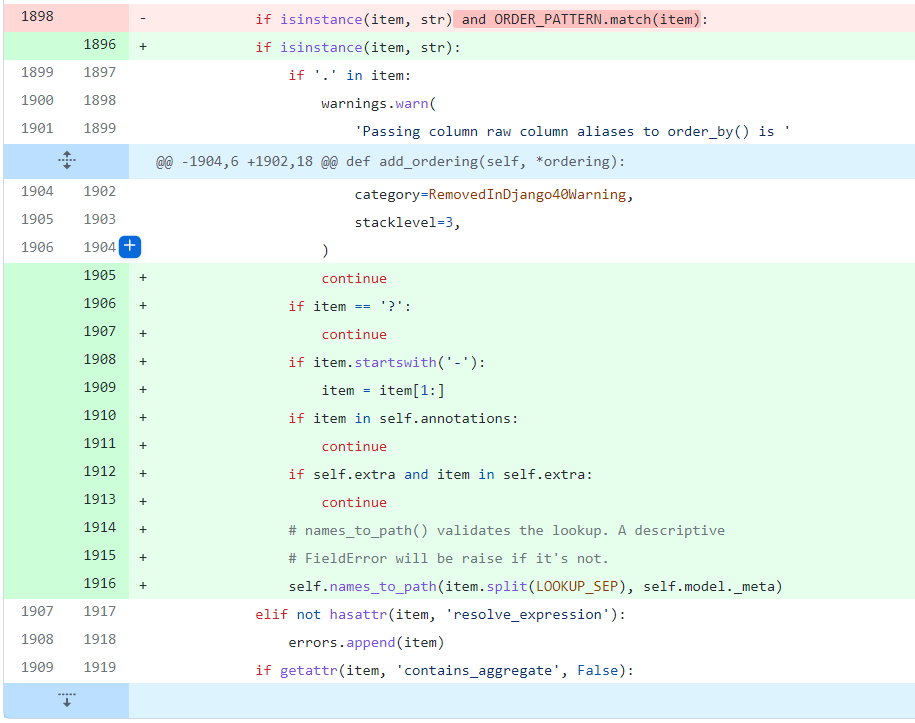 luuanhduc/cve-2021-35042
Django SQL injection vulnerability
 cs4239-u6/node-pdf-generator-ssrf
An example of CVE-2020-7740
 melardev/cve-2019-5418
Docker-based sandbox to reproduce and test CVE-2019-5418 Ruby on Rails path traversal vulnerability via crafted Accept headers.
 rockmelodies/cve-2022-42889
CVE-2022-42889 dockerized sample application (Apache Commons Text RCE)
 marioalejos-cs/dirtycow-lab
Explotación vulnerabilidad Dirty COW (CVE-2016-5195) en Ubuntu 16.04.1.

 intercept6/cve-2023-45857-demo
CVE-2023-45857の挙動を確認するデモ
 noah4puppy/cve-2024-21262
THREE different reproduction, WORKDIR, EXEC & RUNC.
 romanutti/log4shell-vulnerable-app
This repository contains a Spring Boot web application vulnerable to CVE-2021-44228, known as log4shell.
 l1uk/nextjs-middleware-exploit
Research on Next.js middleware vulnerability (CVE-2025-29927) allowing authorization bypass and potential exploits.
 mahajian/cve-2019-9978
Docker-based lab environment to simulate and exploit CVE-2019-9978, a remote code execution vulnerability in WordPress Social Warfare plugin versions…
 asfandalimemon25/cve-2023-50164analysis-
CVE-2023-50164 An attacker can manipulate file upload params to enable paths traversal and under some circumstances this can lead to uploading a…
 dnr6419/cve-2021-24545
WordPress Plugin HTML Author Bio description XSS
 battleofthebots/dejavu
Challenge based on CVE-2021-22204 where users send a malicious file to a web application to gain RCE
 cyberharsh/php-unit-cve-2017-9841
Docker-based lab to reproduce CVE-2017-9841, a remote code execution vulnerability in PHPUnit's eval-stdin.php when installed under a web root.