
CVE-2025-24054
 untouchable17/cve-2025-24054
Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
exploitationpassword-crackingpayload-generation+4
2
untouchable17/cve-2025-24054Windows File Explorer Zero Click NTLMv2-SSP Hash Disclosure
 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 petergabaldon/cve-2024-1346
Weak MySQL database root password in LaborOfficeFree affects version 19.10. This vulnerability allows an attacker to calculate the root password of…
 kaihaochen04/monikerlinktest
cve-2024-21413
 fathanahhidayati/https-github.com-xaitax-cve-2024-21413-microsoft-outlook-remote-code-execution-vulnerability
Proof-of-concept exploit for CVE-2024-21413, a Microsoft Outlook remote code execution vulnerability. Demonstrates NTLM credential leakage and RCE…
 midpipps/cve-2020-1472-easy
A simple implementation/code smash of a bunch of other repos
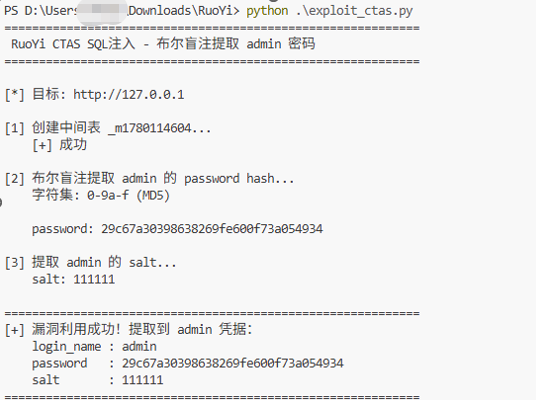 chinesespeople/cve-2026-52614
There is a SQL injection vulnerability in the backend of Ruoyi v4.8.3
 x3rx3ssec/cve-2025-2011
Exploit for CVE-2025-2011
 c4cnm/exploit_cve-2021-24762
This repo shows an exploit to CVE-2021-24762. This is an Blind SQLi exploit that, on default config, greps the admin password.
 moneertv/cve-2023-23397
CVE-2023-23397 C# PoC
 fevra-dev/claimjumper
Professional JWT security testing toolkit. Analyze, crack, forge, and exploit JSON Web Tokens with 15+ vulnerability checks, 100k secret wordlist,…
 dionissh/cve-2024-21413
Proof-of-concept exploit for Microsoft Outlook RCE (CVE-2024-21413) with SMTP-based phishing email delivery, malicious RTF attachment generation, and…
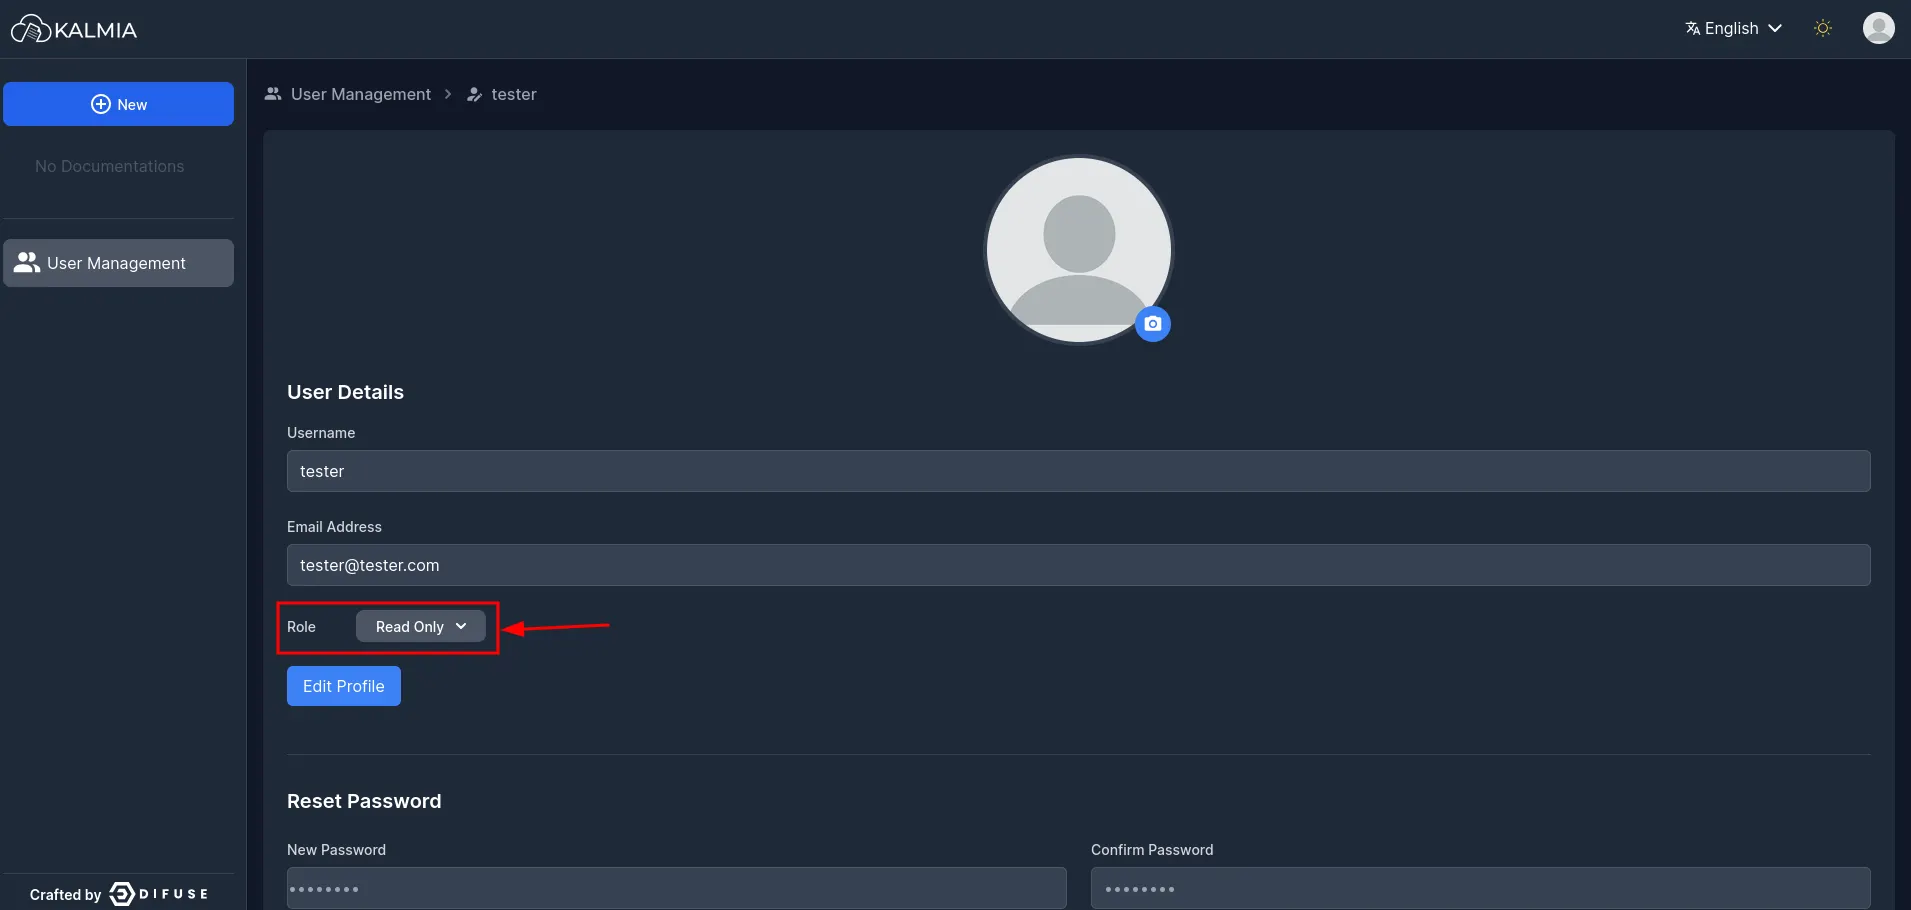 noxurge/cve-2025-65900
DifuseHQ Kalmia CMS version 0.2.0 contains an Incorrect Access Control vulnerability in the /kal-api/auth/users API endpoint. Due to insufficient…
 tim-karov/cmsms-sqli
Python3 exploit for CVE-2019-9053 (CMS Made Simple <= 2.2.9 SQLi). No deps, time-based blind SQLi → admin creds dump. HTB Writeup owned.
 kyomahooin/cve-2008-6970
Blind SQL injection brute force.
 boon-rekcah/cms-made-simple-2.2.9-cve-2019-9053
Python 3 exploit for CVE-2019-9053, an unauthenticated SQL injection in CMS Made Simple 2.2.9, that extracts admin credentials and optionally cracks…
 byrek/cve-2019-9053
Improved code of Daniele Scanu SQL Injection exploit
 c3rrberu5/zerologon-to-shell
Automated exploit script combining CVE-2020-1472 (ZeroLogon) with evil-winrm to gain a remote shell on vulnerable Windows Domain Controllers.