
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
112 results
CVE-2015-6967 preview

CVE-2015-6967

GitHubcuerv0x/cve-2015-6967

Python exploit for CVE-2015-6967 targeting Nibbleblog with a reverse shell payload. Executes authenticated remote code execution via file upload…

exploitationpayload-generationpenetration-testing+3
1 year ago
CVE-2024-23346 preview

CVE-2024-23346

GitHubmawk0235/cve-2024-23346

This is an exploit for CVE-2024-23346 that acts as a "terminal" (tested on chemistry.htb)
command-and-controlexploitationpenetration-testing+2
1 year ago
POC-CVE-2022-28117 preview

POC-CVE-2022-28117

GitHubkimstars/poc-cve-2022-28117

Proof-of-concept exploit for CVE-2022-28117 enabling arbitrary file read via file:/// URI scheme in Navigate CMS, with authentication support.
exploitationinformation-gatheringpenetration-testing+2
2 years ago
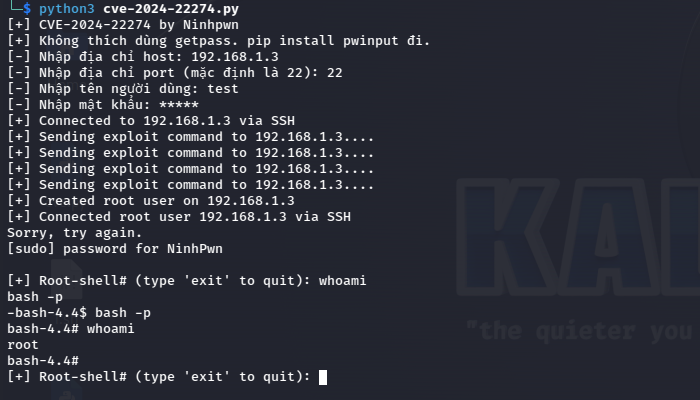
CVE-2024-22274 preview

CVE-2024-22274

GitHubninhpn1337/cve-2024-22274

Exploit for CVE-2024-22274 that creates a privileged user and spawns a root SSH shell on a target host using provided credentials.
exploitationpayload-generationpenetration-testing+3
2 years ago
Confluence-Question-CVE-2022-26138- preview

Confluence-Question-CVE-2022-26138-

GitHubvulnmachines/confluence-question-cve-2022-26138-

Atlassian Confluence Server and Data Center: CVE-2022-26138
exploitationinformation-gatheringpassword-attacks+3
34 years ago
CVE-2007-2447 preview

CVE-2007-2447

GitHubb33m0x00/cve-2007-2447

CVE-2007-2447 samba remote code execution

command-and-controlexploitationpenetration-testing+2
4 years ago
massh-enum preview

massh-enum

GitHubtrimstray/massh-enum

OpenSSH 2.3 up to 7.4 Mass Username Enumeration (CVE-2018-15473).
exploitationinformation-gatheringnetwork-security+3
1596 years ago
CVE-2018-15473 preview

CVE-2018-15473

GitHubsait-nuri/cve-2018-15473

OpenSSH 2.3 < 7.7 - Username Enumeration

authenticationexploitationinformation-gathering+3
425 years ago
SUF preview

SUF

GitHubghostwalkr/suf

SSH Username Finder

exploitationinformation-gatheringvulnerability-analysis
67 years ago
CVE-2016-6210-Exploit preview

CVE-2016-6210-Exploit

GitHubjustlce/cve-2016-6210-exploit

OpenSSH Username Enumeration - CVE-2016-6210

authenticationexploitationinformation-gathering+3
37 years ago
xerteonlinetoolkits-rce preview

xerteonlinetoolkits-rce

GitHubbootstrapbool/xerteonlinetoolkits-rce

Unauthenticated Xerte Online Toolkits exploit. Requires knowing a valid username.
exploitationpayload-generationpenetration-testing+3
3 months ago
CVE-2026-11387 preview

CVE-2026-11387

GitHub1beelze/cve-2026-11387

Exploits unauthenticated privilege escalation in SMS Alert WooCommerce plugin (CVE-2026-11387) via OTP bypass and arbitrary password reset, with…

authenticationexploitationpassword-attacks+4
12 months ago
CVE-2018-9995 preview

CVE-2018-9995

GitHubcodeholic2k18/cve-2018-9995

DVR username password recovery.
exploitationinformation-gatheringiot-security+3
27 years ago
CVE-2023-2594 preview

CVE-2023-2594

GitHubthehackingverse/cve-2023-2594

A vulnerability, which was classified as critical, was found in SourceCodester Food Ordering Management System 1.0. Affected is an unknown function…
exploitationinformation-gatheringpenetration-testing+2
13 years ago
CVE-2026-8181 preview

CVE-2026-8181

GitHubx48ps/cve-2026-8181

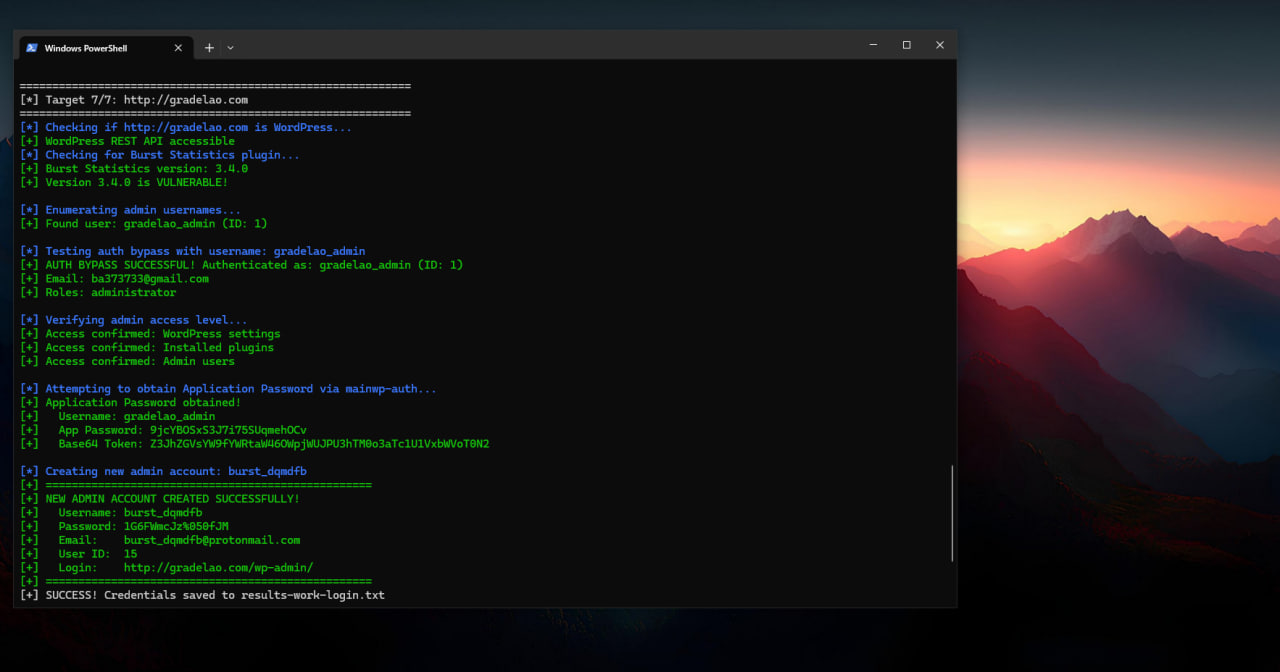
This vulnerability allows unauthenticated attackers who know a valid administrator username to impersonate that admin during REST API requests by…
api-securityauthenticationexploitation+3
3 months ago
CVE-2007-2447 preview

CVE-2007-2447

GitHubjosebarrios/cve-2007-2447

Remote Command Injection Vulnerability (CVE-2007-2447), allows remote attackers to execute arbitrary commands by specifying a Samba username…

command-and-controlexploitationpenetration-testing+2
16 years ago
CVE-2025-51396 preview

CVE-2025-51396

GitHubthewhiteevil/cve-2025-51396

LiveHelperChat <=4.61 - Stored Cross Site Scripting (XSS) via Telegram Bot Username
exploitationinformation-gatheringpenetration-testing+3
11 year ago
exploit_cve-2007-2447_again preview

exploit_cve-2007-2447_again

GitHubmrroma577/exploit_cve-2007-2447_again

just remeber how small mistake in santisize username could give yoy root access to the full machine

exploitationpenetration-testingprivilege-escalation+2
1 year ago
Previous1234567Next