
CVE-2024-6387
 mrmtwoj/cve-2024-6387
regreSSHion is a security tool designed to test for vulnerabilities related to CVE-2024-6387, specifically focusing on SSH and remote access…
exploitationnetwork-securitypenetration-testing+3
mrmtwoj/cve-2024-6387regreSSHion is a security tool designed to test for vulnerabilities related to CVE-2024-6387, specifically focusing on SSH and remote access…
 paulsec/twittor
A fully featured backdoor that uses Twitter as a C&C server
 aircrack-ng/mdk4
IEEE 802.11 Wi-Fi testing tool for protocol weakness exploitation, including beacon flooding, deauthentication, packet fuzzing, and IDS evasion.…
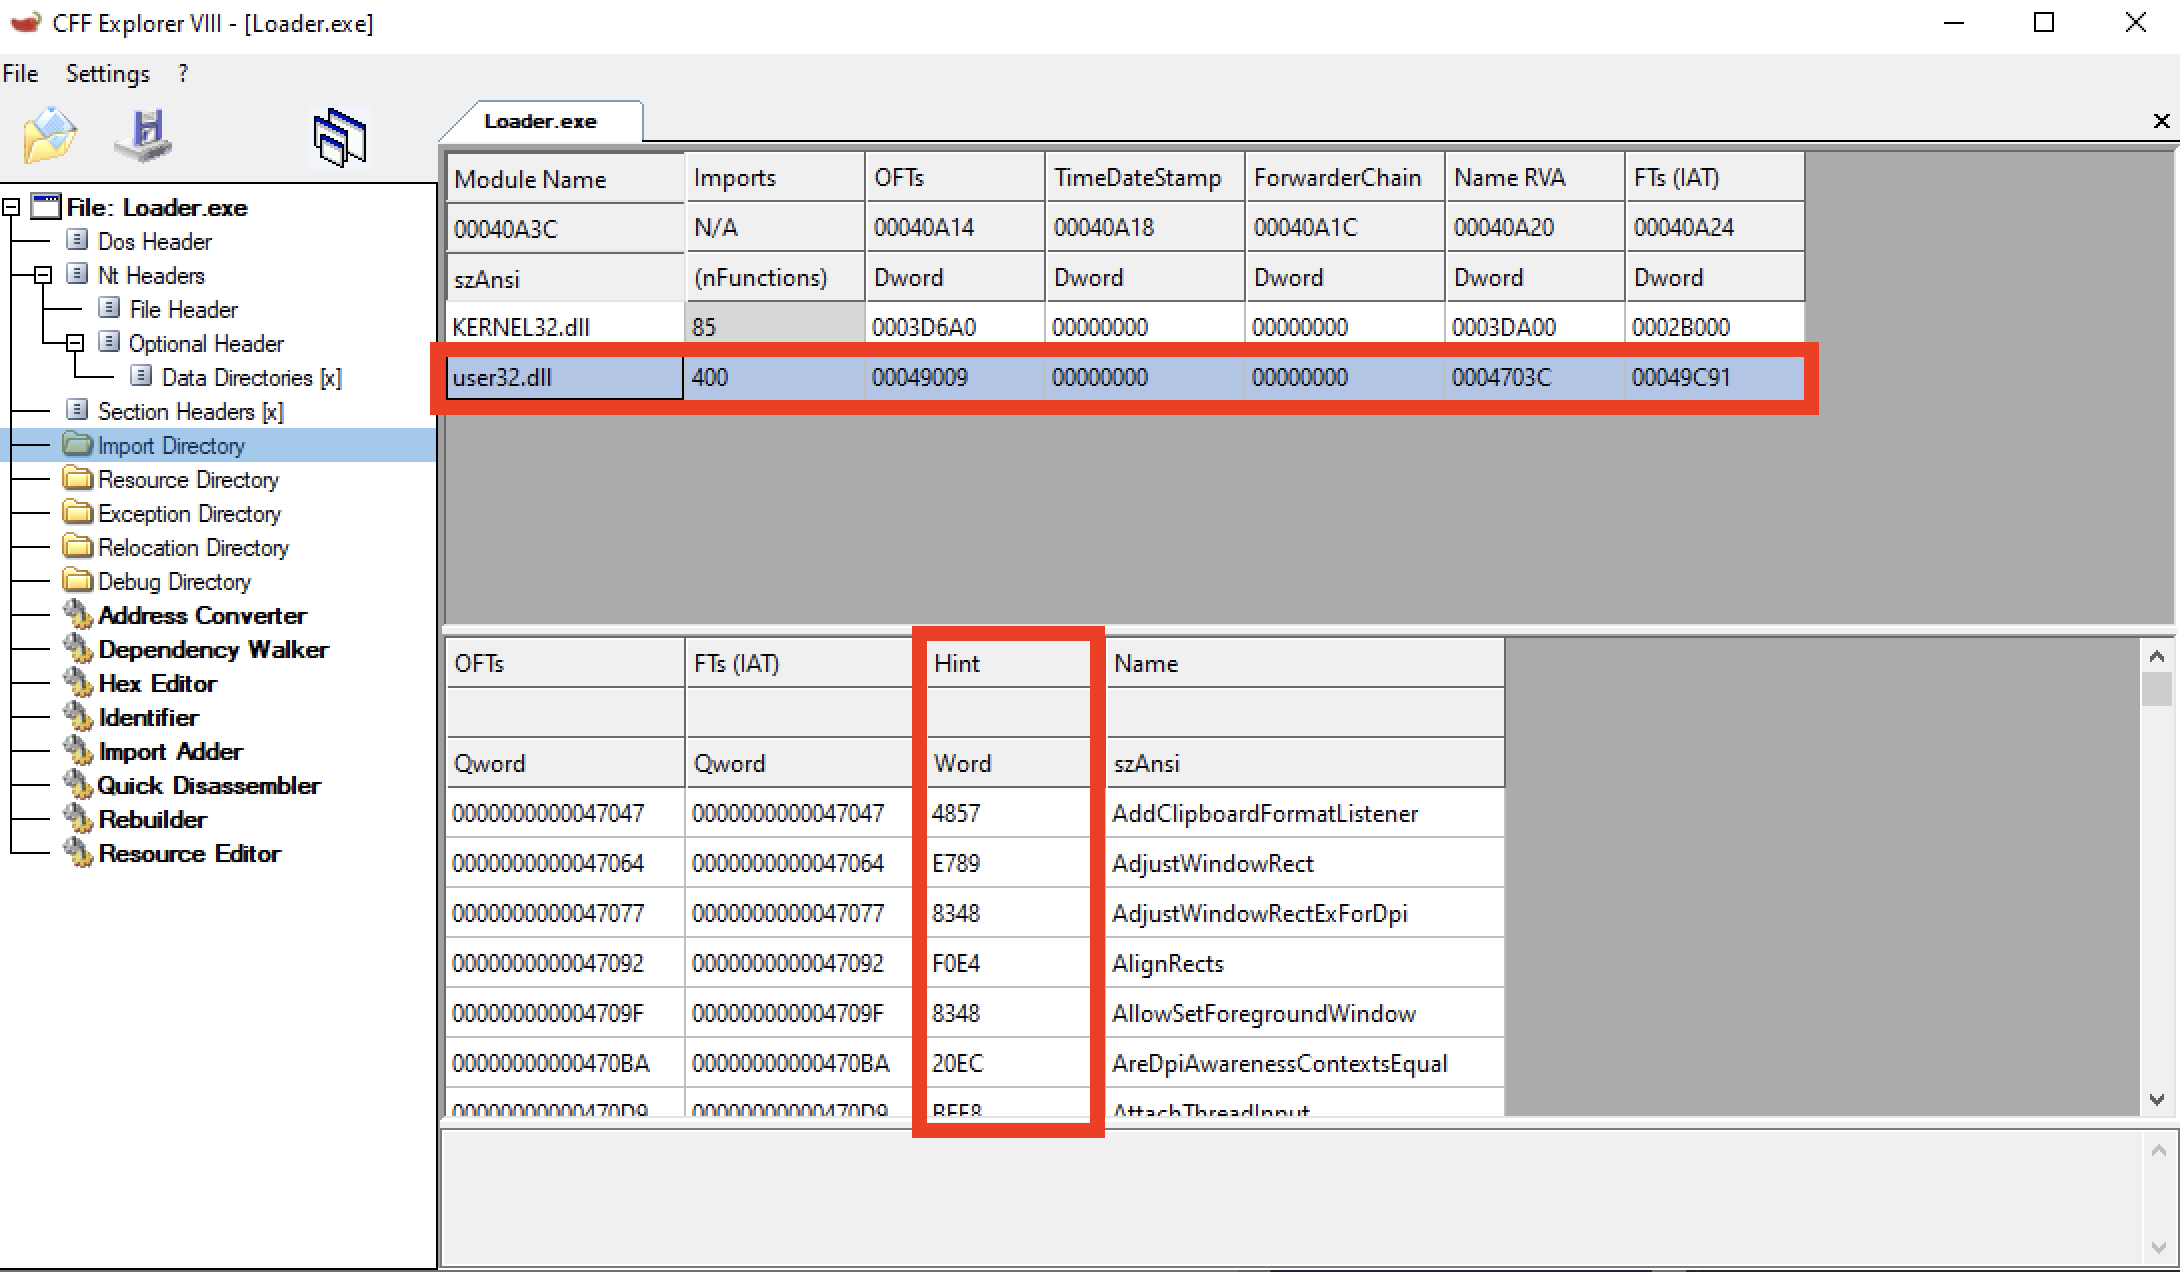 frkngksl/hintinject
A PoC project for embedding shellcode to Hint/Name Table
 0xc4r/cve-2026-21508_poc
Proof-of-concept for CVE-2026-21508, demonstrating a DLL hijacking attack on Windows 11 that escalates privileges by loading a crafted DLL into…
 finngineering/apxutil
A tool to manipulate Schneider Electric PLC archive files
 geniuszly/cve-2022-46080
it is script that enables Telnet on routers by sending a specially crafted request. The script allows users to specify the router's URL, Telnet port,…
 gagaltotal/cve-2026-10523-ivanti-sentry
Proof-of-concept detection tool for Ivanti Sentry authentication bypass and remote code execution vulnerabilities (CVE-2026-10520, CVE-2026-10523).…
 ihenakaarachchi/debian11-dirty_pipe-patcher
A Simple bash script that patches the CVE-2022-0847 (dirty pipe) kernel vulnerability on Debian 11
 f7p-h4nn1b4l/cve-2018-9995-dvr-credentials-extractor
This project demonstrates the publicly disclosed CVE-2018-9995 vulnerability found in multiple embedded DVR devices.
 jbooz1/cve-2017-0213
A version of CVE-2017-0213 that I plan to use with an Empire stager
 some-1hing/cve-2018-16763
Python tool for analyzing CVE-2018-16763 in FUEL CMS with cleaner response parsing and interactive vulnerability checking.
 dahalsamir/cve-2011-2523-exploit
Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…
 donkey0xshot/cve-2017-11882-blocker
Kernel-mode Windows driver that blocks CVE-2017-11882 exploitation by intercepting process creation and denying malicious child processes spawned by…
 jkim72403/cs4277-cve-path-traversal-apache-http-server
We hope to reproduce CVE-2021-41773 to deepen our understanding of real-world cybersecurity vulnerabilities so that we can be knowledgeable about…
 jip-0-0-0-0-0/cve-2024-38063-scanner
A Python tool leveraging Shodan and Scapy to identify and exploit Windows systems vulnerable to CVE-2024-38063, enabling targeted Denial of Service…
 spyx/cve-2019-17240
Go-based brute-force tool exploiting Bludit bruteforce mitigation bypass (CVE-2019-17240) for automated password cracking against admin login pages.
 radoi-teodor/cve-2023-21768-dse-bypass
Windows kernel exploit for CVE-2023-21768 that bypasses Driver Signature Enforcement (DSE) to load unsigned drivers, enabling local privilege…