
Ratpack-1
 epicosy/ratpack-1
Lightweight Java toolkit for building high-performance web applications, with a focus on exploiting CVE-2019-17513 for security testing and…
exploitationpenetration-testingvulnerability-analysis+2
epicosy/ratpack-1Lightweight Java toolkit for building high-performance web applications, with a focus on exploiting CVE-2019-17513 for security testing and…
 eunomie/cve-2022-42889-check
Lightweight Java-based checker for CVE-2022-42889 (Apache Commons Text RCE). Quickly validates if a target is vulnerable to the Text4Shell remote…
 renukaselvar/lua_cve-2020-24370
Lightweight, embeddable scripting language with a fast interpreter, supporting procedural, functional, and object-oriented programming.
 renukaselvar/lua_cve-2020-24370_afterpatch
Lightweight embeddable scripting language with a C API, supporting procedural, functional, and data-driven programming.
 senzee1984/micr0_shell
micr0shell is a Python script that dynamically generates Windows X64 PIC Null-Free reverse shell shellcode.
 graph-x/davscan
Fingerprints servers, finds exploits, scans WebDAV. May or may not also make coffee.
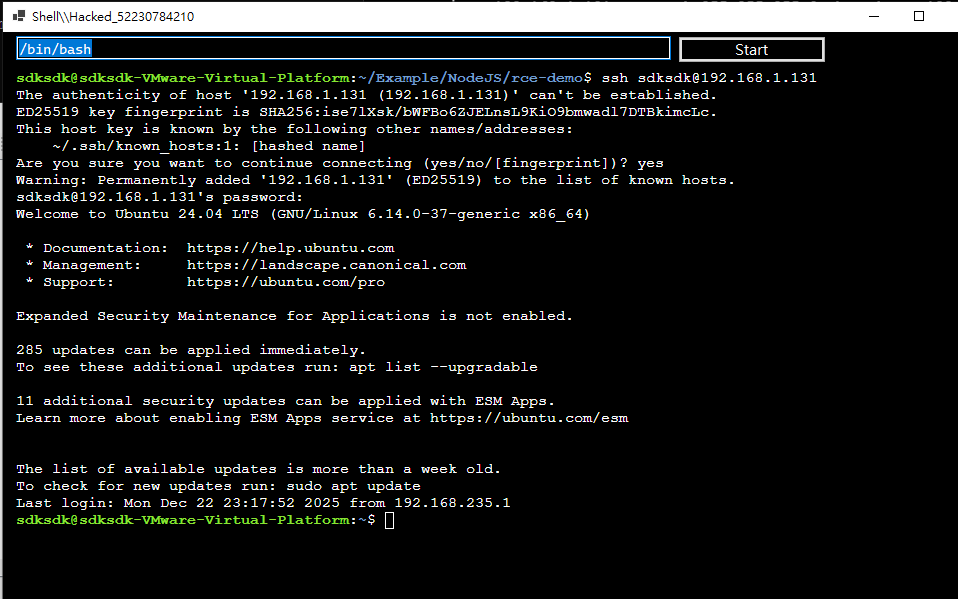 iss4cf0ng/eden-rat
An open-source Linux GUI-based Remote Access Tool developed in C# with a Python payload, intended for legitimate penetration testing and…
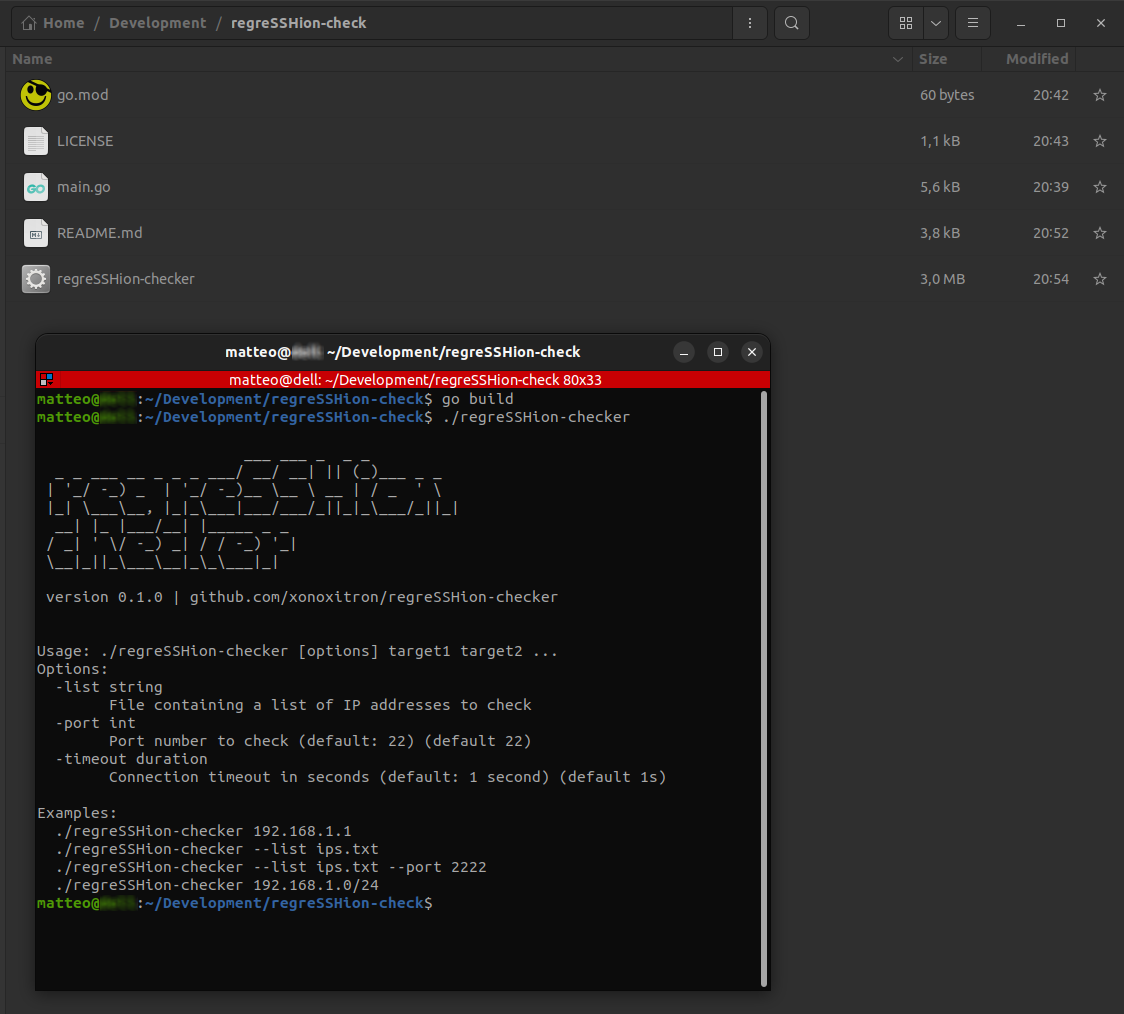 xonoxitron/regresshion-checker
Quickly identifies servers vulnerable to OpenSSH 'regreSSHion' (CVE-2024-6387).
 j4ck3lsyn-gen2/cve-2026-63030-wp2r00t
A fully red-team(offensive security) weaponized variant of wp2shell, built for authorized penetration testing & educational purposes.
 vanigori/cve-2023-38545-sample
Dockerfile containing all the necessary setup files to demo the exploit
 george0papasotiriou/cve-2026-6789-stack-buffer-overflow-in-embedded-tls-certificate-parser
Stack buffer overflow PoC in an embedded TLS certificate parser using a crafted X.509 SAN extension for remote code execution on IoT and industrial…
 kayl22/cve-2025-8110-gogs-rce
GOGS RCE cve-2025-8110 python script that automates the whole attack chain of creating a repository with a symlink file pointing to .git/config and…
 skimask1690/wisedelete
Windows utility that uses the vulnerable WiseDelfile64.sys driver affected by CVE-2025-66680 to enable kernel-assisted file deletion.
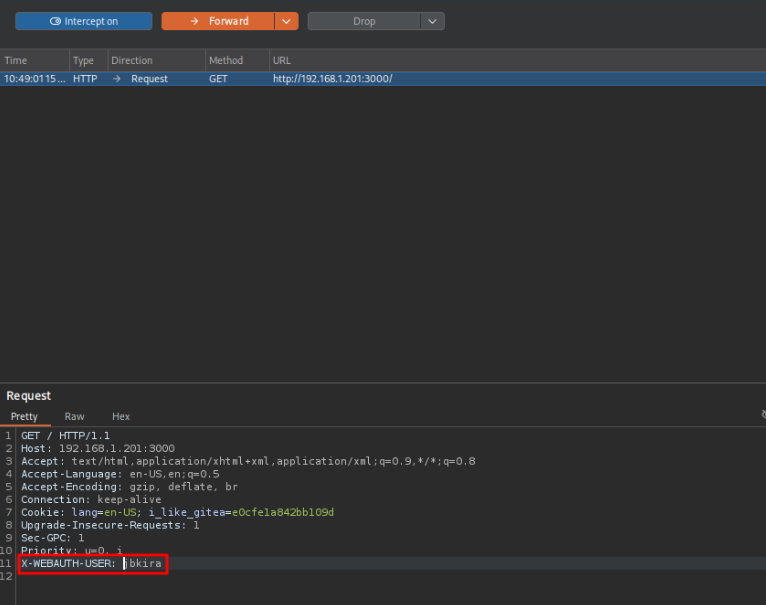 judgedbykira/cve-2026-20896-gitea-authentication-bypass
An explanation and PoC to exploit CVE-2026-20896 Authentication Bypass Vulnerability on Gitea. Being able to steal session tokens for valid users in…
 slayerkkkk/cve-2025-46817-poc
C-based exploit for CVE-2025-46817, a Redis integer overflow vulnerability, enabling crash detection and potential RCE via Lua unpack() payload.
 sangleshubham/react-security-cve-2025-55182-exploit
NodeJS-based exploit script and scanner for the React Server Components "React2Shell" vulnerability (CVE-2025-55182).
 anggatechi/mass-scanner-cve-2026-2631
Async mass-checker for authorized internal testing of CVE-2026-2631 exposure.
 medaz-sploit/cve-2025-9074-docker-desktop-api-escape-poc
Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…