

cve-2021-41773
 mightysai1997/cve-2021-41773
Exploit script for Apache HTTP Server 2.4.49/2.4.50 path traversal and remote code execution (CVE-2021-41773). Includes Docker-based reproduction…
educationexploitationpenetration-testing+3
mightysai1997/cve-2021-41773Exploit script for Apache HTTP Server 2.4.49/2.4.50 path traversal and remote code execution (CVE-2021-41773). Includes Docker-based reproduction…
 samanzamani/copy-fail-checker
Read-only Bash checker for the Copy Fail Linux kernel vulnerability (CVE-2026-31431)
 dungsocool/cve-2024-23897
Docker-based lab and exploit script for CVE-2024-23897, a critical arbitrary file read in Jenkins CLI via args4j expandAtFiles, with steps to chain…
 liamromanis101/cifswitch-check
Detection script for CIFSwitch - CVE-2026-46243
 be-innova/cve-2021-42392-exploit-lab
Educational lab demonstrating CVE-2021-42392 RCE in H2 Database via CREATE ALIAS, with Dockerized vulnerable server and Python exploit script for…
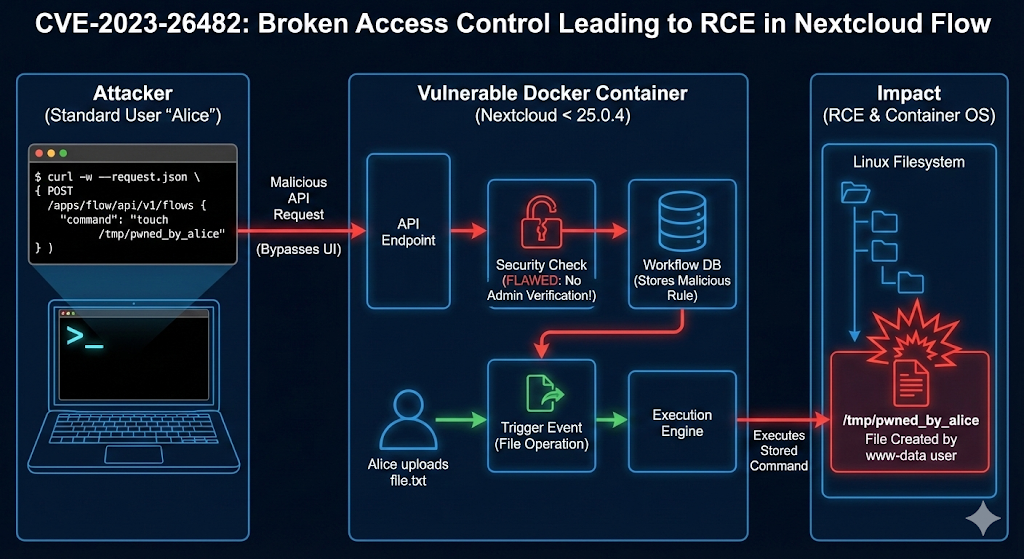 isabbii/poc---cve-2023-26482-rce-lab-nextcloud
Docker-based lab reproducing CVE-2023-26482 (Nextcloud RCE) with automated exploit script for educational vulnerability analysis and exploitation…
 minhluannguyen/cve-2020-7247-reproducer
Docker-based environment to reproduce CVE-2020-7247 (OpenSMTPD) with a Python exploit script for arbitrary command execution and reverse shell via…
 abraxas/cve-2026-75827
Proof-of-concept and lab for CVE-2026-75827, a Grav arbitrary file write via Blueprint dynamic-data error_log, with reproduction script and Docker…
 sne-m23-sn/vulnerable-docker-engine
This exploit offers an in-depth look at the CVE-2021-41091 security vulnerability and provides a step-by-step guide on how to utilize the exploit…
 mightysai1997/cve-2021-42013
Python script to detect and exploit CVE-2021-42013 path traversal and remote code execution in Apache 2.4.50, with bulk scanning and a Docker lab for…
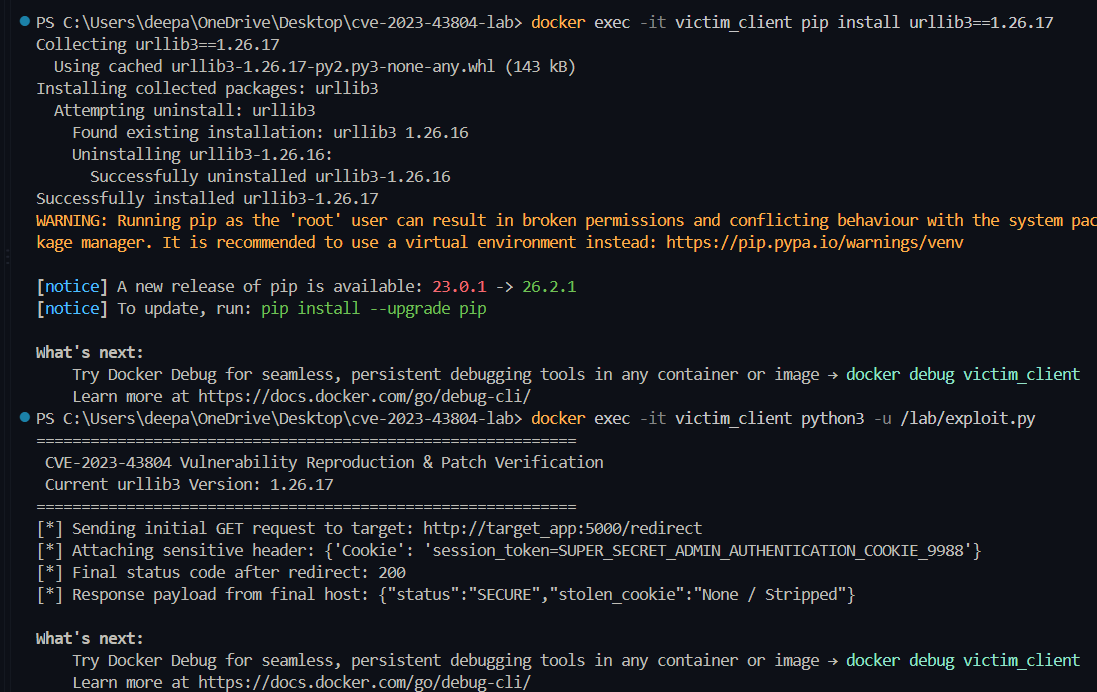 deepanshu-khurana/cve-2023-43804
Containerized three-tier lab reproducing CVE-2023-43804 urllib3 cookie leak via cross-origin redirects, with exploit script and patch verification.
 fimtow/cve-2021-24750
Demonstration of the WP Visitor Statistics plugin exploit
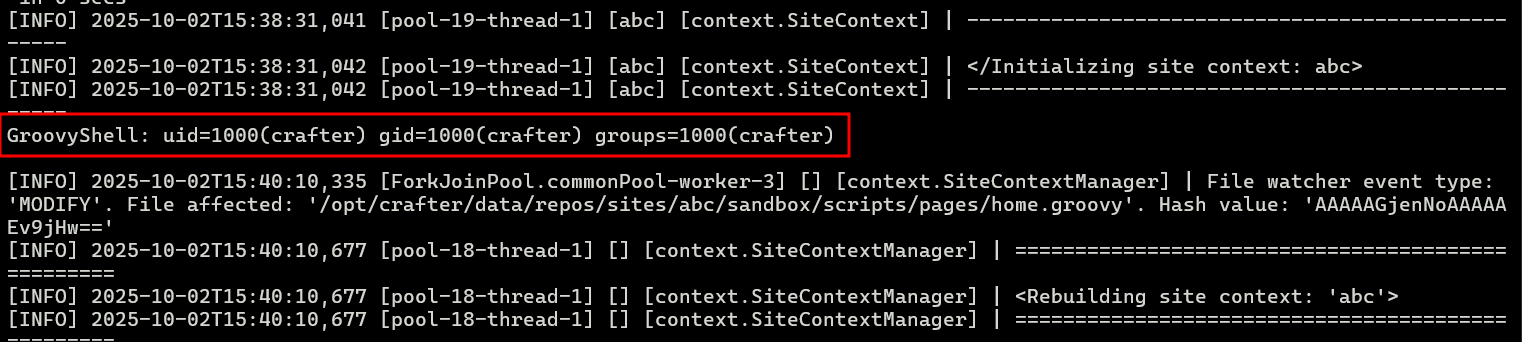 maestro-ant/craftercms-cve-2025-6384
PoC exploit for an authenticated RCE in CrafterCMS via Groovy sandbox bypass (CVE-2025-6384)
 trandonga3/poc-cve-2025-1094
Proof-of-concept exploit for CVE-2025-1094, a PostgreSQL psql SQL injection leading to RCE via libpq escaping bypass. Includes Docker environment,…
 george0papasotiriou/cve-2026-21008-kubernetes-service-account-token-mounted-in-hostpath
Proof-of-concept exploit for Kubernetes service-account token disclosure via hostPath mounts; includes vulnerable pod YAML and Python token-theft…
 devengpk/cve-2022-22965
Dockerized Spring4Shell (CVE-2022-22965) proof-of-concept with Python exploit script and webshell deployment for educational vulnerability testing.
 dinosn/cve-2026-3844
Proof-of-concept exploit for CVE-2026-3844, an unauthenticated arbitrary file upload leading to remote code execution in Breeze Cache <= 2.4.4.…
 nikeee/cve-2026-27607
Proof-of-concept exploit for CVE-2026-27607, a missing post-policy validation in RustFS, demonstrating the vulnerability with a Node.js script and…