
yaml-payload
 seal-sec-demo-2/yaml-payload
SnakeYAML CVE-2022-1471 exploit payload for demo
dynamic-analysis-sandboxingeducationexploitation+3
seal-sec-demo-2/yaml-payloadSnakeYAML CVE-2022-1471 exploit payload for demo
 captain4554/captain4554.github.io
🔍 Scan for CVE-2025-55182 vulnerabilities with a hybrid tool that combines static and dynamic analysis for improved security assessments.
 dbrumley/extract75-cve-2020-13995
Control flow hijack exploit for CVE-2020-13995 with Docker-based deployment and Mayhem fuzzing integration for automated vulnerability testing.
 shoucheng3/x-stream__xstream_cve-2020-26217_1-4-14-java77
Java library for XML serialization and deserialization, with a focus on the CVE-2020-26217 deserialization vulnerability exploit.
 horkimhab/cve-2026-39813
CVE-2026-39813 - Fortinet Sandbox - Draft
 moxie25/nanomq-memory-leak-research
Public advisory and technical analysis for CVE-2026-36590, a NanoMQ v0.24.9 denial-of-service vulnerability.
 rxerium/cve-2025-4427-cve-2025-4428
Detection for CVE-2025-4427 and CVE-2025-4428
 n0n-zer0/spring-boot-tomcat-cve-2025-24813
POC for CVE-2025-24813 using Spring-Boot
 shoucheng3/jenkinsci__workflow-cps-plugin_cve-2022-25173_2646-v6ed3b5b01ff1
Exploit for CVE-2022-25173 targeting Jenkins Pipeline Groovy Plugin's CPS interpreter sandbox bypass, enabling arbitrary code execution within…
 renukaselvar/expat_cve-2024-28757
C library for stream-oriented XML parsing with handler registration, supporting UTF-8/UTF-16 encoding, and autoconf-based build system. Includes…
 lohanichaten/log4j-cve-2021-44228
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) targeting Java applications via JNDI injection for remote code execution.
 adarshpv9746/text4shell--automated-exploit---cve-2022-42889
Automated exploit for CVE-2022-42889 (Text4Shell) with a vulnerable Dockerized app for testing and manual exploitation guidance.
 almkuznetsov/cve-2024-1441
Reproduces fuzzing and crash analysis for CVE-2024-1441 using AFL++ and CASR, with detailed setup and commands for libvirt.
 certcc/certfuzz
This project contains the source code for the CERT Basic Fuzzing Framework (BFF) and the CERT Failure Observation Engine (FOE).
 aftermathlabs/discord-crasher
Some bugs found via binary instrumentation and fuzzing
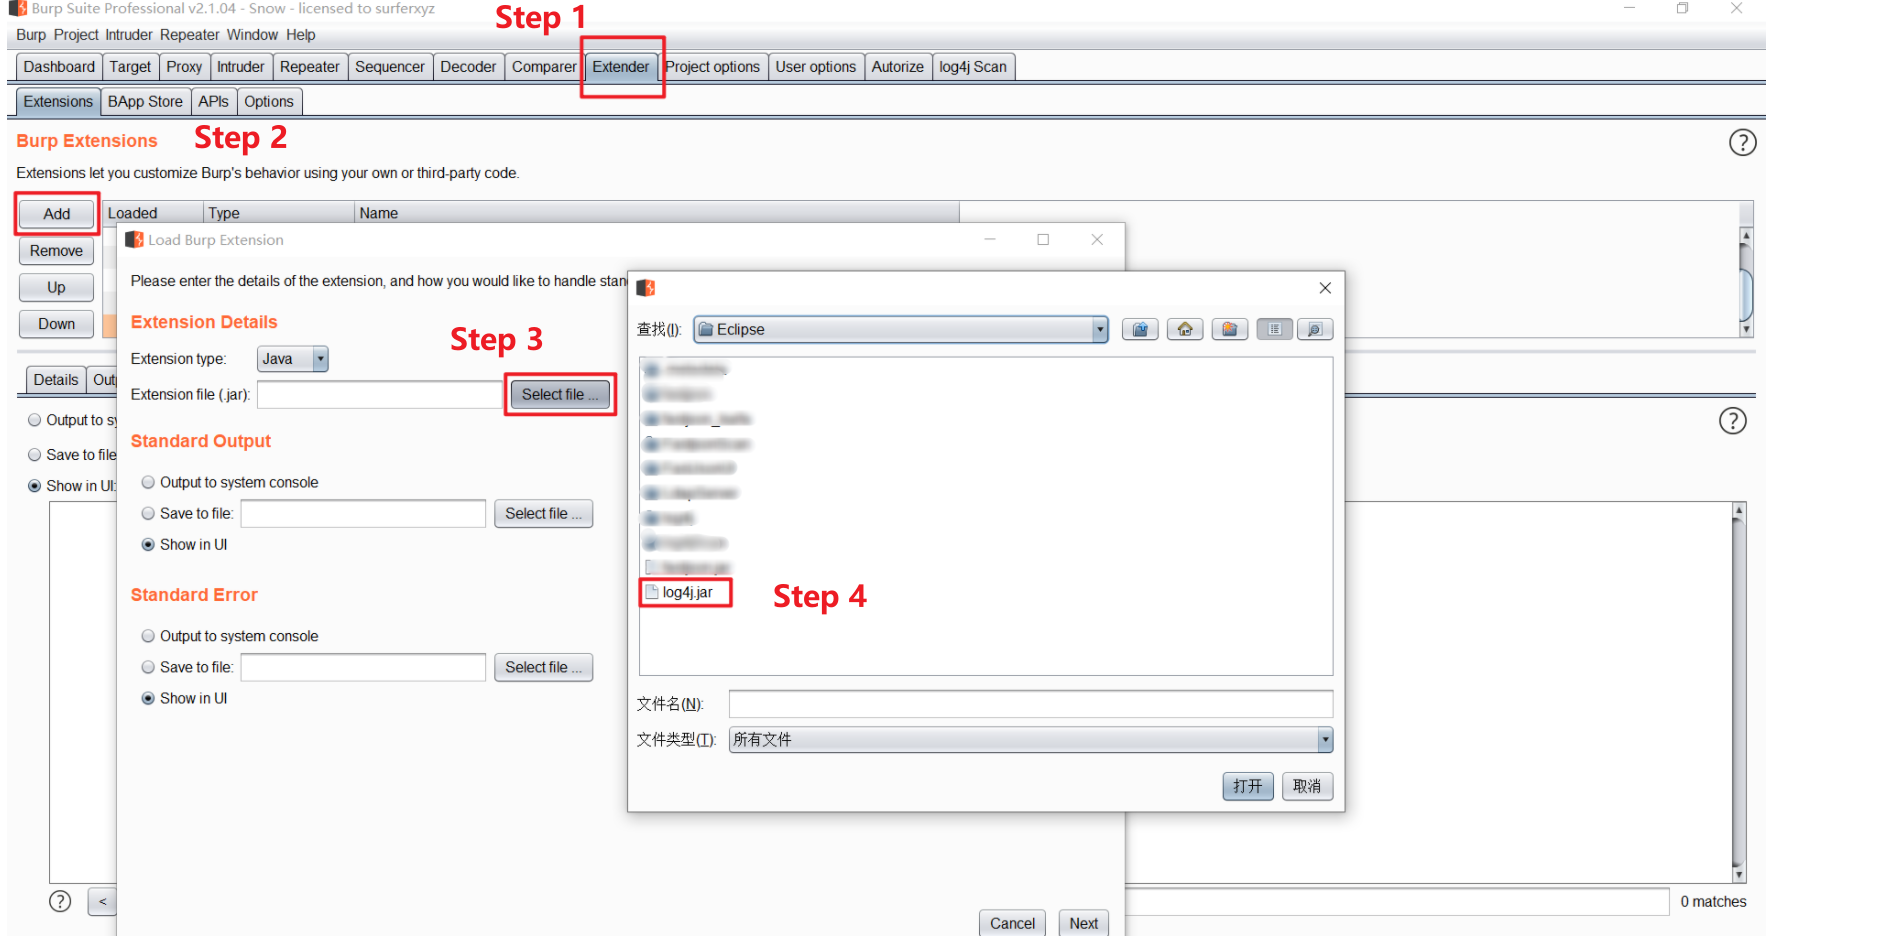 snow0715/log4j-scan-burpsuite
Log4j漏洞(CVE-2021-44228)的Burpsuite检测插件
 egkritsis/cve-2025-61303
Critical Vulnerability (9.8) - RecordedFuture Triage dynamic analysis engine can fail to record malicious behavior when samples produce very…
 aastikgakhar/cve-2025-55182-react2shell
Detects exposed React Server Components vulnerable to CVE-2025-55182 via RSC negotiation.