
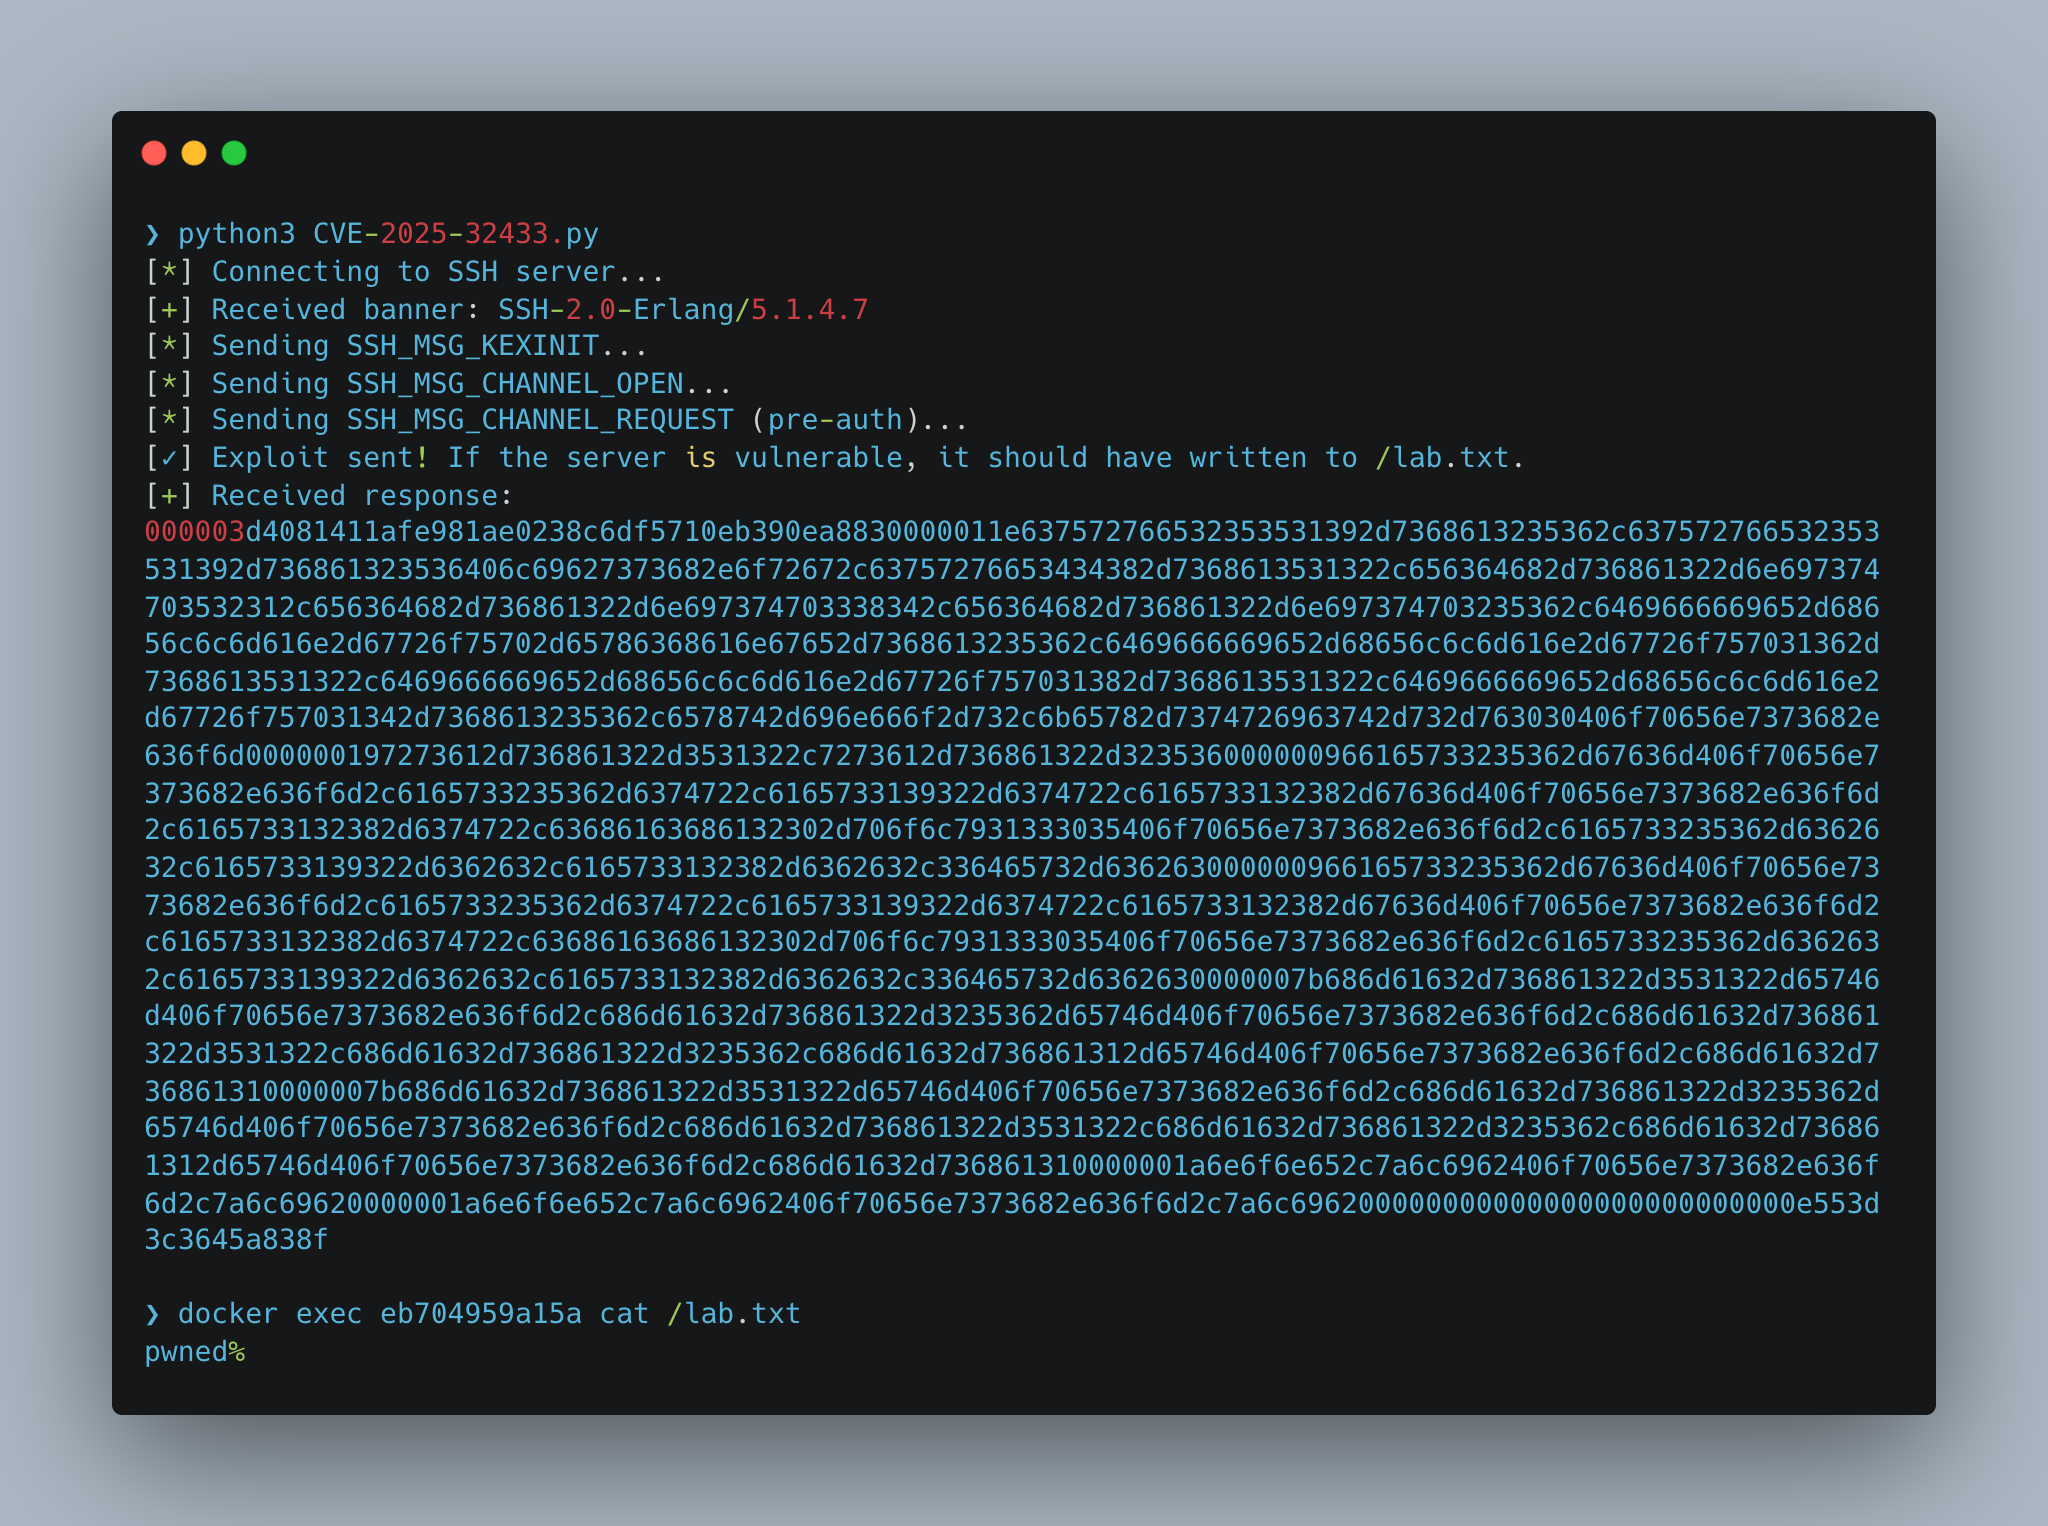
CVE-2025-32433.py
 yonathanpy/cve-2025-32433.py
CVE-2025-32433 PoC – SSH Protocol Python-based PoC for controlled lab testing of SSH message handling, channel operations, and pre-auth interactions.…
educationexploitationlabs-practice+3
2
yonathanpy/cve-2025-32433.pyCVE-2025-32433 PoC – SSH Protocol Python-based PoC for controlled lab testing of SSH message handling, channel operations, and pre-auth interactions.…
 skyejacobson/cyberhawkslab-telnetcve
Writeup/finding of CVE-2026-24061 within the Cyberhawks lab
 belmind/heartbleed
A collection of scripts and instructions to test CVE-2014-0160 (heartbleed). ❤️ 🩸
 yozarseef95/cve-2023-31595
IC Realtime ICIP-P2012T is vulnerable to Incorrect Access Control via an open port
 mbadanoiu/cve-2021-46366
CVE-2021-46366: Credential Bruteforce Attack via CSRF + Open Redirect in Magnolia CMS
 tankirat/cve-2017-5638
Educational analysis of Apache Struts 2 RCE vulnerability CVE-2017-5638, including exploit details, Equifax case study, and prevention measures.
 bishopfox/sliver
Adversary Emulation Framework
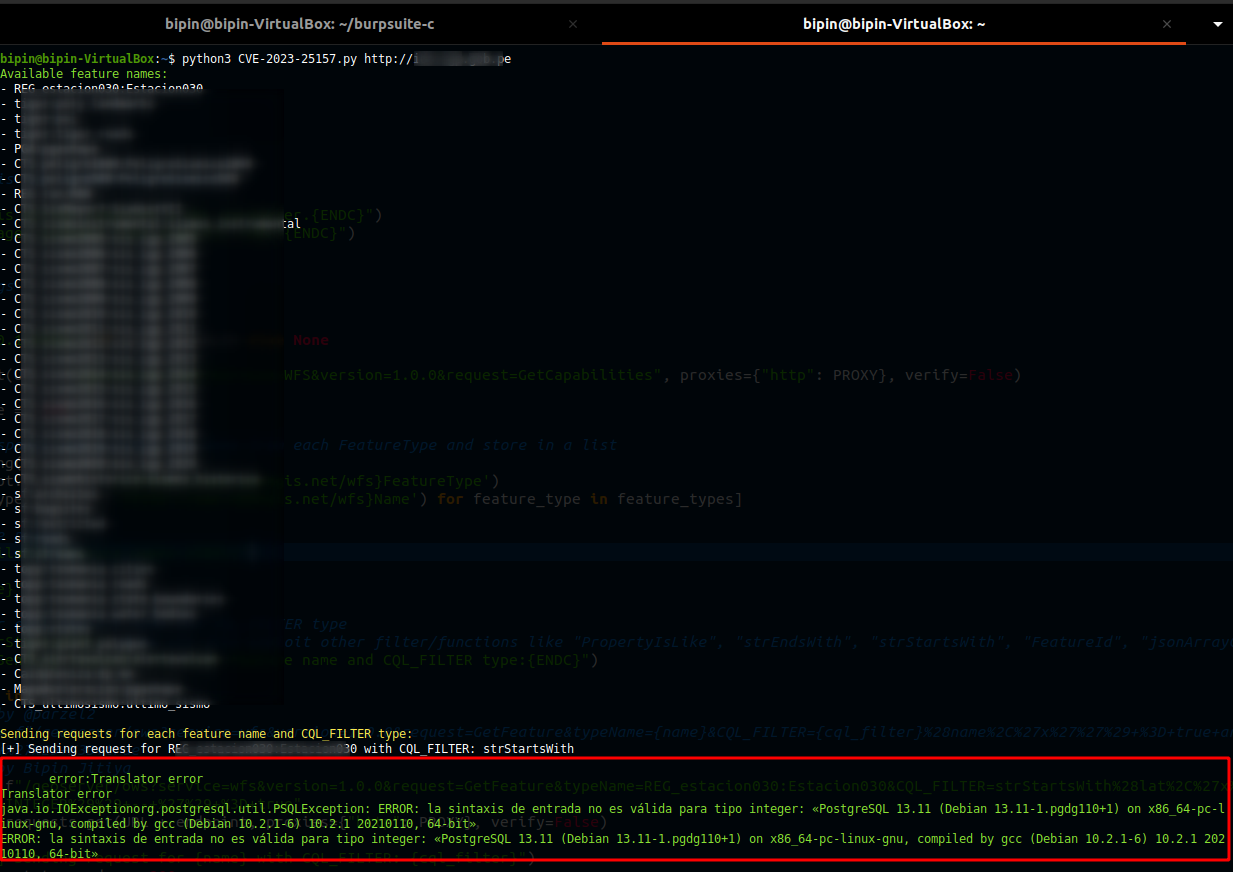 win3zz/cve-2023-25157
CVE-2023-25157 - GeoServer SQL Injection - PoC
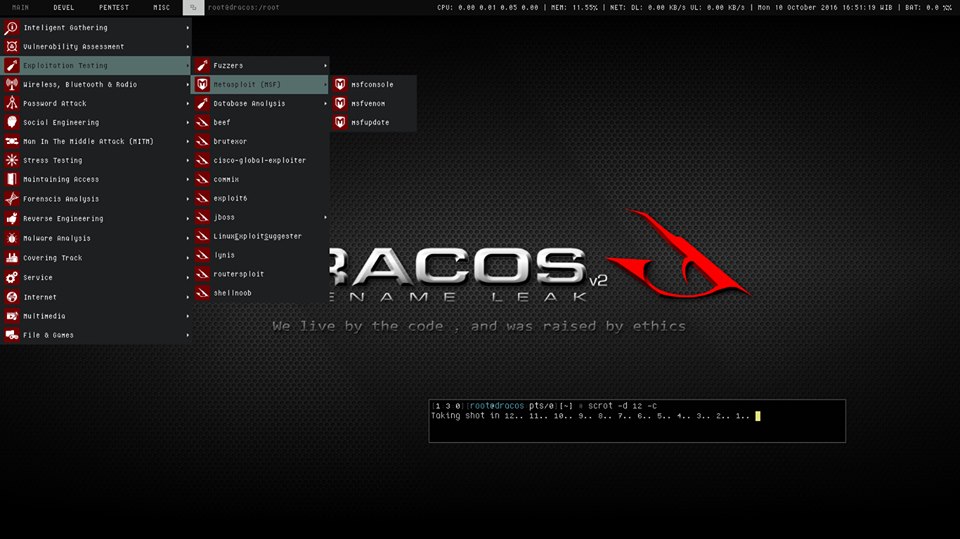 screetsec/dracos
Dracos Linux ( www.dracos-linux.org ) is the Linux operating system from Indonesian
 7h30th3r0n3/ollamahound
Mass reconnaissance, version fingerprinting, CVE tester and live exploitation framework for Ollama open instances.
 cyberdudebivash/cyberdudebivash-cisco-asyncos-cve-2025-20393-scanner
This tool helps identify exposure to CVE-2025-20393 by checking for open TCP/6025 ports, responsive Spam Quarantine interfaces, and known…
 cappricio-securities/cve-2018-11784
Apache Tomcat - Open Redirect
 dirac231/cve-2024-40498
Blind SQL Injection to RCE in a PHP open source application
 mbadanoiu/cve-2019-14223
CVE-2019-14223: Open Redirect in Alfresco Share
 xalgorix/xalgorix
Autonomous AI pentesting agents — real-time reconnaissance, vulnerability detection, and exploitation orchestration. Go + TypeScript.
 k8gege/ladongo
Ladon for Kali 全平台开源内网渗透扫描器,Windows/Linux/Mac/路由器内网渗透,使用它可轻松一键批量探测C段、B段、A段存活主机、高危漏洞检测MS17010、SmbGhost,远程执行SSH/Winrm,密码爆破SMB/SSH/FTP/Mysql/Mssql/Oracle…
 tylous/sniffair
A framework for wireless pentesting.