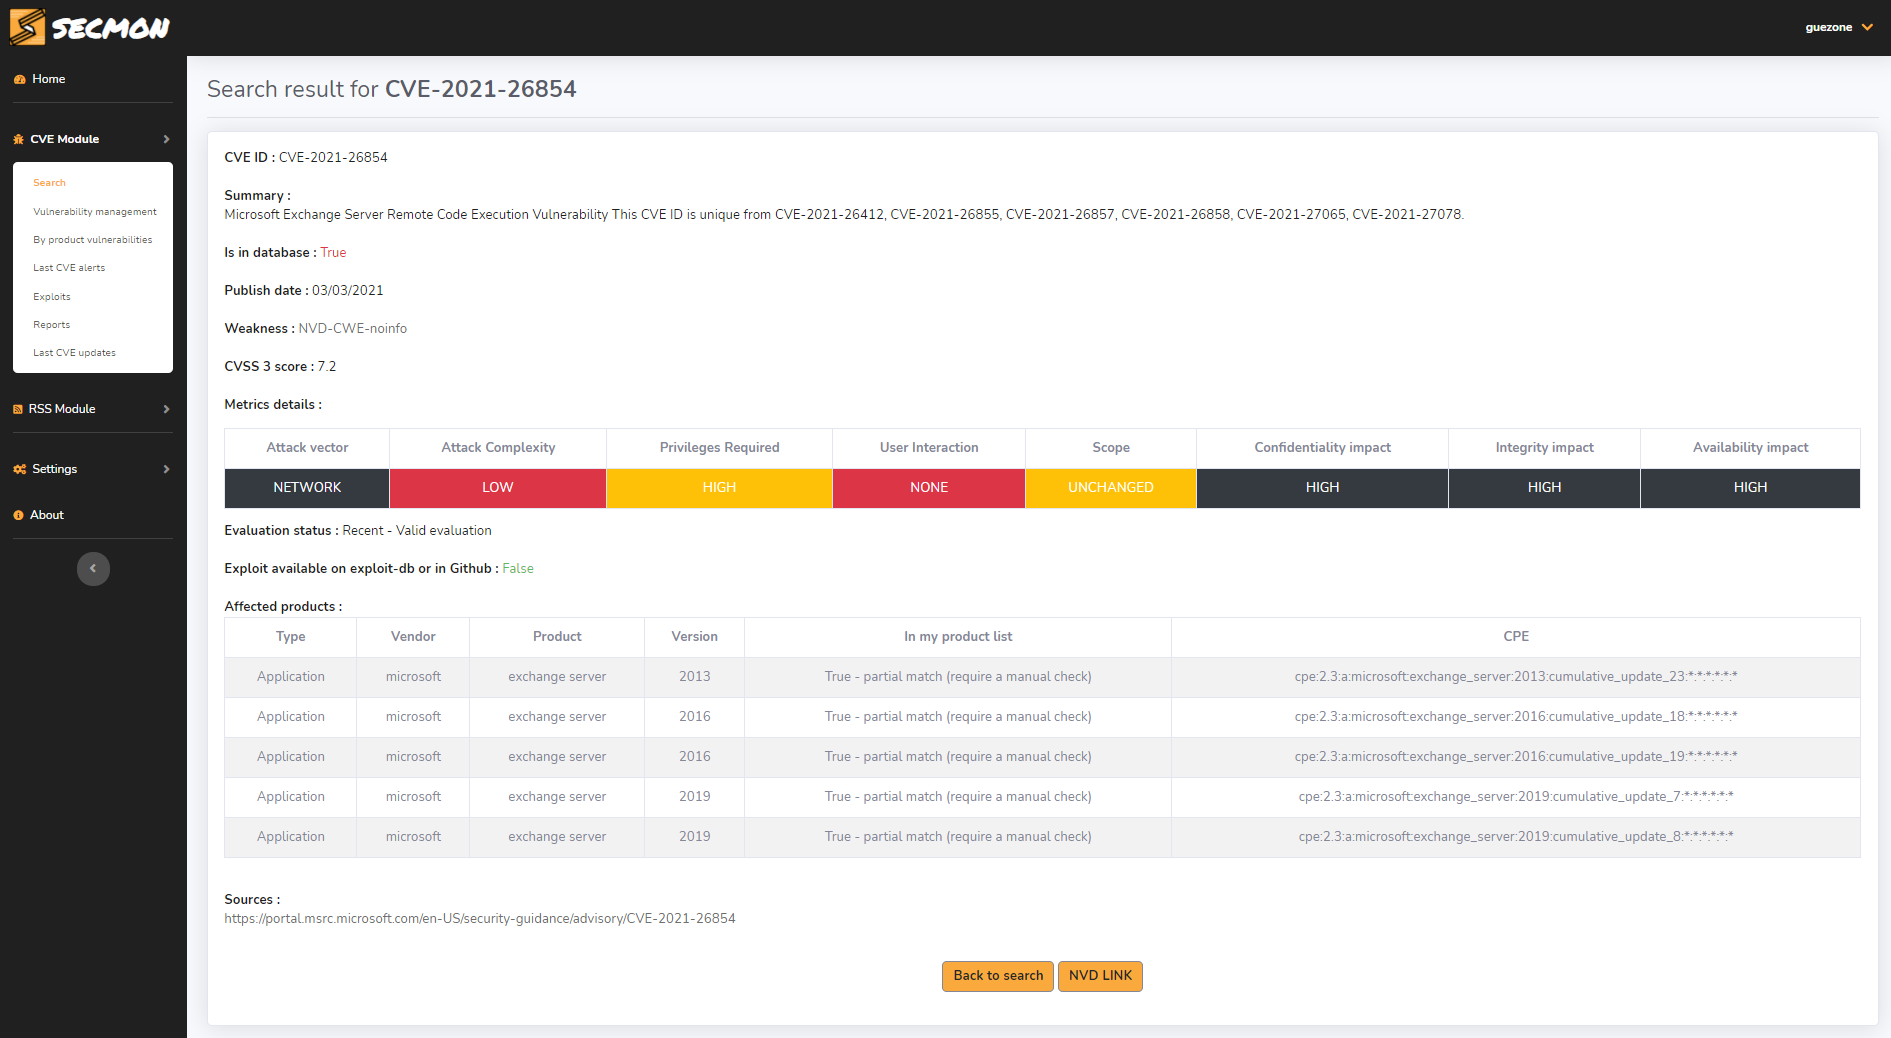
PowerPriv
 g0ldengunsec/powerpriv
A Powershell implementation of PrivExchange designed to run under the current user's context
authenticationexploitationlateral-movement+2
125
g0ldengunsec/powerprivA Powershell implementation of PrivExchange designed to run under the current user's context
 sud0ru/cpldcomtrigger
CPL remote trigger
 je6k/cve-2021-34473-exchange-proxyshell
对Exchange Proxyshell 做了二次修改,精确的拆分、实现辅助性安全测试。
 io1337/icg-autoexploiterbot
Automated exploitation tool targeting CMS vulnerabilities in Joomla, WordPress, Drupal, PrestaShop, and OsCommerce with built-in brute-force and…
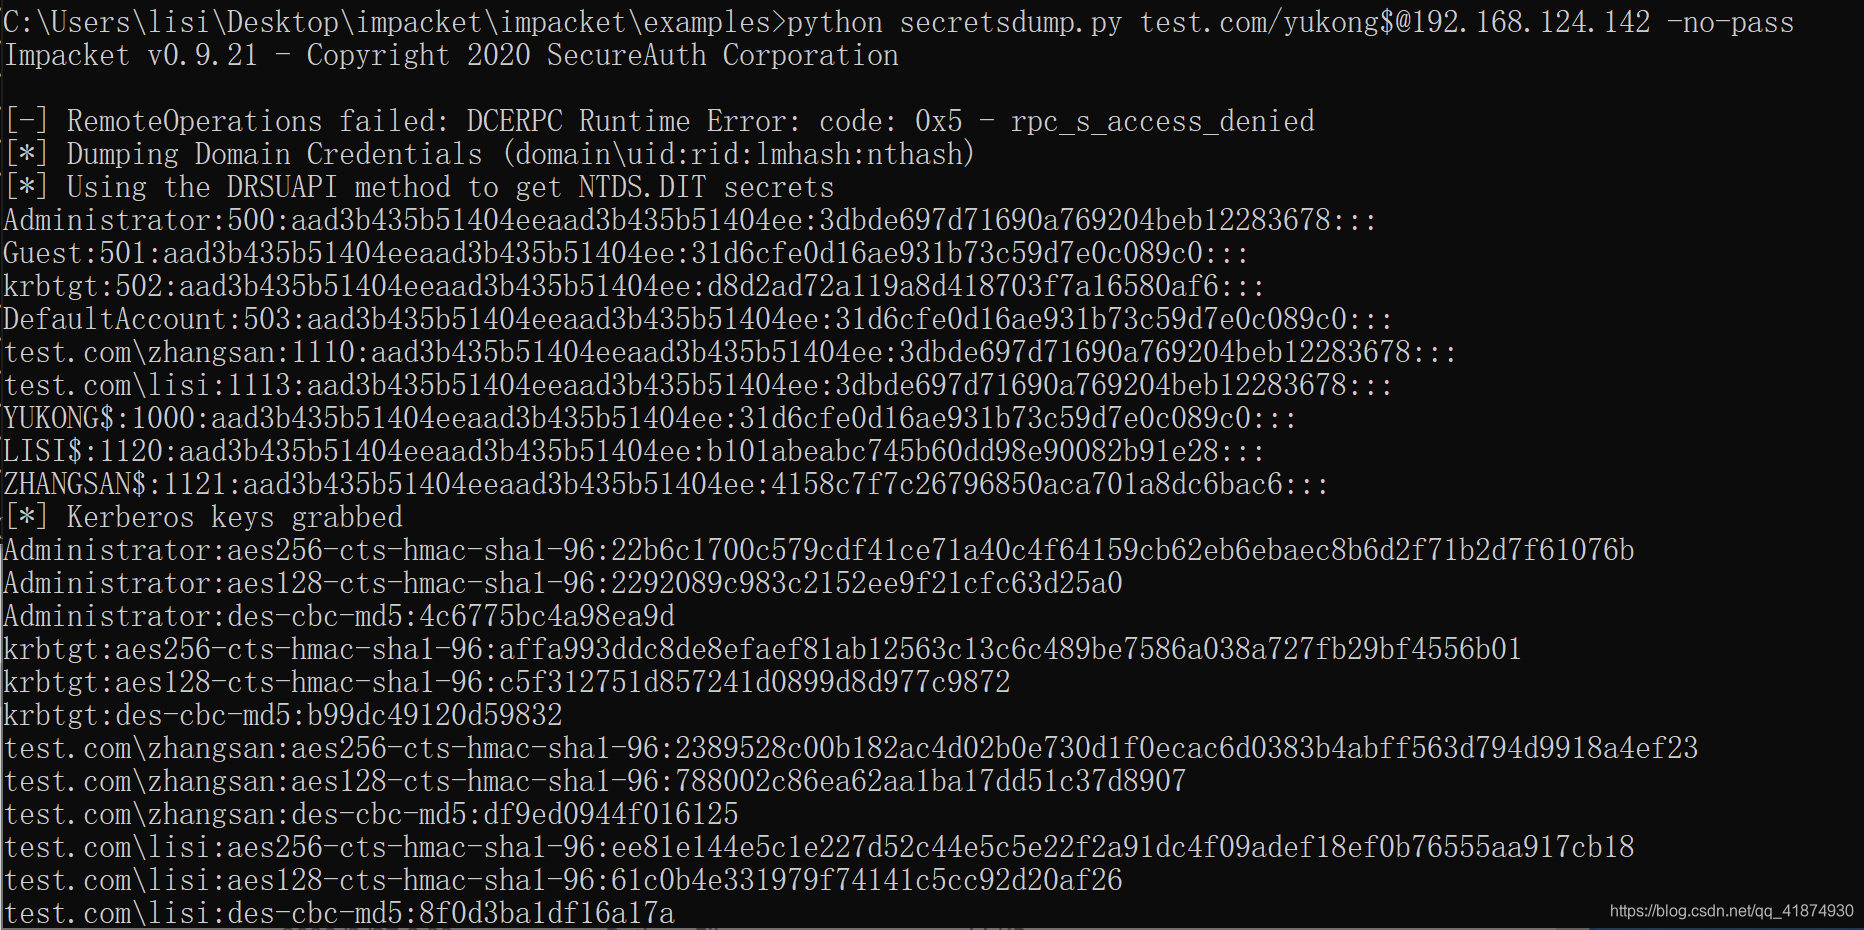 shanfenglan/cve-2020-1472
Exploit for CVE-2020-1472 (Zerologon) that resets domain controller machine account password, enabling credential dumping and privilege escalation to…
 sezayi1972/cve-2019-0708
CVE-2019-0708 Exploit
 notmedic/netntlmtosilverticket
SpoolSample -> Responder w/NetNTLM Downgrade -> NetNTLMv1 -> NTLM -> Kerberos Silver Ticket
 dirkjanm/pkinittools
Tools for Kerberos PKINIT and relaying to AD CS
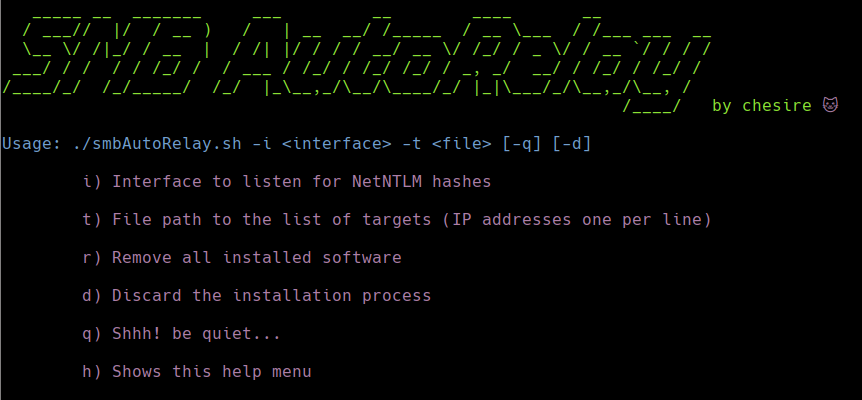 cheshireca7/smbautorelay
SMB Auto Relay provides the automation of SMB/NTLM Relay technique for pentesting and red teaming exercises in active directory environments.
 hainhc/cve-2026-73570
Proof-of-concept exploit for CVE-2026-73570, an unauthenticated OS command injection in Zimbra Collaboration Suite via zimbra-snmp log injection,…
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 theunknownsoul/cve-2023-23397-pow
Proof of Work of CVE-2023-23397 for vulnerable Microsoft Outlook client application.
 phaedrik/cve-2023-23397-poc
Two POCs I created for the CVE-2023-23397 Outlook NTLM vulnerability, to be used internally.
 b1ack0wl/cve-2020-1472
Exploit for CVE-2020-1472 (ZeroLogon) that resets the domain controller account password and enables DCSync for full domain compromise.
 cyberdudebivash/cyberdudebivash-cisco-asyncos-cve-2025-20393-scanner
This tool helps identify exposure to CVE-2025-20393 by checking for open TCP/6025 ports, responsive Spam Quarantine interfaces, and known…
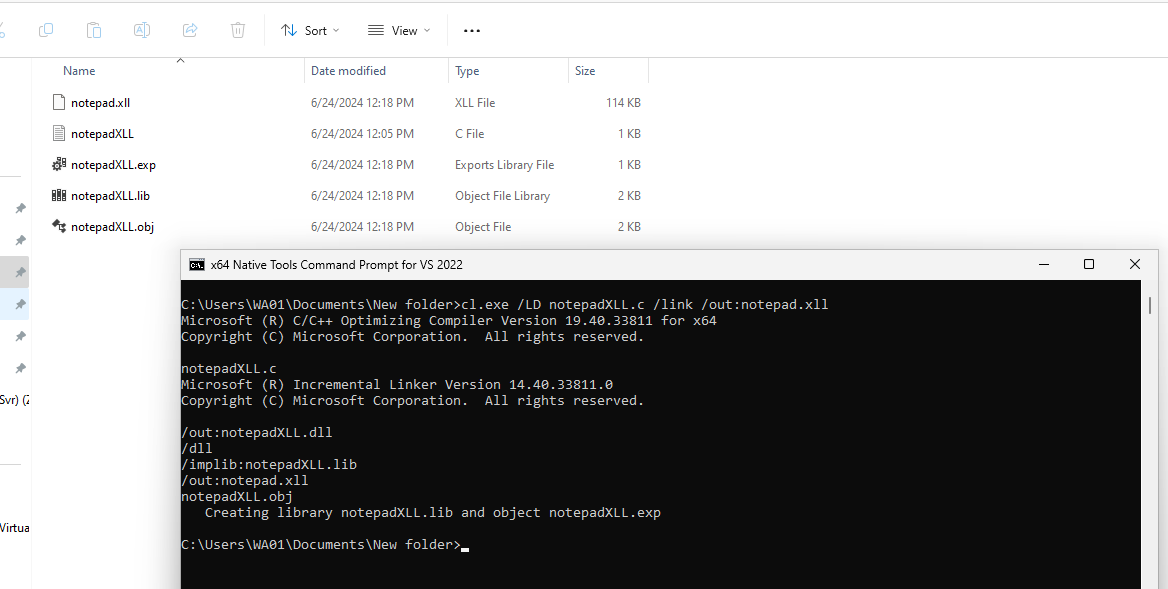 h3x0v3rl0rd/xll_windows_reverse_shell
xll windows reverse shell