
CVE-2021-4034
 locksec/cve-2021-4034
Exploit PoC for the polkit pkexec (PWNKIT) vulnerability
binary-exploitationexploitationexploit-frameworks+2
2
locksec/cve-2021-4034Exploit PoC for the polkit pkexec (PWNKIT) vulnerability
 yuspring/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel privilege escalation via AF_ALG authenc length check bypass, achieving root by modifying…
 wesmar/cve-2026-31431
Working proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD page cache corruption, granting root…
 ben-slates/cve-2026-31431-exploit
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability enabling local privilege escalation via algif_aead.…
 simoesctt/ctt-nfs-vortex-rce
New Physics Disclosure This repository contains a full weaponized exploit for **CVE-2026-21509**, targeting the Windows Network File System (NFSv4.1)…
 lonelyor/cve-2026-31431-exp
C and Rust exploit for CVE-2026-31431 with payload encryption, cache writeback, adaptive chunking, and multi-architecture support (x86, ARM, i386).
 kennetham/cve_2016_0728
Proof-of-concept exploit for CVE-2016-0728, a Linux kernel vulnerability enabling local privilege escalation via keyctl subsystem.
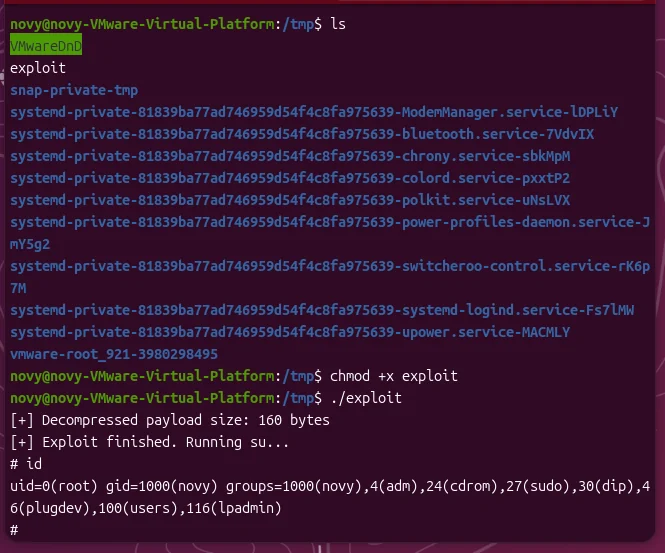 novysodope/copy-fail-cve-2026-31431-c
CVE-2026-31431 - standalone binary exploit (no Python required)
 lkeld/cve-2026-43499-poc
Weaponized proof-of-concept for CVE-2026-43499 (GhostLock), a Linux kernel rtmutex bug enabling local privilege escalation. Includes per-distribution…
 cs8425/copy-fail-go
Go-based exploit for CVE-2026-31431, a local privilege escalation vulnerability, that modifies /usr/bin/su to gain root access on Linux distributions.
 pupiles/bof-dnsmasq-cve-2017-14493
dnsmasq rop exploit with NX bypass
 guiimoraes/cve-2026-31431
Python implementation of a Linux kernel local privilege escalation exploit for CVE-2026-31431, leveraging xfrm ESP-in-UDP MSG_SPLICE_PAGES no-COW to…
 g1nt0n1x/copy-fail-cve-2026-31431-shell
PoC shell exploit for CVE-2026-31431 (copy_fail) — Linux LPE via AF_ALG + splice page-cache overwrite. Single-shot, no race condition, kernel…
 crackercat/cve-2020-1020-exploit
Local privilege escalation exploit for CVE-2020-1020 targeting Windows 7/8/8.1 x64 via Type1 Font Pool Overflow.
 teamn4c/sg-2026-0024
CVE-2026-43284 and CVE-2026-43500 Dirty Frag PoC and exploit
 adityabhatt3010/cve-2026-31431
Local privilege escalation exploit for CVE-2026-31431, abusing AF_ALG AEAD socket handling to achieve root shell access on vulnerable Linux kernels.
 foxtrot/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a Wi-Fi vulnerability, leveraging libwifi for packet parsing and crafted for educational purposes.
 rainbowdynamix/fortilol
FortiClient FortiShield exploit (CVE-2015-5736) for Windows 10 1809