
CVE-2025-11771
 jfriedli/cve-2025-11771
Proof-of-concept exploit for CVE-2025-11771 demonstrating unauthenticated sale record creation via a WordPress REST API endpoint, with browser…
api-security-testingexploitationpenetration-testing+2
jfriedli/cve-2025-11771Proof-of-concept exploit for CVE-2025-11771 demonstrating unauthenticated sale record creation via a WordPress REST API endpoint, with browser…
 d0n601/cve-2025-12720
g-FFL Cockpit <= 1.7.1 - Improper Authorization to Unauthenticated Product Deletion
 fuyuooumi1027/cve-2023-45857-demo
Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…
 adelittle/cve-2021-4191_exploits
Exploit script for CVE-2021-4191 that enumerates GitLab users via the GraphQL API, useful for security assessments and validating exposure.
 clemfavre/cve-2023-45612_exploit
Reproduction of a high severty security problem that allows XXE (XML eXternal Entity) attacks on Ktor's XML serialization.
 prestonhashworth/cve-2025-55182
CVE-2025-55182 testing toolkit with Postman collection, cURL examples, and F5 WAF signature validation for vulnerability assessment and protection…
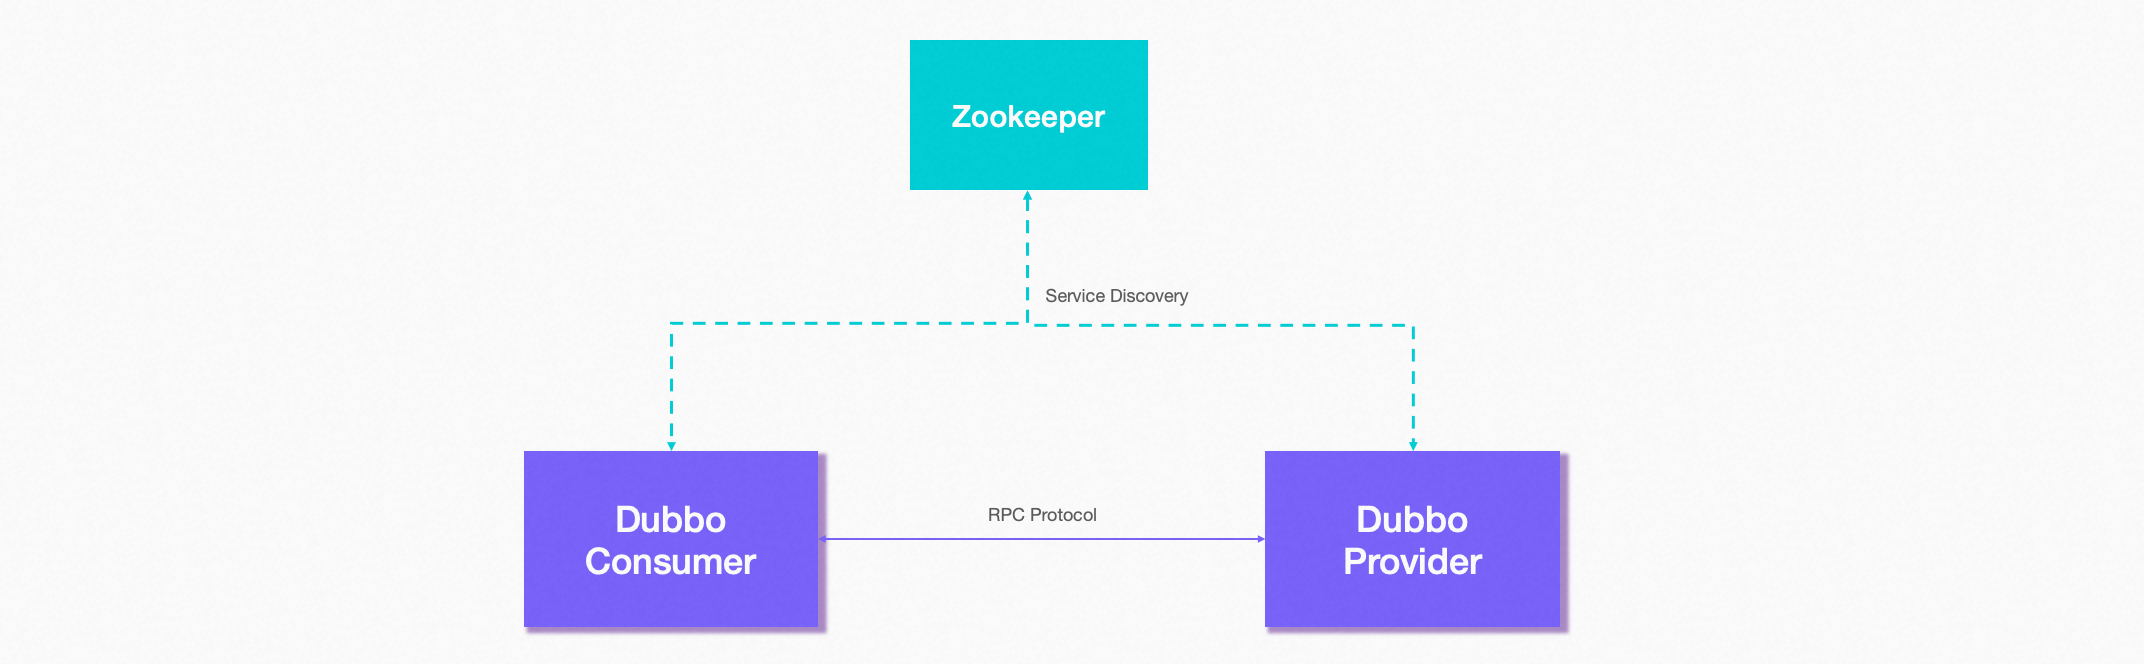 shoucheng3/apache__dubbo_cve-2021-30180_2-7-9
Exploit for CVE-2021-30180 targeting Apache Dubbo RPC framework, enabling remote code execution via crafted RPC requests in vulnerable versions.
 0xsu3ks/cve-2025-29556
PoC for CVE-2025-29556 creating Security Officer accounts on ExaGrid EX10 backup appliances via a low-privilege API session, enabling privilege…
 crackercat/cve-2022-24112
Apache APISIX apisix/batch-requests RCE
 skysliently/cve-2022-22947-pb-ai
一个由AI生成的漏洞验证应用
 shoucheng3/spring-cloud__spring-cloud-gateway_cve-2022-22947_3-0-6
Spring Cloud Gateway repository demonstrating CVE-2022-22947 exploitation for API security testing and vulnerability analysis.
 ashiqrehan-21/mcp-inspector-cve-2025-49596
MCP-Inspector-vulncheck is a Python script that checks if an MCP Inspector server is vulnerable to CVE-2025-49596. It tests whether the /sse endpoint…
 fevar54/forticlient_ems_cve_2026_35616_poc.py
PoC de CVE-2026-35616: control de acceso indebido en FortiClient EMS.
 randomrobbiebf/cve-2023-45828
RumbleTalk Live Group Chat <= 6.1.9 - Missing Authorization via handleRequest
 cetinpy/cve-2024-50633
Proof-of-concept exploit for CVE-2024-50633, a Broken Object Level Authorization (BOLA) vulnerability in Indico v3.2.9–v3.3.2, enabling unauthorized…
 mayank-s16/swagger-html-injection-cve-2025-8191
XSS Test Swagger 3.14.1 to 3.37.0
 grtmaldet/big-ip-next-cve-2024-26026
Proof-of-concept exploit for CVE-2024-26026: unauthenticated SQL injection in F5 BIG-IP Next Central Manager API, enabling remote data extraction and…
 nxploited/cve-2024-9707-poc
he Hunk Companion Plugin for WordPress: Vulnerable to Unauthorized Plugin Installation/Activation (Versions Up to and Including 1.8.4)