

CVE-2024-13184
 randomrobbiebf/cve-2024-13184
The Ultimate WordPress Toolkit – WP Extended <= 3.0.12 - Unauthenticated SQL Injection via Login Attempts Module
exploitationinformation-gatheringpenetration-testing+2
1
randomrobbiebf/cve-2024-13184The Ultimate WordPress Toolkit – WP Extended <= 3.0.12 - Unauthenticated SQL Injection via Login Attempts Module
 d0n601/cve-2025-6220
Ultimate Addons for Contact Form 7 <= 3.5.12 - Authenticated (Administrator+) Arbitrary File Upload via 'save_options'
 aqwainfosec/cve-2025-56807
Proof-of-concept for a stored XSS vulnerability in FairSketch RISE Ultimate Project Manager & CRM v3.9.4, demonstrating arbitrary JavaScript…
 rizqimaulanaa/cve-2023-3460
Proof-of-concept exploit for CVE-2023-3460 enabling unauthorized admin access in the Ultimate Member WordPress plugin. Intended for educational…
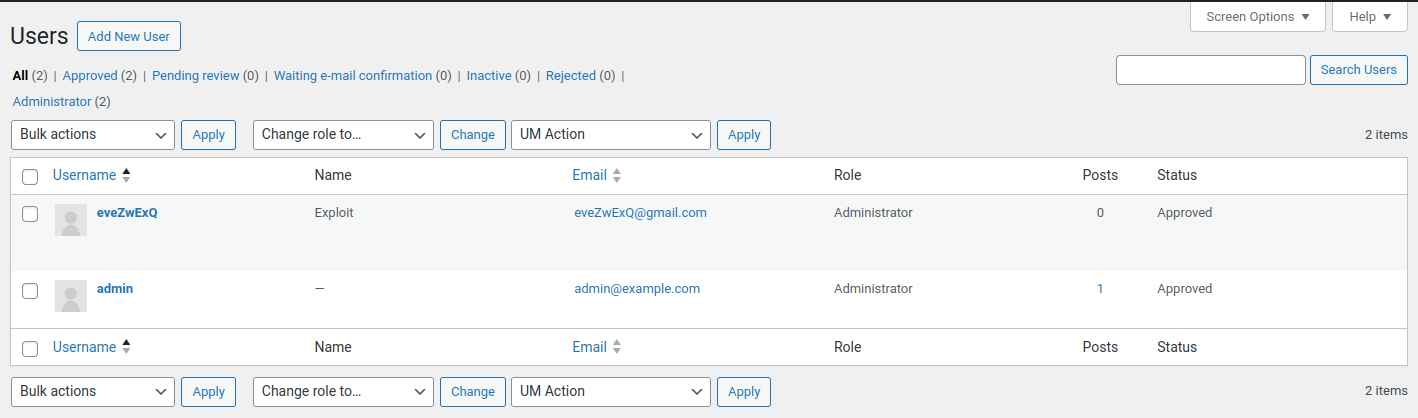 julienbrs/exploit-cve-2023-3460
Exploit and analysis of CVE-2023-3460, a critical privilege escalation in the Ultimate Member WordPress plugin, with reproduction environment and…
 dottak/cve-2024-56278
Proof-of-concept exploit for CVE-2024-56278, a remote code execution vulnerability in the WP Ultimate Exporter WordPress plugin, demonstrating file…
 abdurahmon3236/cve-2024-6529
Proof-of-concept scripts demonstrating reflected XSS in the Ultimate Classified Listings WordPress plugin and admin cookie theft via crafted payloads…
 d0n601/cve-2025-47549
Ultimate Before After Image Slider & Gallery – BEAF <= 4.6.10 - Authenticated (Admin+) Arbitrary File Upload via beaf_options_save
 pashayogi/cve-2024-8289
CVE-2024-8289 https://www.cve.org/CVERecord?id=CVE-2024-8289, Vendor wcmp Product MultiVendorX – The Ultimate WooCommerce Multivendor Marketplace…
 0x4d31/awesome-oscp
A curated list of awesome OSCP resources
 xlinshan/coldroot
Mac OS Trojan (RAT) made with love <3
 voidsshadows/hikvision-city-hunter
This tool is a modern evolution of older PoCs like those for CVE-2017-7921 and ICSA-17-124-01, updated for 2025 with live console output, threading…
 moksh-nfsu/cve-2026-36392
Proof-of-concept for stored XSS in RISE CRM item title field (CVE-2026-36392), demonstrating session hijacking and account takeover with remediation…
 ghostn4444/cve-2025-55182
Next.js RSC RCE vulnerability scanner with multiple scan modes, WAF bypass, interactive shell, and batch scanning for authorized penetration testing.
 ajansha/cve-2025-60378
Proof of concept for stored HTML injection in RISE CRM, demonstrating how authenticated users can inject malicious HTML into invoices and messages,…
 manojcode/easy-file-share-7.2-exploit-cve-2018-9059
My version - Easy File Sharing Web Server 7.2 - 'UserID' - Win 7 'DEP' bypass
 dimarcosk/cve-2023-3460_poc
GitHub repository for CVE-2023-3460 POC