
Archived
Dr0p1t-Framework
 d4vinci/dr0p1t-framework
A framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
anti-botcommand-and-controlexploitation+9
d4vinci/dr0p1t-frameworkA framework that create an advanced stealthy dropper that bypass most AVs and have a lot of tricks
 kiexitdispatcher/goredops
🦫 | GoRedOps is a repository dedicated to gathering and sharing advanced techniques and offensive malware for Red Team, with a specific focus on…
 optiv/freeze.rs
Freeze.rs is a payload toolkit for bypassing EDRs using suspended processes, direct syscalls written in RUST
 kungaocode/vulnerability-analysis-
Automated reproduction and analysis of CVE-2021-26708 — a use-after-free vulnerability in the Linux kernel's AF_VSOCK subsystem (v5.10.12). Includes…
 tinashelorenzi/cve-2025-55182
Proof-of-concept exploit for CVE-2025-55182, a critical unauthenticated RCE in React Server Components. Includes automated Python exploit, technical…
 xoreaxeaxeax/schrodingers-toctou
Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…
 h3raklez/cve-2025-21756
Educational lab demonstrating a use-after-free (UAF) exploit in the Linux kernel's vsock subsystem for local privilege escalation to root, with…
 ermensonx/cve-2025-14857-mongobleed
Functional proof-of-concept exploit for CVE-2025-14847 (MongoBleed), a pre-authentication heap memory disclosure vulnerability in MongoDB. Includes…
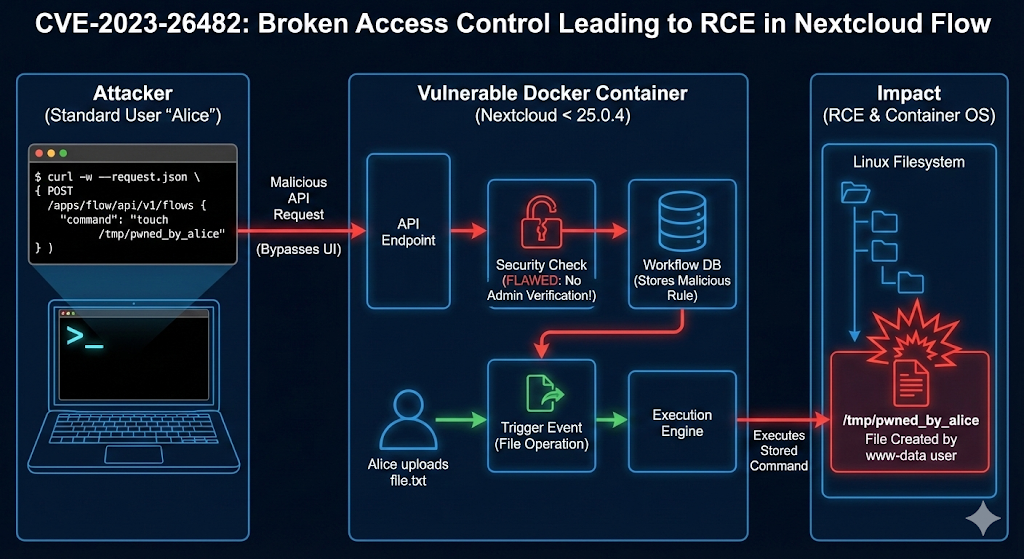 isabbii/poc---cve-2023-26482-rce-lab-nextcloud
Docker-based lab reproducing CVE-2023-26482 (Nextcloud RCE) with automated exploit script for educational vulnerability analysis and exploitation…
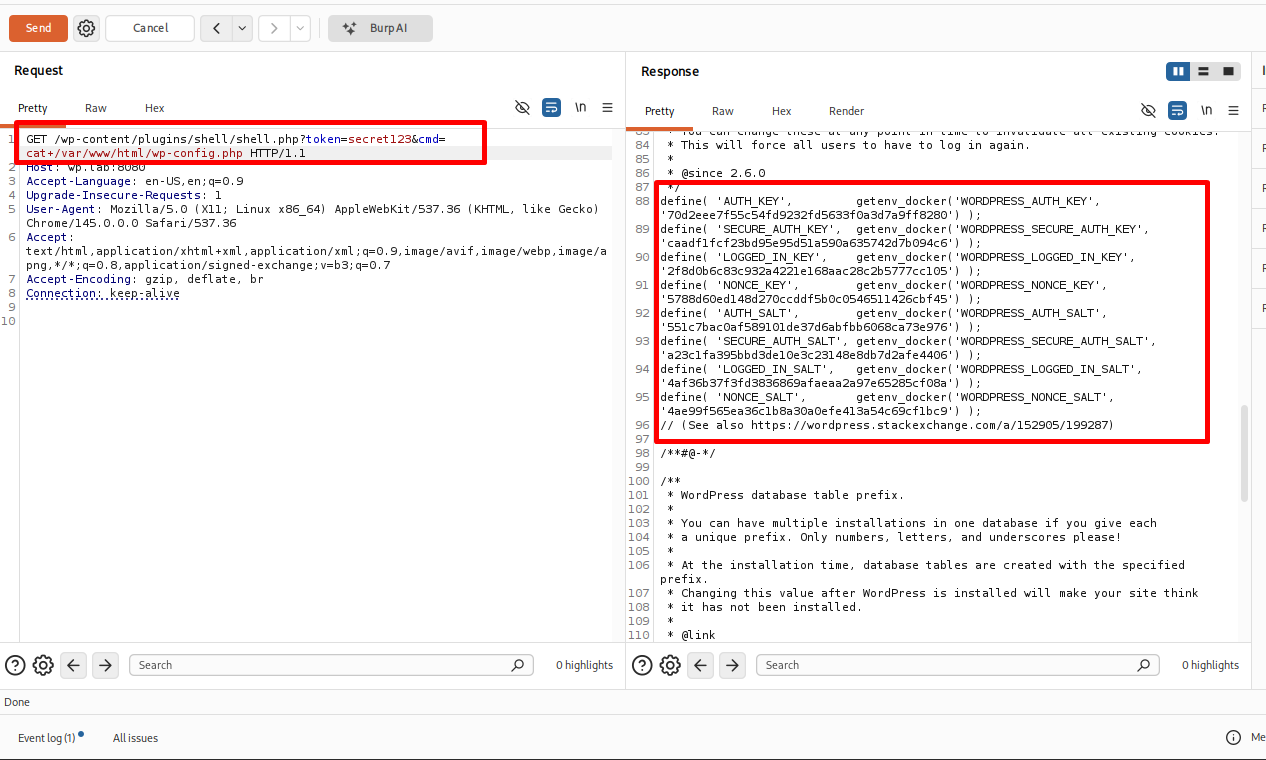 dungsocool/cve-2026-60137_cve-2026-63030
WordPress unauthenticated RCE exploit combining route confusion and SQL injection. Automated script, lab setup, and detailed vulnerability analysis…
 izxci/cve-2026-49777
Python exploit for CVE-2026-49777, a critical unauthenticated RCE in ShapedPlugin Product Slider Pro for WooCommerce. Includes automated detection…
 alpinine/cve-2026-1312-testing
Reproduction environment for CVE-2026-1312 with Docker-based setup and automated execution script for vulnerability testing and analysis.
 cybersecurity-enthusiasts-ce/cve-2025-55182-researching-process
Defensive research repository for CVE-2025-55182 (Pre-Auth RCE in React Server Components/Next.js). Includes technical analysis, detection rules…
 splintersfury/autopiff
Semantic analysis engine for detecting vulnerability fixes in Windows kernel driver patches — 58 YAML rules, Ghidra decompilation, reachability…
 trustedsec/ts_llmlib
Python library for local LLM-powered security analysis with Ghidra binary analysis, C/C++ vulnerability scanning, and MCP tool integration for…
 devianntsec/cve-2024-30051
Master's Thesis research on CVE-2024-30051 (Windows DWM Heap Overflow). Features a high-reliability exploit with automated heap spray optimization,…
 ndhet/bot-cve-2026-42940
Automated bot for exploiting CVE-2026-42940, providing vulnerability exploitation and analysis capabilities.
 techwithorgito/cve-2025-55182-researching-process
Defensive research repository for CVE-2025-55182 (Pre-Auth RCE in React Server Components/Next.js). Includes technical analysis, detection rules…