

eps-CVE-2017-0261
 kcufid/eps-cve-2017-0261
Analysis and PoC exploit for EPS vulnerability CVE-2017-0261, including IDA disassembly, intermediate documents, and original exploit files.
binary-analysisexploitationmalware-analysis+2
10
kcufid/eps-cve-2017-0261Analysis and PoC exploit for EPS vulnerability CVE-2017-0261, including IDA disassembly, intermediate documents, and original exploit files.
 sneakynachos/cve-2026-2796-escape-wasm-by-using-wasm
PoC exploit chain for CVE-2026-2796: SpiderMonkey WebAssembly sandbox escape (signature type confusion -> arbitrary R/W -> RCE)
 dangokyo/cve-2017-3000
A full exploit of CVE-2017-3000 on Flash Player Constant Blinding PRNG
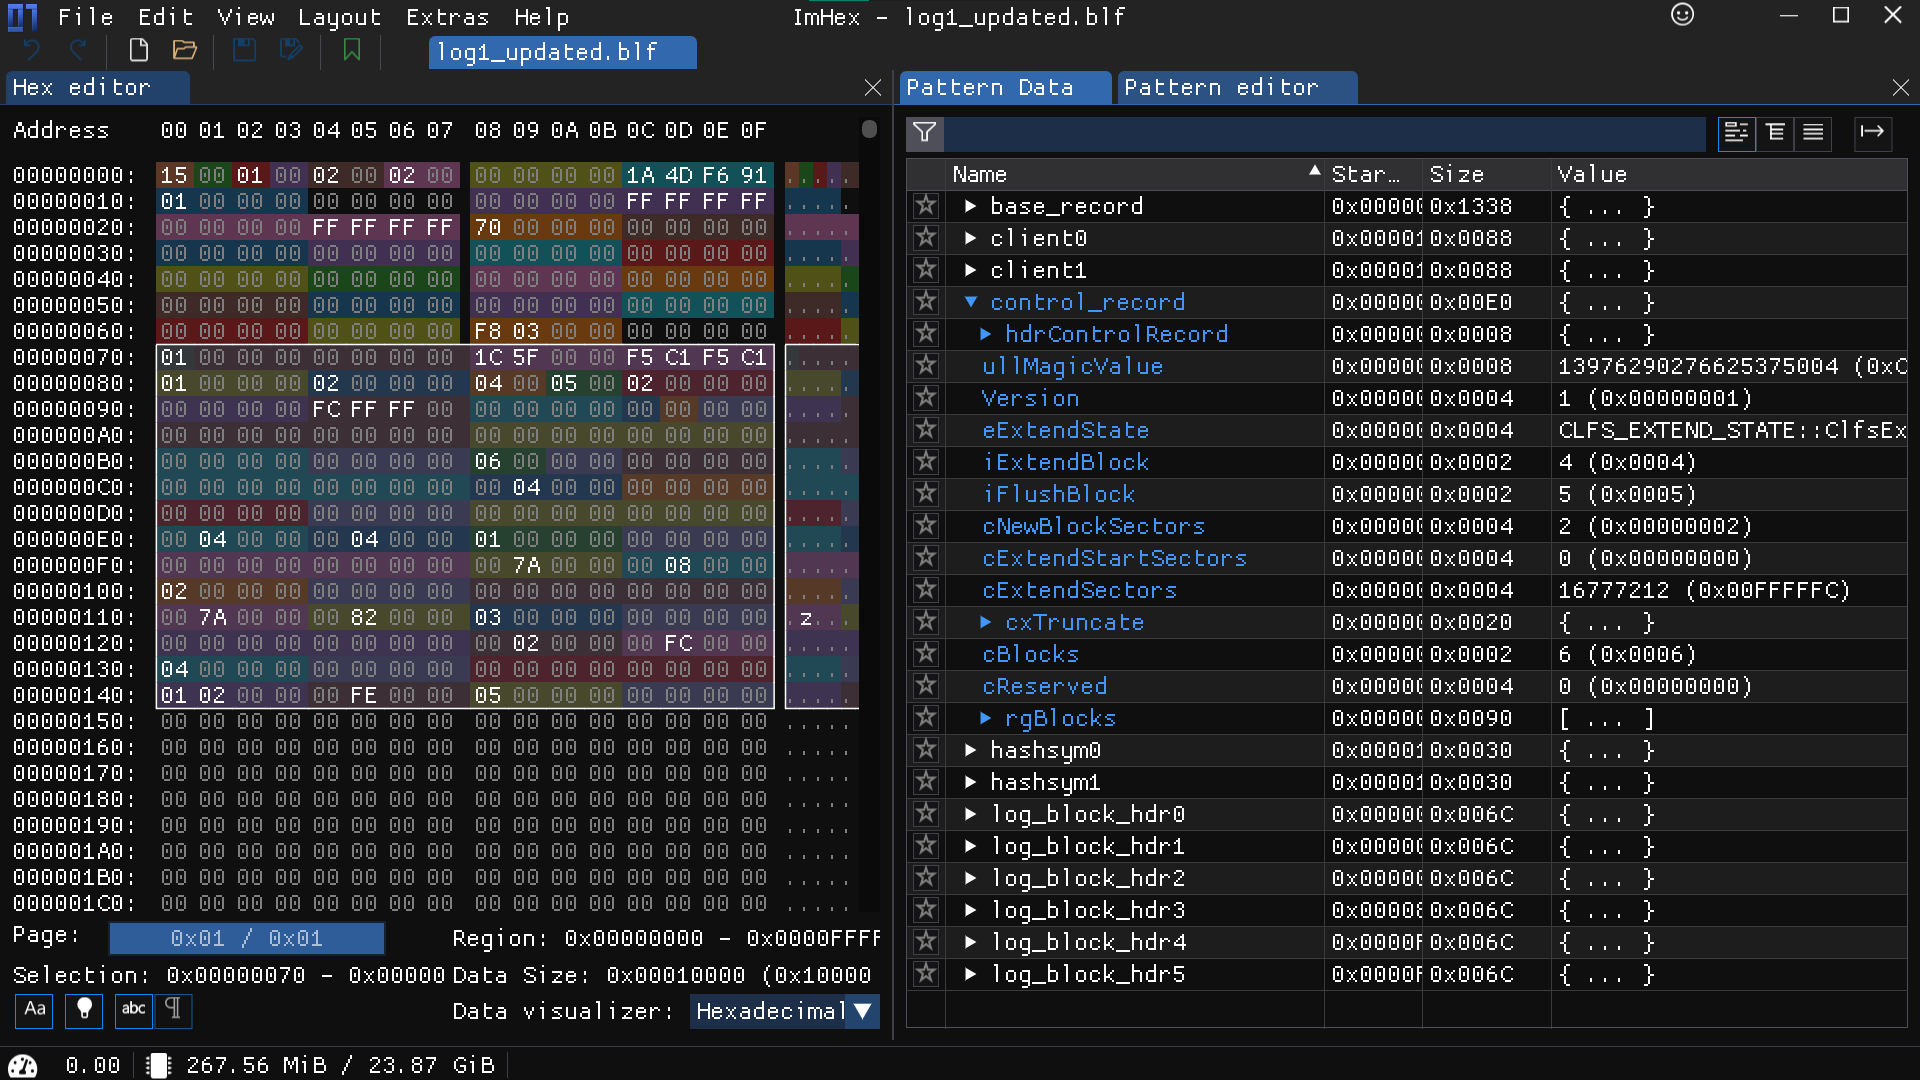 romanrybachek/cve-2023-36900
Denial-of-Service PoC | Writeup | Header with CLFS structures | Imhex pattern for .blf extension
 novaek/cve-2026-0073-research
CVE-2026-0073 is an RCE with a CVSS severity score of 8.3, and here we will explain how it works.
 spiralbl0ck/cve-2022-3653
CVE-2022-3653 just the c++ component in Vulkan for later study
 downwithup/cve-2018-16711
PoC code for CVE-2018-16711 (exploit by wrmsr)
 sneakynachos/cve-2026-15718-who-put-ptrs-in-my-wasm
PoC exploit chain for CVE-2026-15718: SpiderMonkey wasm baseline compiler array.fill missing-sync -> invalid pointer -> addrOf/fakeobj -> arbitrary…
 australeo/cve-2021-28476
Proof-of-concept for CVE-2021-28476, a Hyper-V vmswitch.sys arbitrary pointer dereference allowing guest-to-host denial-of-service and potential RCE.

 fm0ss/cve-2025-9951-ffmpeg-jp2-poc
Proof-of-concept for CVE-2025-9951 demonstrating controlled callback execution in FFmpeg via JPEG 2000 component-mapping mismatch. Includes write-up,…
 probnotanexploiter/cve-2024-26170-extended
researching for CVE-2024-26170 or cimfs.sys to find overflows or bugs that is considered a zero-day
 gmh5225/ampa.sys-exp
Not mine code. only for saving
 flamelu/cve-2020-17035-patch-analysis
Analysis of the patch for CVE-2020-17035, detailing the vulnerability and exploitation mechanism in the affected binary component.
 lucas-cauhe/cargo-perm
Cargo exploit from CVE-2023-38497
 pazhanivelmani/av_cve-2020-0162_a10r33
Exploit for CVE-2020-0162 targeting a specific vulnerability, implemented in C++ for binary exploitation and security testing.