
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
310 results
PR0CESS preview

PR0CESS

GitHubaaaddress1/pr0cess

some gadgets about windows process and ready to use :)
exploitationmalware-analysispayload-development+3
6153 years ago
AMSI.fail preview

AMSI.fail

GitHubflangvik/amsi.fail

C# Azure Function with an HTTP trigger that generates obfuscated PowerShell snippets that break or disable AMSI for the current process.

defensive-toolsexploitationids-ips-evasion+2
4687 months ago
Shellcode-Injection-Techniques preview

Shellcode-Injection-Techniques

GitHubplackyhacker/shellcode-injection-techniques

C# implementations of shellcode injection techniques including classic injection, thread hijacking, process hollowing, and atom bombing, using…

exploitationpost-exploitationred-teaming+1
4654 years ago
WSASS preview

WSASS

GitHubtwosevenonet/wsass

This is the tool to dump the LSASS process on modern Windows 11
adversarial-attackexploitationpenetration-testing+2
6744 months ago
spawn preview

spawn

GitHubboku7/spawn

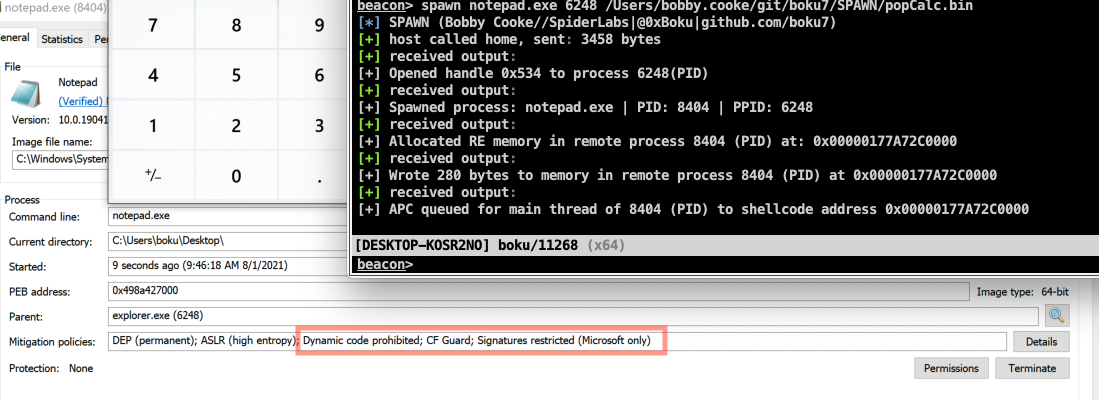
Cobalt Strike BOF that spawns a sacrificial process, injects it with shellcode, and executes payload. Built to evade EDR/UserLand hooks by spawning…

command-and-controlexploitationpayload-development+5
4643 years ago
DllNotificationInjection preview

DllNotificationInjection

GitHubdec0ne/dllnotificationinjection

A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…
exploitationred-teamingshellcode
4673 years ago
PPLcontrol preview

PPLcontrol

GitHubitm4n/pplcontrol

Windows tool to list, get, set, protect, and unprotect process protection levels (PP/L) for debugging, inspection, and privilege escalation.
defensive-toolsexploitationprivilege-escalation+1
4073 years ago
evil-mhyprot-cli preview

evil-mhyprot-cli

GitHubkkent030315/evil-mhyprot-cli

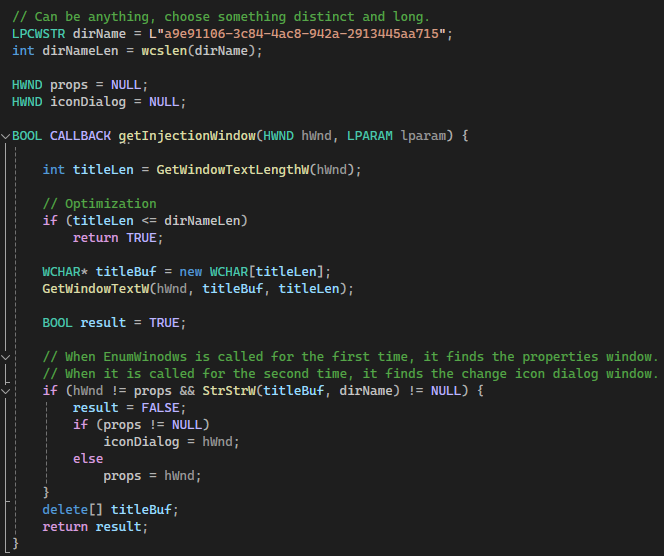
A PoC for Mhyprot2.sys vulnerable driver that allowing read/write memory in kernel/user via unprivileged user process.
binary-exploitationexploitationprivilege-escalation+2
3585 years ago
IconJector preview

IconJector

GitHubd419h/iconjector

Inject DLLs into the explorer process using icons

adversarial-attackexploitationpayload-development+3
4151 year ago
PPLBlade preview

PPLBlade

GitHubtastypepperoni/pplblade

Bypasses PPL protection to dump LSASS process memory, obfuscates dump files with XOR, and exfiltrates them remotely via RAW or SMB without writing to…

data-exfiltrationexploitationmemory-forensics+2
6023 years ago
IHxExec preview

IHxExec

GitHubcicada8-research/ihxexec

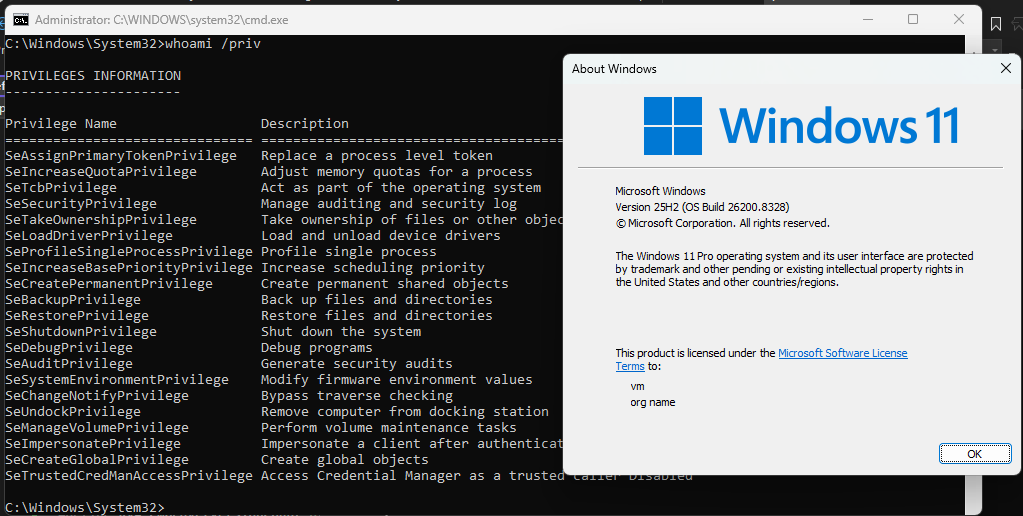
Process injection alternative
exploitationlateral-movementpenetration-testing+3
4042 years ago
CVE-2026-40369-EXPLOIT preview

CVE-2026-40369-EXPLOIT

GitHuborinimron123/cve-2026-40369-exploit

Full exploit code for CVE-2026-40369 - A Windows kernel arbitrary write vulnerability that allows browser sandbox escape from all browsers render…
binary-exploitationexploitationprivilege-escalation+1
2614 months ago
inject-assembly preview

inject-assembly

GitHubkyleavery/inject-assembly

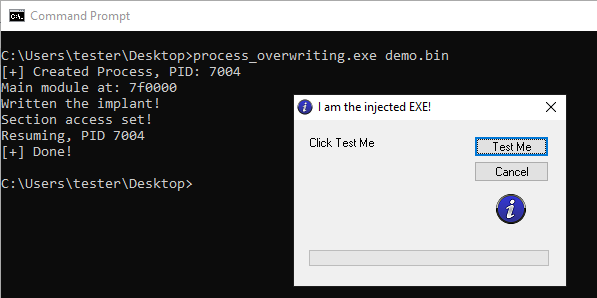
Inject .NET assemblies into an existing process
exploitationpost-exploitationred-teaming+1
5094 years ago
process_overwriting preview

process_overwriting

GitHubhasherezade/process_overwriting

PE injection technique that overwrites a suspended process's executable with a payload, enabling code execution under a benign process identity.

binary-exploitationexploitationpayload-development+1
4731 year ago
Skrull preview

Skrull

GitHubaaaddress1/skrull

Generates anti-copy malware launchers using Process Ghosting to bypass AV/EDR signature scanning and prevent automatic sample submission. Supports…
anti-botexploitationmalware-analysis+2
4594 years ago
SilentButDeadly preview

SilentButDeadly

GitHubloosehose/silentbutdeadly

SilentButDeadly is a network communication blocker specifically designed to neutralize EDR/AV software by preventing their cloud connectivity using…
command-and-controldefensive-toolsexploitation+7
45211 months ago
p3-loader preview

p3-loader

GitHuborange-cyberdefense/p3-loader

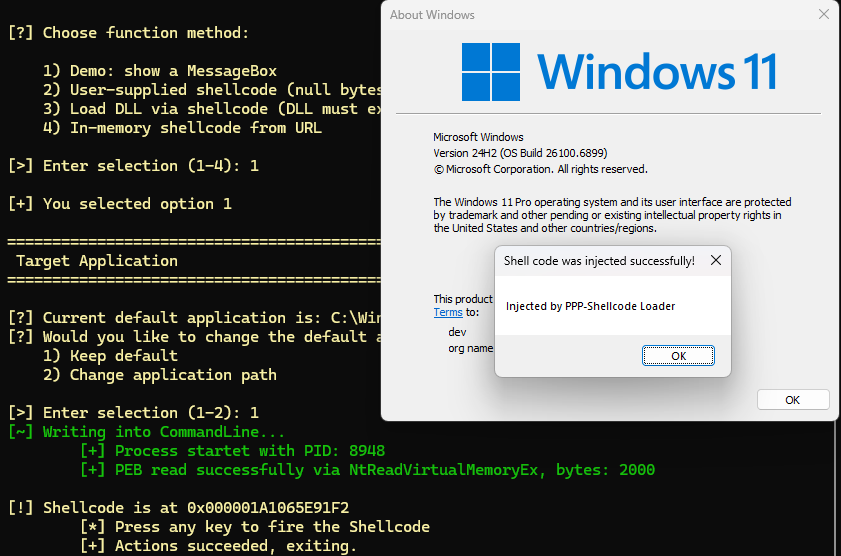
P³-Shellcode Loader is a loader that implements a code injection technique which leverages the Process Parameters structure as an execution and…
binary-exploitationdefensive-toolseducation+8
2363 months ago
jscythe preview

jscythe

GitHubevilsocket/jscythe

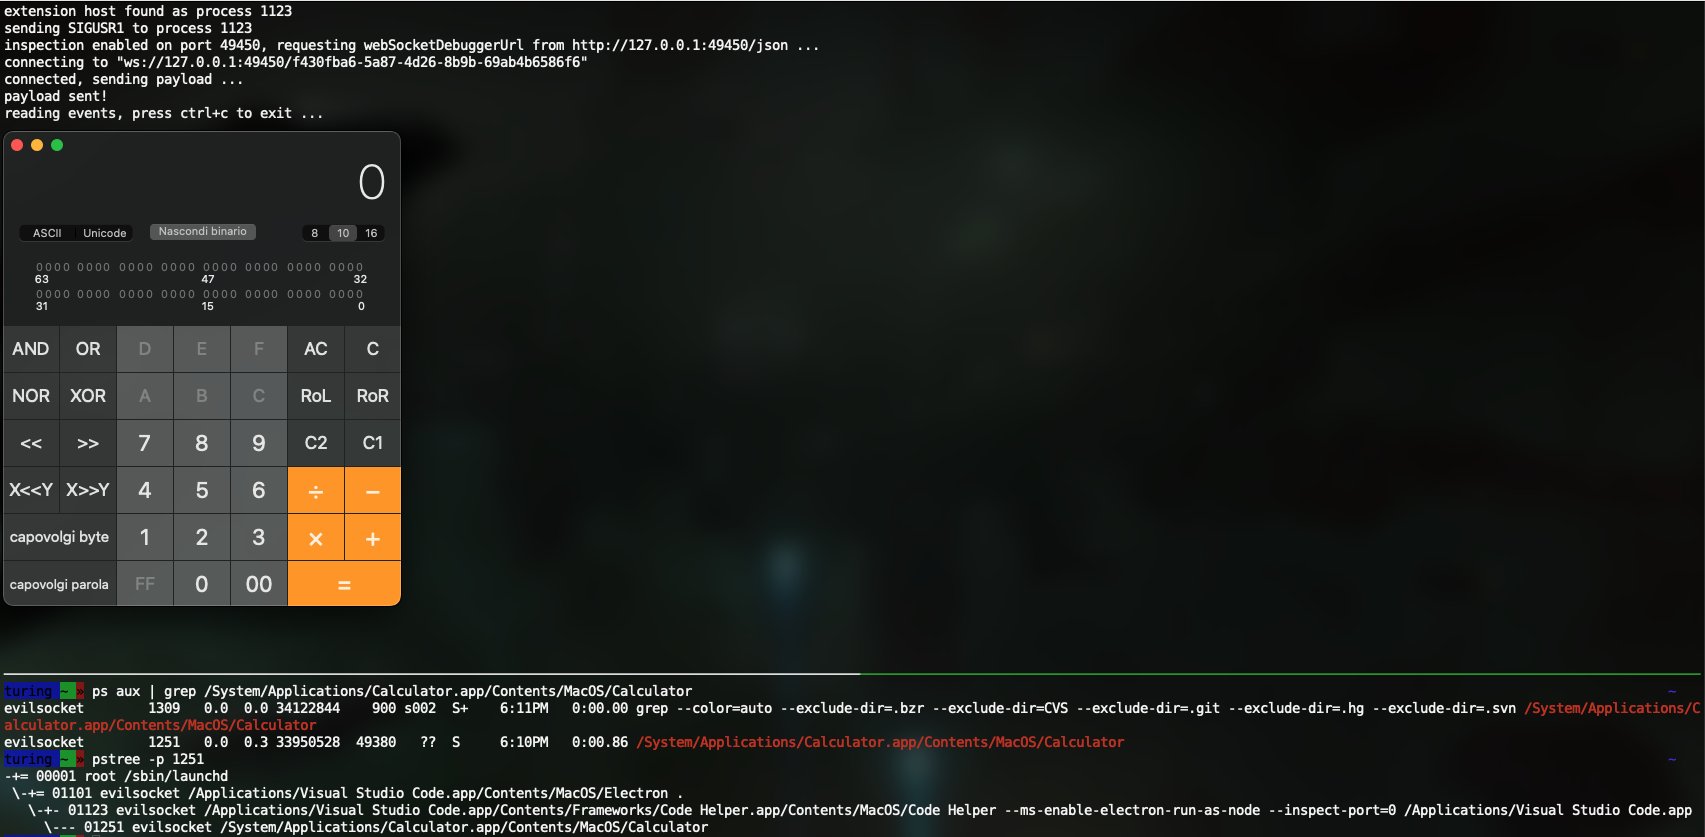
Abuse the node.js inspector mechanism in order to force any node.js/electron/v8 based process to execute arbitrary javascript code.

exploitationpost-exploitationred-teaming+1
3332 years ago
Previous123…18Next