
CVE-2025-61765_PoC
 locus-x64/cve-2025-61765_poc
Proof of Concept of an unsafe pickle deserialization vulnerability in Socket.IO
container-escapeeducationexploitation+3
1
locus-x64/cve-2025-61765_pocProof of Concept of an unsafe pickle deserialization vulnerability in Socket.IO
 wiseep/cve-2025-5287
Wordpress likes and dislikes add-on - SQL Injection
 zvckster/cve-2025-63353
Multi-language PoC (Python · Go · JS · C) and technical documentation for CVE-2025-63353, a critical predictable-default-PSK vulnerability in…
 shanika04/apache_kylin
CVE-2020-1937
 george0papasotiriou/llm-jailbreak-via-chain-of-logic-injection-cve-2026-3098
Multi-stage prompt injection technique that bypasses LLM safety alignment via identity reassignment, refusal suppression, and output coercion,…
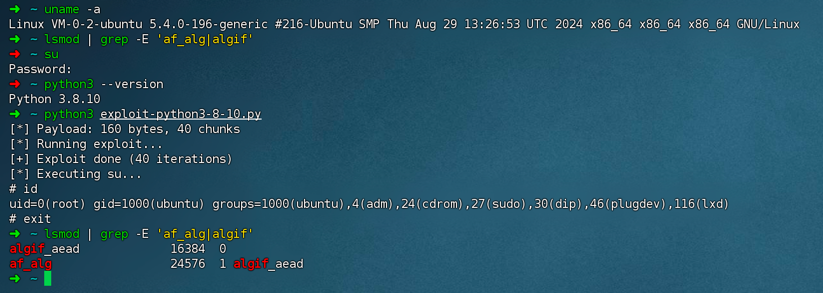 y5neko/copy-fail-cve-2026-31431-universal
Multi-language implementation and compatibility with older versions of Python.
 sumanrox/rschunter
Mass Hunting & Exploitation PoC for CVE-2025-55182 & CVE-2025-66478
 abrewer251/cve-2025-6543_citrixnetscaler_poc
Multi-host, multi-port scanner and auditor for CVE-2025-6543-affected NetScaler devices. Supports SNMP and SSH enumeration with optional CSV…
 boneys/cve-2025-12101-scanner-poc
Multi-threaded scanner for CVE-2025-12101, a reflected XSS in Citrix NetScaler, with single/multi-host scanning, dual protocol testing, proxy…
 jamesjguthrie/shitrix-cve-2019-19781
Shell exploit script for CVE-2019-19781 (Citrix ADC) enabling remote command execution on vulnerable targets with multi-word command support.
 k3ystr0k3r/intrack
A flexible internet crawler used for scanning technologies, instances and vulnerabilities worldwide across the internet.
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 moscowchill/lstar-en
LSTAR - CobaltStrike Translated to EN
 mattb709/cve-2025-24813-scanner
CVE-2025-24813-Scanner is a Python-based vulnerability scanner that detects Apache Tomcat servers vulnerable to CVE-2025-24813, an arbitrary file…
 praetorian-inc/gato
GitHub Actions Pipeline Enumeration and Attack Tool
 kibouo/rustpad
Multi-threaded Padding Oracle attacks against any service. Written in Rust.
 joehquak/mi8e5-unlocker-by-cve-2026-43499
Multi OS Support: Version for MacOS/Linux and Windows, Fully translated to English
 0xinfection/logmepwn
A fully automated, reliable, super-fast, scanning and validation toolkit for the Log4J RCE CVE-2021-44228 vulnerability.