
ghosttester
 1and1-serversupport/ghosttester
Script to test vulnarability for CVE-2015-0235
educationexploitationpenetration-testing+2
1and1-serversupport/ghosttesterScript to test vulnarability for CVE-2015-0235
 fser/ghost-checker
Test wether you're exposed to ghost (CVE-2015-0235). All kudos go to Qualys Security
 arm13/ghost_exploit
CVE-2015-0235 EXIM ESTMP GHOST Glibc Gethostbyname() DoS Exploit/PoC
 n0bitaemon/cve-2026-26980-poc
Ghost CMS Content API Blind SQL Injection
 wojtekchwala/cve-2025-66849
Ghost CMS Privilege Escalation PoC
 rvzsec/cve-2023-40028
CVE-2023-40028 PoC Exploit
 axroux/ghost-path-traversal-cve-2023-32235-
A Directory Traversal attack (also known as path traversal) aims to access files and directories that are stored outside the intended folder.
 0xblackash/cve-2026-24061
CVE-2026-24061
 nickanderson/cfengine-cve_2015_0235
gethostbyname*() buffer overflow exploit in glibc - CVE-2015-0235 https://community.qualys.com/blogs/laws-of-vulnerabilities/2015/01/27/the-ghost-vuln…
 entysec/ghost
Ghost Framework is an Android post-exploitation framework that exploits the Android Debug Bridge to remotely access an Android device.
 dinosn/ghost-cve-2026-26980
CVE-2026-26980 — Ghost CMS Content API SQL Injection Lab (unauthenticated blind SQLi via slug filter ordering)
 0xdtc/ghost-5.58-arbitrary-file-read-cve-2023-40028
CVE-2023-40028 affects Ghost, an open source content management system, where versions prior to 5.59.1 allow authenticated users to upload files that…
 eqstlab/cve-2026-26980
Ghost Content API SQL Injection
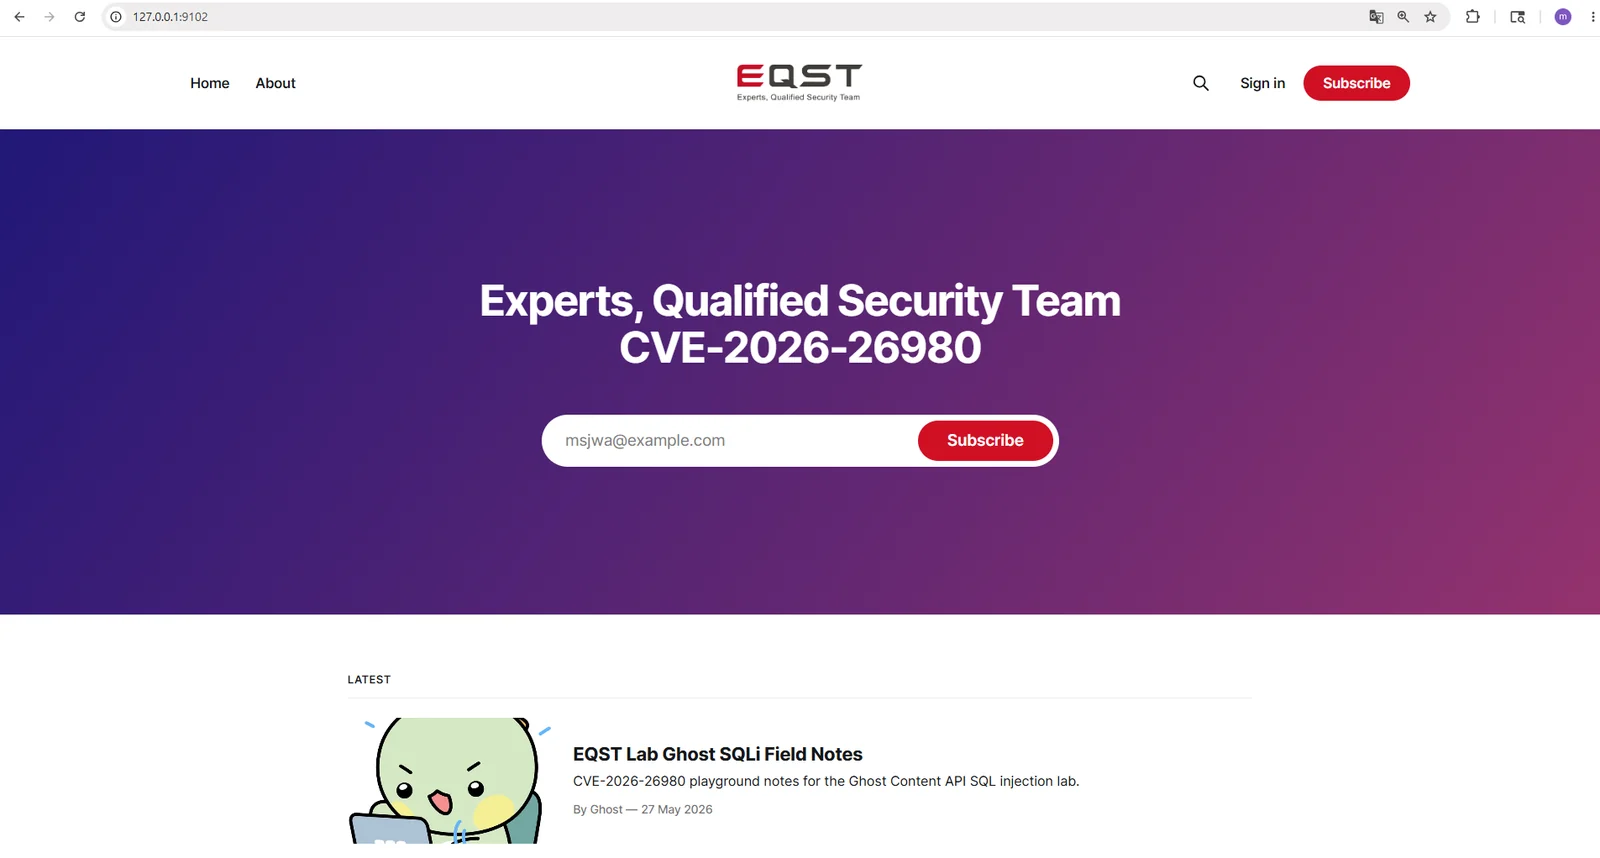 yym8538/cve-2026-26980
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
 syogod/cve-2023-40028
CVE-2023-40028 is a security vulnerability affecting Ghost CMS versions prior to 5.59.1.
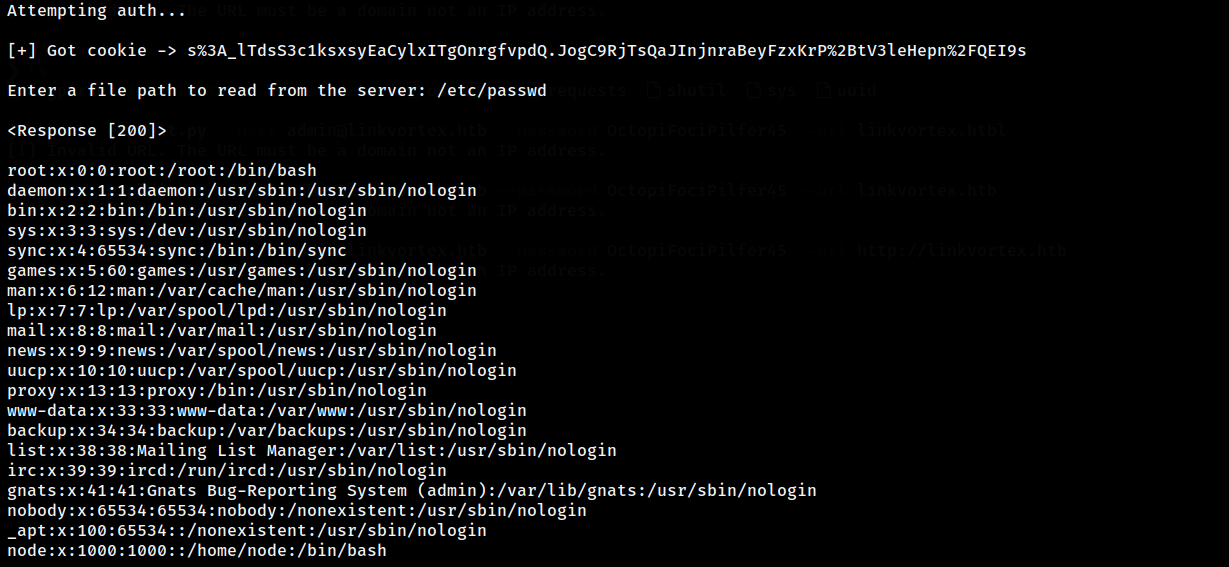 monke443/cve-2023-40028
Arbitrary file read in Ghost-CMS allows an attacker to upload a malicious ZIP file with a symlink.