
CVE-2025-29927-check
 c0dejump/cve-2025-29927-check
script to check cve "CVE-2025-29927" while waiting to add it to HExHTTP
exploitationinformation-gatheringpenetration-testing+2
c0dejump/cve-2025-29927-checkscript to check cve "CVE-2025-29927" while waiting to add it to HExHTTP
 0xeremus/dirty-pipe-poc
POC Exploit to add user to Sudo for CVE-2022-0847 Dirty Pipe Vulnerability
 1neptune/fragnesia
Add go CVE-2026-46300 (Fragnesia) local privilege escalation exploit
 bypazs/cve-2022-32114
An unrestricted file upload vulnerability in the Add New Assets function of Strapi v4.1.12 allows attackers to execute arbitrary code via a crafted…
 1neptune/dirtyfrag
Add go CVE-2026-43284 / CVE-2026-43500 (dirtyfrag) local privilege escalation exploit
 rio128128/mass-cve-2023-28121-kdoec
CVE-2023-28121 - WooCommerce Payments < 5.6.2 - Unauthenticated Privilege Escalation [ Mass Add Admin User ]
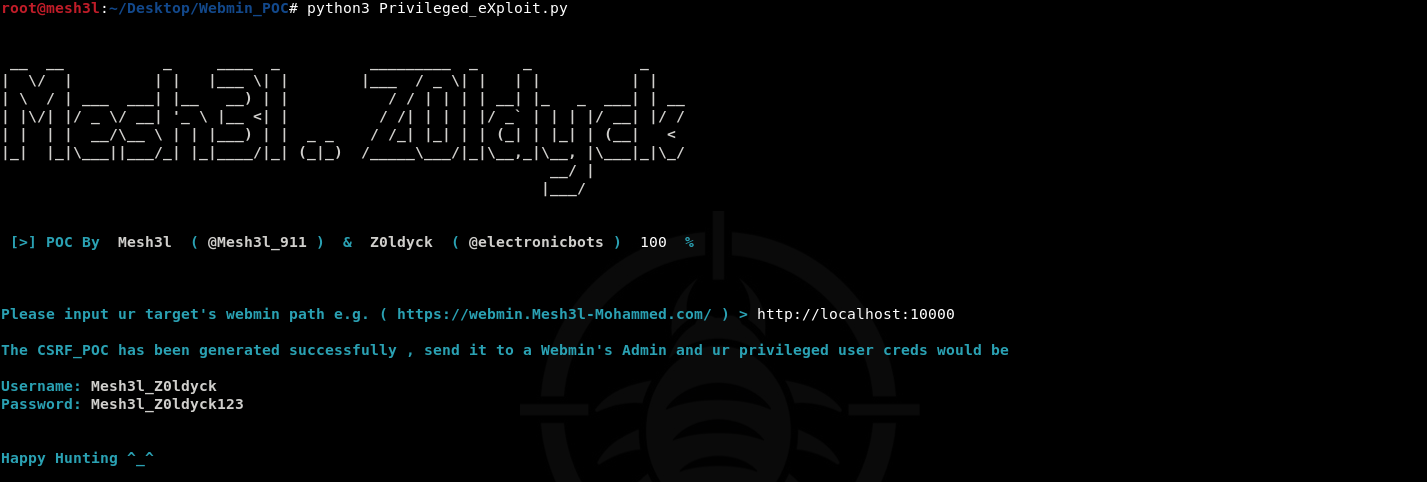 mesh3l911/cve-2021-31762
Exploiting a Cross-site request forgery (CSRF) attack to creat a new privileged user through the Webmin's add users feature
 drew-alleman/cve-2020-11651
A script that exploits SaltStack CVE-2020-11651 and CVE-2020-11652 to add new users to a vulnerable Salt master by injecting entries into /etc/passwd…
 whoami-chmod777/cve-2021-1675-cve-2021-34527
PowerShell exploit for PrintNightmare (CVE-2021-1675) performing local privilege escalation via Print Spooler, with custom DLL payload injection to…
 cyb3rpeace/cve-2021-34527
PowerShell local privilege escalation exploit for PrintNightmare (CVE-2021-34527) targeting Windows Print Spooler. Embeds custom DLL payload to add…
 joaomorenorf/cve-2014-3704
This code is taken from "Drupal 7.0 < 7.31 - 'Drupalgeddon' SQL Injection (Add Admin User)" and was converted to Python 3 to suit the exercise in…
 huzaifahussain98/cve-2020-23586
CSRF allows to Add Network Traffic Control Type Rule
 ynsmroztas/cve-2020-6287-sap-add-user
sap netweaver portal add user administrator
 vijayshankar22/cve-2017-12542
This script checks if an HP iLO server is vulnerable and can add an admin user
 bypazs/cve-2023-26982
Trudesk v1.2.6 was discovered to contain a stored cross-site scripting (XSS) vulnerability via the Add Tags parameter under the Create Ticket…
 mesh3l911/cve-2021-32160
Exploiting a Reflected Cross-Site Scripting (XSS) attack to create a privileged user through the Webmin's add users feature then getting a reverse…
 mbadanoiu/mal-005
MAL-005: Zip Slip in Add Carbon Applications in WSO2 ESB
 azhao1981/cve-2021-29441
Exploit for CVE-2021-29441 targeting Alibaba Nacos to add unauthorized accounts, enabling authentication bypass and unauthorized access.